

OpenHunterAI
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
ai-securityapi-securityapi-security-testing+9
324
lumoslab-innovation/openhunteraiLocal-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 openpcc/openpcc
An open-source framework for verifiably private AI inference
 4ier/neo
Turn any web app into an API. Chrome extension captures browser traffic, auto-generates schemas, lets AI replay APIs directly. No official API needed.
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 pwnfunction/sandbox
Run untrusted AI code safely, fast
 coffinxp/gemini-api-key-hunter
Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…
 agentrust-io/cmcp
cMCP: Confidential MCP Gateway. Hardware-attested policy enforcement for MCP tool calls.
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
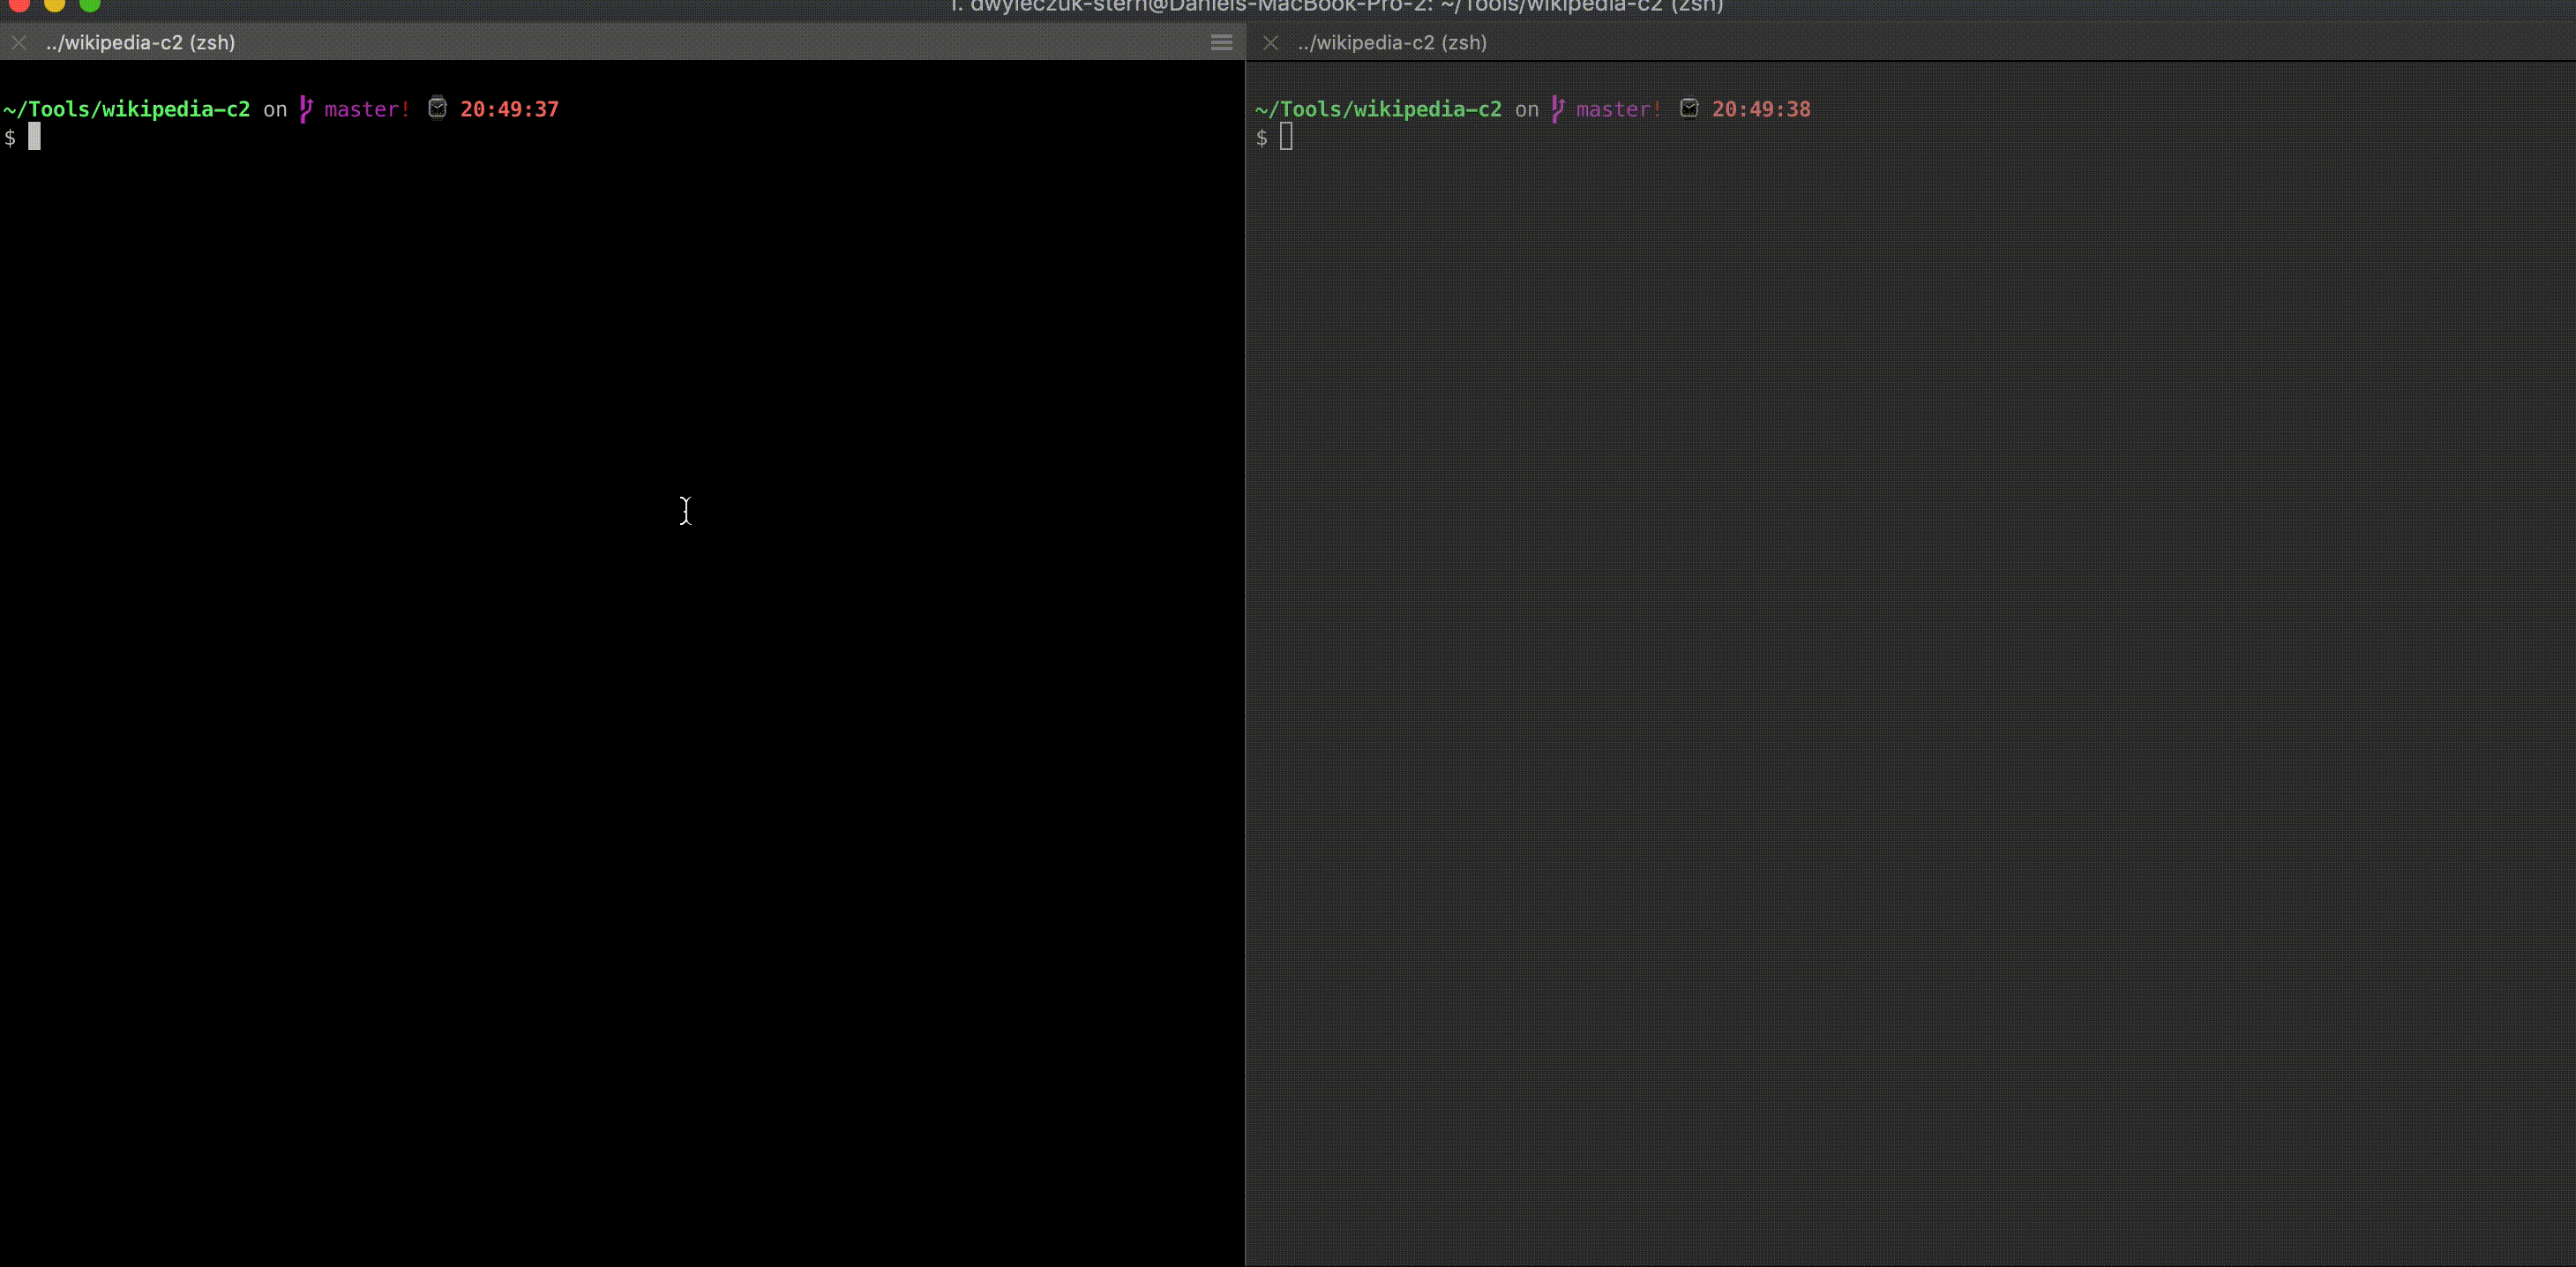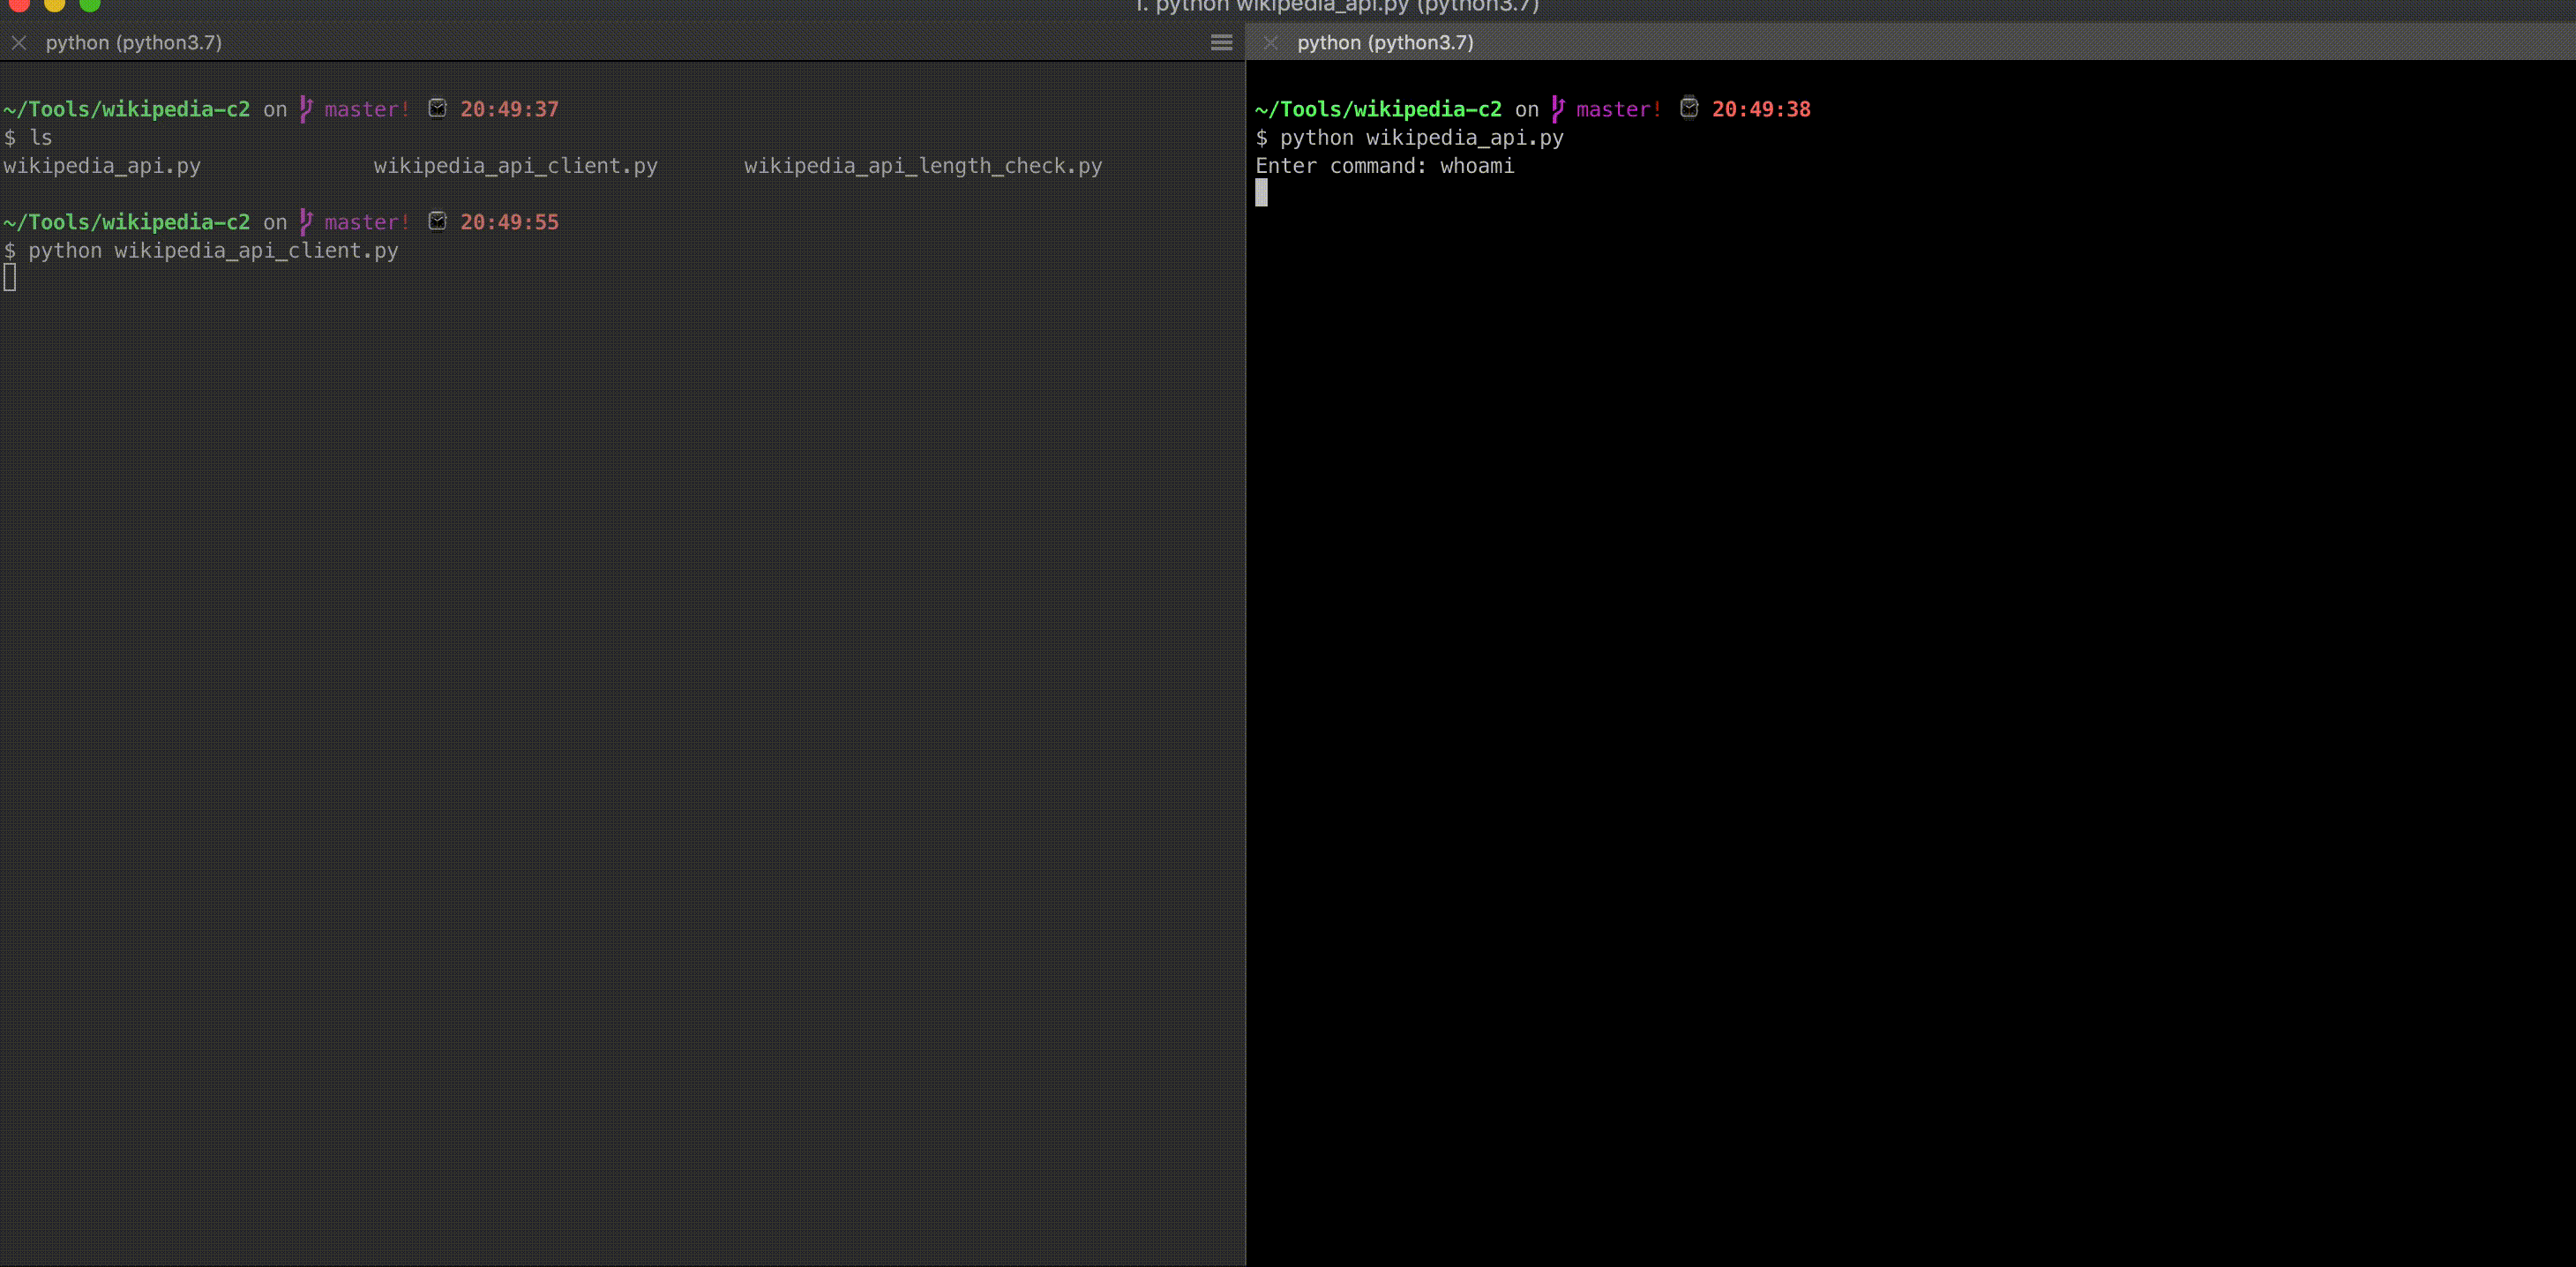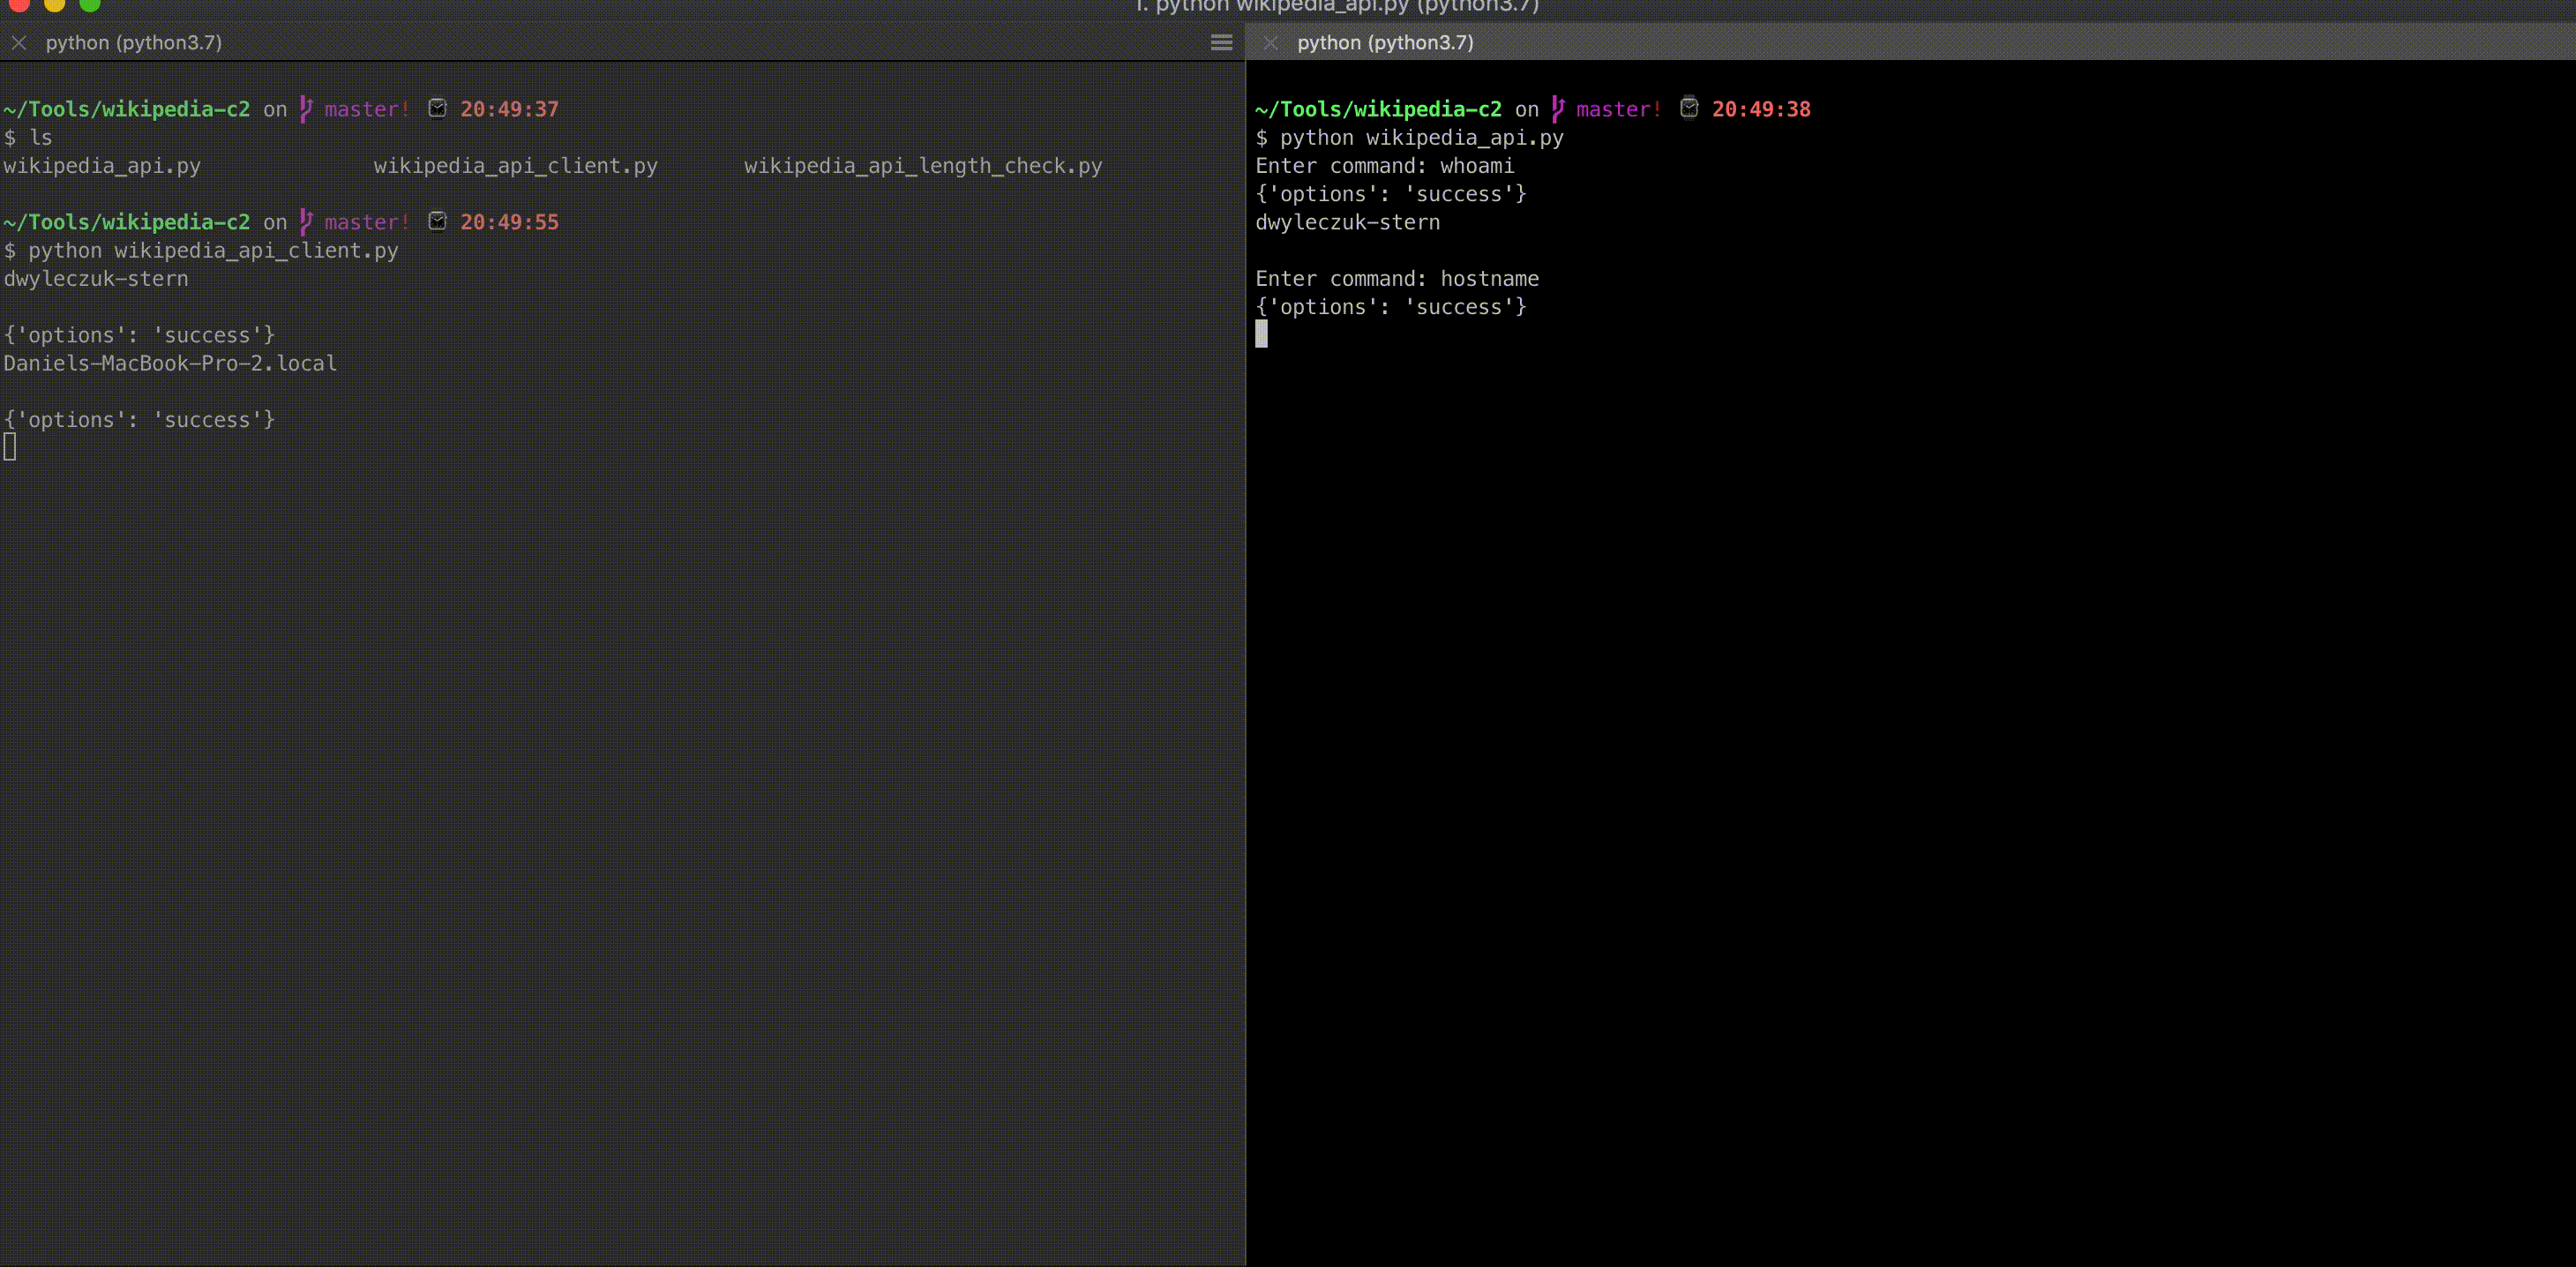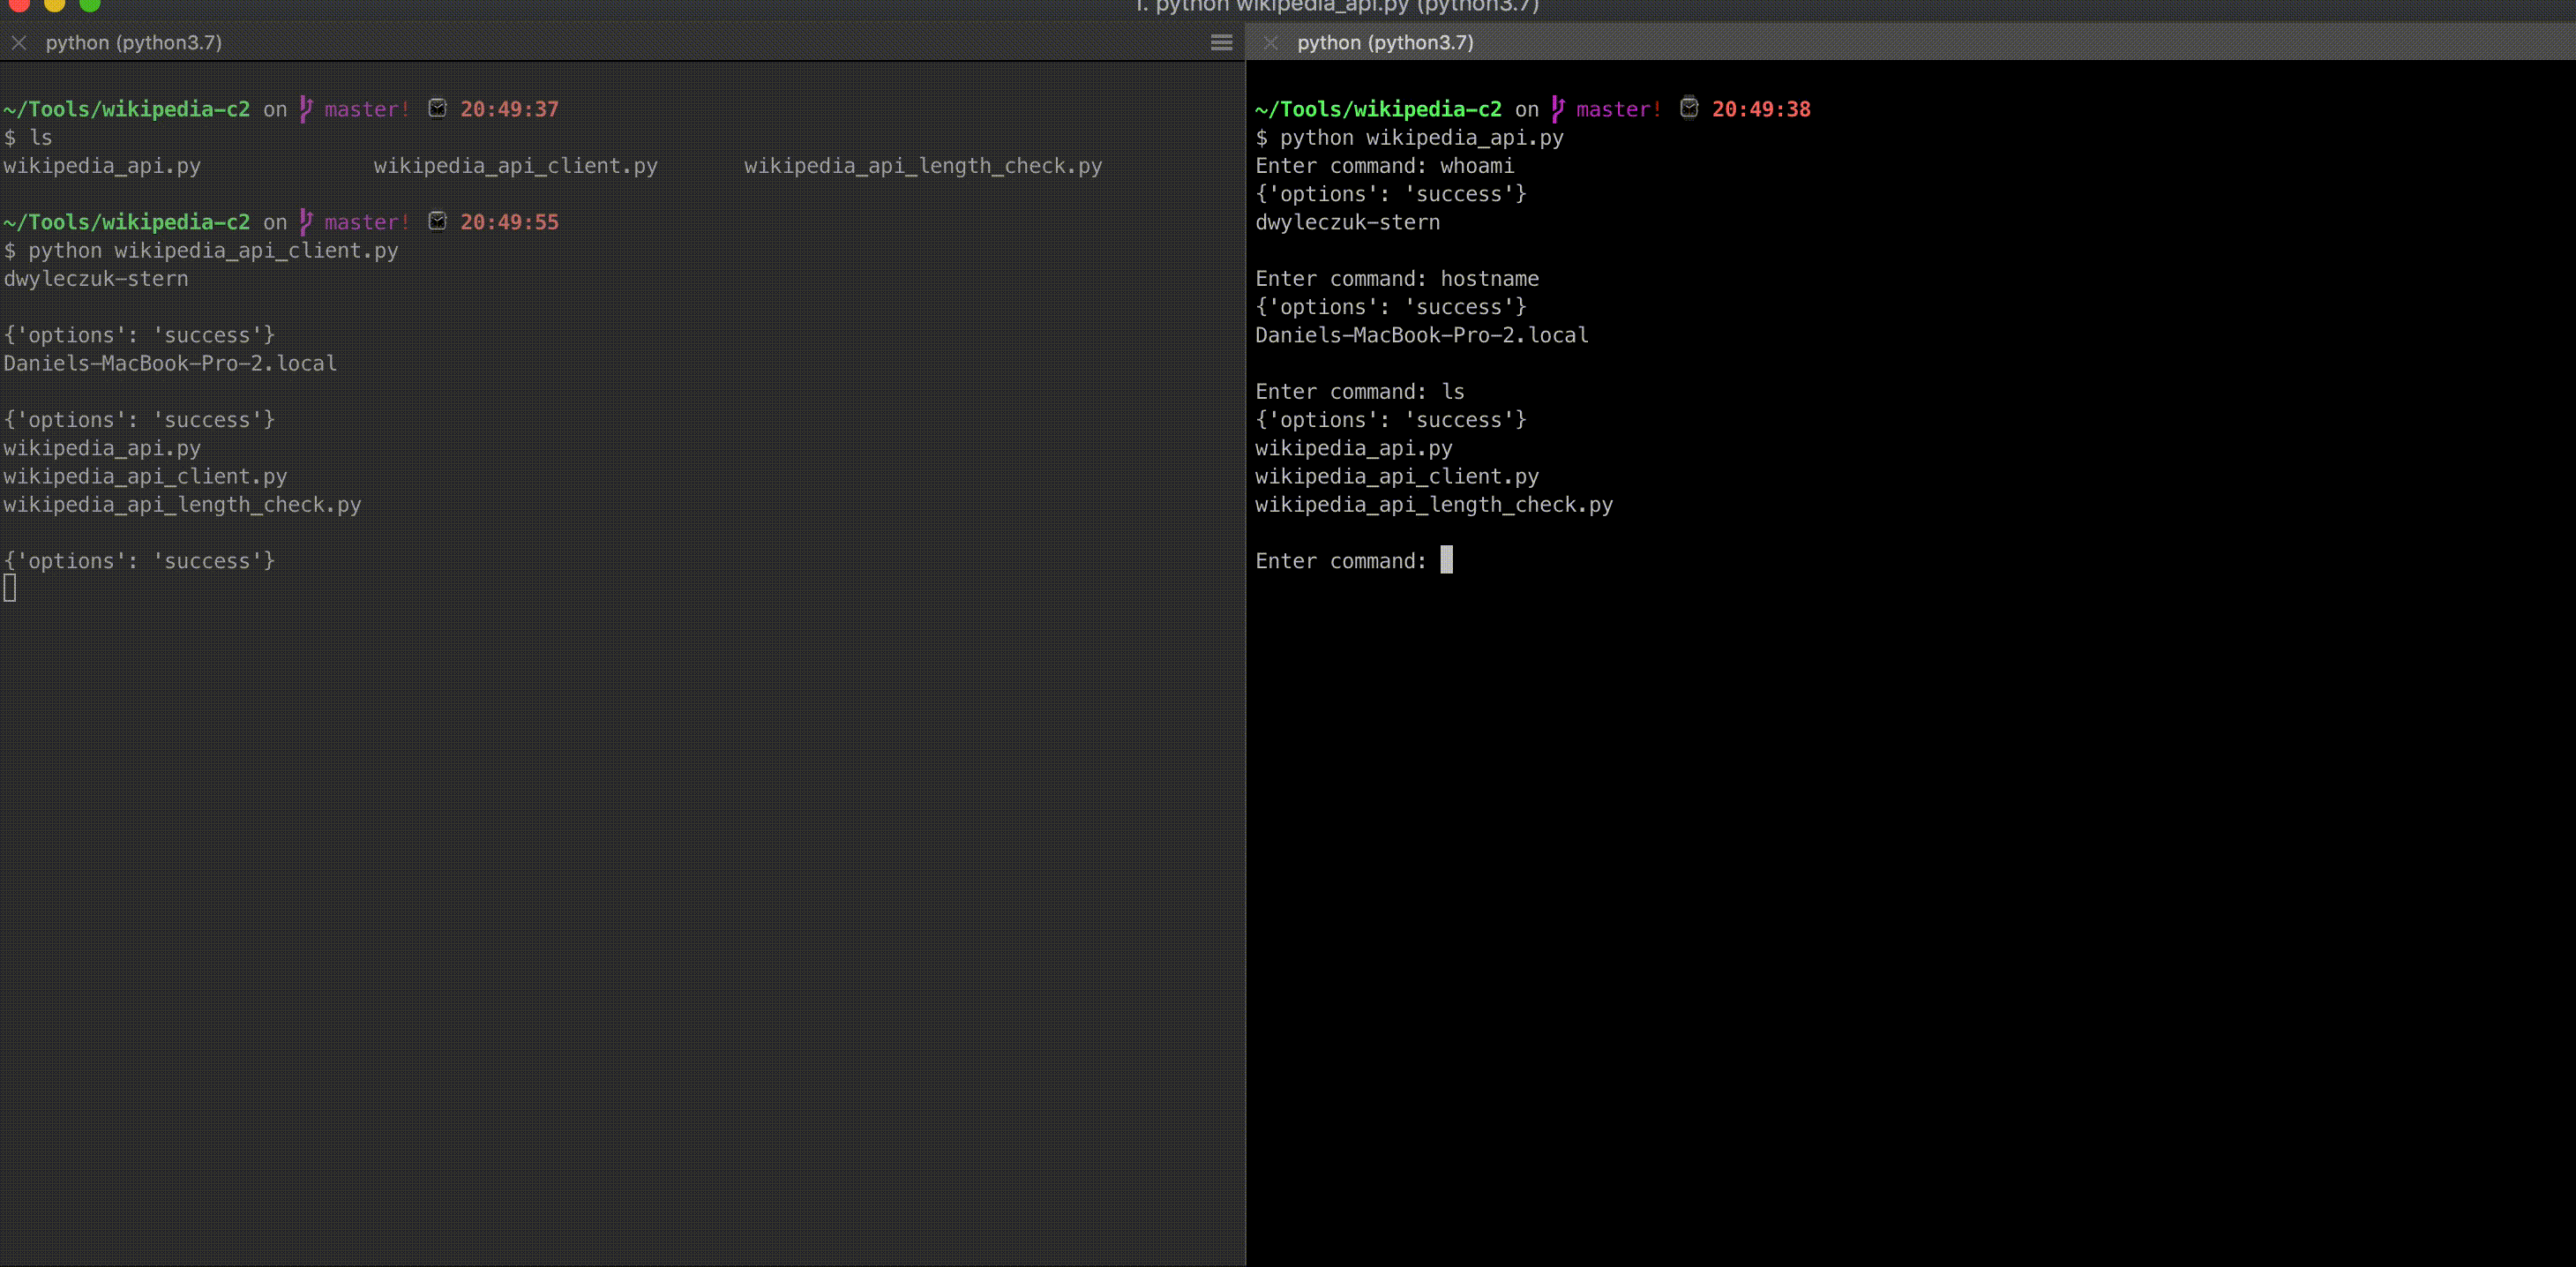 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 sublime-security/ics-phishing-toolkit
Open source tooling to stop ICS phishing (malicious calendar invites)
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 nccgroup/http-mcp-bridge
HTTP proxy bridge for security testing of remote MCP servers, allowing standard HTTP tools to send JSON-RPC messages and manage sessions.
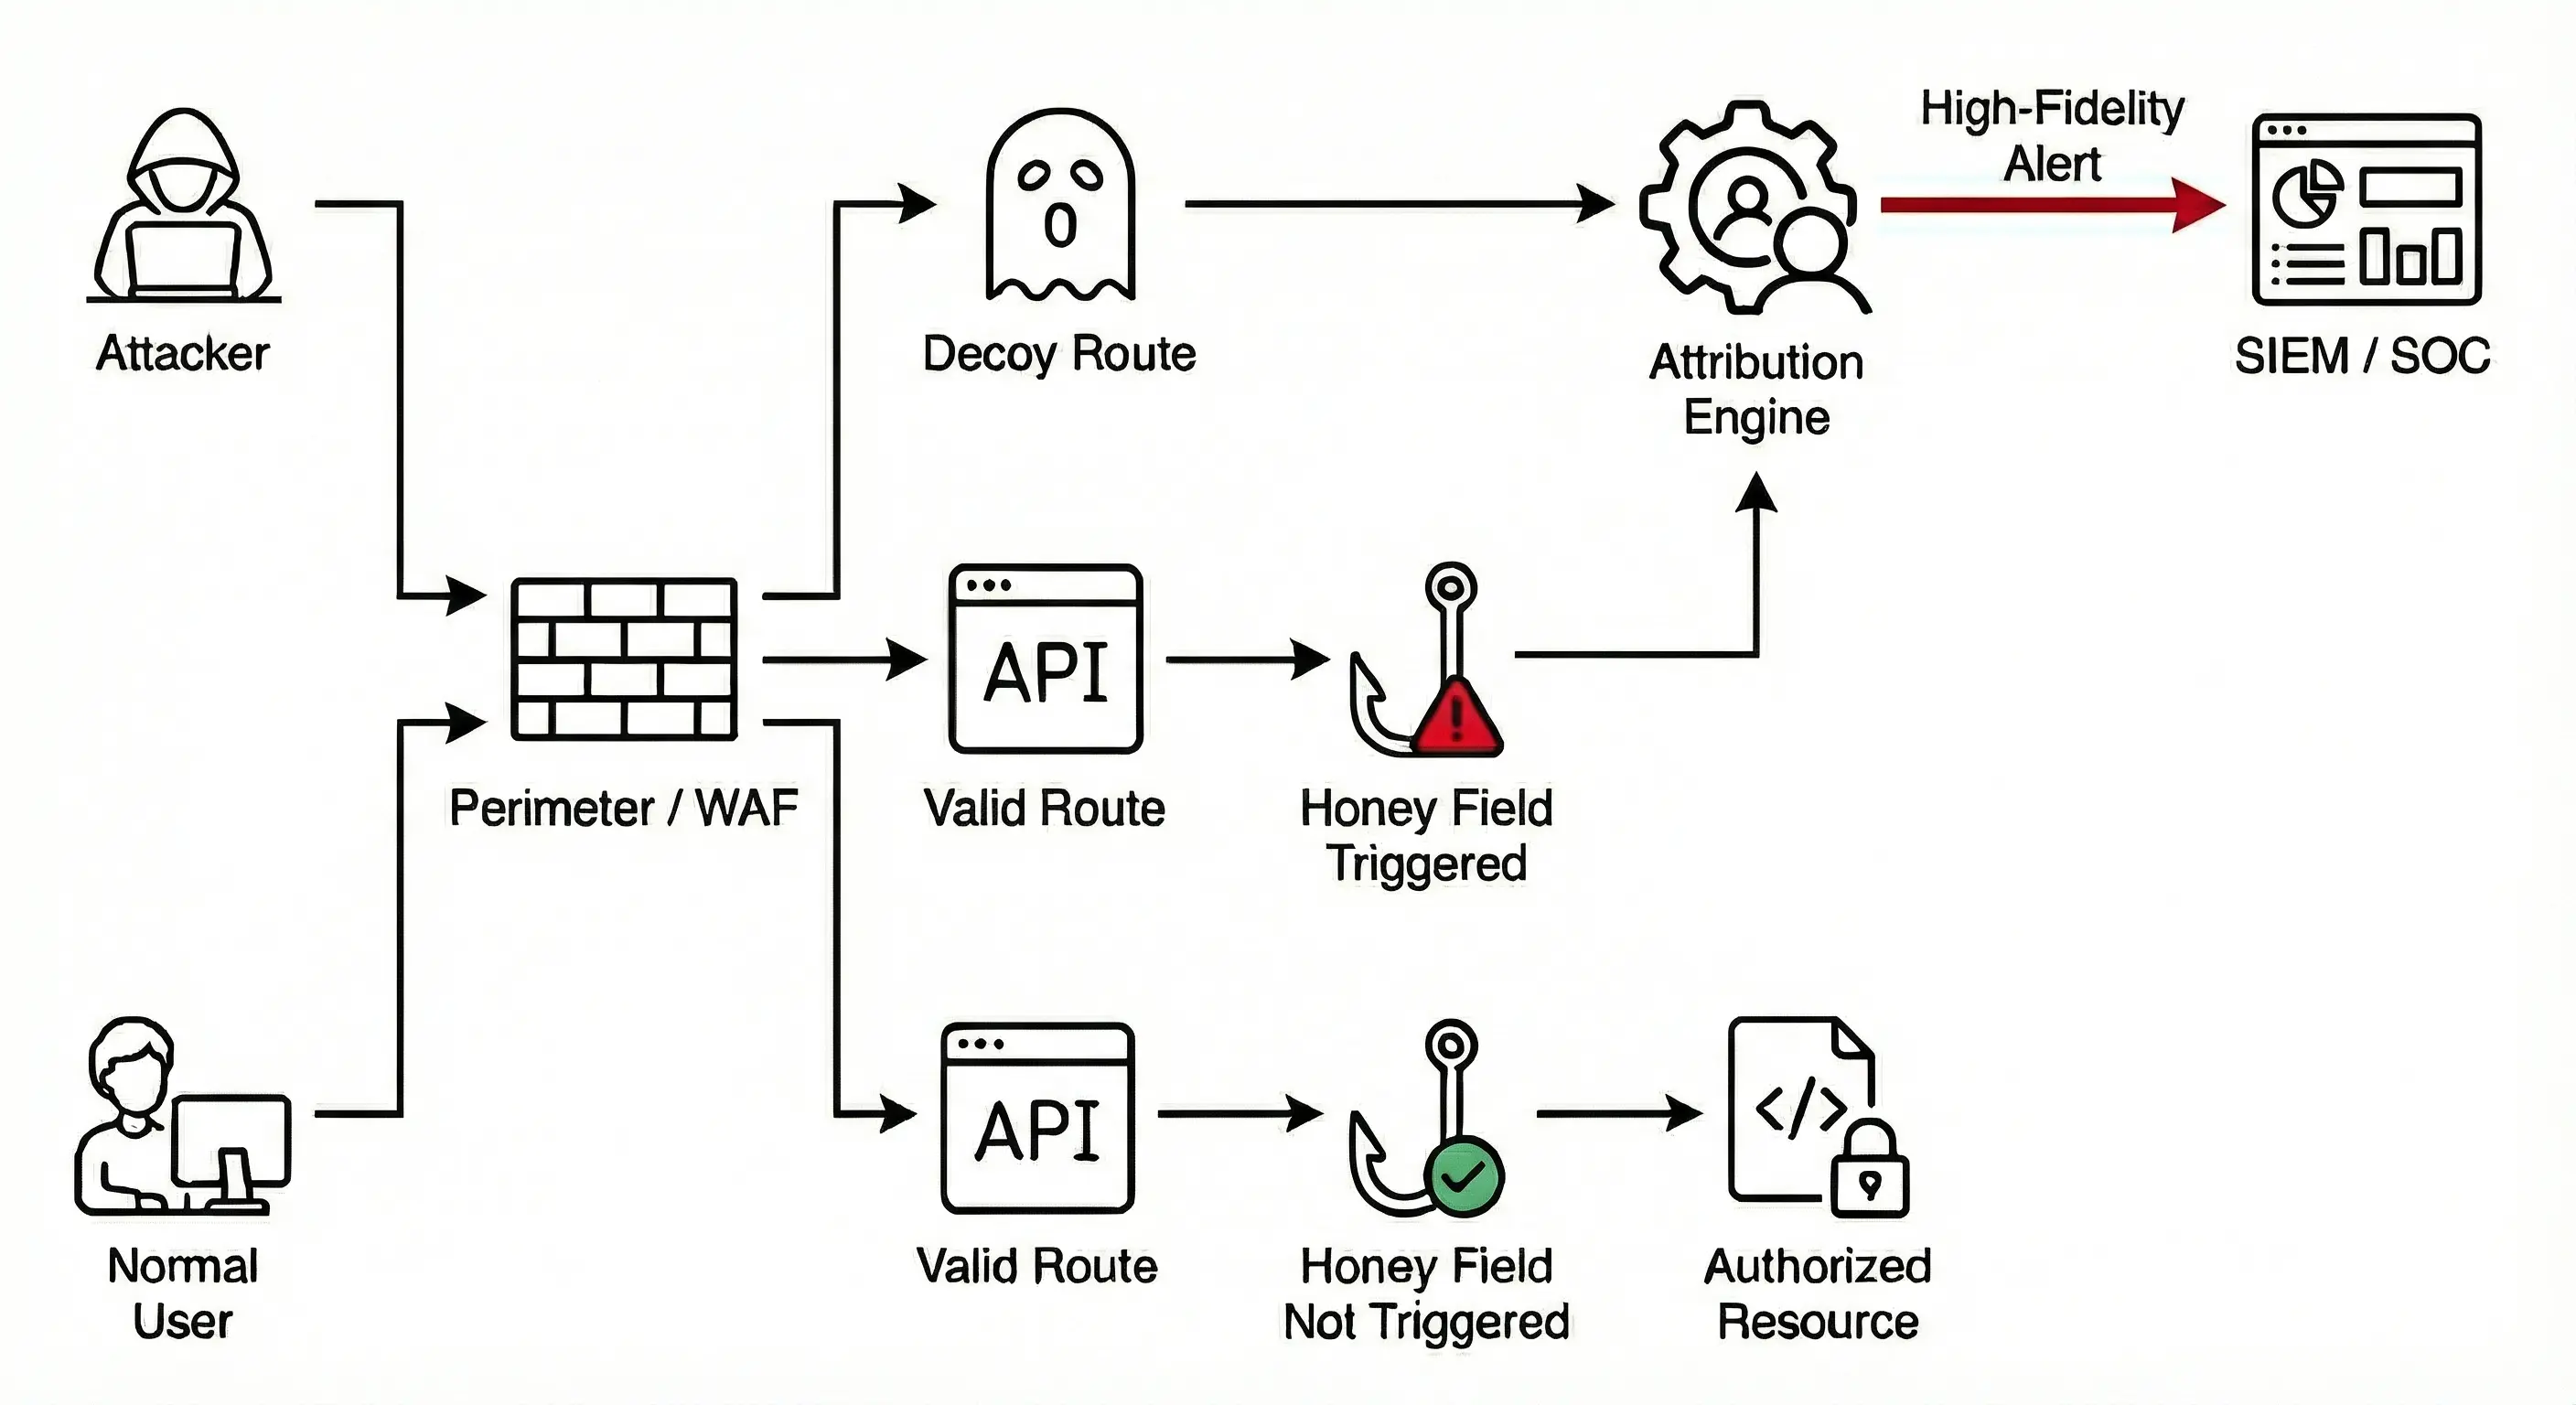 trappsec-dev/trappsec
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
 vikasudasi/exfil-scan
Scan LLM outputs and AI-generated content for data exfiltration signals (EchoLeak, CVE-2025-32711) before they reach users or downstream systems
 irgoncalves/f5-waf-enforce-sig-cve-2021-44228
This enforces signatures for CVE-2021-44228 across all policies on a BIG-IP ASM device