
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
235 results
CVE-2024-57972 preview

CVE-2024-57972

GitHubtania-silva/cve-2024-57972

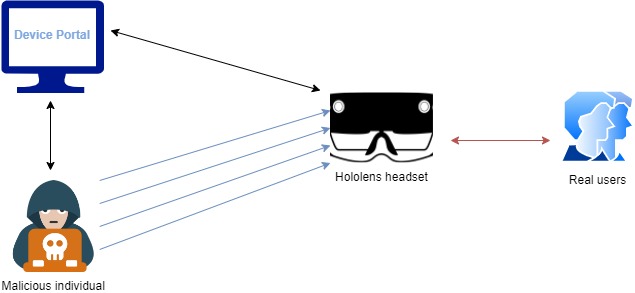
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.
api-securityexploitationhardware-iot-security+2
1 year ago
jwt_tool preview

jwt_tool

GitHubticarpi/jwt_tool

:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
api-securityapi-security-testingcryptography+5
6.8k1 year ago
http-mcp-bridge preview

http-mcp-bridge

GitHubnccgroup/http-mcp-bridge

HTTP proxy bridge for security testing of remote MCP servers, allowing standard HTTP tools to send JSON-RPC messages and manage sessions.
api-securitypenetration-testingweb-proxies-interception+1
174 months ago
CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field preview

CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field

GitHubtheopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field

Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)

ai-securityapi-securityexploitation+3
1 month ago
CVE-2023-27587-PoC preview

CVE-2023-27587-PoC

GitHubvagnerd/cve-2023-27587-poc

The simple PoC of CVE-2023-27587
api-securityexploitationinformation-gathering+3
53 years ago
janusec preview

janusec

GitHubjanusec/janusec

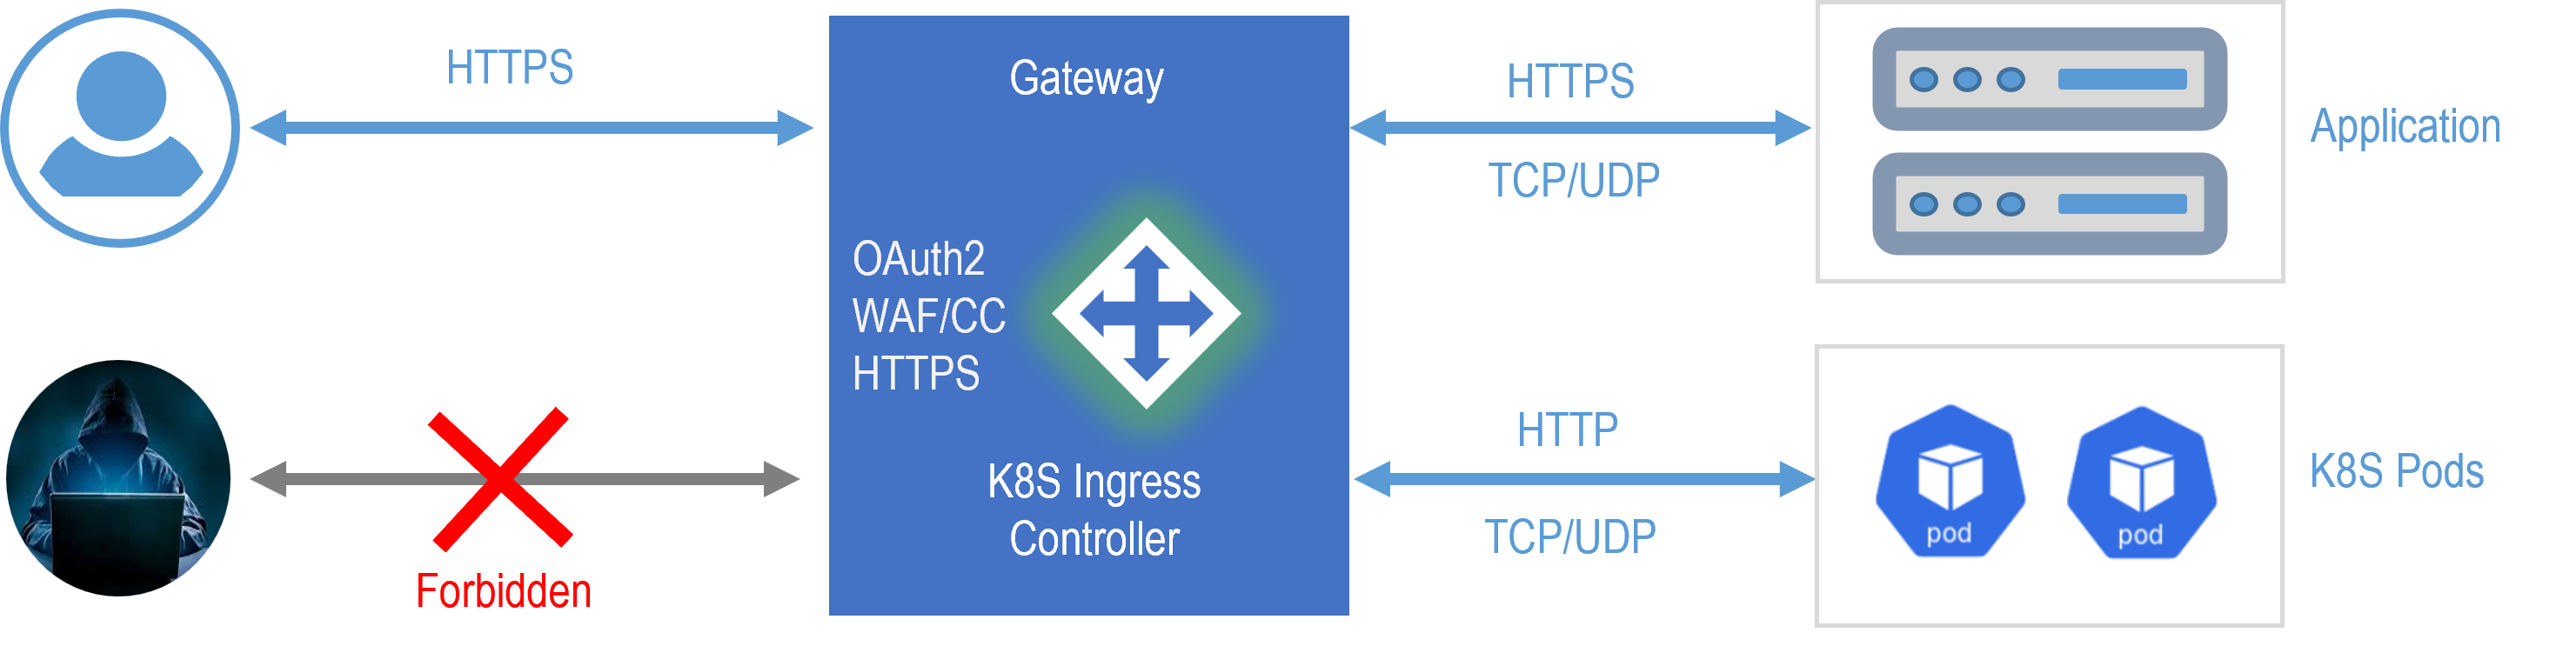
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…

api-securityauthenticationcloud-security+8
1.2k1 month ago
porch-pirate preview

porch-pirate

GitHubwatchdogsecurity/porch-pirate

Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
api-securityinformation-gatheringosint+4
4772 years ago
CVE-2026-40179-PoC preview

CVE-2026-40179-PoC

GitHubbsdrip/cve-2026-40179-poc

Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
api-securityexploitationvulnerability-analysis+1
15 days ago
CVE-2026-58231 preview

CVE-2026-58231

GitHubwildandeveloper/cve-2026-58231

Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
api-securityauthenticationinformation-gathering+4
23 days ago
-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis- preview

-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis-

GitHubkaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-

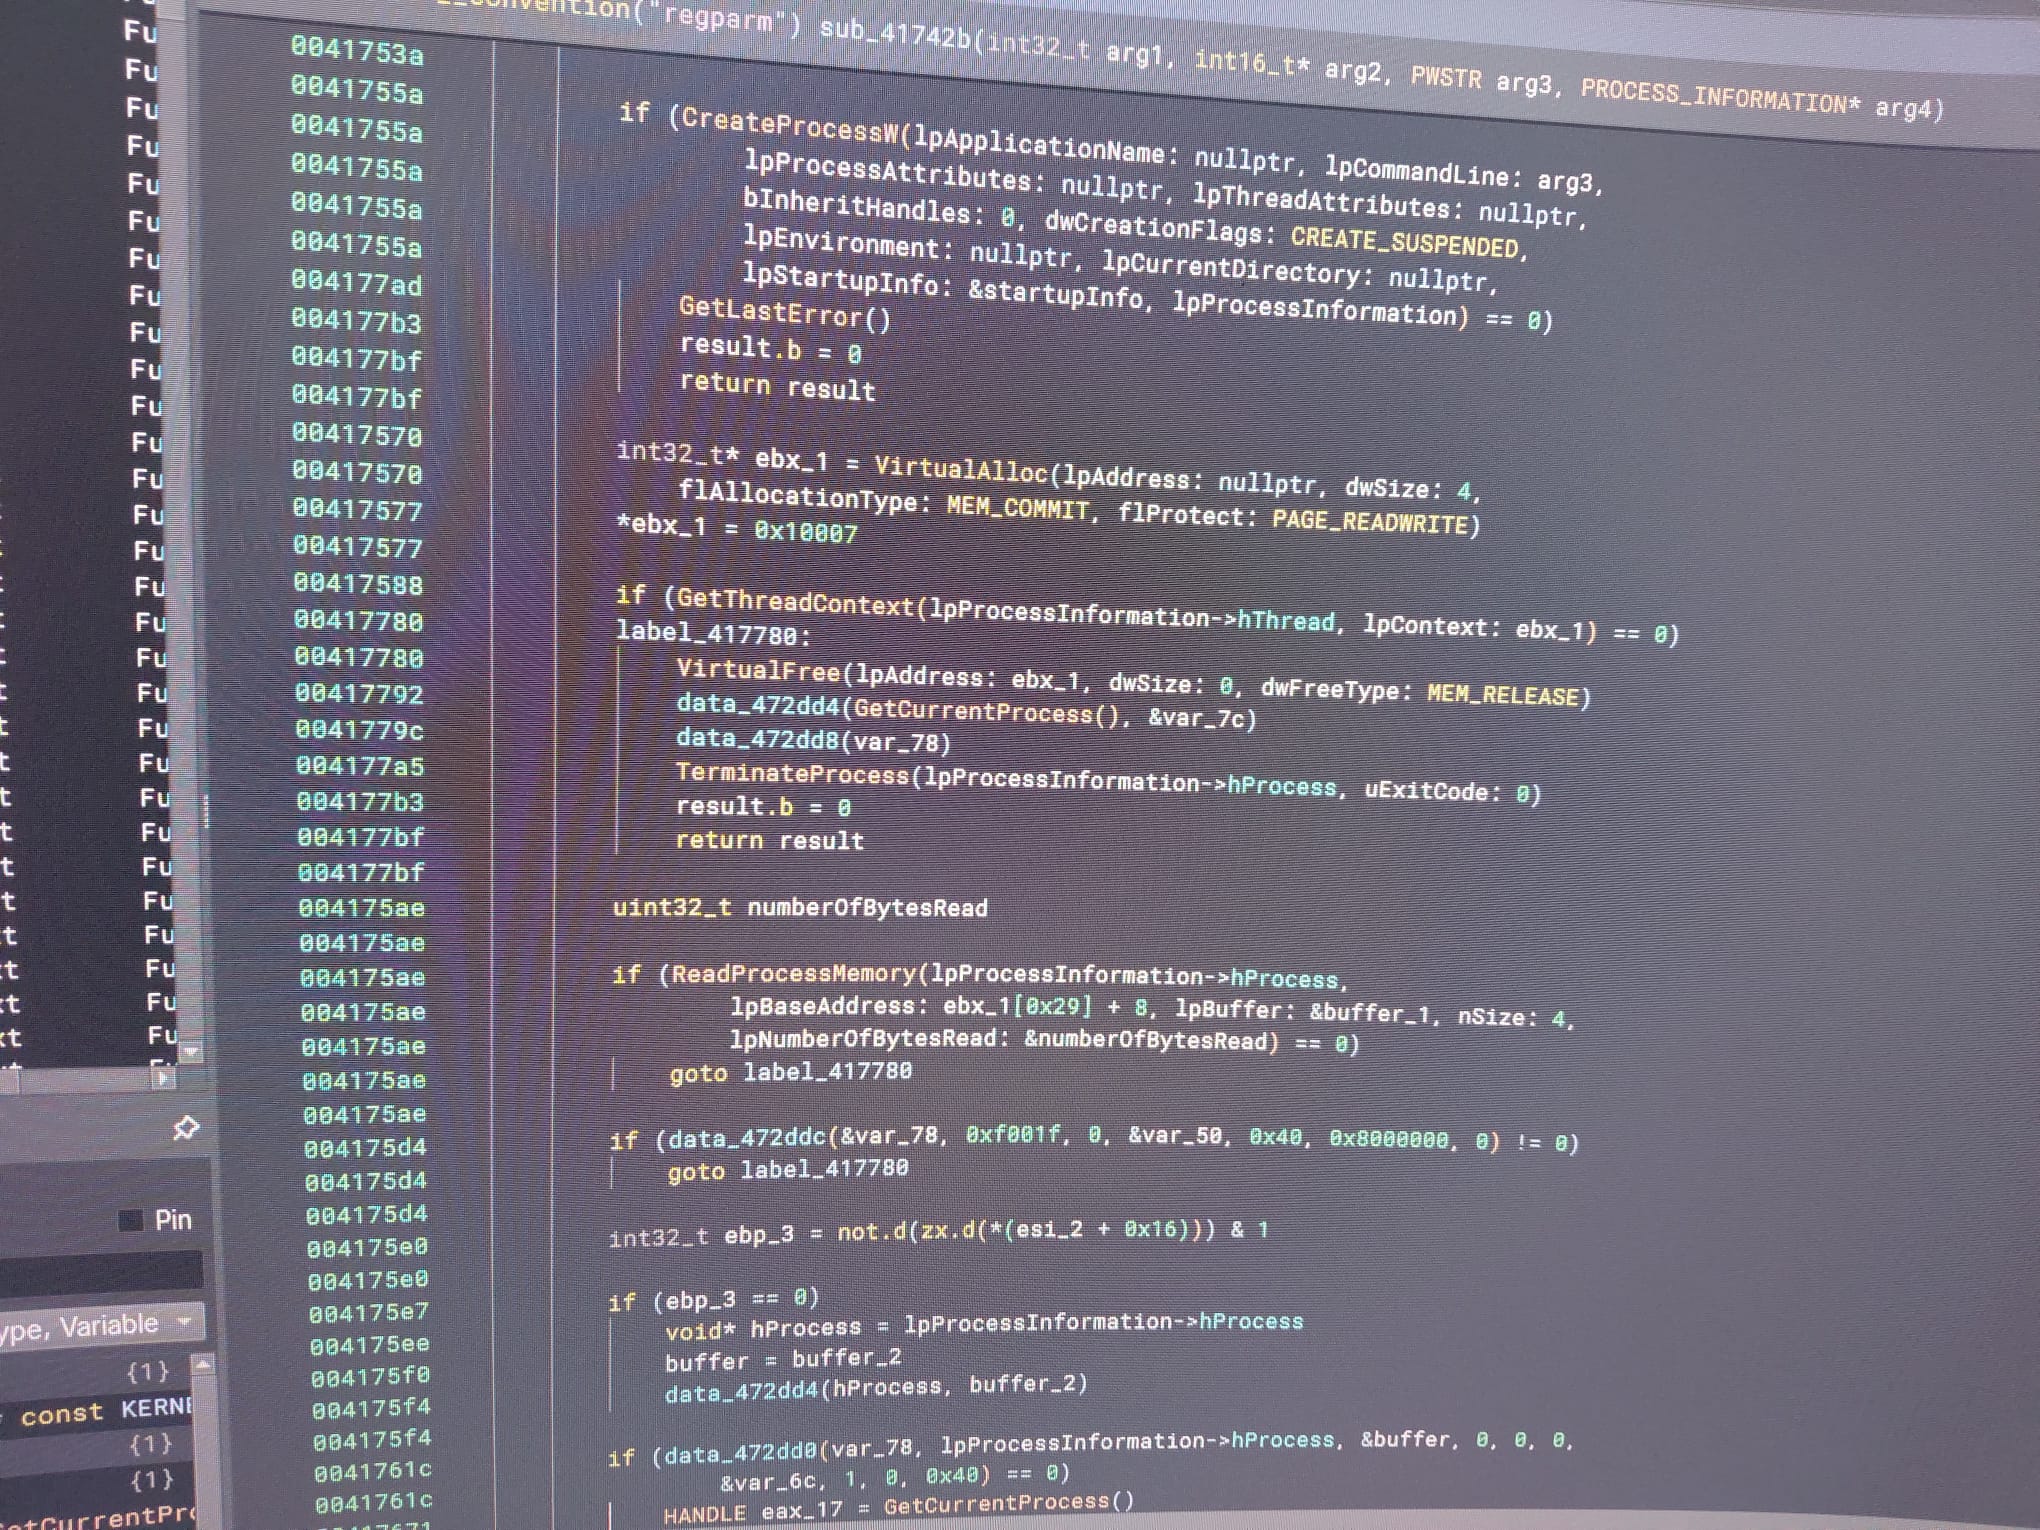
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
api-securitybinary-analysisdynamic-analysis-sandboxing+8
22 months ago
Azure-APIM-Dev-Portal-Signup-Bypass preview

Azure-APIM-Dev-Portal-Signup-Bypass

GitHubdz-y/azure-apim-dev-portal-signup-bypass

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
api-securityapi-security-testingauthentication-authorization+6
1 month ago
CVE-2025-30144 preview

CVE-2025-30144

GitHubtibrn/cve-2025-30144

Proof-of-concept for CVE-2025-30144: JWT issuer validation bypass in fast-jwt library allowing attackers to forge tokens with array-based iss claims.

api-securityauthenticationexploitation+3
1 year ago
CVE-2024-1208-and-CVE-2024-1210 preview

CVE-2024-1208-and-CVE-2024-1210

GitHubkarlemilnikka/cve-2024-1208-and-cve-2024-1210

Detailed disclosure of CVE-2024-1208 and CVE-2024-1210: sensitive information exposure via REST API in LearnDash WordPress plugin, allowing…
api-securityeducationinformation-gathering+3
32 years ago
mcp-doorman preview

mcp-doorman

GitHubsushank05/mcp-doorman

A lightweight mcp to prevent poisoning CVE (CVE-2025-54136), researchers hijacking Claude Code/Copilot/Gemini via prompt injection, and hundreds of…
ai-securityapi-securitydefensive-tools+5
12 days ago
API-Security-Checklist preview

API-Security-Checklist

GitHubshieldfy/api-security-checklist

Checklist of the most important security countermeasures when designing, testing, and releasing your API
api-securityauthentication-authorizationcurated-resources+4
23.3k1 month ago
CVE-2026-52217-VTEX-Checkout-CrossTenant-IDOR preview

CVE-2026-52217-VTEX-Checkout-CrossTenant-IDOR

GitHubteteco/cve-2026-52217-vtex-checkout-crosstenant-idor

The VTEX Checkout Service exposes OrderForm data through the endpoints `/api/checkout/pub/orderForm/{orderFormId}` and `/attachments/*`. These…

api-securityauthentication-authorizationinformation-gathering+3
2 months ago
sudowp-clickfunnels-zurich preview

sudowp-clickfunnels-zurich

GitHubsudo-wp/sudowp-clickfunnels-zurich

A security-patched fork of the legacy ClickFunnels Classic WordPress plugin. Fixes critical Stored XSS vulnerabilities (CVE-2022-4782) while…
api-securityauthentication-authorizationcode-analysis+3
16 months ago
CVE-2026-22014-GraphQL-Persisted-Queries-Injection-via-ID-Manipulation preview

CVE-2026-22014-GraphQL-Persisted-Queries-Injection-via-ID-Manipulation

GitHubgeorge0papasotiriou/cve-2026-22014-graphql-persisted-queries-injection-via-id-manipulation

Proof-of-concept exploit for CVE-2026-22014 demonstrating persisted-query ID manipulation in GraphQL APIs to bypass allowlists and execute arbitrary…

api-securityapi-security-testingexploitation+4
1 month ago
Previous1234…14Next