

lua-resty-waf
 p0pr0ck5/lua-resty-waf
High-performance WAF built on the OpenResty stack
anti-botapi-securitydefensive-tools+1
p0pr0ck5/lua-resty-wafHigh-performance WAF built on the OpenResty stack
 liodeus/swaggerhole
A python3 script searching for secret on swaggerhub
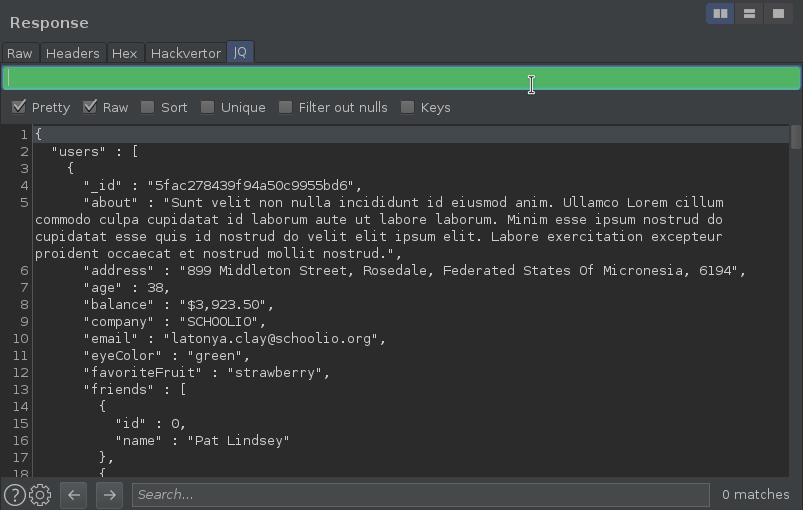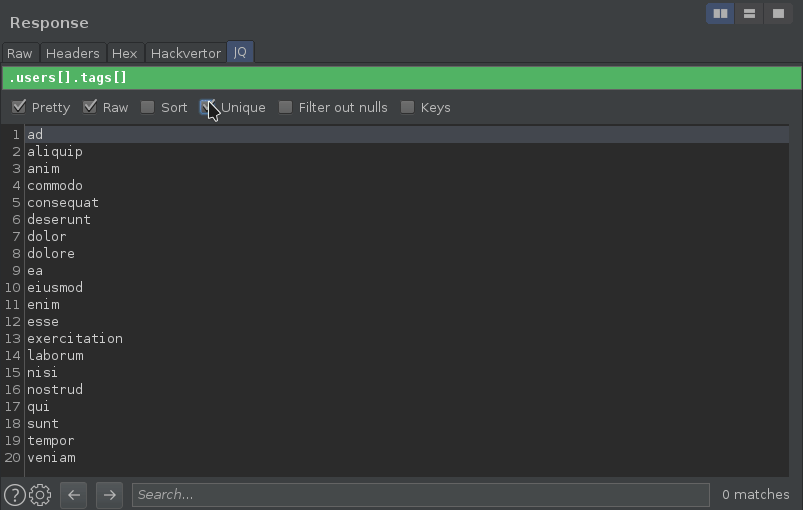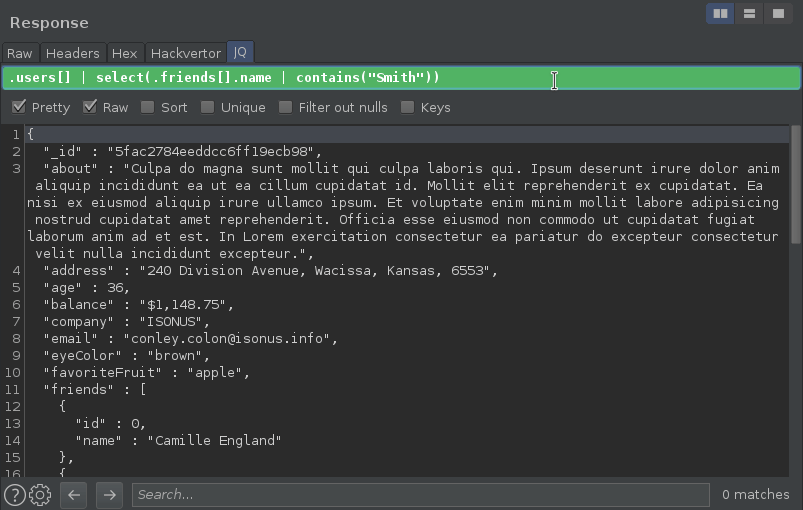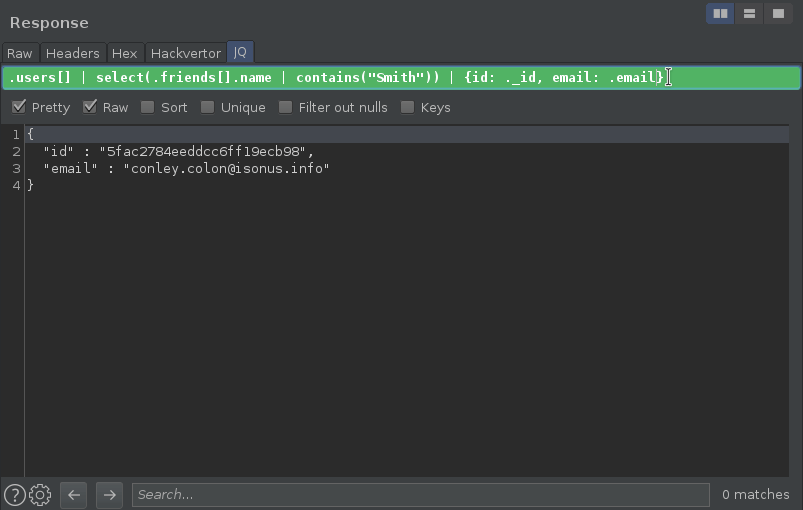 synacktiv/burp-jq
Burp extension to filter JSON on the fly with JQ queries in the HTTP message viewer.
 irgoncalves/f5-waf-enforce-sig-cve-2021-44228
This enforces signatures for CVE-2021-44228 across all policies on a BIG-IP ASM device
 keraattin/cve-2026-33032
One missing function call on the route registration was enough to turn the MCP interface into an unauthenticated RCE gateway.
 hereticl1nk/eits-portal-exploit-cve-2026-31367-poc
PoC exploit for unauthenticated RCE in EITS Admin Dashboard v2.4.0 via command injection in /api/v1/debug, allowing arbitrary OS command execution on…
 comparedarray/printix-cve-2022-29554
A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…
 0x0w1z/cve-2025-61777
CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.
 theopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field
Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 osyanina/westone-cve-2021-45232-scanner
A vulnerability scanner that detects CVE-2021-45232 vulnerabilities.
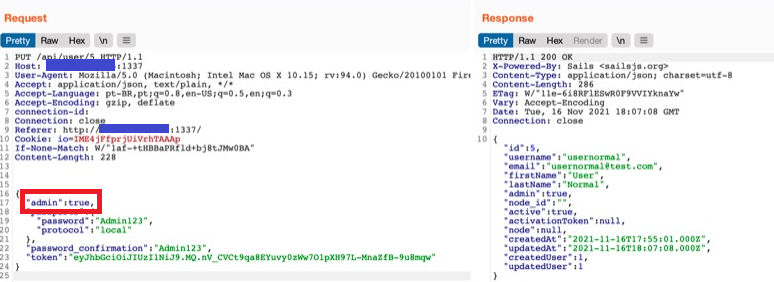 paulotrindadec/cve-2021-44103
Proof-of-concept exploit for CVE-2021-44103 demonstrating vertical privilege escalation in Konga API Gateway 0.14.9, allowing authenticated users to…