
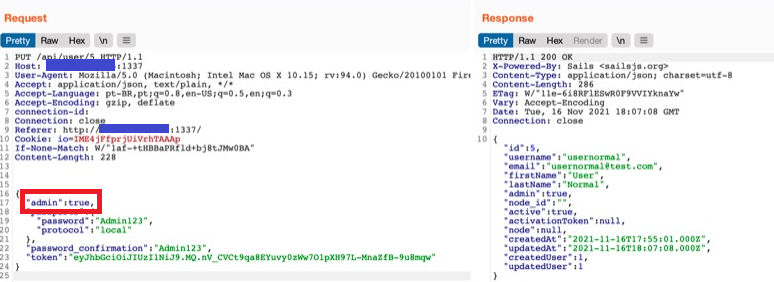
CVE-2021-44103
 paulotrindadec/cve-2021-44103
Proof-of-concept exploit for CVE-2021-44103 demonstrating vertical privilege escalation in Konga API Gateway 0.14.9, allowing authenticated users to…
api-securityexploitationpenetration-testing+3
3
paulotrindadec/cve-2021-44103Proof-of-concept exploit for CVE-2021-44103 demonstrating vertical privilege escalation in Konga API Gateway 0.14.9, allowing authenticated users to…
 george0papasotiriou/cve-2026-21020-protobuf-message-parsing-polymorphic-deserialization-vulnerability
PoC for CVE-2026-21020, demonstrating Protobuf Any-type polymorphic deserialization where attacker-controlled type_url can lead to logic bugs, RCE,…
 squeeze440/inference-gateway-poc
PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
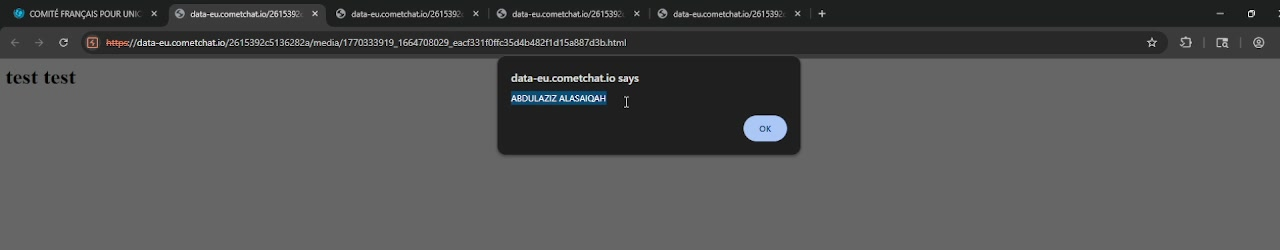 defineid/wildfire
CVE-2026-39154, Stored XSS in CometChat JS SDK
 wa6n3r/cve-2026-35616
Exploit script for CVE-2026-35616 that bypasses certificate chain verification in Fortinet API by discovering valid CNs, generating a forged client…
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
 0x0w1z/cve-2025-61777
CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
 yuxblank/cve-2022-2466---request-context-not-terminated-with-graphql
Proof-of-concept for CVE-2022-2466 demonstrating unauthenticated GraphQL request context termination in Quarkus/SmallRye, bypassing authorization…
 faccimatteo/cve-2022-4361
Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…
 fevar54/cve-2026-35616-detector.py
Detector de CVE-2026-35616: identifica servidores FortiClient EMS vulnerables (7.4.5-7.4.6).
 sibikrish001/cve-2025-55462
Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…
 furkankayapinar/react-next-scanner
CVE-2025-55182 and CVE-2025-66478
 saykino/cve-2025-56223
Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…
 mostafaanouarghorab/microservicecve-2021-39156
 osyanina/westone-cve-2021-45232-scanner
A vulnerability scanner that detects CVE-2021-45232 vulnerabilities.
 imthecopilotnow/cve-2025-492030
Proof-of-concept for CVE-2025-492030: account takeover via session token validation bypass in SecureVPN API endpoint /api/v1/authenticate.
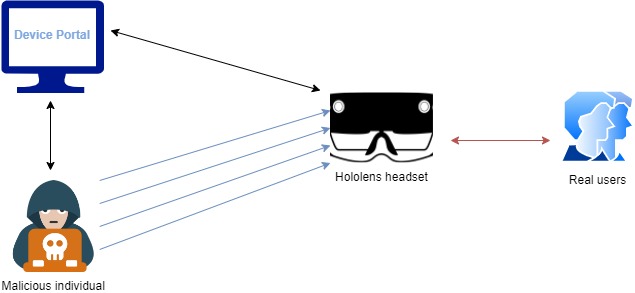 tania-silva/cve-2024-57972
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.
 tibrn/cve-2025-30144
Proof-of-concept for CVE-2025-30144: JWT issuer validation bypass in fast-jwt library allowing attackers to forge tokens with array-based iss claims.