
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
85 results
CVE-2022-24112 preview

CVE-2022-24112

GitHubsecnn/cve-2022-24112

Apache APISIX batch-requests RCE(CVE-2022-24112)
api-securityexploitationremote-access-tool+2
84 years ago
CVE-2025-48827 preview

CVE-2025-48827

GitHub0xgh057r3c0n/cve-2025-48827

Critical Unauthenticated API Access in vBulletin
api-securityexploitationpenetration-testing+2
111 year ago
f5-waf-quick-patch-cve-2021-44228 preview

f5-waf-quick-patch-cve-2021-44228

GitHubirgoncalves/f5-waf-quick-patch-cve-2021-44228

This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
api-securitycloud-securitydevsecops+3
34 years ago
CVE-2020-17518 preview

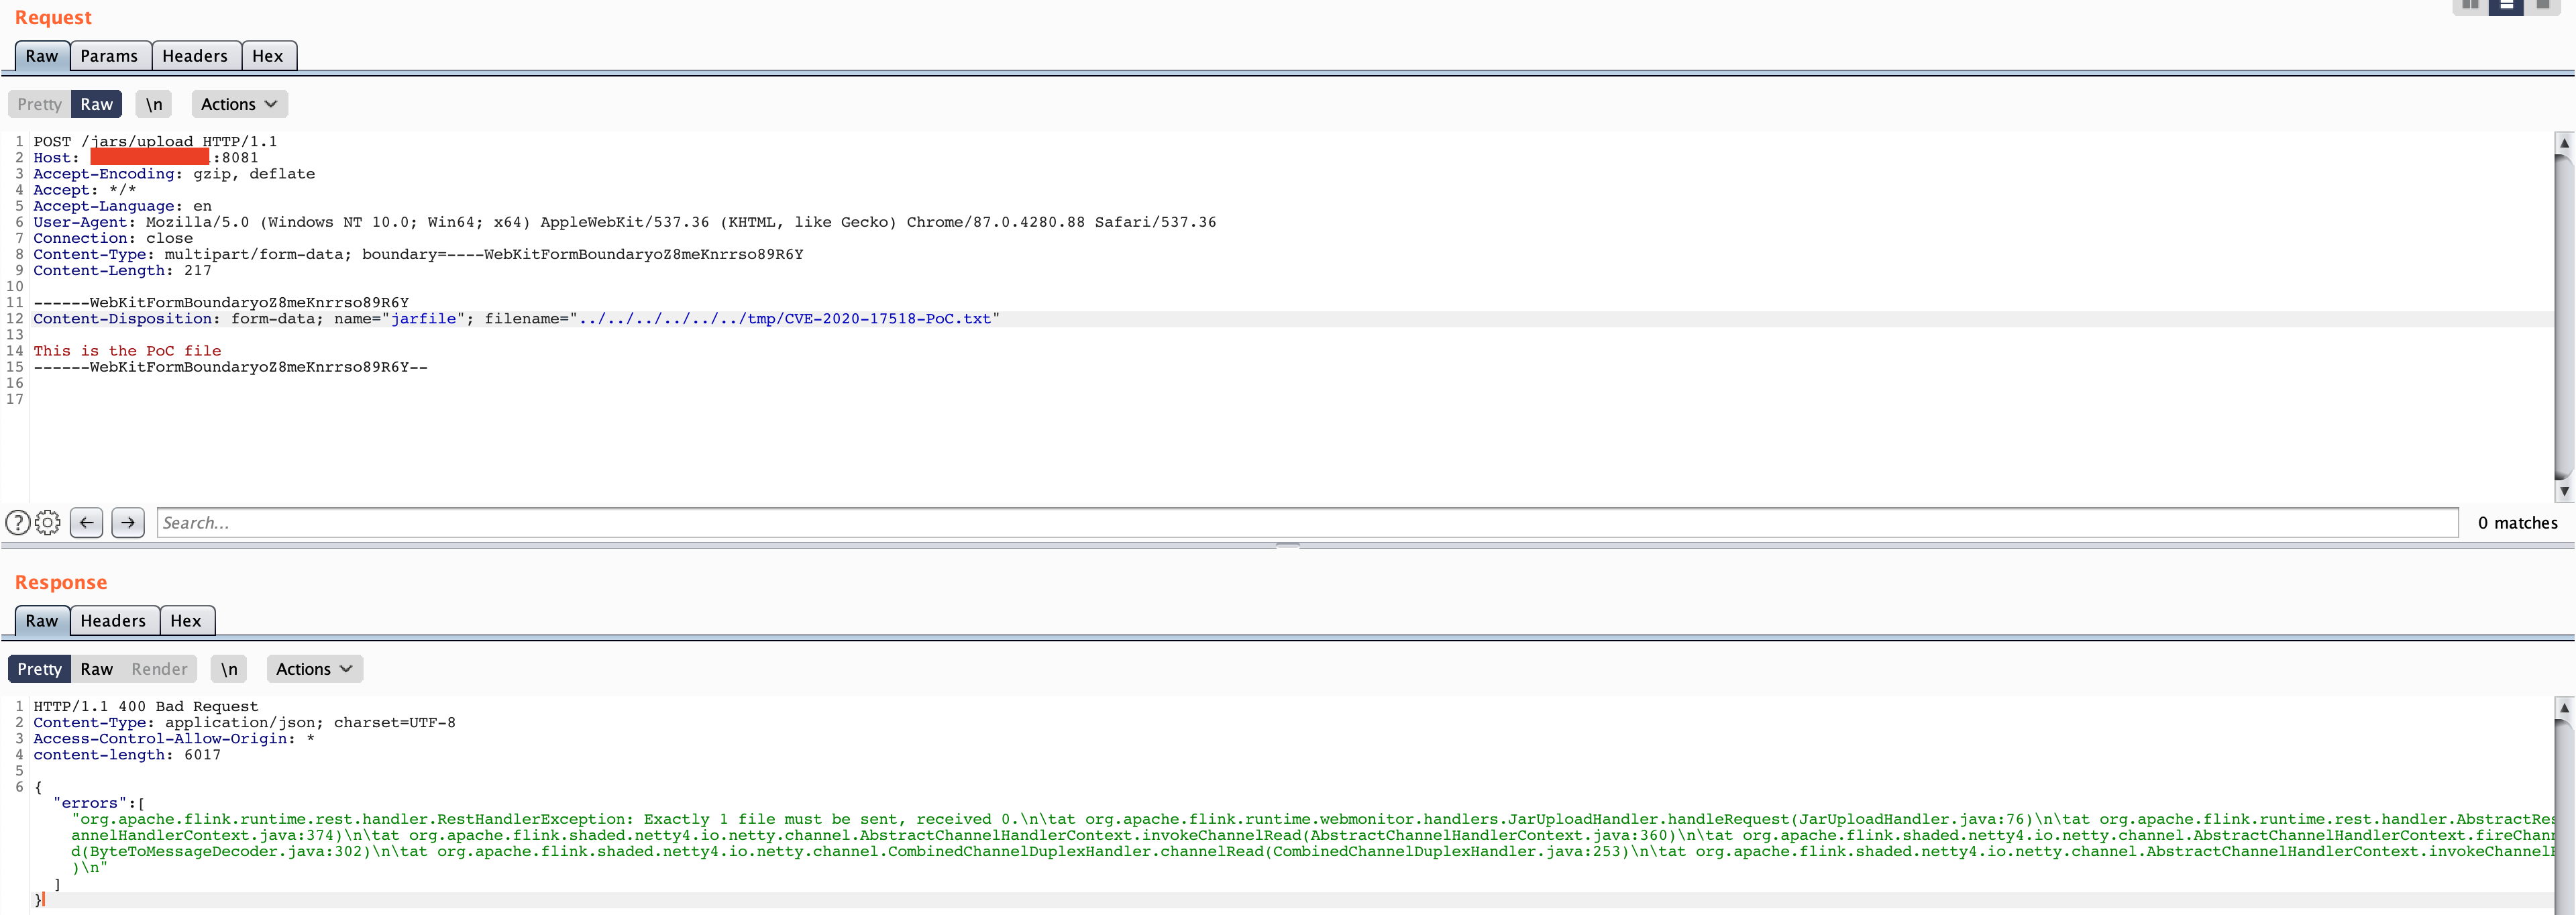
CVE-2020-17518

GitHubmurataydemir/cve-2020-17518

[CVE-2020-17518] Apache Flink RESTful API Arbitrary File Upload via Directory Traversal
api-securityexploitationpenetration-testing+3
35 years ago
CVE-2026-40179-PoC preview

CVE-2026-40179-PoC

GitHubbsdrip/cve-2026-40179-poc

Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
api-securityexploitationvulnerability-analysis+1
1 month ago
CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field preview

CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field

GitHubtheopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field

Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)
ai-securityapi-securityexploitation+3
2 months ago
CVE-2026-21020-Protobuf-Message-Parsing-Polymorphic-Deserialization-Vulnerability preview

CVE-2026-21020-Protobuf-Message-Parsing-Polymorphic-Deserialization-Vulnerability

GitHubgeorge0papasotiriou/cve-2026-21020-protobuf-message-parsing-polymorphic-deserialization-vulnerability

PoC for CVE-2026-21020, demonstrating Protobuf Any-type polymorphic deserialization where attacker-controlled type_url can lead to logic bugs, RCE,…

api-securityexploitationpenetration-testing+1
2 months ago
inference-gateway-PoC preview

inference-gateway-PoC

GitHubsqueeze440/inference-gateway-poc

PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
api-securityauthenticationexploitation+3
1 month ago
CVE-2026-52616 preview

CVE-2026-52616

GitHubs1ko/cve-2026-52616

Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
api-securityexploitationnetwork-security+1
1 month ago
CVE-2025-61777 preview

CVE-2025-61777

GitHub0x0w1z/cve-2025-61777

CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
api-securityexploitationpenetration-testing+2
21 year ago
CVE-2025-62727-Demo preview

CVE-2025-62727-Demo

GitHubch4n3-yoon/cve-2025-62727-demo

Proof of concept of CVE-2025-62727 that can cause denial-of-service in FastAPI (based Starlette <= 0.48.0)
api-securityexploitationvulnerability-analysis+1
111 months ago
CVE-2025-67923 preview

CVE-2025-67923

GitHubrandomrobbiebf/cve-2025-67923

JetEngine <= 3.7.7 — Unauthenticated Stored Cross-Site Scripting via CCT REST API
api-securityexploitationvulnerability-analysis+2
7 months ago
CVE-2021-45232 preview

CVE-2021-45232

GitHubdskho/cve-2021-45232

Proof-of-concept scanner for CVE-2021-45232, targeting unauthenticated API access and default credentials in Apache APISIX Dashboard.
api-securityexploitationmisconfiguration+2
4 years ago
MicroserviceCVE-2021-39156 preview

MicroserviceCVE-2021-39156

GitHubmostafaanouarghorab/microservicecve-2021-39156
api-securityexploitationpenetration-testing+3
6 months ago
CVE-2019-11287 preview

CVE-2019-11287

GitHubmbadanoiu/cve-2019-11287

CVE-2019-11287: DoS via Heap Overflow in RabbitMQ Web Management Plugin
api-securityexploitationvulnerability-analysis+1
1 year ago
CVE-2025-30144 preview

CVE-2025-30144

GitHubtibrn/cve-2025-30144

Proof-of-concept for CVE-2025-30144: JWT issuer validation bypass in fast-jwt library allowing attackers to forge tokens with array-based iss claims.
api-securityauthenticationexploitation+3
1 year ago
SwaggerUI-CVE-2016-1000229 preview

SwaggerUI-CVE-2016-1000229

GitHubbarteeees/swaggerui-cve-2016-1000229

CVE-2016-1000229
api-securityexploitationpenetration-testing+2
1 year ago
shadowd preview
Archived

shadowd

GitHubzecure/shadowd

The Shadow Daemon web application firewall server

api-securitydefensive-toolsintrusion-detection+3
3053 years ago
Previous12345Next