
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
497 results
CVE-2026-67598 preview

CVE-2026-67598

GitHubilhomjonr/cve-2026-67598

CVE-2026-67598 — Emlog Pro: disabled TLS certificate validation in AI assistant (MITM → API-key theft). CWE-295, CVSS 9.1. Reported by @IlhomjonR.

ai-securityapi-securitycode-analysis+3
2 months ago
CVE-2026-64849 preview

CVE-2026-64849

GitHubbiutrap/cve-2026-64849

Proof-of-concept exploit for CVE-2026-64849: triggers SSRF in MLflow webhook API via crafted POST, fetching cloud instance metadata from…

api-securitycloud-securityexploitation+4
2 months ago
CVE-2026-73519-WolfStack-PoC preview

CVE-2026-73519-WolfStack-PoC

GitHubsqueeze440/cve-2026-73519-wolfstack-poc

PoC for CVE-2026-73519 - WolfStack hardcoded cluster secret leads to unauthenticated RCE (CVSS 9.8)

api-securityauthenticationcontainer-security+3
2 months ago
CVE-2026-18953 preview

CVE-2026-18953

GitHubronamosa/cve-2026-18953

PoC for CVE-2026-18953 — arbitrary file write (CWE-22) in awslabs.aws-transform-mcp-server's get_resource tool via the savePath parameter
api-securityexploitationpenetration-testing+1
2 months ago
CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field preview

CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field

GitHubtheopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field

Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)

ai-securityapi-securityexploitation+3
3 months ago
CVE-2026-72585-PoC preview

CVE-2026-72585-PoC

GitHubnel-droid/cve-2026-72585-poc

PoC: Grafana Editor role deletes protected contact points (CVE-2026-72585, Medium 6.5)
api-securityauthentication-authorizationexploitation+2
2 months ago
CVE-2021-44103 preview

CVE-2021-44103

GitHubpaulotrindadec/cve-2021-44103

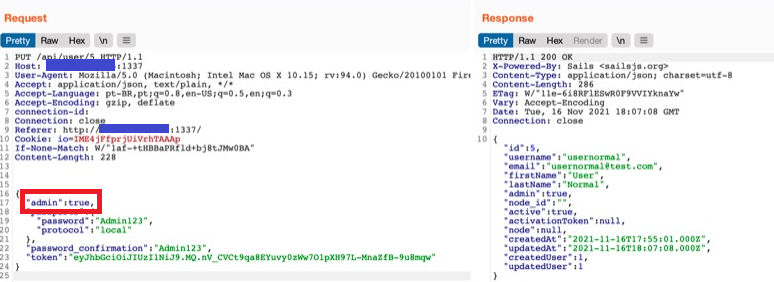
Proof-of-concept exploit for CVE-2021-44103 demonstrating vertical privilege escalation in Konga API Gateway 0.14.9, allowing authenticated users to…

api-securityexploitationpenetration-testing+3
34 years ago
pasteguard-PoC preview

pasteguard-PoC

GitHubsqueeze440/pasteguard-poc

PoC — cross-origin proxy abuse of configured provider API keys in PasteGuard (GHSA-q94x-p9rc-q89f, CVE-2026-86998, CVSS 7.6).
api-securityexploitationpapers-research+3
1 month ago
EITS-Portal-Exploit-CVE-2026-31367-PoC preview

EITS-Portal-Exploit-CVE-2026-31367-PoC

GitHubhereticl1nk/eits-portal-exploit-cve-2026-31367-poc

PoC exploit for unauthenticated RCE in EITS Admin Dashboard v2.4.0 via command injection in /api/v1/debug, allowing arbitrary OS command execution on…
api-securityexploitationpenetration-testing+2
2 months ago
Azure-APIM-Dev-Portal-Signup-Bypass preview

Azure-APIM-Dev-Portal-Signup-Bypass

GitHubdz-y/azure-apim-dev-portal-signup-bypass

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

api-securityapi-security-testingauthentication-authorization+6
3 months ago
inference-gateway-PoC preview

inference-gateway-PoC

GitHubsqueeze440/inference-gateway-poc

PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).

api-securityauthenticationexploitation+3
1 month ago
joomla_CVE-2023-23752 preview

joomla_CVE-2023-23752

GitHubvulnmachines/joomla_cve-2023-23752

Joomla! 4.0.0 through 4.2.7. An improper access check allows unauthorized access to webservice endpoints.
api-securityexploitationinformation-gathering+3
33 years ago
Wildfire preview

Wildfire

GitHubdefineid/wildfire

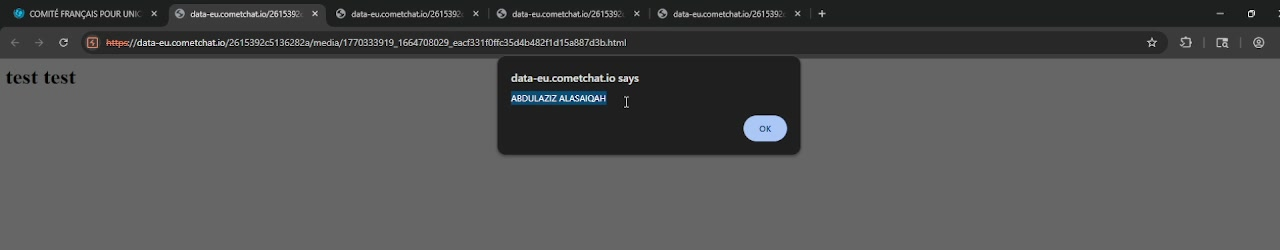
CVE-2026-39154, Stored XSS in CometChat JS SDK
api-securityexploitationpayload-development+4
2 months ago
CVE-2026-27344 preview

CVE-2026-27344

GitHubac8999/cve-2026-27344

Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…

api-securityauthentication-authorizationmisconfiguration+3
2 months ago
CVE-2026-71203-PoC preview

CVE-2026-71203-PoC

GitHubnel-droid/cve-2026-71203-poc

PoC: changedetection.io unauthenticated OpenAPI schema disclosure (CVE-2026-71203, Medium 5.3)

api-securityapi-security-testingexploitation+4
2 months ago
Fix-CVE-2026-60137-CVE-2026-63030-in-wordpress preview

Fix-CVE-2026-60137-CVE-2026-63030-in-wordpress

GitHubmrmtwoj/fix-cve-2026-60137-cve-2026-63030-in-wordpress

CVE-2026-60137Temporary Emergency Mitigation for CVE-2026-60137 & CVE-2026-63030 (wp2shell)
api-securitycode-analysisdefensive-tools+3
3 months ago
sentrymcp preview

sentrymcp

GitHubzaydmulani09/sentrymcp

A static + runtime security scanner for MCP (Model Context Protocol) servers

ai-securityapi-securitymisconfiguration+3
2 months ago
secdim-assurance-drift-challenge preview

secdim-assurance-drift-challenge

GitHubfranklincg/secdim-assurance-drift-challenge

SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary

api-securityauthentication-authorizationctf+5
1 month ago
Previous1…232425…28Next