keycloak__keycloak_CVE-2022-4137_20-0-3

Open source identity and access management solution providing single sign-on, user federation, and centralized authentication for modern applications…

Open source identity and access management solution providing single sign-on, user federation, and centralized authentication for modern applications…

Agent-based JMX access via JSON/HTTP with bulk requests, fine-grained security policies, and proxy mode for remote MBeanServer monitoring and…

A vulnerability scanner that detects CVE-2021-45232 vulnerabilities.

A vulnerability scanner that detects CVE-2021-37580 vulnerabilities.

Proof-of-concept for CVE-2025-492030: account takeover via session token validation bypass in SecureVPN API endpoint /api/v1/authenticate.

Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.

Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…

Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…

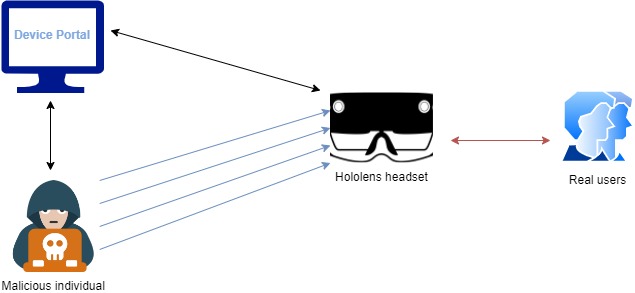
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.

Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

CVE-2019-11287: DoS via Heap Overflow in RabbitMQ Web Management Plugin

Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…

Apache ShenYu 管理员认证绕过

Proof-of-concept for CVE-2020-26527: demonstrates a CORS misconfiguration in Damstra Smart Asset 2020.7 API that trusts arbitrary origins, allowing…

Proof-of-concept for CVE-2025-30144: JWT issuer validation bypass in fast-jwt library allowing attackers to forge tokens with array-based iss claims.

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

CVE-2016-1000229