spring-cloud__spring-cloud-config_CVE-2020-5405_2-1-6-RELEASE

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.

Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…

Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…

Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…

Apache ShenYu 管理员认证绕过

CVE-2016-1000229

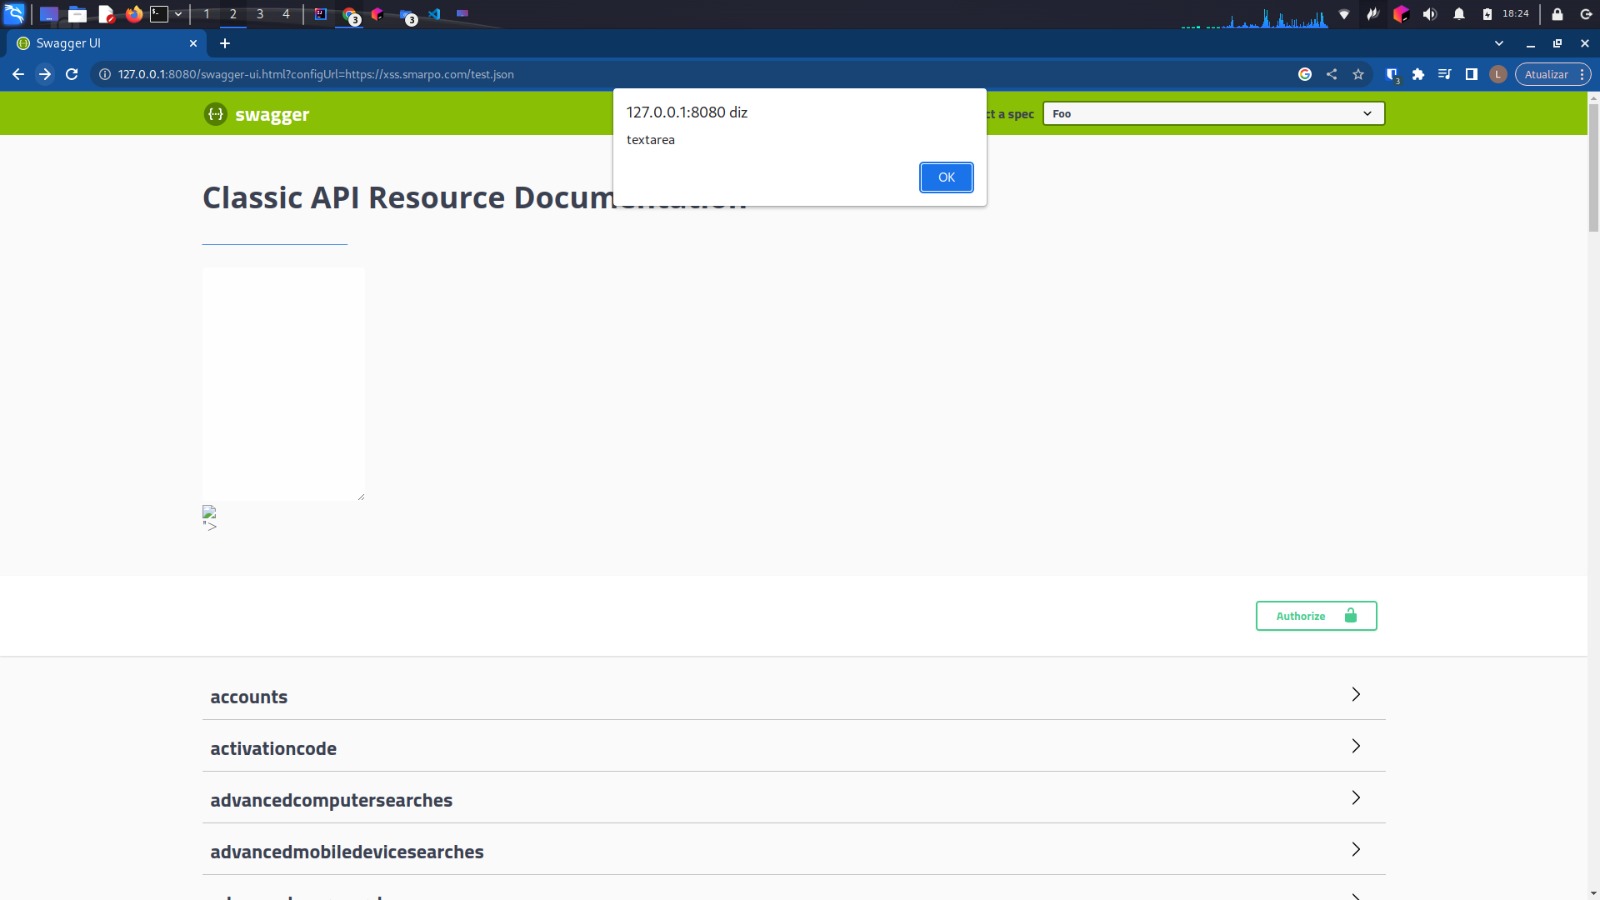
Python-based proof-of-concept script demonstrating CVE-2018-25031 XSS vulnerability in Swagger UI using Selenium for automated detection across…

Proof-of-concept for CVE-2020-26527: demonstrates a CORS misconfiguration in Damstra Smart Asset 2020.7 API that trusts arbitrary origins, allowing…

CVE-2016-4468

Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…

Open source integration framework for defining routing and mediation rules via DSLs (Java, XML, YAML) to connect various systems consuming or…

Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…

GraphQL vulnerability disclosure: CVE-2023-26144