
CVE-2026-71204-PoC
 nel-droid/cve-2026-71204-poc
PoC: changedetection.io settings blind-merge mass assignment (CVE-2026-71204, Medium 6.3)
api-securityauthentication-authorizationexploitation+2
nel-droid/cve-2026-71204-pocPoC: changedetection.io settings blind-merge mass assignment (CVE-2026-71204, Medium 6.3)
 biutrap/cve-2026-64849
Proof-of-concept exploit for CVE-2026-64849: triggers SSRF in MLflow webhook API via crafted POST, fetching cloud instance metadata from…
 nel-droid/cve-2026-72585-poc
PoC: Grafana Editor role deletes protected contact points (CVE-2026-72585, Medium 6.5)
 bsdrip/cve-2026-40179-poc
Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
 hereticl1nk/eits-portal-exploit-cve-2026-31367-poc
PoC exploit for unauthenticated RCE in EITS Admin Dashboard v2.4.0 via command injection in /api/v1/debug, allowing arbitrary OS command execution on…
 squeeze440/cve-2026-73519-wolfstack-poc
PoC for CVE-2026-73519 - WolfStack hardcoded cluster secret leads to unauthenticated RCE (CVSS 9.8)
 envincion1991-cmyk/cve-2026-51954
Vulnerability Research
 theopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field
Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)
 squeeze440/inference-gateway-poc
PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
 nel-droid/cve-2026-71203-poc
PoC: changedetection.io unauthenticated OpenAPI schema disclosure (CVE-2026-71203, Medium 5.3)
 ronamosa/cve-2026-18953
PoC for CVE-2026-18953 — arbitrary file write (CWE-22) in awslabs.aws-transform-mcp-server's get_resource tool via the savePath parameter
 squeeze440/pasteguard-poc
PoC — cross-origin proxy abuse of configured provider API keys in PasteGuard (GHSA-q94x-p9rc-q89f, CVE-2026-86998, CVSS 7.6).
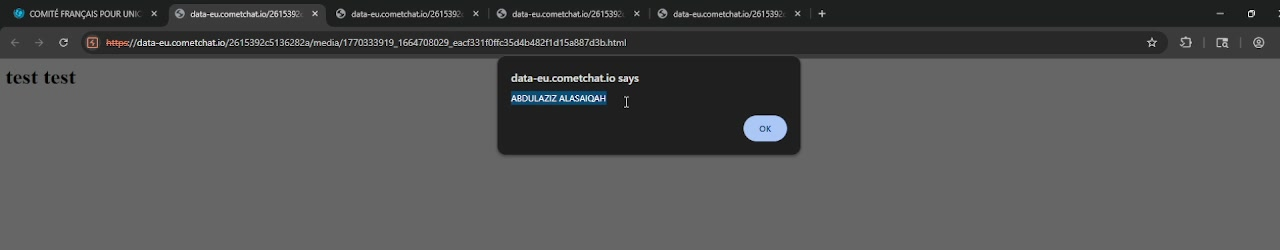 defineid/wildfire
CVE-2026-39154, Stored XSS in CometChat JS SDK
 zaydmulani09/sentrymcp
A static + runtime security scanner for MCP (Model Context Protocol) servers
 randomrobbiebf/super-secret-finder
Burp Plugin for Secret Matching
 cyberency/cve-2025-6514
mcp-remote exposed to OS command injection
 k3ystr0k3r/cve-2026-31816
CVE-2026-31816 - Budibase Authentication Bypass to RCE
 keraattin/cve-2026-33032
One missing function call on the route registration was enough to turn the MCP interface into an unauthenticated RCE gateway.