hapifhir__org_hl7_fhir_core_CVE-2023-28465_5-6-1055

Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…

Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…

Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…

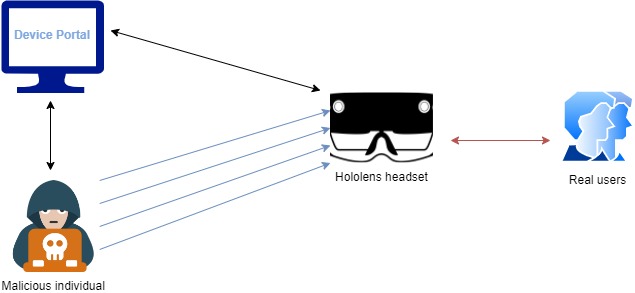
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.

CVE-2019-11287: DoS via Heap Overflow in RabbitMQ Web Management Plugin

Proof-of-concept for CVE-2025-30144: JWT issuer validation bypass in fast-jwt library allowing attackers to forge tokens with array-based iss claims.

Proof-of-concept for CVE-2020-26527: demonstrates a CORS misconfiguration in Damstra Smart Asset 2020.7 API that trusts arbitrary origins, allowing…

CVE-2016-1000229

Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch

Reference implementation of Bean Validation 2.0 (JSR-380) providing annotation-driven metadata model and API for JavaBean and method validation with…

GraphQL vulnerability disclosure: CVE-2023-26144

Operational security controls with forensic guarantees

Ruby templating system for generating JSON and XML APIs, with a fix for CVE-2014-4671. Supports partials, inheritance, and custom nodes for flexible…

CrowdStrike Feed Management System. CrowdFMS is a framework for automating collection and processing of samples from VirusTotal, by leveraging the…

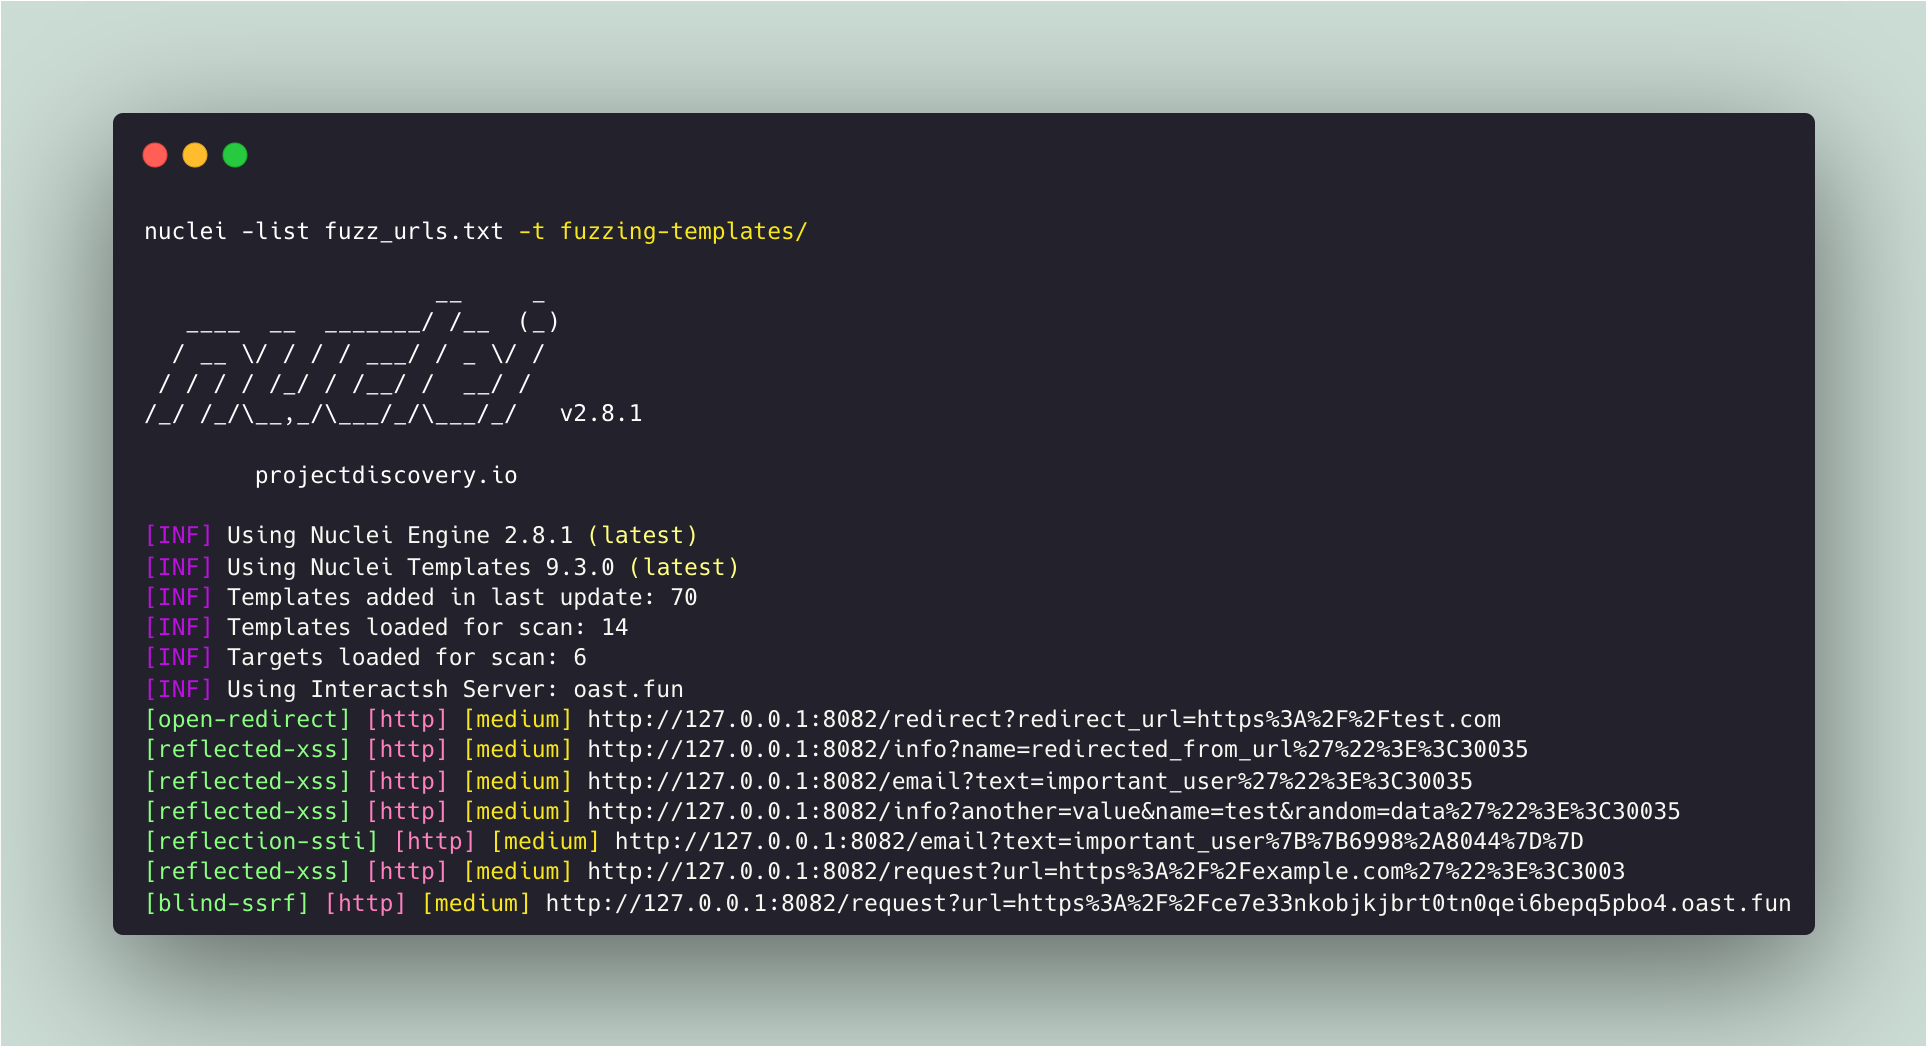
Community curated list of nuclei templates for finding "unknown" security vulnerabilities.

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

Secure local REST, CLI, MCP, and agent bridge for IDA Pro 9.x