CVE-2024-1208-and-CVE-2024-1210

Detailed disclosure of CVE-2024-1208 and CVE-2024-1210: sensitive information exposure via REST API in LearnDash WordPress plugin, allowing…

Detailed disclosure of CVE-2024-1208 and CVE-2024-1210: sensitive information exposure via REST API in LearnDash WordPress plugin, allowing…

4gaBoards < 3.3.9 - User Information Disclosure

Sensitive Information Exposure via assignments in LearnDash.

The code for personally reproducing the corresponding vulnerability

CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)

Enrolled agent can smuggle arbitrary OpenSearch _bulk operations via DataValue.index. GHSA-ff9g-85jq-r3g3. Draft

Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…

CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)

Axios CRLF Injection (CVE-2026-40175) 취약점 대응 가이드 및 fetch 기반 마이그레이션 분석

Proof-of-concept exploit for CVE-2026-30945, an IDOR in StudioCMS allowing arbitrary API token revocation and denial of service. Includes manual and…

Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…

Documents a high-severity ExaGrid EX10 MailConfiguration API access control flaw that leaks plaintext SMTP credentials to authenticated operators,…

Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…

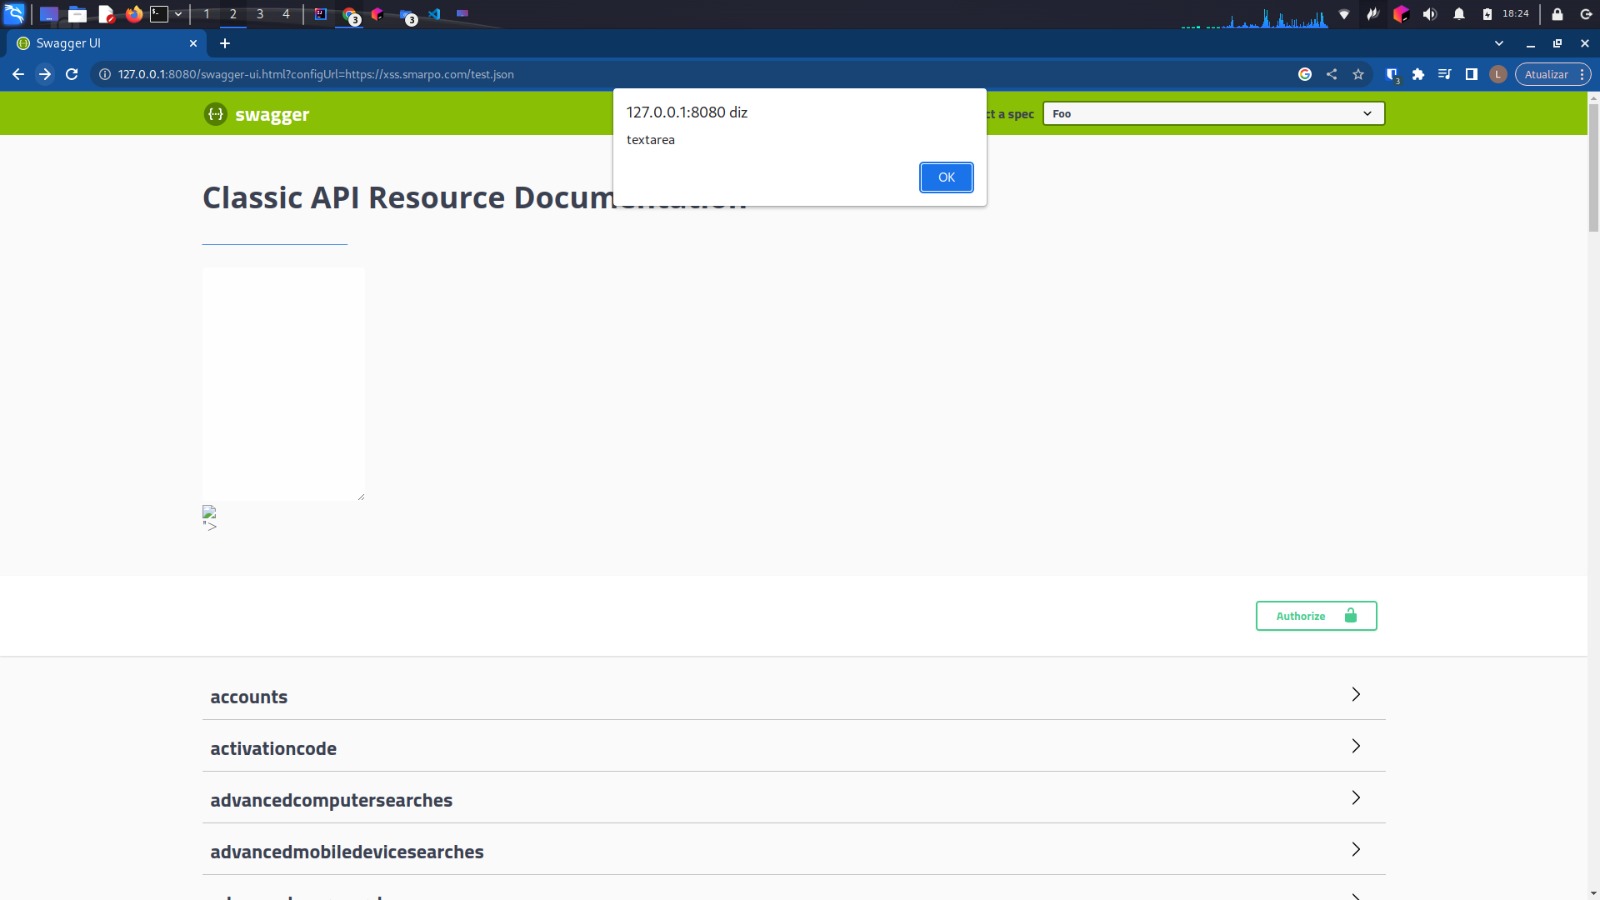
Python-based proof-of-concept script demonstrating CVE-2018-25031 XSS vulnerability in Swagger UI using Selenium for automated detection across…