fabric8io__kubernetes-client_CVE-2021-4178_5-0-2

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…

Open Source Identity and Access Management For Modern Applications and Services

Authorization library enforcing ACL, RBAC, ABAC, and custom access-control models with RESTful matching and policy management APIs for applications…

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…

Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…

SecureCivic is a citizen-built, open source identity verification platform designed for SSA adoption. It replaces private data brokers with a secure,…

Open-source identity and access management solution providing authentication, user federation, single sign-on, and fine-grained authorization for…

Centralized configuration server for distributed systems with HTTP API, Git-backed storage, property encryption/decryption, and integration with…

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…

Lightweight Python library for obfuscating JWT payload values using XOR encryption with timestamp-based keys, preventing plaintext decoding of…

Proof-of-concept for CVE-2025-30144: JWT issuer validation bypass in fast-jwt library allowing attackers to forge tokens with array-based iss claims.

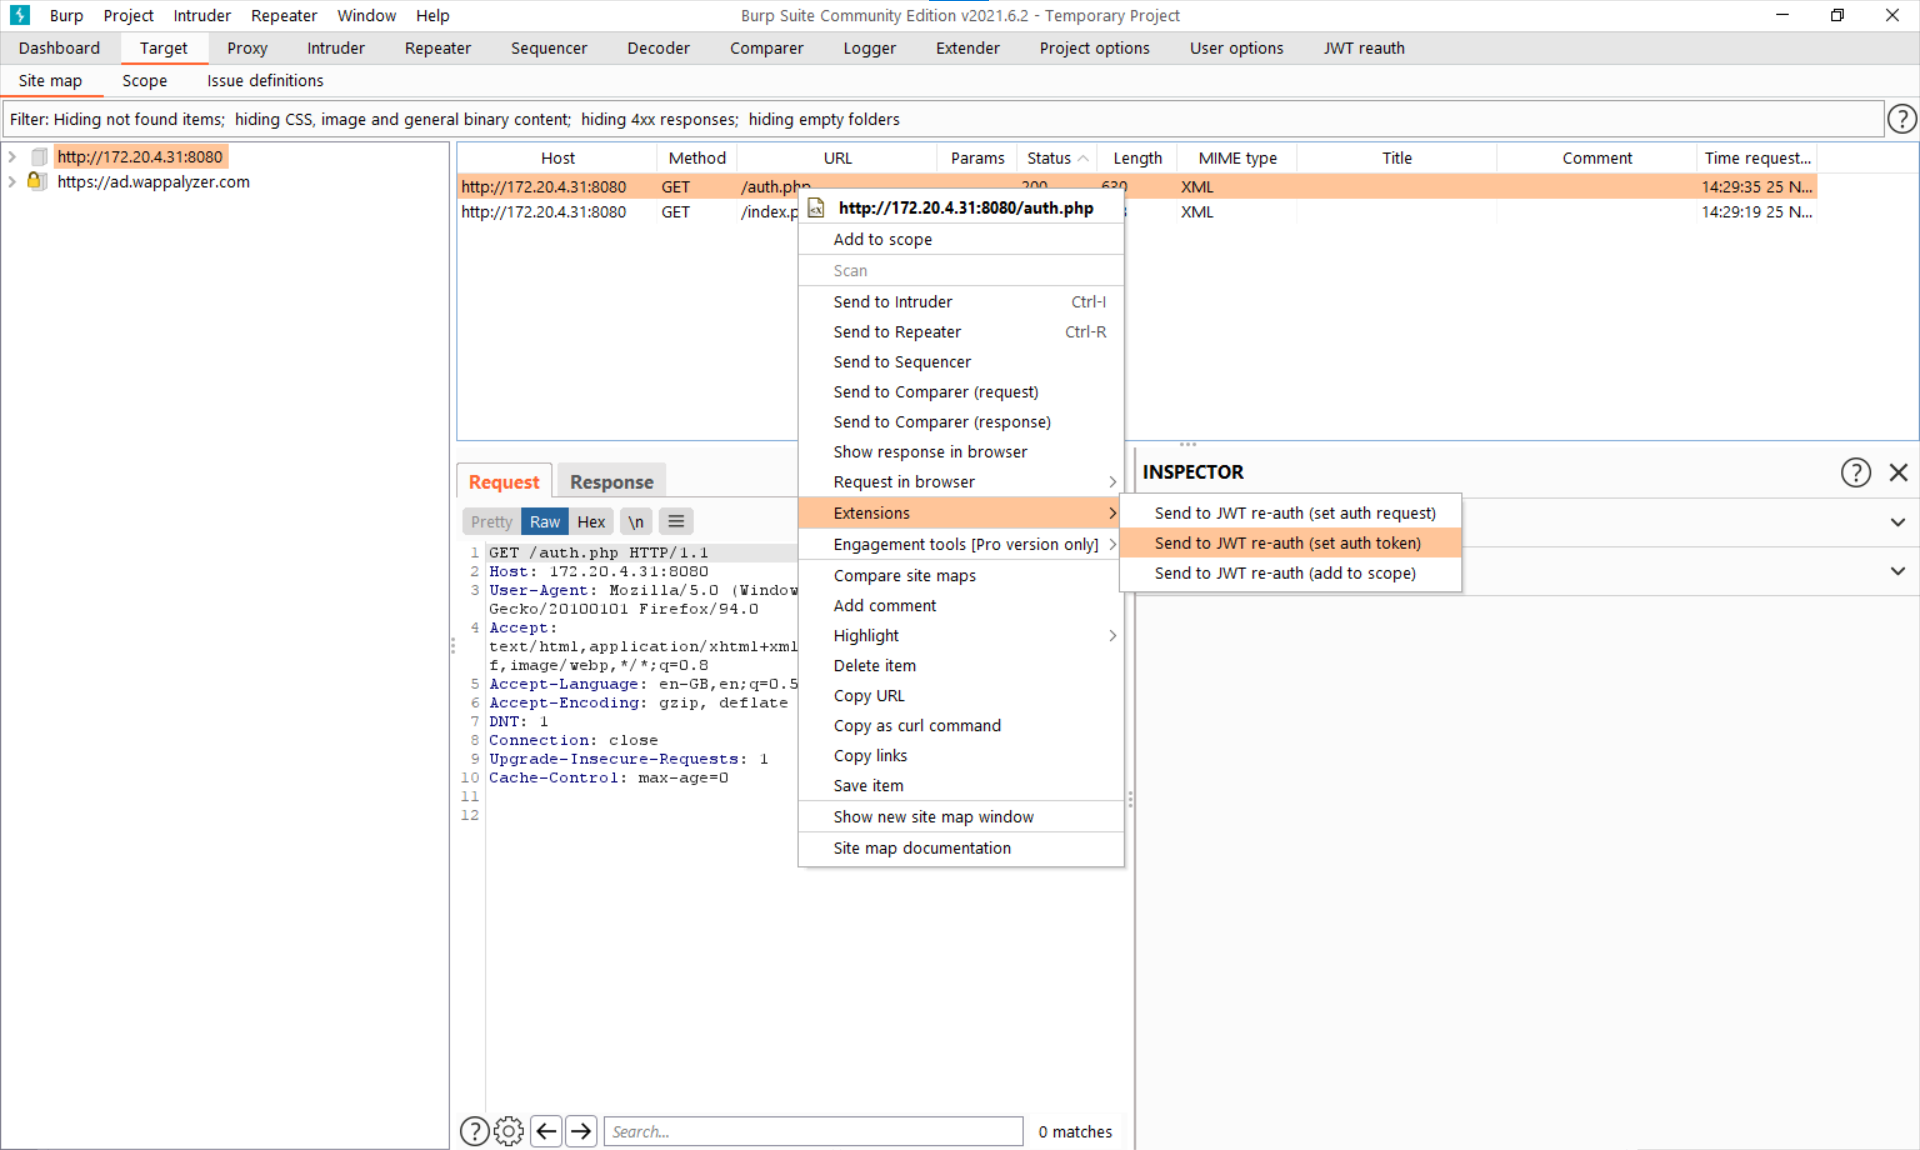
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.

🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…

Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.

Public reference for CVE-2025-56643 – Wiki.js 2.5.307 JWT Session Vulnerability