
wikipedia-c2
 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
api-securitycommand-and-controlexploitation+3
297 years ago
daniel-infosec/wikipedia-c2POC for utilizing wikipedia API for Command and Control
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 hunt-benito/the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass
Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…
 horkimhab/cve-2026-19650-cve-2026-19478
Proof-of-concept exploit resources for CVE-2026-19650 and CVE-2026-19478 targeting a GitLab GraphQL vulnerability, intended for authorized research,…
 sibikrish001/cve-2025-55462
Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…
 shoucheng3/springsource__spring-security-oauth_cve-2018-1260_2-3-2-release
OAuth and OAuth2 support library for Spring Security, enabling secure API authentication and authorization for consumer and provider implementations…
 shoucheng3/keycloak__keycloak_cve-2014-3656_1-0-5-final
Open-source identity and access management solution providing authentication, user federation, single sign-on, and fine-grained authorization for…
 shoucheng3/asf__cxf_cve-2019-17573_3-2-11
Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5405_2-1-6-release
Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…
 shoucheng3/asf__nifi_cve-2023-36542_1-22-0
Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…
 shoucheng3/asf__cxf_cve-2016-6812_3-0-11
Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.
 shoucheng3/hibernate__hibernate-validator_cve-2019-10219_6-0-17-final
Reference implementation of Bean Validation 2.0 (JSR-380) providing annotation-driven metadata model and API for JavaBean and method validation with…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 everywall/ladder
Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML
 gdatasoftwareag/vaas
Verdict-as-a-Service SDKs: Analyze files for malicious content
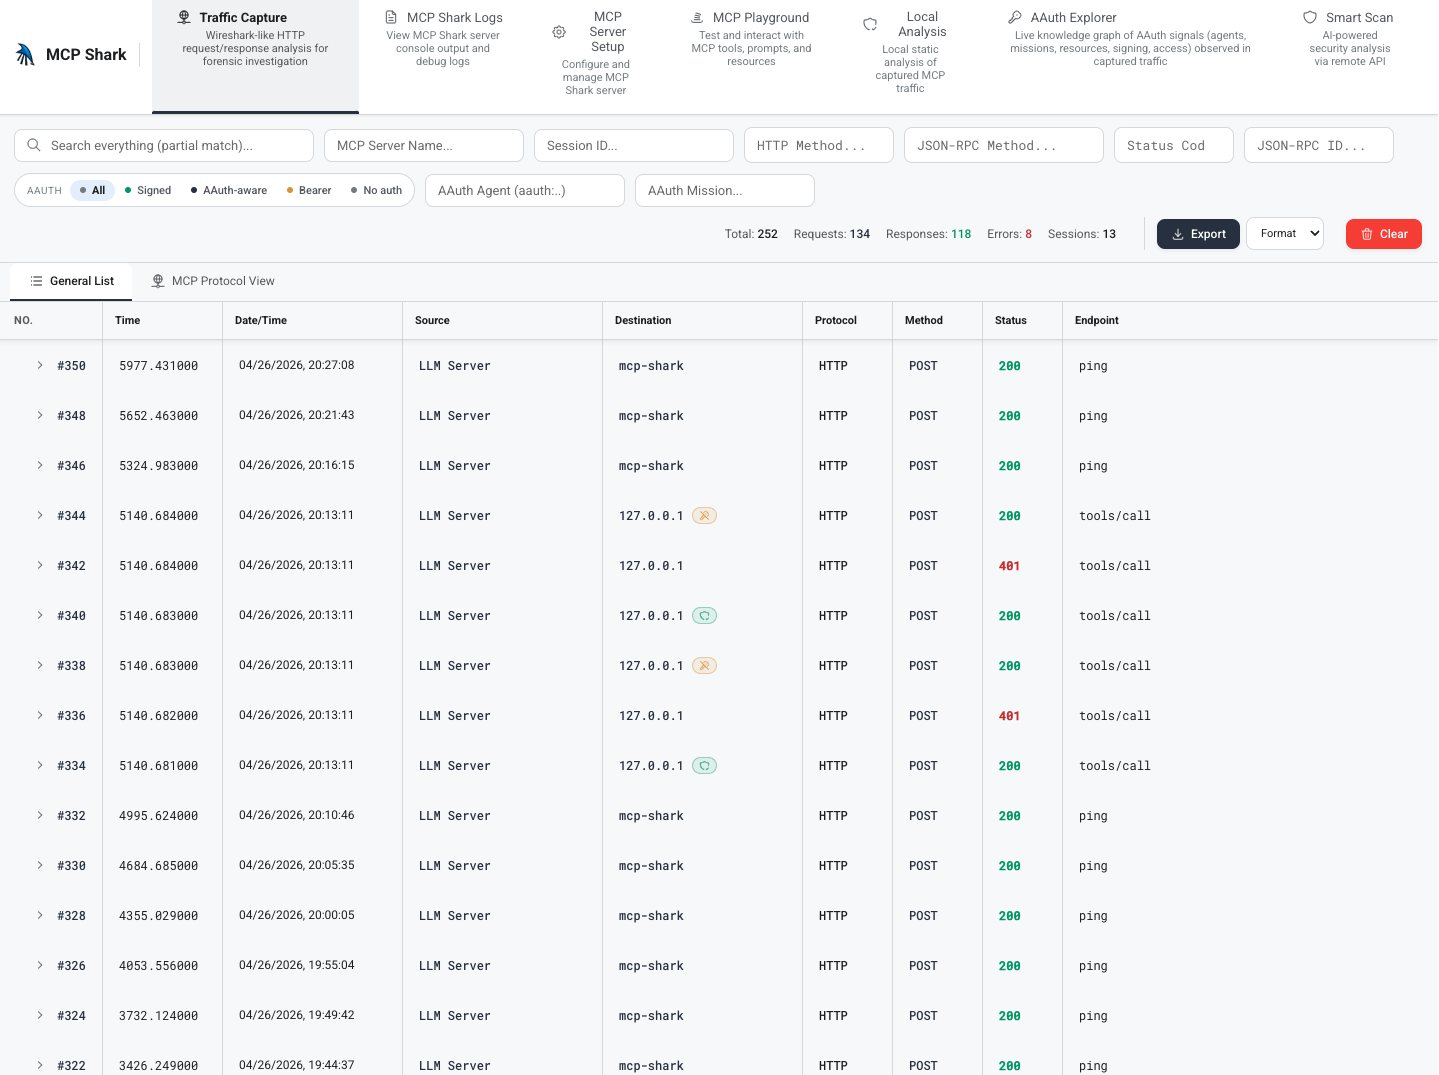 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 ackemed/cve-2026-1529-poc-keycloak-unauthorized-registration-via-improper-invitation-token-validation
Exploit tool for CVE-2026-1529, demonstrating unauthorized organization registration in Keycloak via JWT token manipulation. Includes token…
 shoucheng3/apache__sling-org-apache-sling-xss_cve-2016-5394_1-0-8
Java library providing XSS escaping and filtering services (XSSAPI, XSSFilter) to sanitize user-submitted content and prevent cross-site scripting…