
CVE-2026-53959
 anirbala98/cve-2026-53959
4gaBoards < 3.3.9 - User Information Disclosure
api-securityeducationexploitation+5
anirbala98/cve-2026-539594gaBoards < 3.3.9 - User Information Disclosure
 karlemilnikka/cve-2024-1209
Sensitive Information Exposure via assignments in LearnDash.
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
 horkimhab/cve-wazuh
Enrolled agent can smuggle arbitrary OpenSearch _bulk operations via DataValue.index. GHSA-ff9g-85jq-r3g3. Draft
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 leekanghyun/axios-security-guide
Axios CRLF Injection (CVE-2026-40175) 취약점 대응 가이드 및 fetch 기반 마이그레이션 분석
 filipegaudard/cve-2026-30945-poc
Proof-of-concept exploit for CVE-2026-30945, an IDOR in StudioCMS allowing arbitrary API token revocation and denial of service. Includes manual and…
 fevar54/cve-2025-4679-secureoauth-demo---enfoque-educativo
Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…
 0xsu3ks/cve-2025-29557
Documents a high-severity ExaGrid EX10 MailConfiguration API access control flaw that leaks plaintext SMTP credentials to authenticated operators,…
 shoucheng3/hapifhir__org_hl7_fhir_core_cve-2023-28465_5-6-1055
Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…
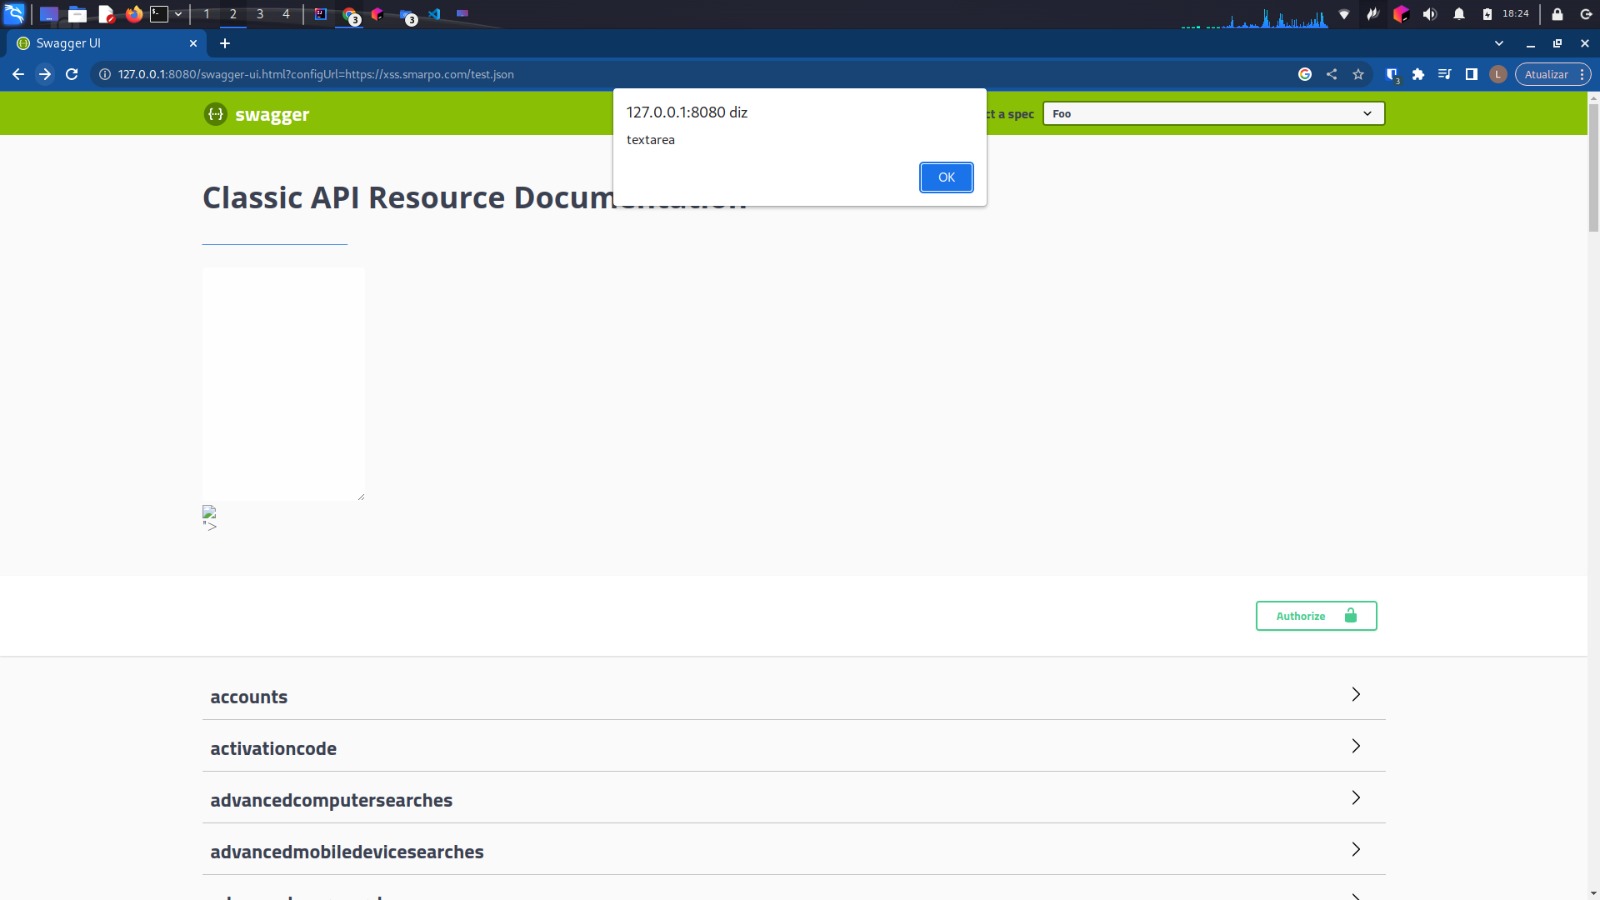 lucasrenaa/cve-2018-25031
Python-based proof-of-concept script demonstrating CVE-2018-25031 XSS vulnerability in Swagger UI using Selenium for automated detection across…