apache__camel_CVE-2018-8041_2-20-3

Open source integration framework for defining routing and mediation rules via DSLs (Java, XML, YAML) to connect various systems consuming or…

Open source integration framework for defining routing and mediation rules via DSLs (Java, XML, YAML) to connect various systems consuming or…

OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).

Ingress NGINX Controller for Kubernetes

Synapse: Matrix homeserver written in Python/Twisted.

NAXSI is an open-source, high performance, low rules maintenance WAF for NGINX

OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)

The Shadow Daemon web application firewall server

A wrapper of voku/anti-xss for Laravel

Pivotable Reverse WhoIs / PDNS Fusion with Registrant Tracking & Alerting plus API for automated queries (JSON/CSV/TXT)

NebulousAD automated credential auditing tool.

CrowdStrike Feed Management System. CrowdFMS is a framework for automating collection and processing of samples from VirusTotal, by leveraging the…

Modern Web Firewall: stop account takeovers, weak passwords, cloud IPs, DoS attacks, disposable emails

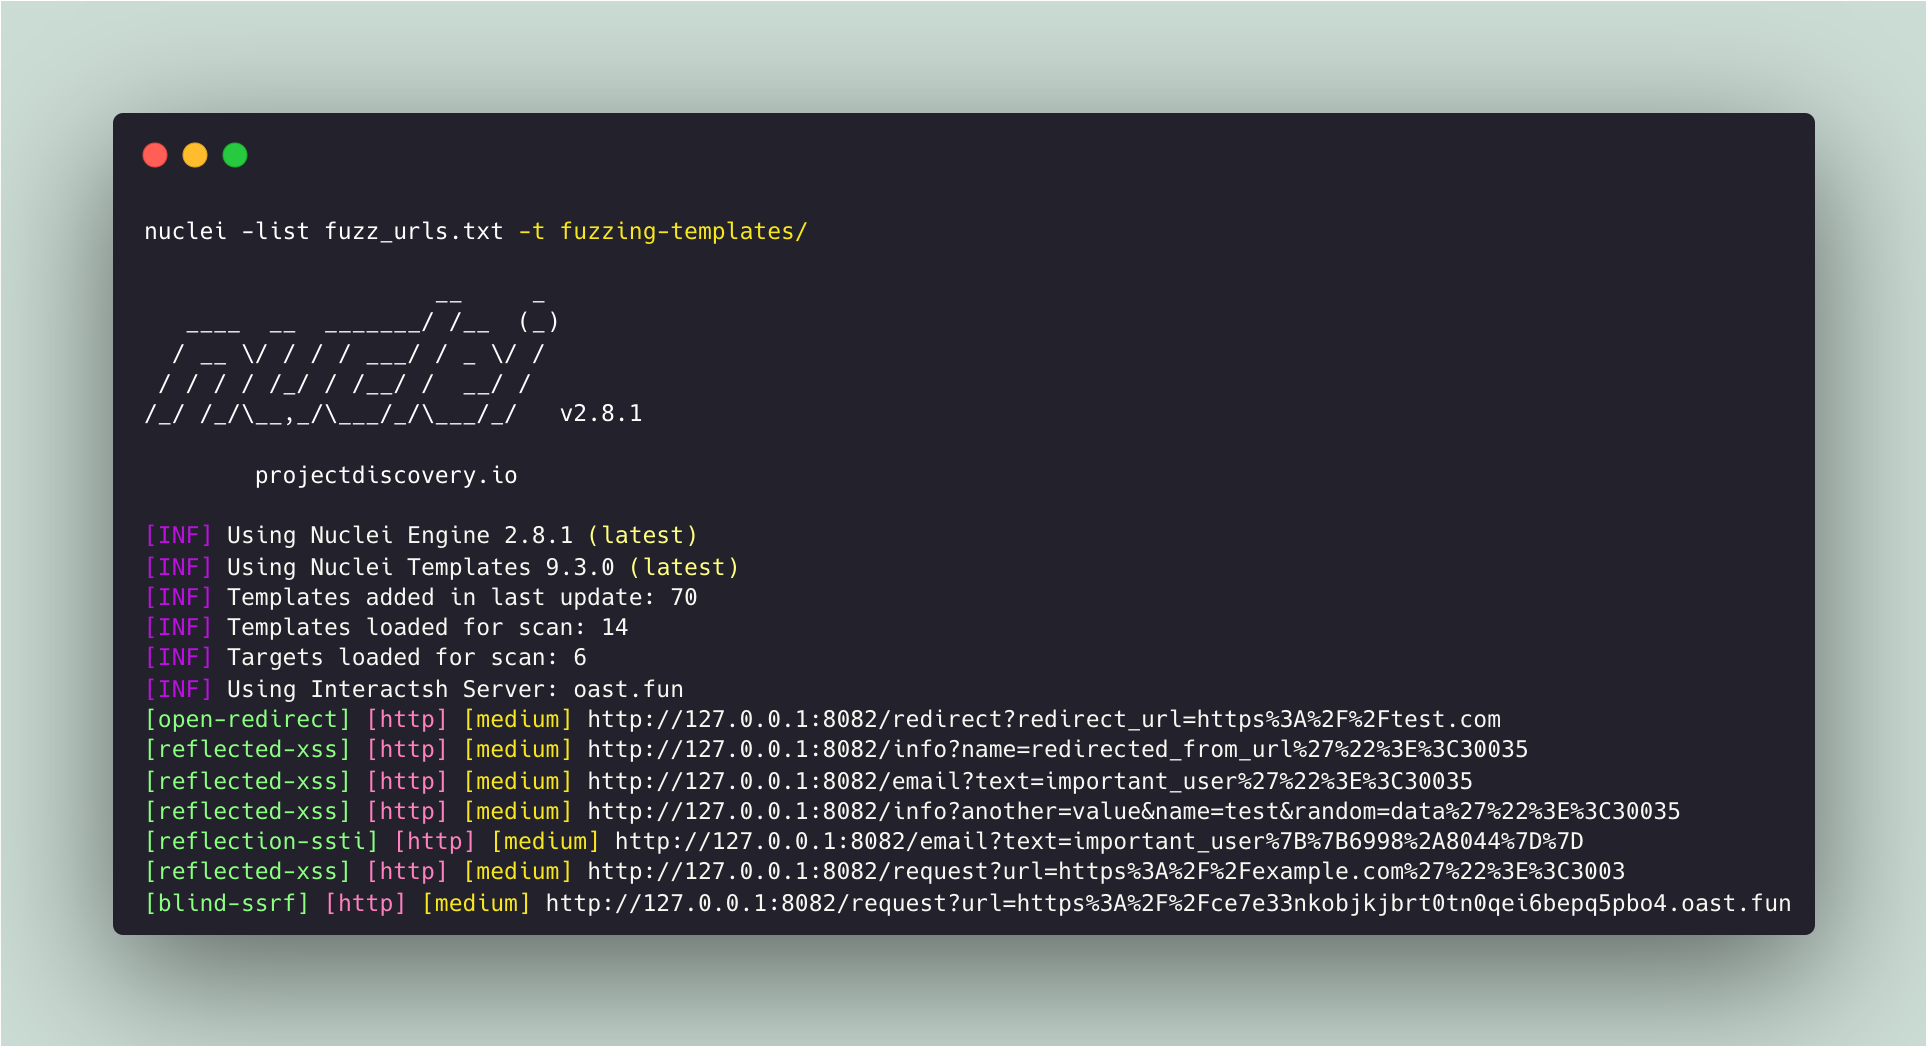
Community curated list of nuclei templates for finding "unknown" security vulnerabilities.

PowerShell Module for managing Microsoft Defender Advanced Threat Protection

EU focused compliance MCP server

CVE-2020-8554: Man in the middle using LoadBalancer or ExternalIPs

Ruby templating system for generating JSON and XML APIs, with a fix for CVE-2014-4671. Supports partials, inheritance, and custom nodes for flexible…

Operational security controls with forensic guarantees