
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
10 results
CVE-2026-76504-Proof-of-concept preview

CVE-2026-76504-Proof-of-concept

GitHubshadowforge-cyber/cve-2026-76504-proof-of-concept

EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)

api-securityauthenticationexploitation+5
2
7 days ago
zappzarapp-php-security preview

zappzarapp-php-security

GitLabmarcstraube/zappzarapp-php-security

PHP 8.4+ security library (mirror)
api-securityauthentication-authorizationcode-analysis+6
1 month ago
CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field preview

CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field

GitHubtheopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field

Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)
ai-securityapi-securityexploitation+3
2 months ago
CVE-2026-52217-VTEX-Checkout-CrossTenant-IDOR preview

CVE-2026-52217-VTEX-Checkout-CrossTenant-IDOR

GitHubteteco/cve-2026-52217-vtex-checkout-crosstenant-idor

The VTEX Checkout Service exposes OrderForm data through the endpoints `/api/checkout/pub/orderForm/{orderFormId}` and `/attachments/*`. These…
api-securityauthentication-authorizationinformation-gathering+3
3 months ago
openclaw-dashboard preview

openclaw-dashboard

GitHubtugcantopaloglu/openclaw-dashboard

🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
api-securityauthenticationcloud-security+7
7026 months ago
tetsuo-pulse preview

tetsuo-pulse

GitHub7etsuo/tetsuo-pulse

Tetsuo Socket Library

api-securitycryptographydns-analysis+6
707 months ago
CVE-2025-63667 preview

CVE-2025-63667

GitHubremenis/cve-2025-63667

Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…
api-securityauthenticationembedded-systems-security+4
110 months ago
CVE-2025-56643 preview

CVE-2025-56643

GitHub0xbs0d27/cve-2025-56643

Public reference for CVE-2025-56643 – Wiki.js 2.5.307 JWT Session Vulnerability
api-securityauthenticationexploitation+2
111 months ago
CVE-2025-492030 preview

CVE-2025-492030

GitHubimthecopilotnow/cve-2025-492030

Proof-of-concept for CVE-2025-492030: account takeover via session token validation bypass in SecureVPN API endpoint /api/v1/authenticate.
api-securityauthenticationexploitation+3
1 year ago
jwt-reauth preview

jwt-reauth

GitHubnccgroup/jwt-reauth

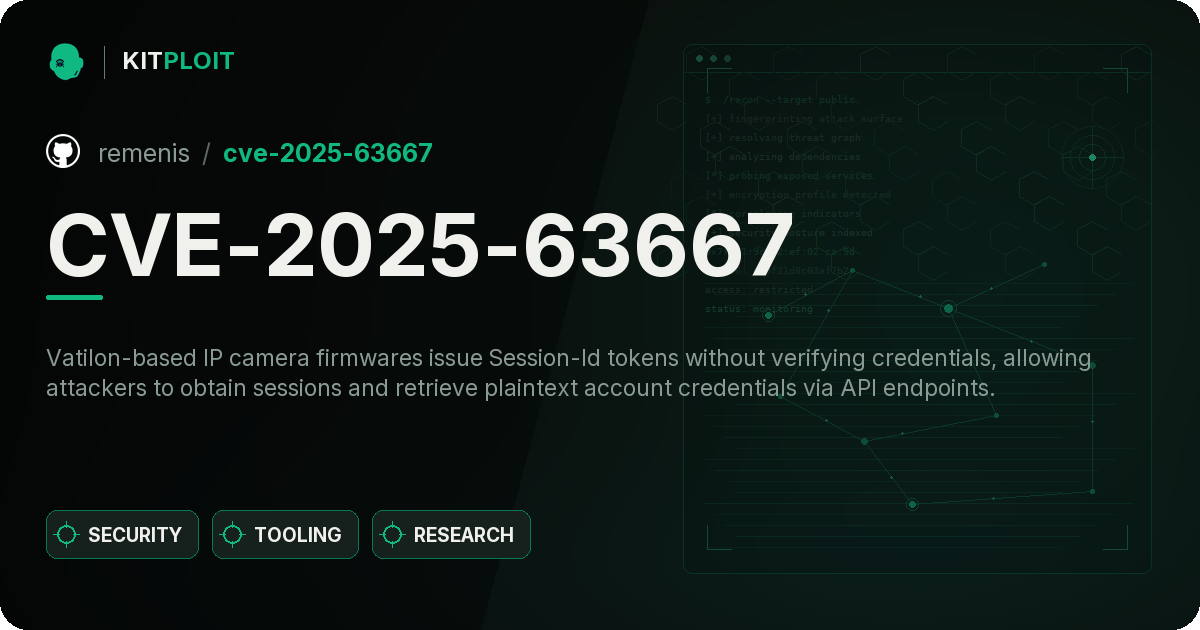
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.

api-securityauthenticationpenetration-testing+3
1063 years ago
