
PentestingEverything
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
api-securitycloud-securityctf+9
2.1k
m14r41/pentestingeverythingComplete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
 cappricio-securities/cappriciosec-university
A Hacker's E-learning App for Tamil People
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 bytesizedmarius/rewerse-engineering
Rewe API reverse engineering in Go
 itsc1sco/mcpjam-to-root
From MCPJam Inspector RCE to root — CVE-2026-23744, JupyterLab token disclosure, kernel execution, and OPSMCP privilege escalation
 trandonga3/poc-cve-2026-63030-cve-2026-60137-
Exploit chain for WordPress Core using REST API route-confusion and SQL injection for unauthenticated RCE, privilege escalation, and full server…
 anirbala98/cve-2026-53959
4gaBoards < 3.3.9 - User Information Disclosure
 horkimhab/cve-2026-19650-cve-2026-19478
Proof-of-concept exploit resources for CVE-2026-19650 and CVE-2026-19478 targeting a GitLab GraphQL vulnerability, intended for authorized research,…
 george0papasotiriou/cve-2026-3030-prototype-pollution-in-json-merge-patch
Demonstrates CVE-2026-3030 prototype pollution in a Node.js JSON merge patch REST API, including a vulnerable server and exploit script for privilege…
 horkimhab/cve-wazuh
Enrolled agent can smuggle arbitrary OpenSearch _bulk operations via DataValue.index. GHSA-ff9g-85jq-r3g3. Draft
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 securelayer7/promptpurify
Prompt-injection guardrail for LLM applications. Compact model that outperforms larger open-source guards. No regex, no signatures. Demo:…
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
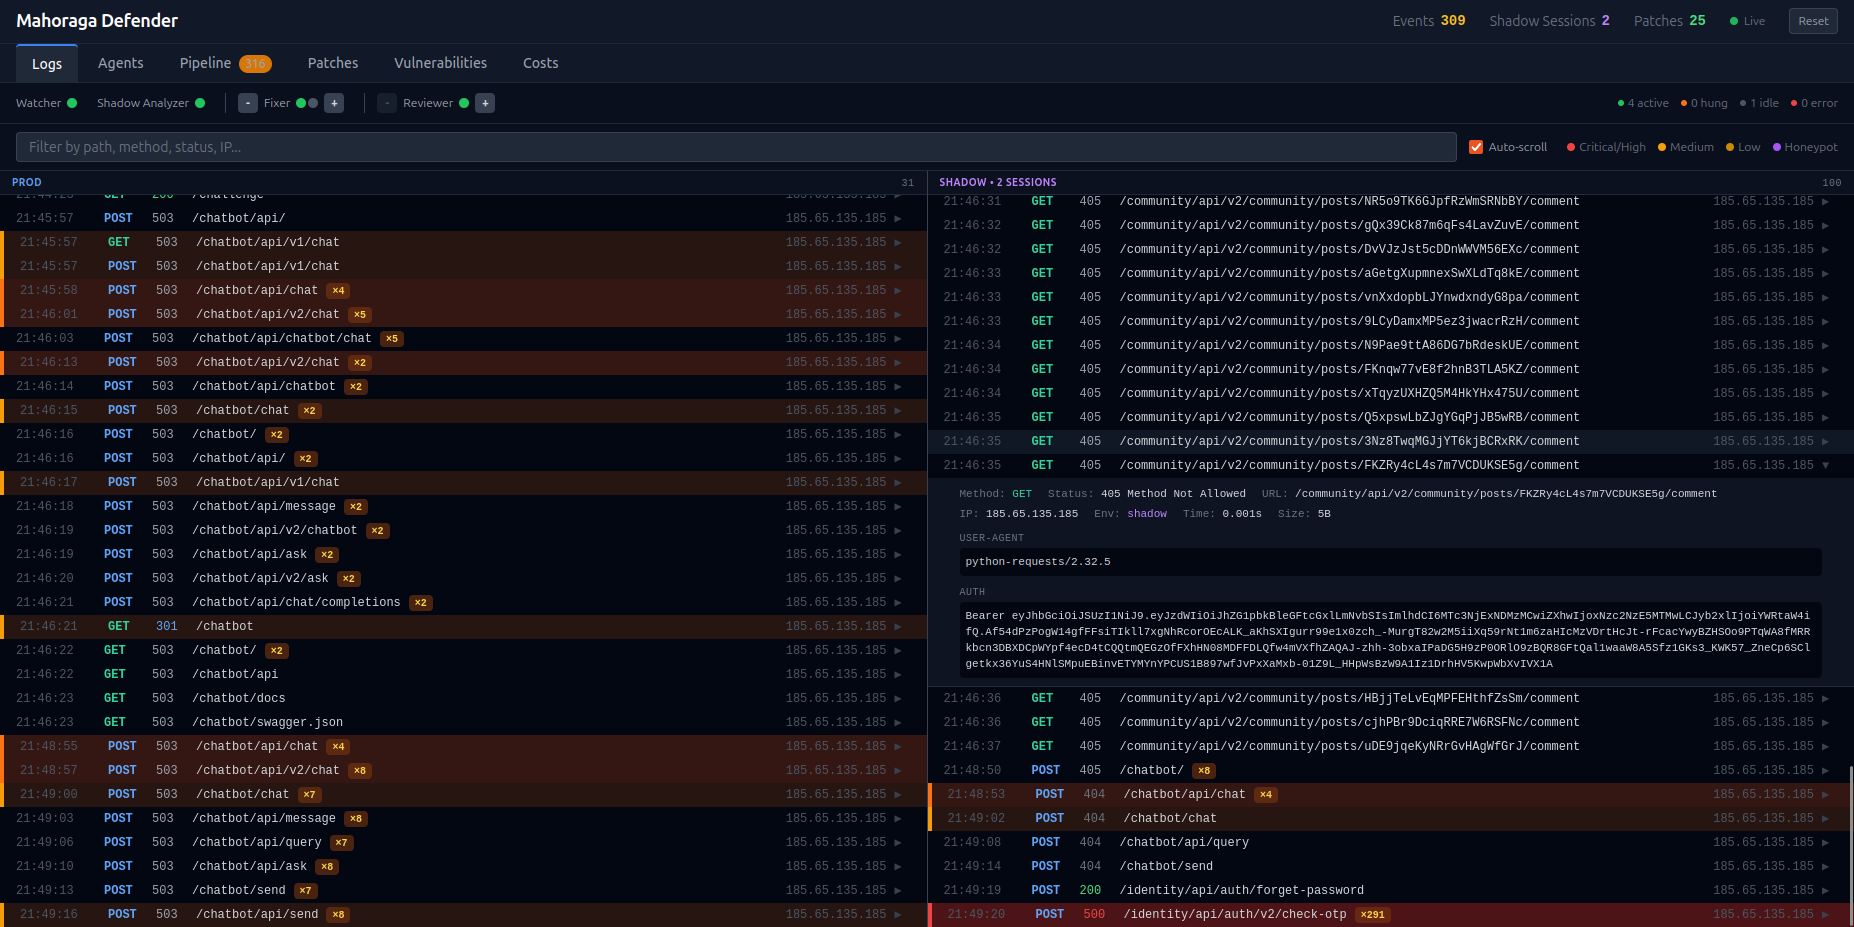 ageofalgorithms/mahoraga-webapp-defender
AI-powered reactive website defense system that detects attacks, analyzes them, and autonomously patches source code in real-time using LLM agents.
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 leekanghyun/axios-security-guide
Axios CRLF Injection (CVE-2026-40175) 취약점 대응 가이드 및 fetch 기반 마이그레이션 분석