
Wildfire
 defineid/wildfire
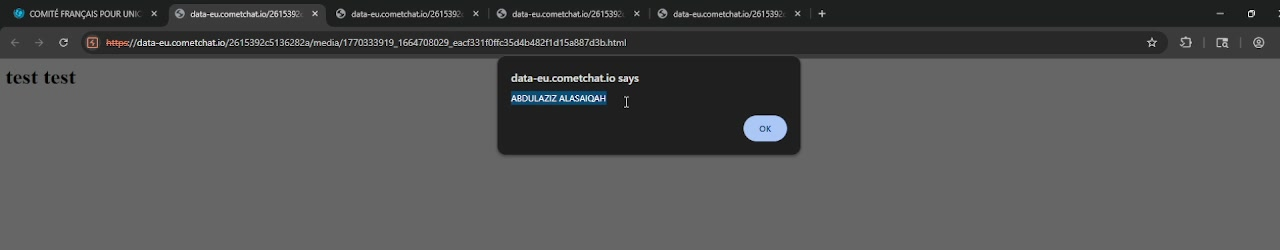
CVE-2026-39154, Stored XSS in CometChat JS SDK
api-securityexploitationpayload-development+4
defineid/wildfireCVE-2026-39154, Stored XSS in CometChat JS SDK
 sam00/poc-cve-2026-32621-apollo-federation-xss-vulnerability
PoC exploit for CVE-2026-32621 demonstrating Apollo Federation deepMerge prototype pollution via crafted GraphQL aliases, with patched-version tests.
 george0papasotiriou/cve-2026-21020-protobuf-message-parsing-polymorphic-deserialization-vulnerability
PoC for CVE-2026-21020, demonstrating Protobuf Any-type polymorphic deserialization where attacker-controlled type_url can lead to logic bugs, RCE,…
 george0papasotiriou/cve-2026-11103-graphql-batching-alias-rate-limit-bypass
Proof-of-concept exploit for CVE-2026-11103 demonstrating GraphQL rate-limit bypass through batching and field aliases; includes vulnerable Node.js…
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS