
DOMPurify
 cure53/dompurify
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
api-securitycode-analysisdefensive-tools+3
17.4k
cure53/dompurifyDOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 shadowforge-cyber/cve-2026-12944
Python PoC exploiting CVE-2026-12944, an SSRF in Langflow 1.10.0 via urllib in custom components, with authenticated read and fetch capabilities.
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 apache/casbin
Authorization library enforcing ACL, RBAC, ABAC, and custom access-control models with RESTful matching and policy management APIs for applications…
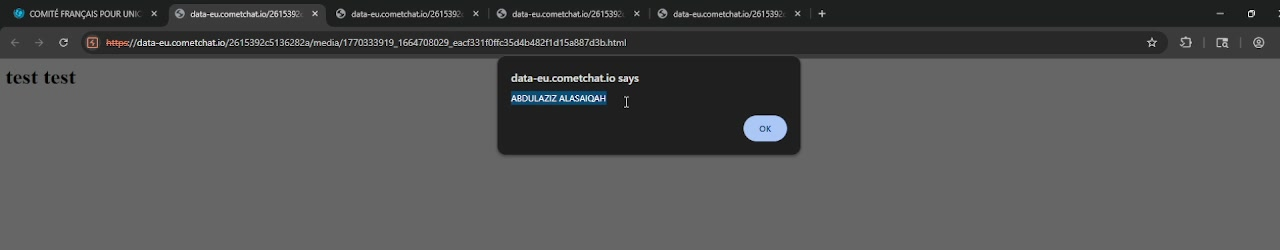 defineid/wildfire
CVE-2026-39154, Stored XSS in CometChat JS SDK
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 kaysec/hybrid-submit
A script that automatically submits files to Hybrid Analysis (API)
 wa6n3r/cve-2026-35616
Exploit script for CVE-2026-35616 that bypasses certificate chain verification in Fortinet API by discovering valid CNs, generating a forged client…
 vigil-xy/agent-scanning
Unified dashboard to monitor, govern, and audit AI agents in real-time. Enforce budgets, detect policy violations, and export compliance reports for…
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
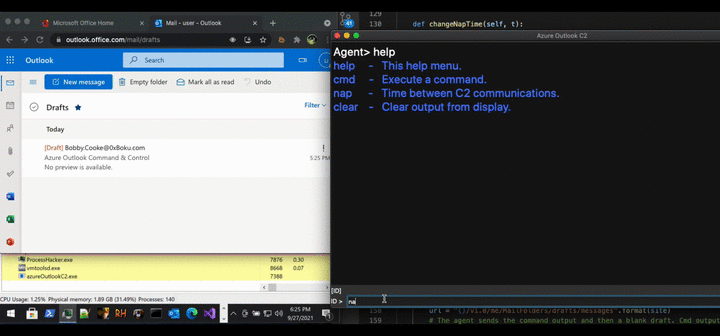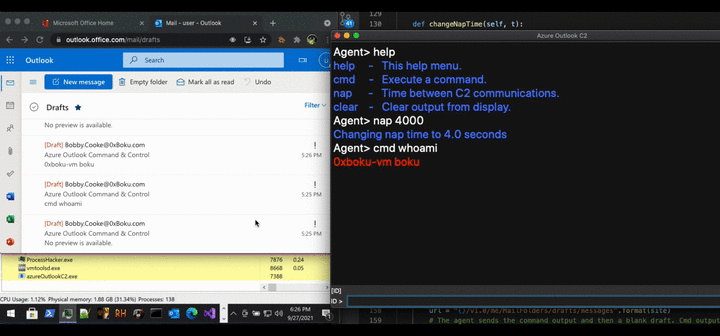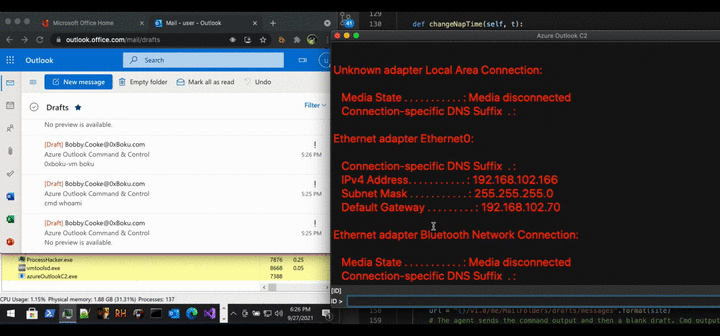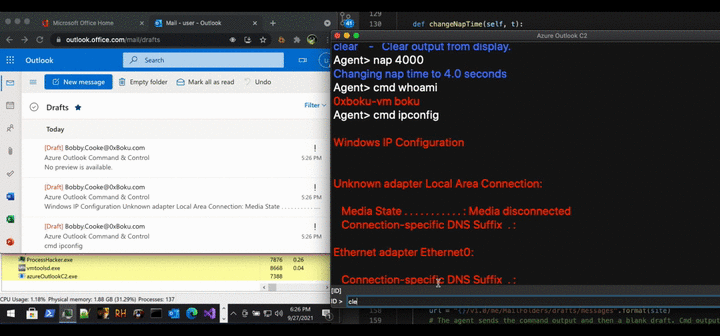 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…