
CVE-2025-6514
 cyberency/cve-2025-6514
mcp-remote exposed to OS command injection
api-securityauthenticationcommand-and-control+3
cyberency/cve-2025-6514mcp-remote exposed to OS command injection
 oh-az/noargs
Windows API hooking tool that dynamically spoofs and conceals process arguments via Detours library and PEB manipulation, enabling stealthy process…
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
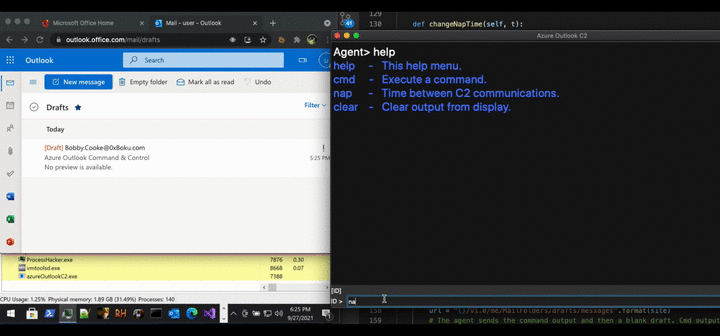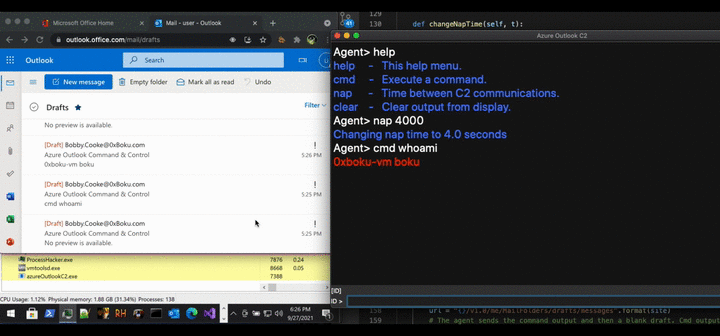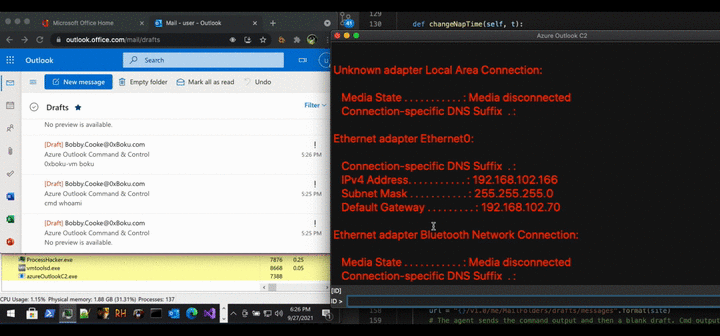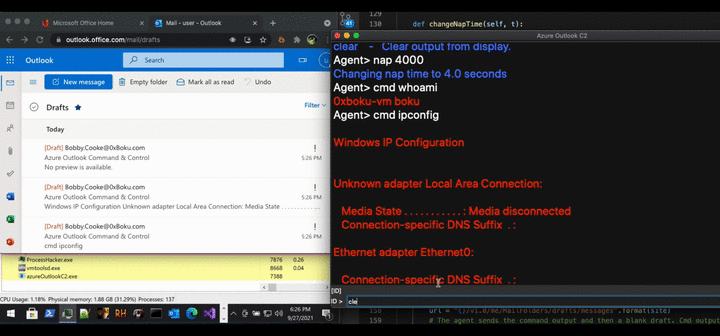 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 acczdy/cve-2022-24112_poc
CVE-2022-24112_POC
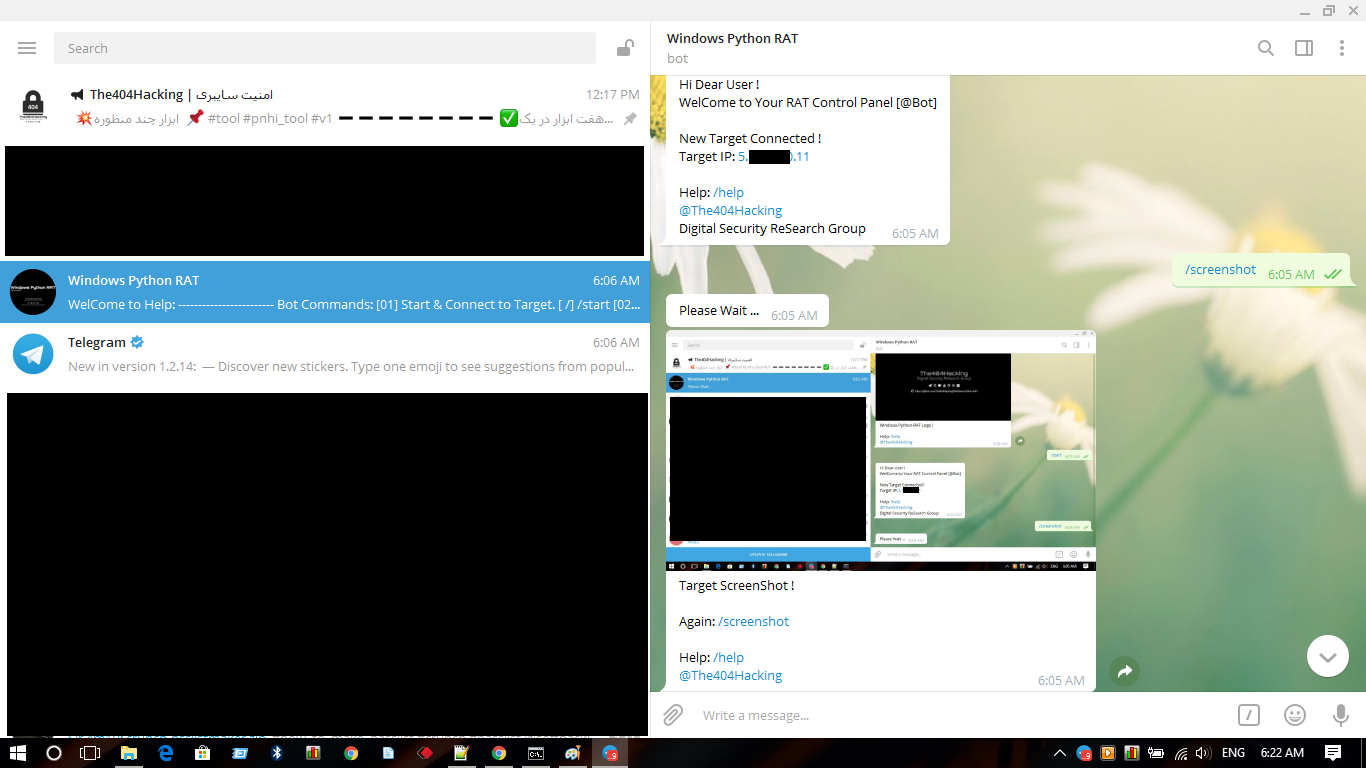 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
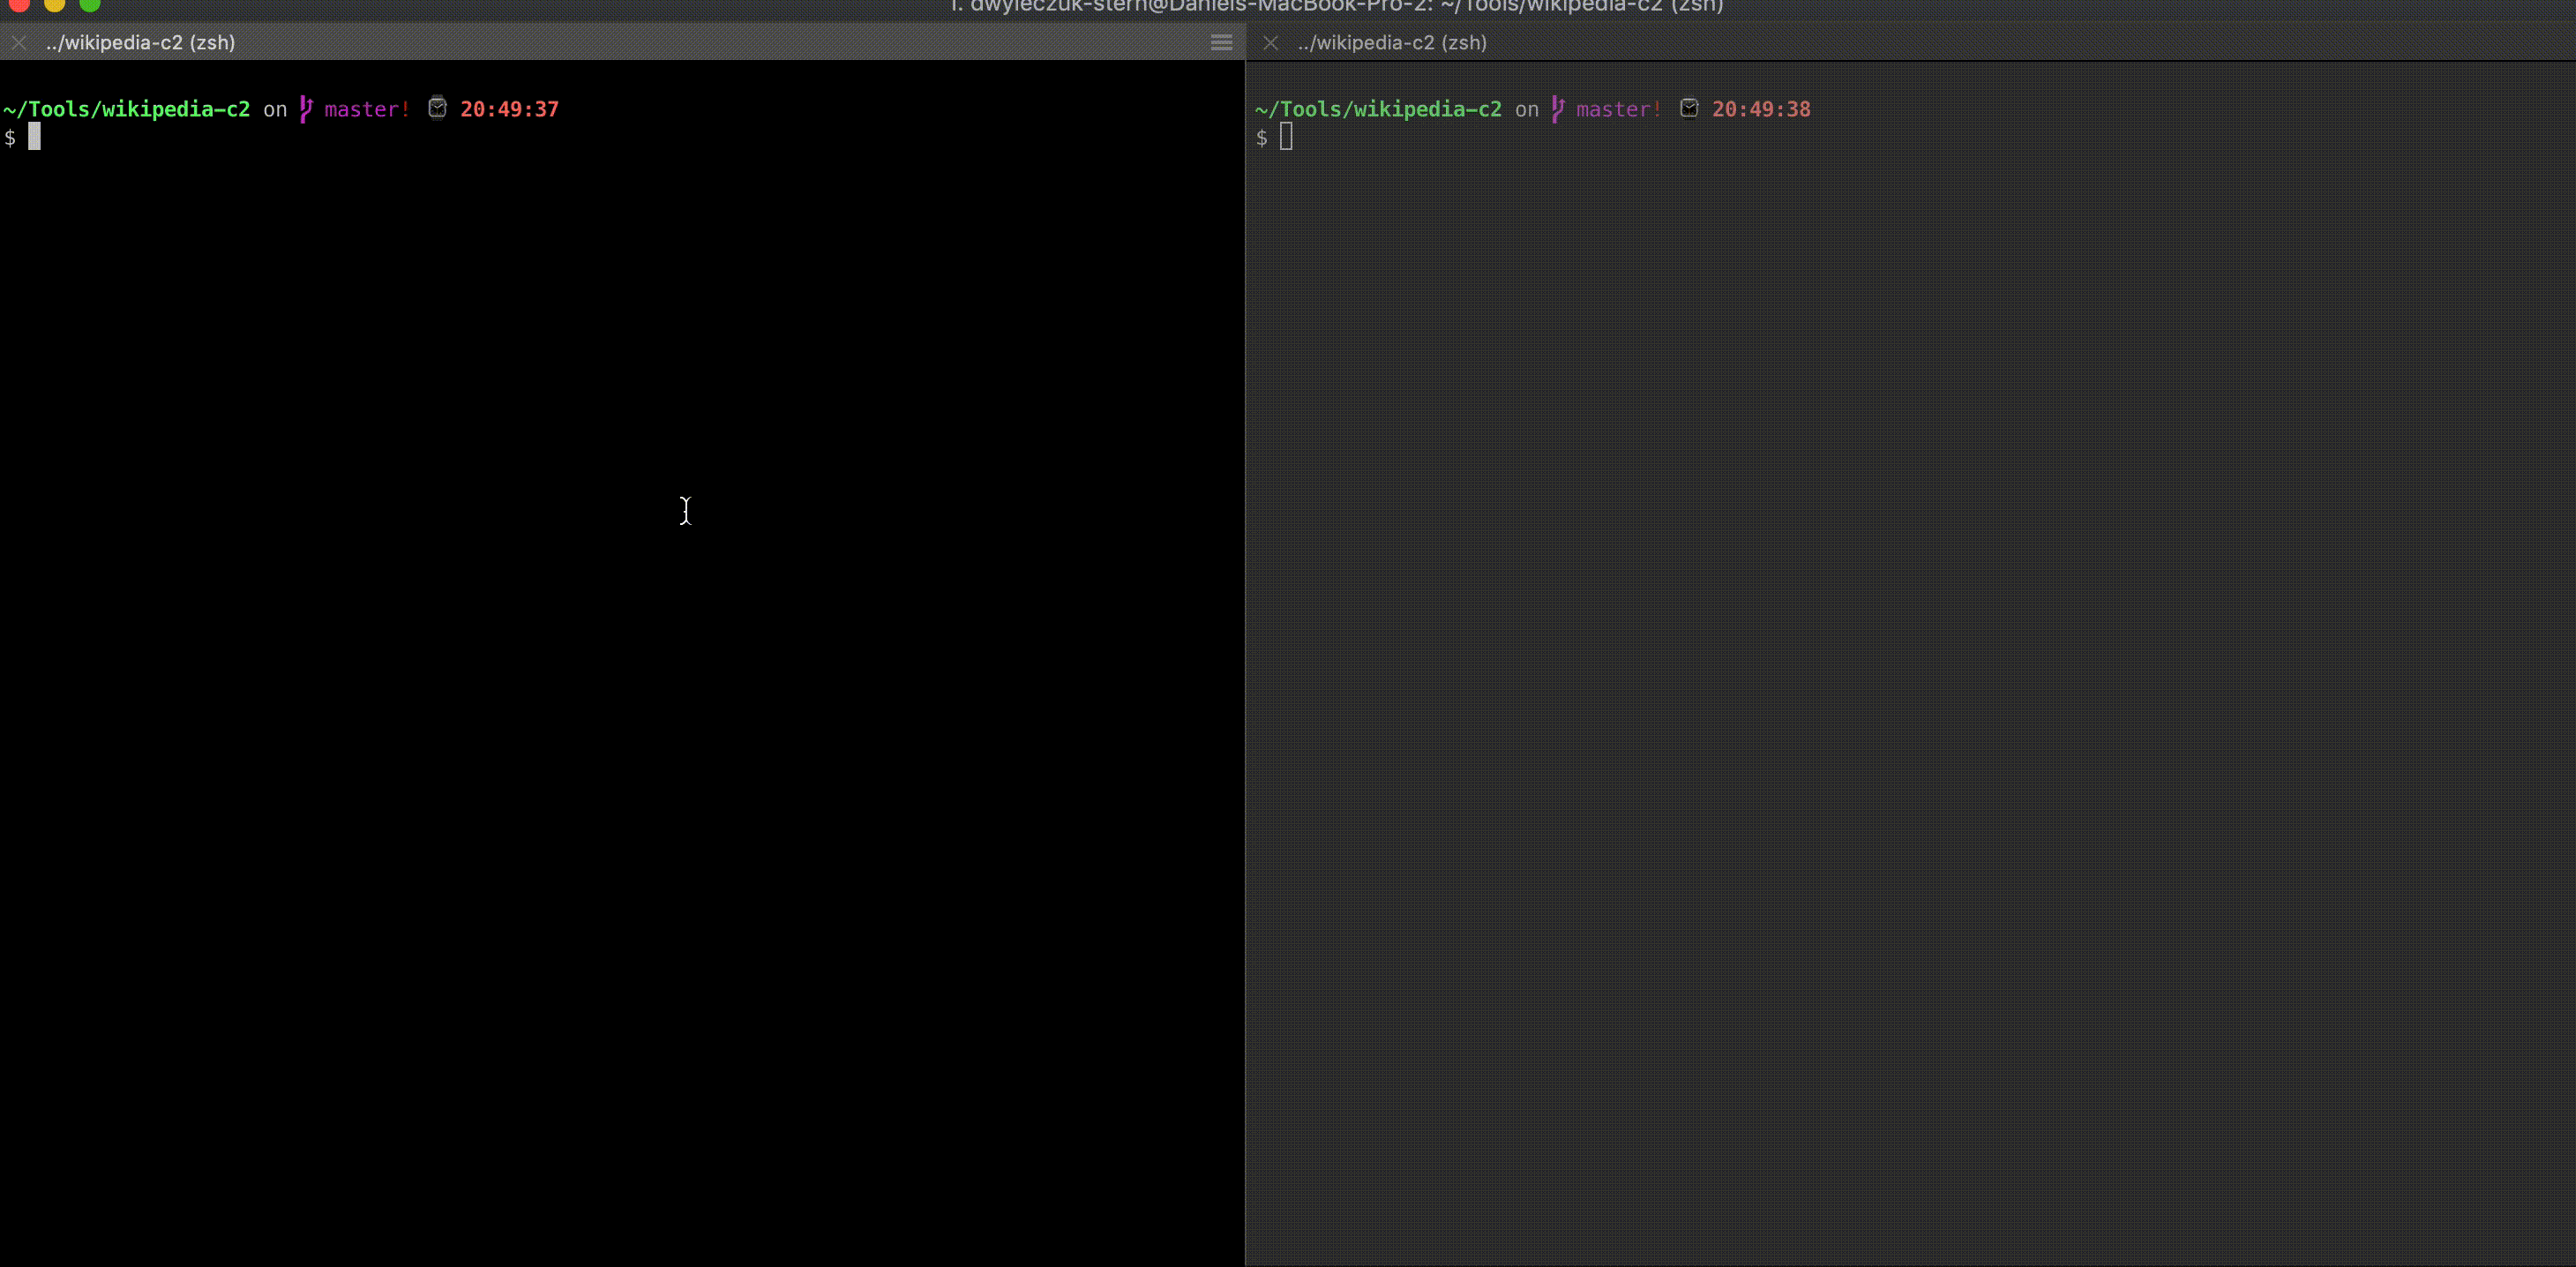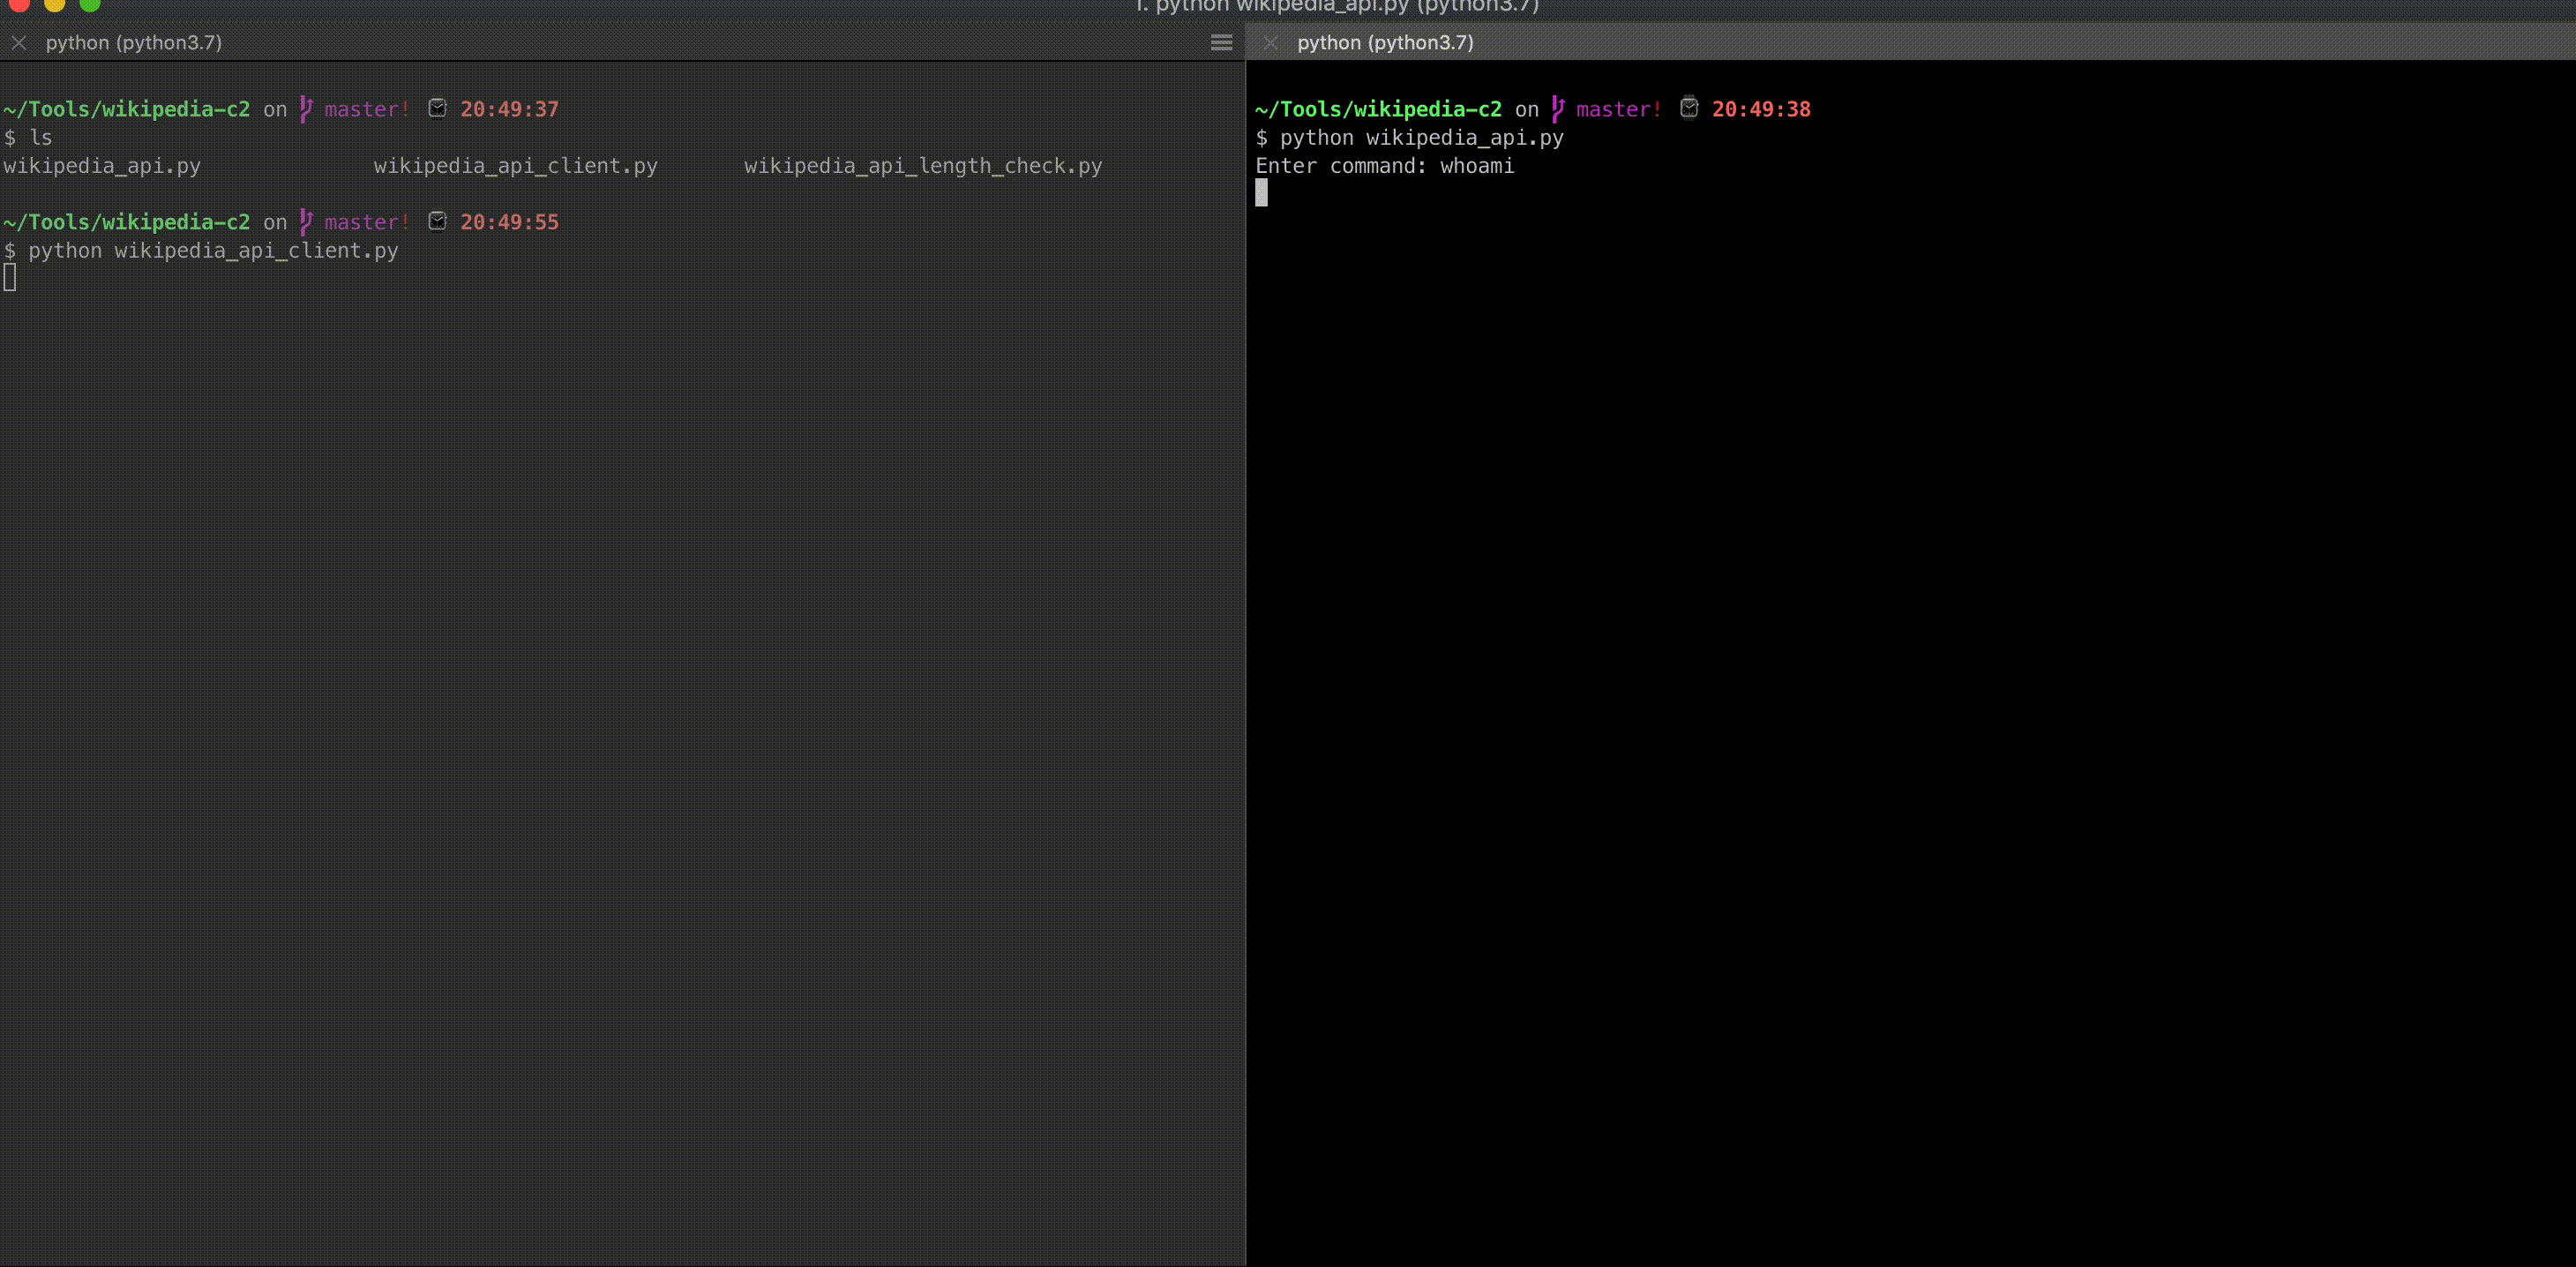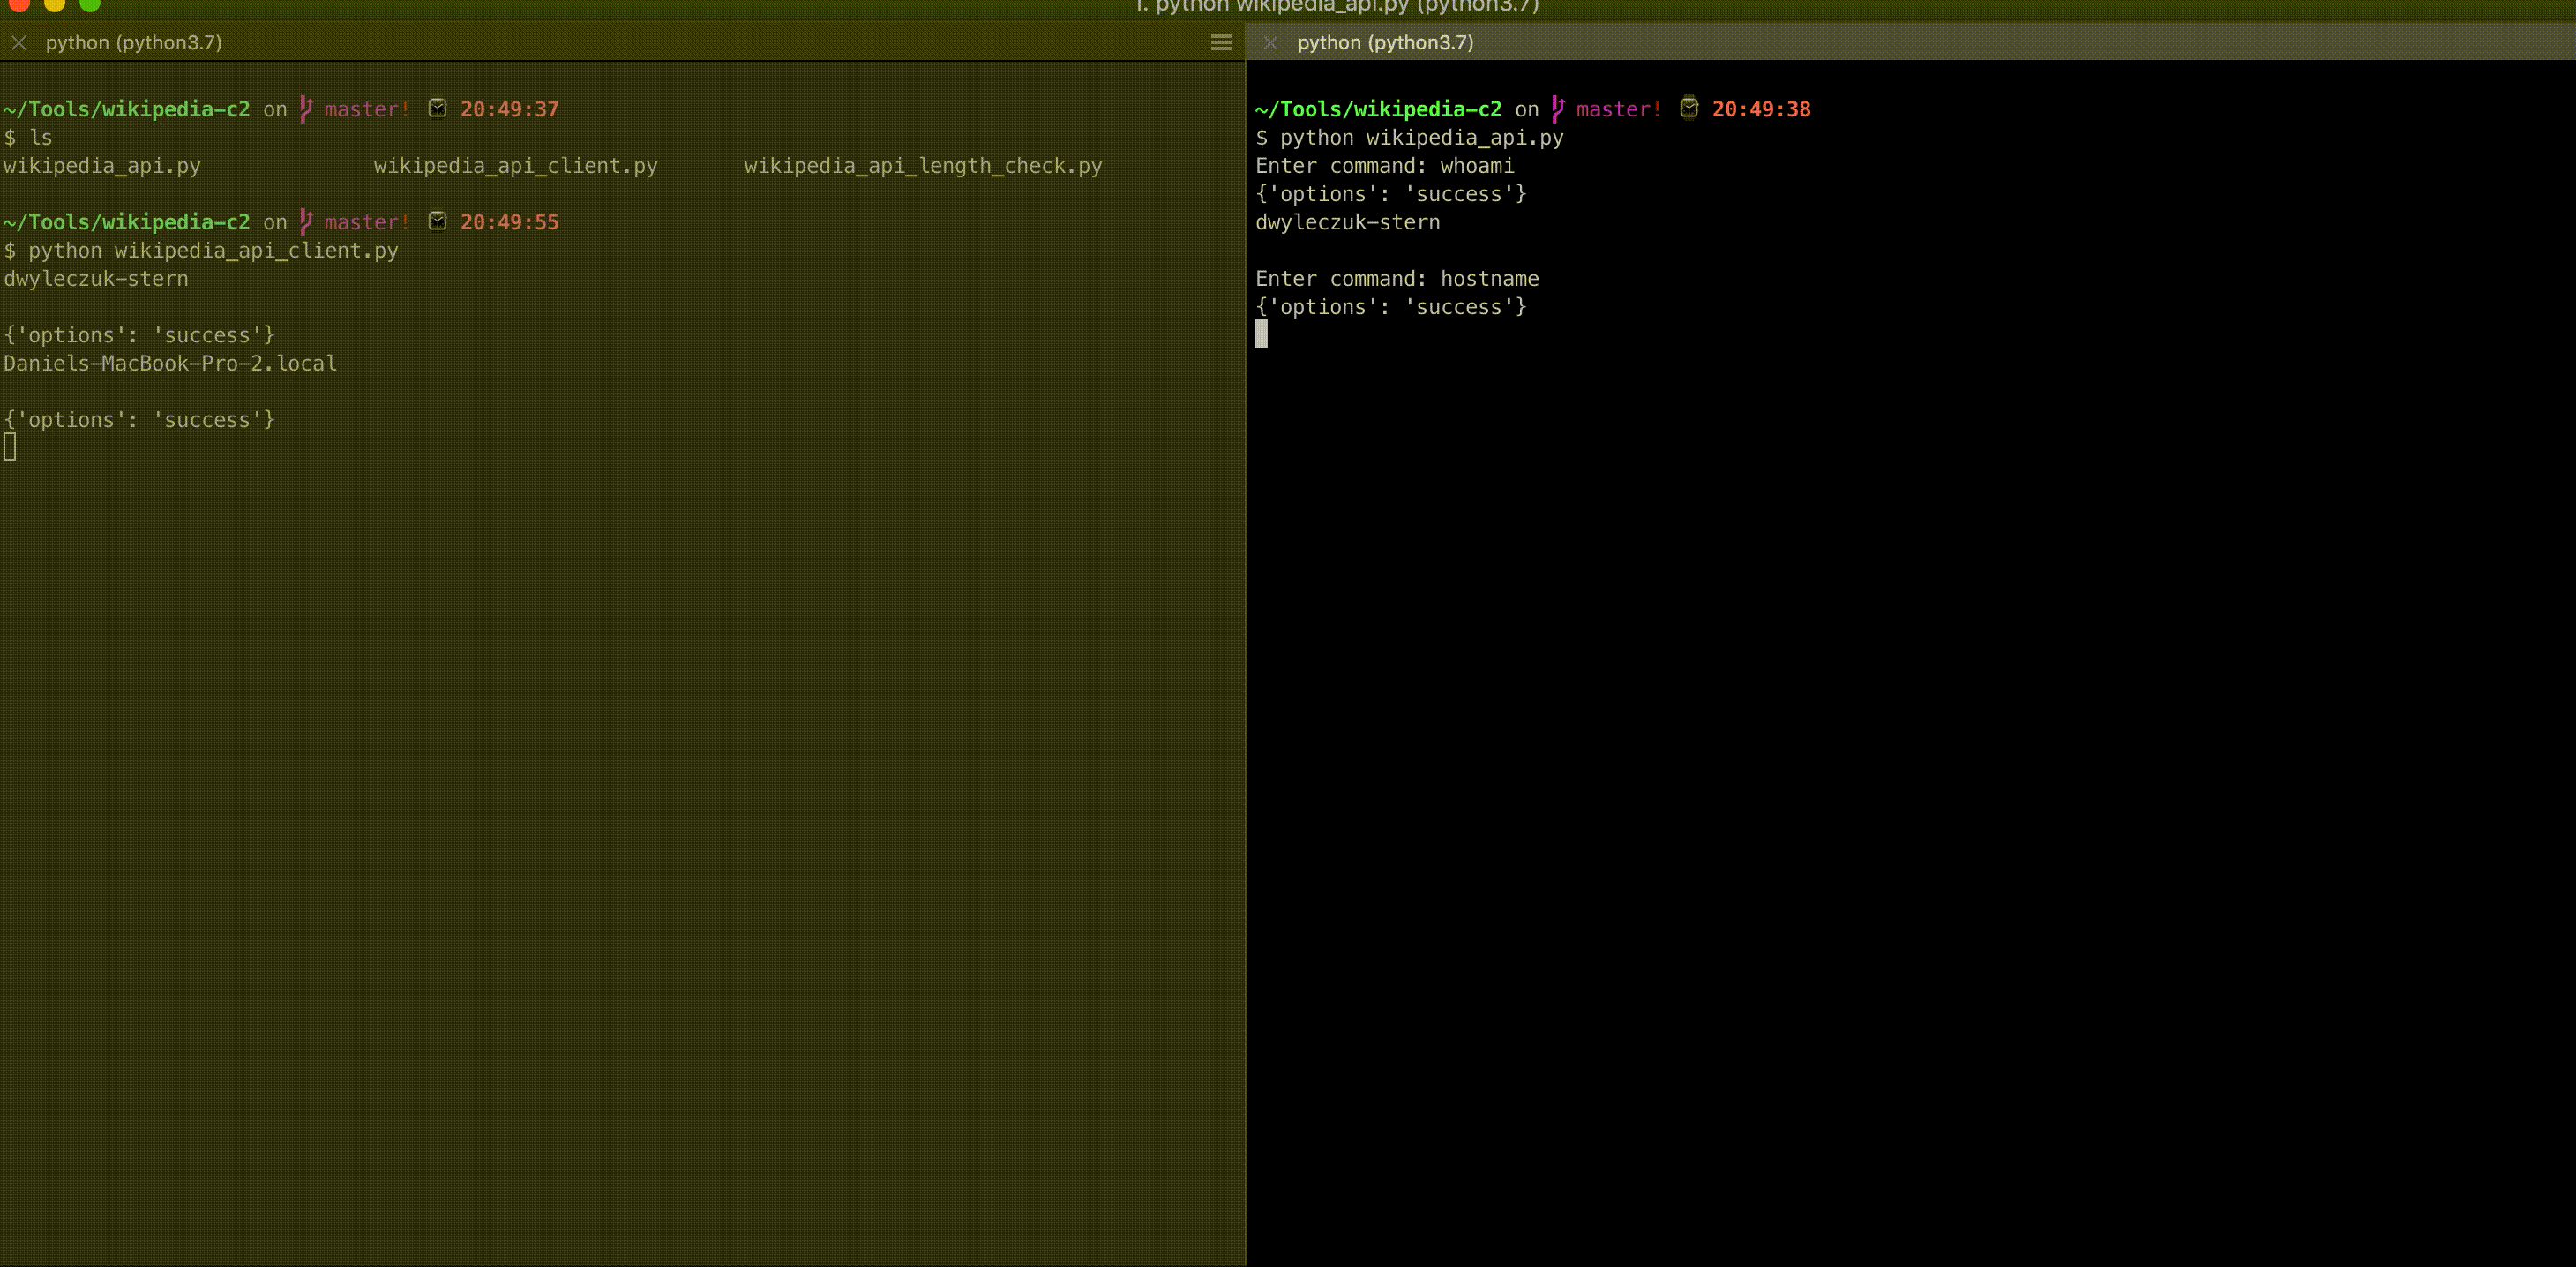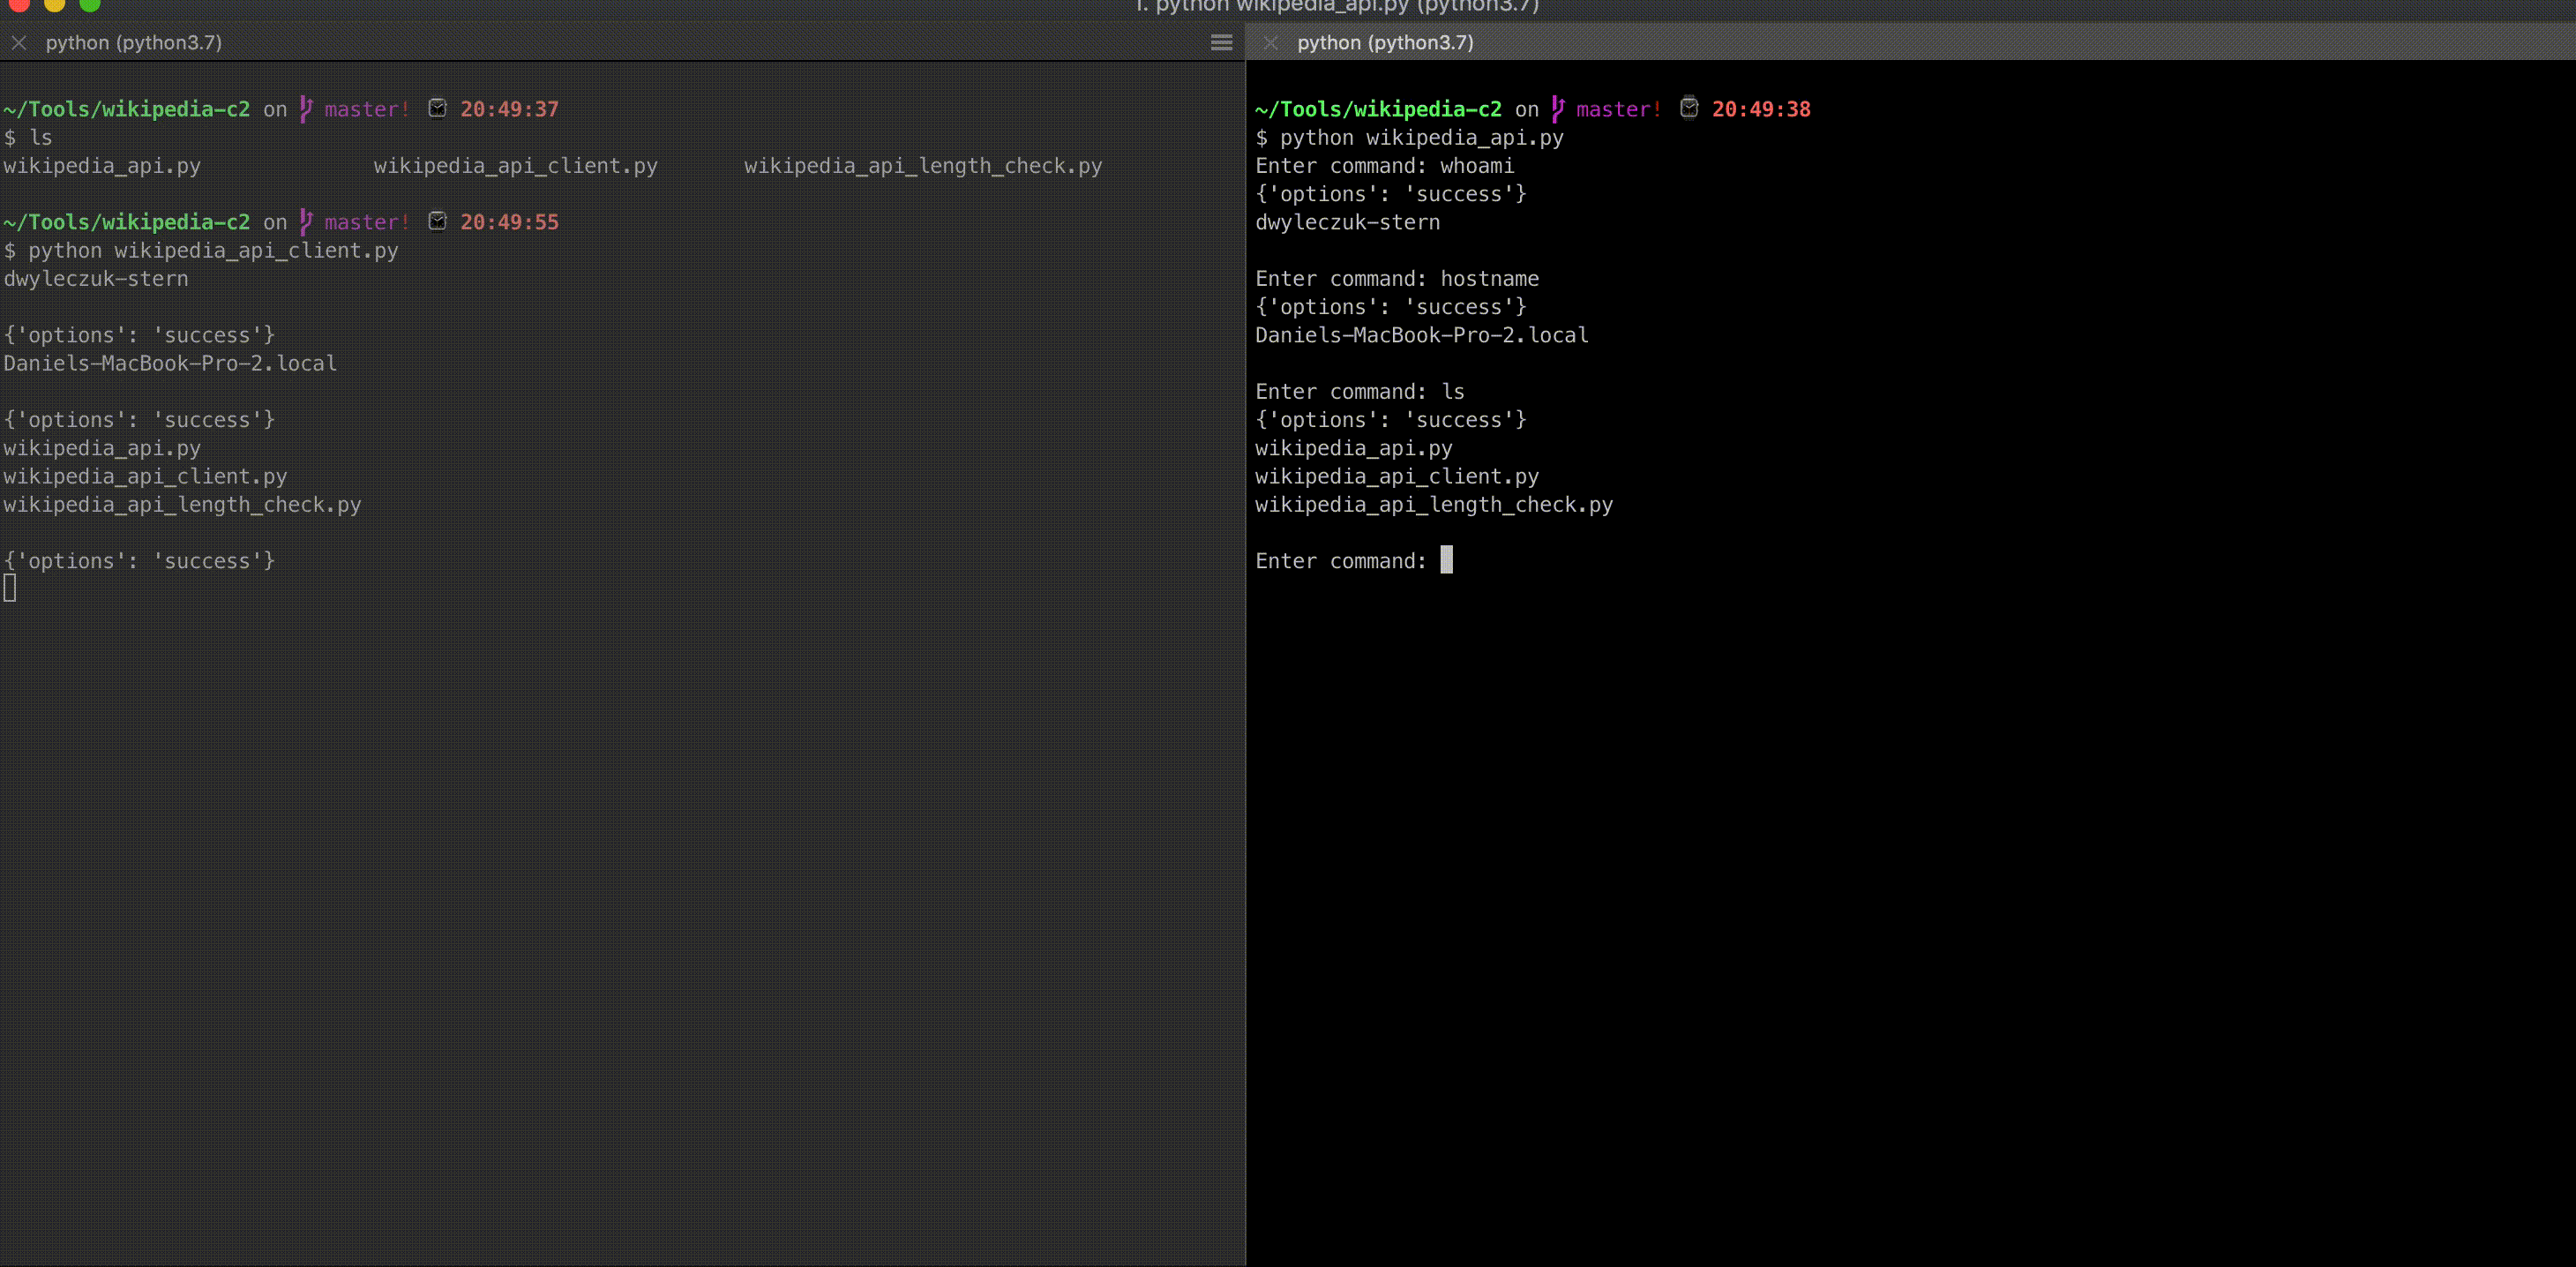 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control