

opa
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
api-securityauthenticationauthentication-authorization+10
12.4k
open-policy-agent/opaDeclarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
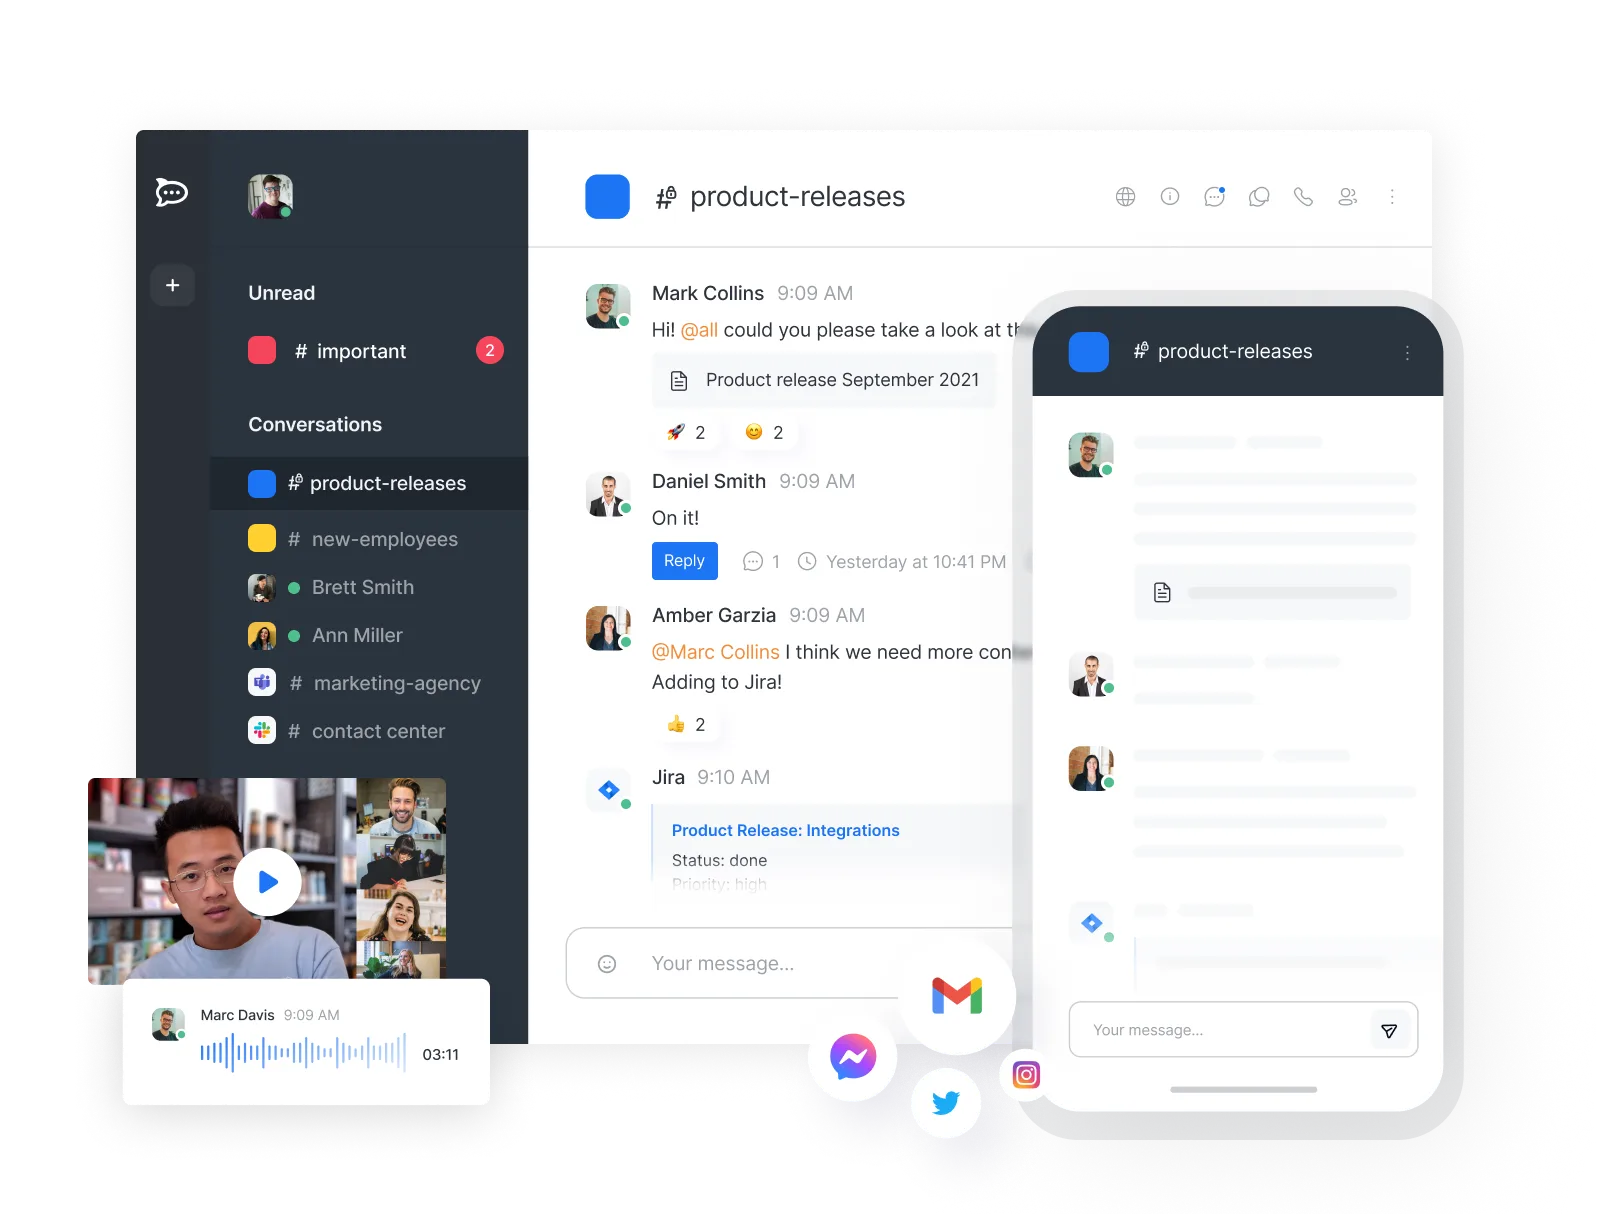 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations
 keycloak/keycloak
Open Source Identity and Access Management For Modern Applications and Services
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 cerbos/cerbos
Authorization engine for context-aware access control with YAML policies, RBAC/ABAC support, check/plan APIs, and GitOps-friendly deployment.
 apache/brpc
Industrial-grade C++ RPC framework for building high-performance distributed systems, supporting multiple protocols (HTTP, gRPC, Redis, Thrift) with…
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 pingidentity/ldapsdk
UnboundID LDAP SDK for Java
 apache/casbin
Authorization library enforcing ACL, RBAC, ABAC, and custom access-control models with RESTful matching and policy management APIs for applications…
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 abraxas/gitea-public-only-pat-org
Proof-of-concept lab for a Gitea authorization bypass where a public-only PAT with write:organization creates a private organization via POST…
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 umputun/reproxy
Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…