Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
52 results
zte-smartlife-app-pwned preview

zte-smartlife-app-pwned

GitHubminanagehsalalma/zte-smartlife-app-pwned

ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
android-securityapi-securitycryptography+7
4 days ago
hdwebmobile-photo-video-reviews preview

hdwebmobile-photo-video-reviews

GitHubhtrxuan/hdwebmobile-photo-video-reviews

WooCommerce plugin: photo & video product reviews, closing CVE-2026-12684's unauthenticated-upload vulnerability class by construction
api-securitycurated-resourceseducation+2
11 days ago
CVE-2026-5724 preview

CVE-2026-5724

GitHubtibrn/cve-2026-5724

Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
api-securityauthenticationexploitation+2
4 months ago
CVE-2026-33032 preview

CVE-2026-33032

GitHubkeraattin/cve-2026-33032

One missing function call on the route registration was enough to turn the MCP interface into an unauthenticated RCE gateway.
api-securityexploitationnetwork-security+4
55 months ago
CVE-2025-61777 preview

CVE-2025-61777

GitHub0x0w1z/cve-2025-61777

CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
api-securityexploitationpenetration-testing+2
211 months ago
lua-resty-waf preview

lua-resty-waf

GitHubp0pr0ck5/lua-resty-waf

High-performance WAF built on the OpenResty stack
anti-botapi-securitydefensive-tools+1
1.3k2 years ago
EITS-Portal-Exploit-CVE-2026-31367-PoC preview

EITS-Portal-Exploit-CVE-2026-31367-PoC

GitHubhereticl1nk/eits-portal-exploit-cve-2026-31367-poc

PoC exploit for unauthenticated RCE in EITS Admin Dashboard v2.4.0 via command injection in /api/v1/debug, allowing arbitrary OS command execution on…

api-securityexploitationpenetration-testing+2
1 month ago
OAUTHScan preview

OAUTHScan

GitHubakabe1/oauthscan

Burp Suite Extension useful to verify OAUTHv2 and OpenID security
api-securityapi-security-testingauthentication-authorization+6
1801 year ago
CVE-2026-11103-GraphQL-Batching-Alias-Rate-Limit-Bypass preview

CVE-2026-11103-GraphQL-Batching-Alias-Rate-Limit-Bypass

GitHubgeorge0papasotiriou/cve-2026-11103-graphql-batching-alias-rate-limit-bypass

Proof-of-concept exploit for CVE-2026-11103 demonstrating GraphQL rate-limit bypass through batching and field aliases; includes vulnerable Node.js…
api-securityapi-security-testingexploitation+3
1 month ago
WuppieFuzz preview

WuppieFuzz

GitHubtno-s3/wuppiefuzz

A coverage-guided REST API fuzzer developed on top of LibAFL
api-securityapi-security-testingfuzzing+3
22710 days ago
Azure-APIM-Dev-Portal-Signup-Bypass preview

Azure-APIM-Dev-Portal-Signup-Bypass

GitHubdz-y/azure-apim-dev-portal-signup-bypass

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
api-securityapi-security-testingauthentication-authorization+6
1 month ago
BFScan preview

BFScan

GitHubblackfan/bfscan

Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
android-securityapi-securityinformation-gathering+5
2579 months ago
CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field preview

CVE-2026-66421-OpenClaw-Dashboard-Stored-XSS-via-lastMessage-Session-Field

GitHubtheopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field

Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)
ai-securityapi-securityexploitation+3
1 month ago
jwt-reauth preview

jwt-reauth

GitHubnccgroup/jwt-reauth

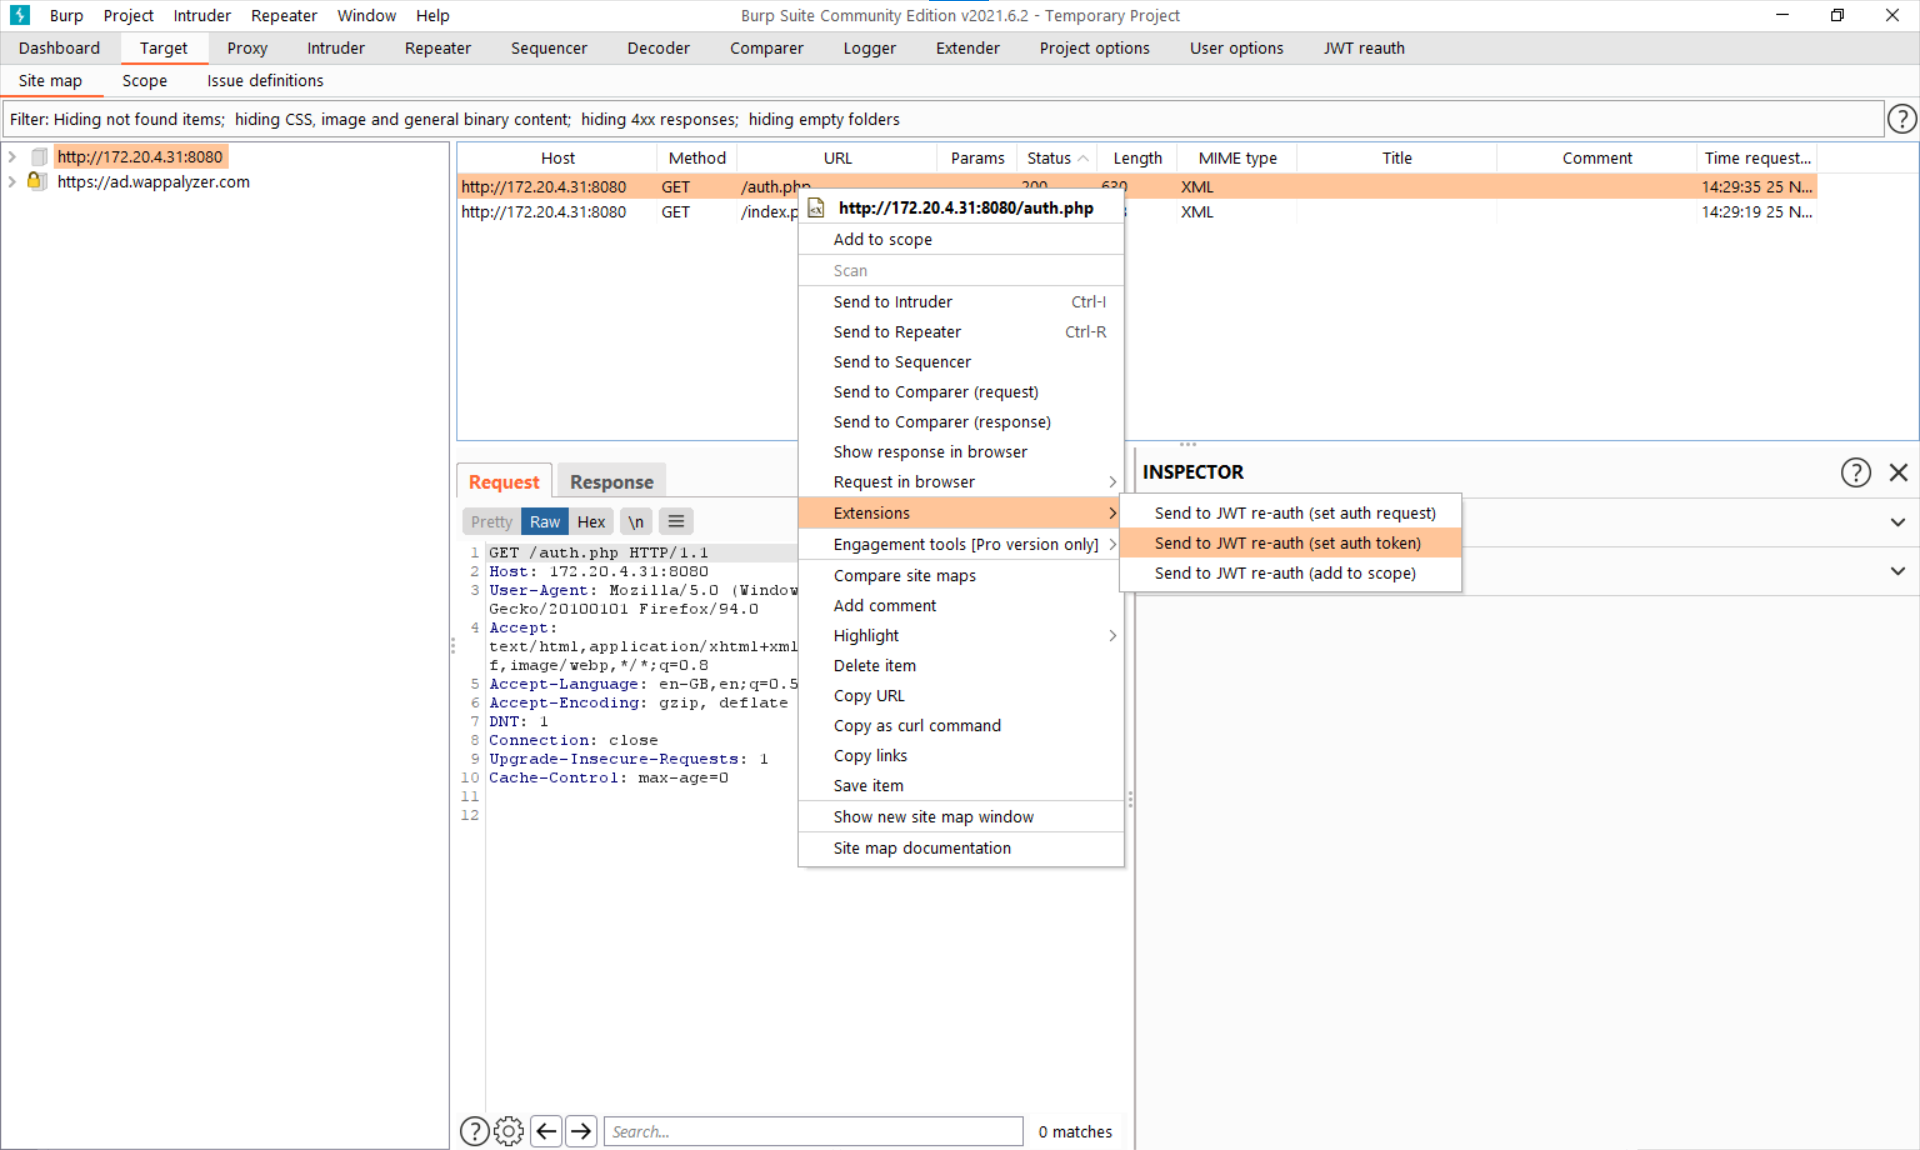
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
api-securityauthenticationpenetration-testing+3
1063 years ago
burp-jq preview

burp-jq

GitHubsynacktiv/burp-jq

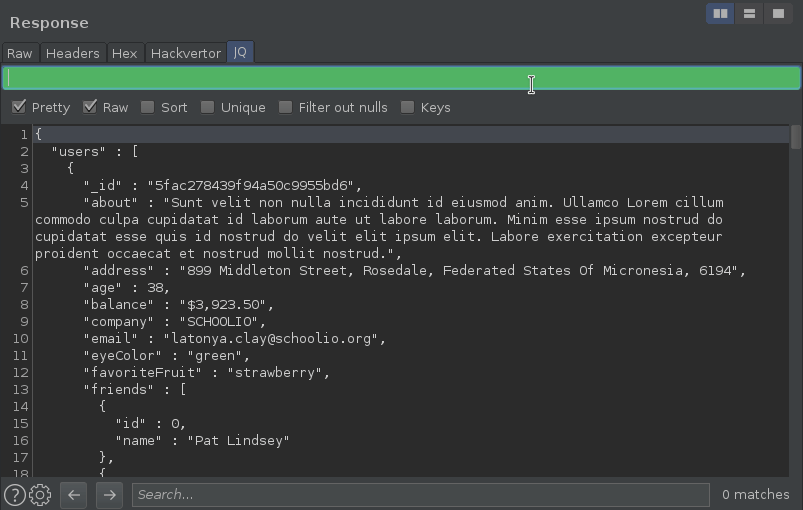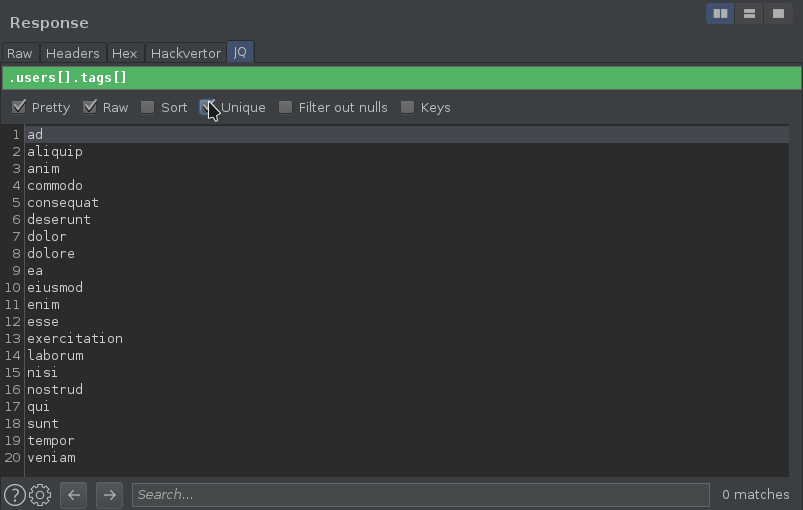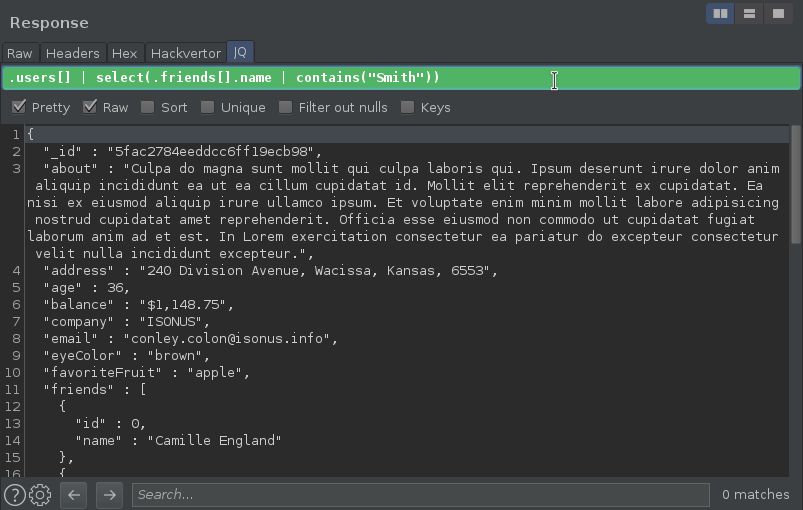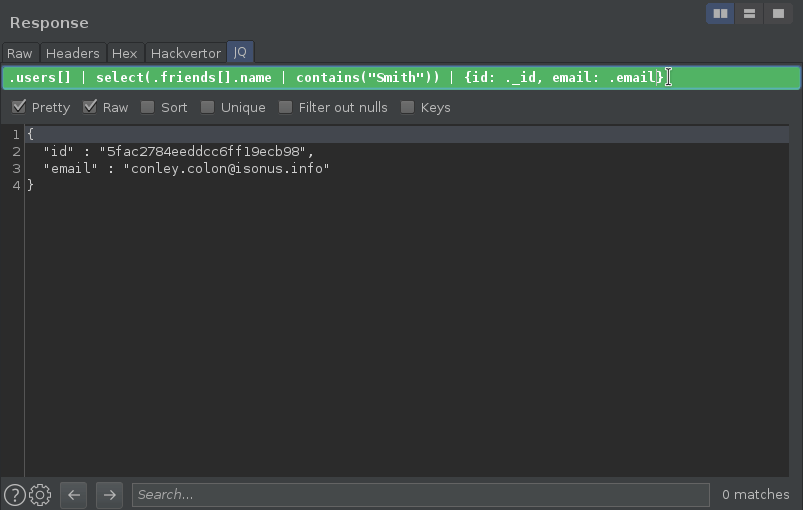
Burp extension to filter JSON on the fly with JQ queries in the HTTP message viewer.
api-securityutilities-frameworksweb-proxies-interception
505 years ago
ladder preview

ladder

GitHubeverywall/ladder

Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML
anti-botapi-securityweb-proxies-interception+1
9.1k1 month ago
web3-decoder preview

web3-decoder

GitHubnccgroup/web3-decoder

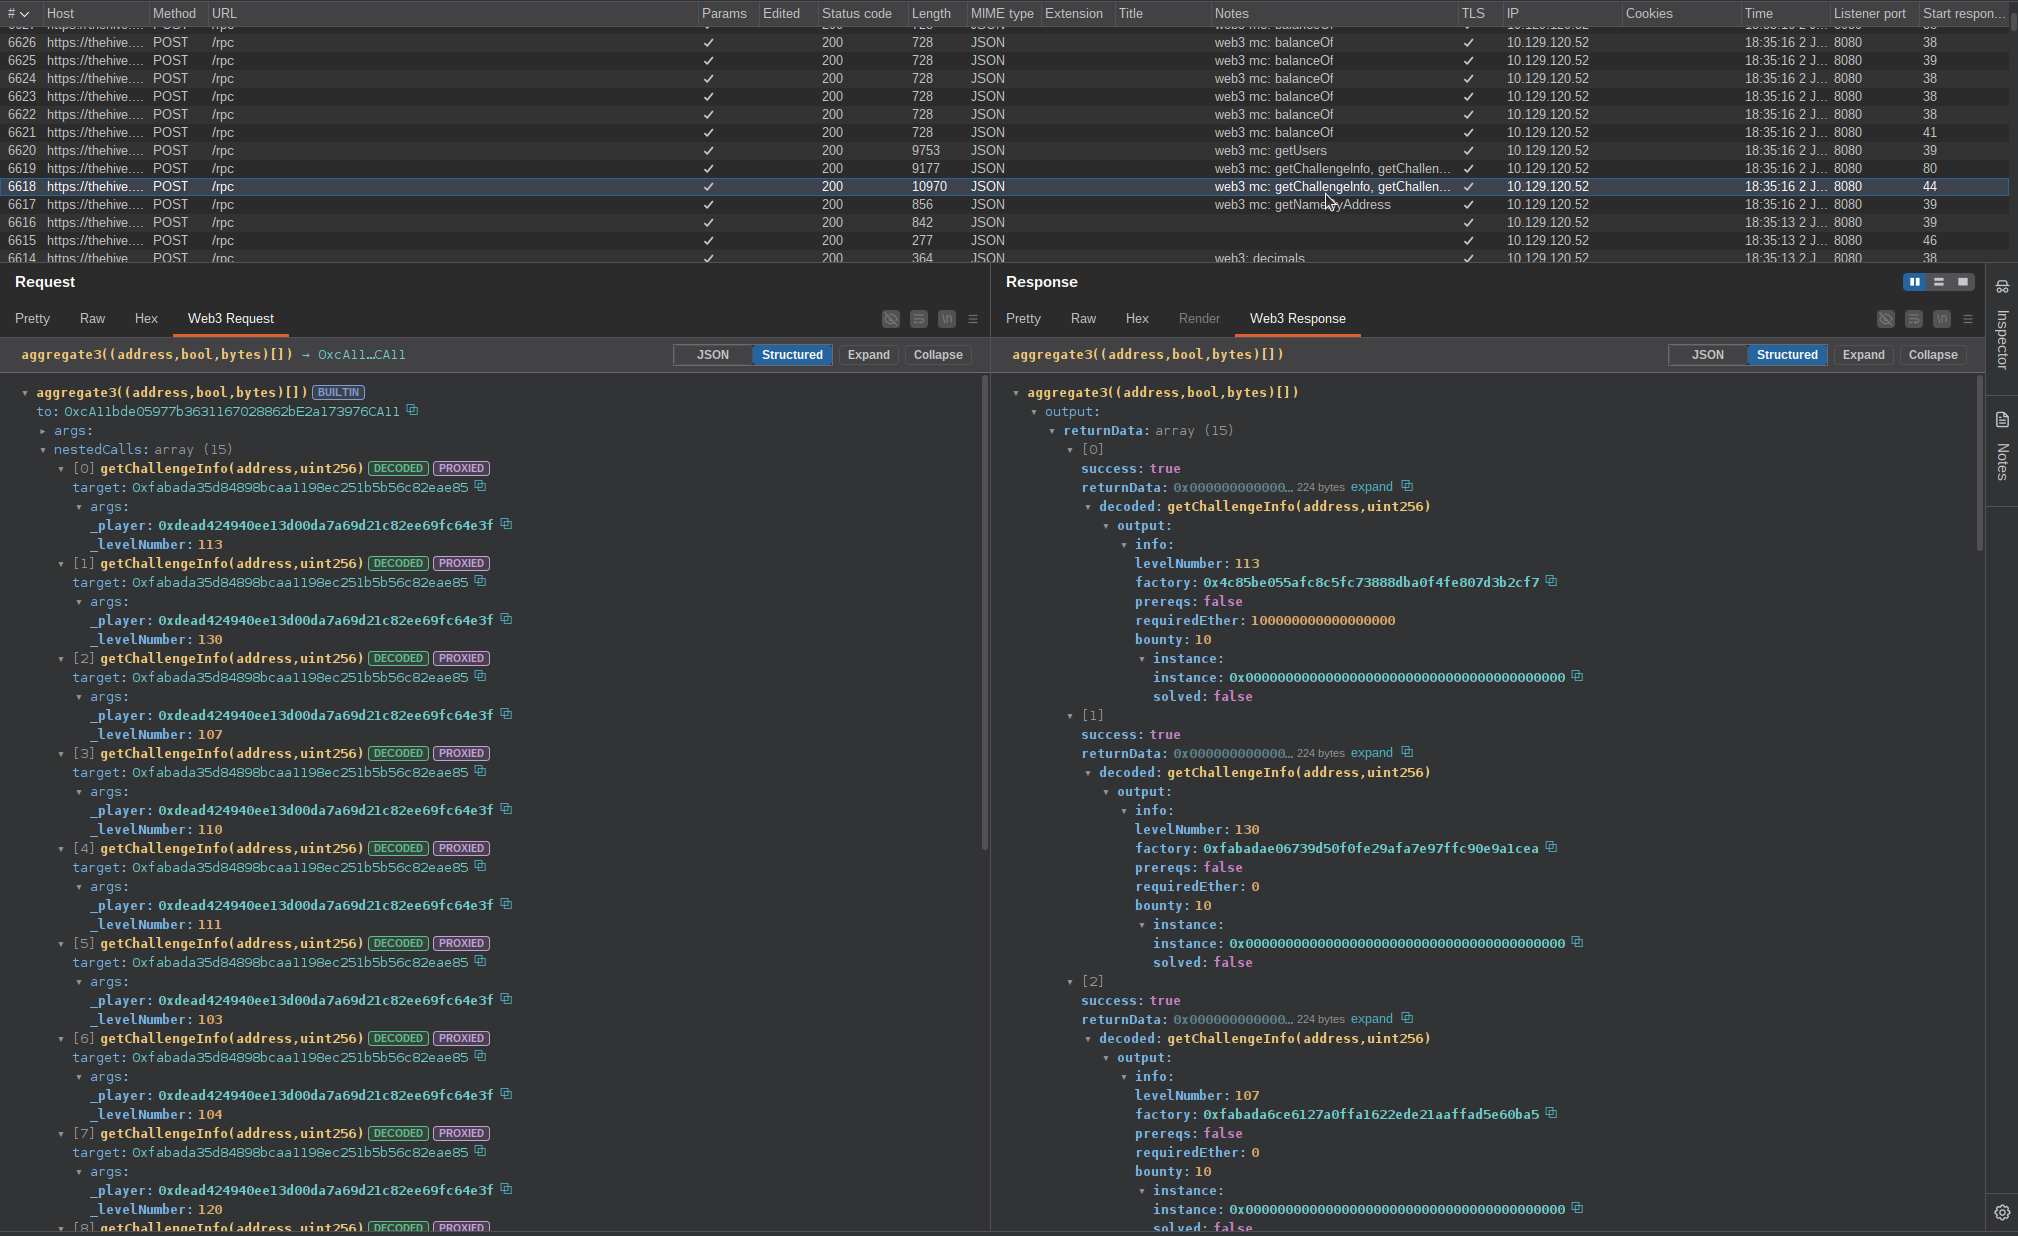
Burp Suite extension for decoding Web3 JSON-RPC traffic, including smart contract function calls, responses, and ABI resolution with proxy-aware and…
api-securityinformation-gatheringpenetration-testing+3
1173 months ago
CVE-2026-31283 preview

CVE-2026-31283

GitHubsaykino/cve-2026-31283

Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…

api-securityeducationemail-security+3
5 months ago
Previous123Next