
jellyfin-suggestions-idor
 abraxas/jellyfin-suggestions-idor
Jellyfin Server 12.2 - High - Remote - IDOR - GET /Items/Suggestions omit-userId dumps hidden library Path and IDs
api-securityinformation-gatheringlabs-practice+4
abraxas/jellyfin-suggestions-idorJellyfin Server 12.2 - High - Remote - IDOR - GET /Items/Suggestions omit-userId dumps hidden library Path and IDs
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 abraxas/pfsense-api-snort-file-join
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - File read - Snort rules {file} decode-then-join
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 abraxas/gitea-follow-existence
Demonstrates a Gitea account-enumeration oracle: authenticated PUT /api/v1/user/following/{username} returns 204 for hidden accounts and 404 for…
 abraxas/gitea-stargazers-hidden
Proof-of-concept and lab for an unauthenticated Gitea information disclosure: the stargazers and watchers API leaks usernames that profile endpoints…
 abraxas/gitea-user-keys-idor
Proof-of-concept and lab for a Gitea IDOR (CWE-639) in GET /api/v1/user/keys/{id}, letting an authenticated read:user token enumerate other users'…
 abraxas/nextcloud-calendar-sharee-publish
Nextcloud 35.0.0 — a calendar edit-sharee can publish the owner's calendar to an unauthenticated URL
 vulncheck-oss/cli
VulnCheck's official command line tool
 asvorg/cve-2026-105030-poc
A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 bombobombone/cve-2026-103440
Report summary and local proof-of-concept script demonstrating CVE-2026-103440, a PageTriage API disclosure of suppressed reviewer usernames on…
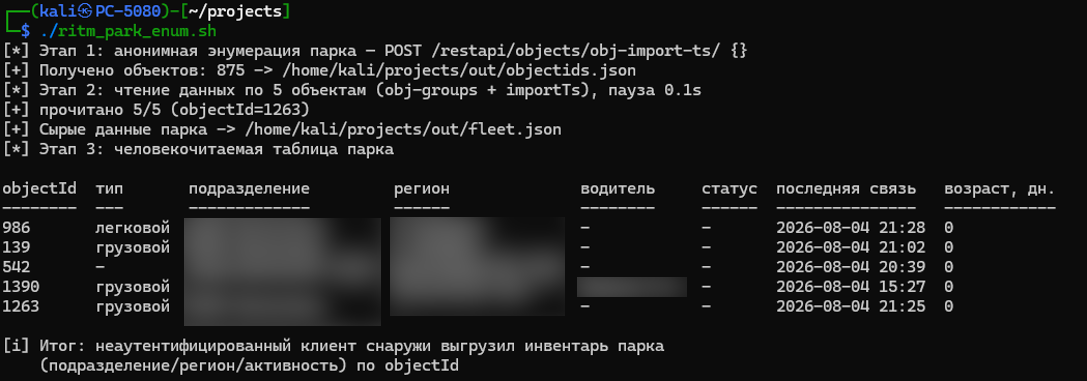 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 mr-redoo7/cve-2026-27739-poc
Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…
 yggcwhat/cve-2021-45232
Batch vulnerability scanner that integrates FOFA to discover and test Apache APISIX Dashboard instances for CVE-2021-45232 unauthorized access.
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 wattocyber/lm-fingerprint
Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.