

threatripper
 mevislobo2006/threatripper
Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…
api-securitydefensive-toolseducation+4
1
mevislobo2006/threatripperOffline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…

 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 abraxas/gitea-stargazers-hidden
Proof-of-concept and lab for an unauthenticated Gitea information disclosure: the stargazers and watchers API leaks usernames that profile endpoints…
 abraxas/hyperswitch-payout-confirm-secret
Proof-of-concept and lab for a Hyperswitch payout confirm flaw: a dummy client_secret plus amount in POST /payouts/{id}/confirm raises the stored…
 abraxas/lago-stripe-invoice-idor
Reproduces a CWE-639 IDOR in Lago v1.53.0 where the Stripe one-time webhook loads invoices without organization scoping, enabling cross-org payment…
 abraxas/nextcloud-calendar-sharee-publish
Nextcloud 35.0.0 — a calendar edit-sharee can publish the owner's calendar to an unauthenticated URL
 vulncheck-oss/cli
VulnCheck's official command line tool
 usebruno/bruno
Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)
 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 bombobombone/cve-2026-103440
Report summary and local proof-of-concept script demonstrating CVE-2026-103440, a PageTriage API disclosure of suppressed reviewer usernames on…
 bombobombone/cve-2026-102973
Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…
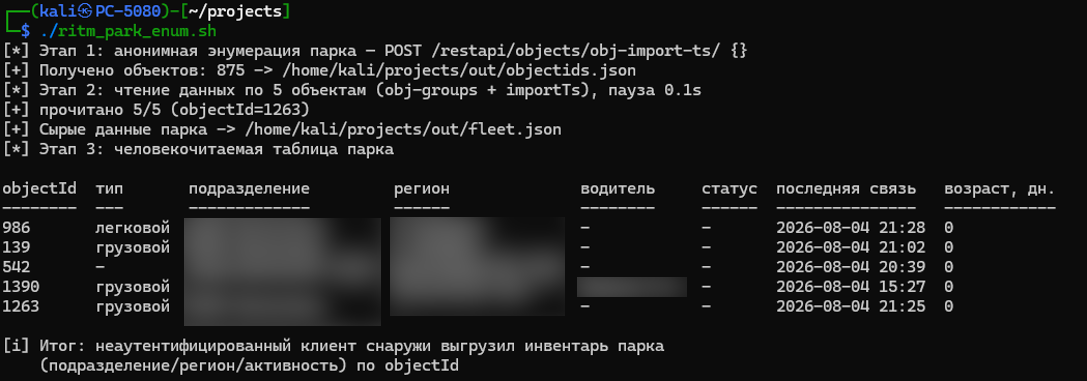 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…