
CVE-2026-94609
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
api-securityauthentication-authorizationeducation+6
anthonyk2923/cve-2026-94609Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 shadowforge-cyber/cve-2026-12944
Python PoC exploiting CVE-2026-12944, an SSRF in Langflow 1.10.0 via urllib in custom components, with authenticated read and fetch capabilities.
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…
 mr-redoo7/cve-2026-27739-poc
Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…
 isaca0315/cve-2026-44351-poc
Proof-of-concept for CVE-2026-44351, an authentication bypass in fast-jwt <6.2.4 where an empty HMAC key lets attackers forge arbitrary JWTs accepted…
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
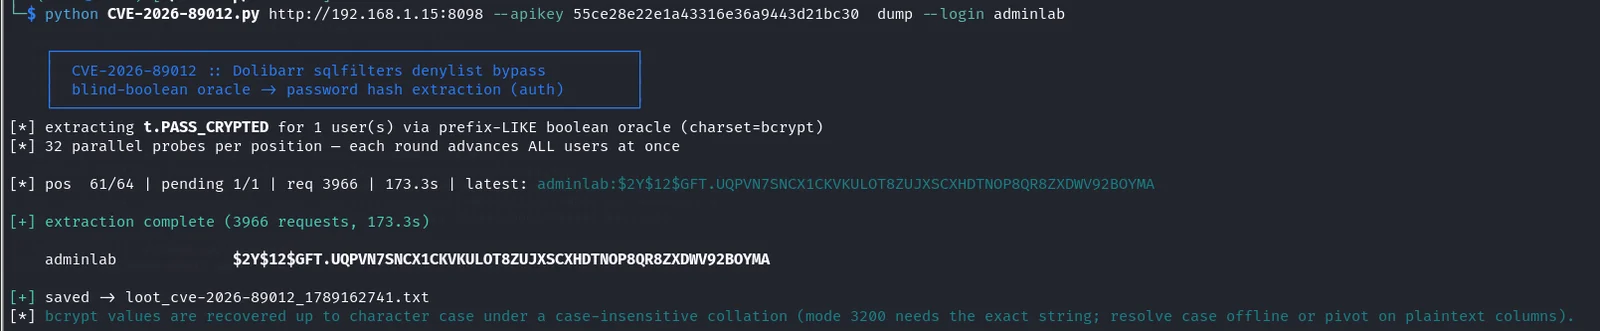 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 squeeze440/inference-gateway-poc
PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
 squeeze440/pasteguard-poc
PoC — cross-origin proxy abuse of configured provider API keys in PasteGuard (GHSA-q94x-p9rc-q89f, CVE-2026-86998, CVSS 7.6).
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 terra-nova83/cve-2026-0915-json-patch.-v2.0
Provides a security patch for CVE-2026-0915, adding strict JSON schema validation, input sanitization, and rate limiting to prevent injection and DoS…