
CVE-2026-16764
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
api-securityauthentication-authorizationeducation+6
1
hakaioffsec/cve-2026-16764Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
 itsc1sco/mcpjam-to-root
From MCPJam Inspector RCE to root — CVE-2026-23744, JupyterLab token disclosure, kernel execution, and OPSMCP privilege escalation
 trandonga3/poc-cve-2026-63030-cve-2026-60137-
Exploit chain for WordPress Core using REST API route-confusion and SQL injection for unauthenticated RCE, privilege escalation, and full server…
 george0papasotiriou/cve-2026-21020-protobuf-message-parsing-polymorphic-deserialization-vulnerability
PoC for CVE-2026-21020, demonstrating Protobuf Any-type polymorphic deserialization where attacker-controlled type_url can lead to logic bugs, RCE,…
 george0papasotiriou/cve-2026-3030-prototype-pollution-in-json-merge-patch
Demonstrates CVE-2026-3030 prototype pollution in a Node.js JSON merge patch REST API, including a vulnerable server and exploit script for privilege…
 george0papasotiriou/cve-2026-4444-jwt-algorithm-confusion-via-kid-injection
POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…
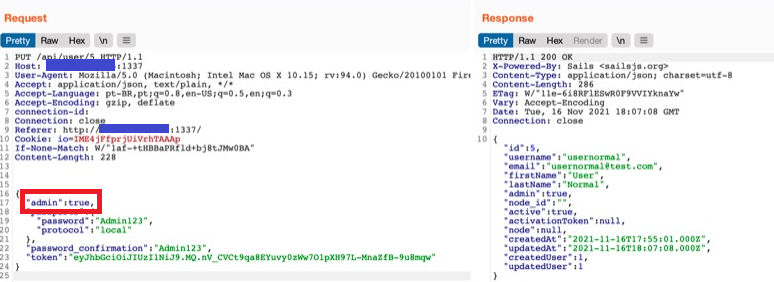 paulotrindadec/cve-2021-44103
Proof-of-concept exploit for CVE-2021-44103 demonstrating vertical privilege escalation in Konga API Gateway 0.14.9, allowing authenticated users to…
 comparedarray/printix-cve-2022-29554
A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…