
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
51 results
threatripper preview

threatripper

GitLabmevislobo2006/threatripper

Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…

api-securitydefensive-toolseducation+4
1
1 month ago
jellyfin-playlist-itemids preview

jellyfin-playlist-itemids

GitHubabraxas/jellyfin-playlist-itemids

Jellyfin Server 12.2 - High - Remote - IDOR - public playlist ItemIds leftover of GHSA-9x85 then unauth stream
api-securitydata-exfiltrationinformation-gathering+5
17 days ago
pfsense-api-acb-userkey preview

pfsense-api-acb-userkey

GitHubabraxas/pfsense-api-acb-userkey

pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - ACB userkey capability URL
api-securitydata-exfiltrationexploitation+7
20 days ago
pfsense-api-acme-key-dump preview

pfsense-api-acme-key-dump

GitHubabraxas/pfsense-api-acme-key-dump

pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET /services/acme dumps keys

api-securitydata-exfiltrationexploitation+6
20 days ago
jshound preview

jshound

GitHubambitsecurity/jshound

Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.

api-securitycrawlerinformation-gathering+5
1315 days ago
APIHarvester preview

APIHarvester

GitHubpiratesshield/apiharvester

The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
api-securityapi-security-testingcrawler+9
353 months ago
CVE-2026-15583 preview

CVE-2026-15583

GitHubabraxas/cve-2026-15583

Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
api-securitydata-exfiltrationexploitation+6
6 days ago
POC-CVE-2026-93680 preview

POC-CVE-2026-93680

GitHubrmhowe425/poc-cve-2026-93680

Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
api-securityauthenticationdata-exfiltration+4
1 month ago
CVE-2026-86259 preview

CVE-2026-86259

GitHubuziii2208/cve-2026-86259

OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
api-securitycloud-securitydata-exfiltration+6
1 month ago
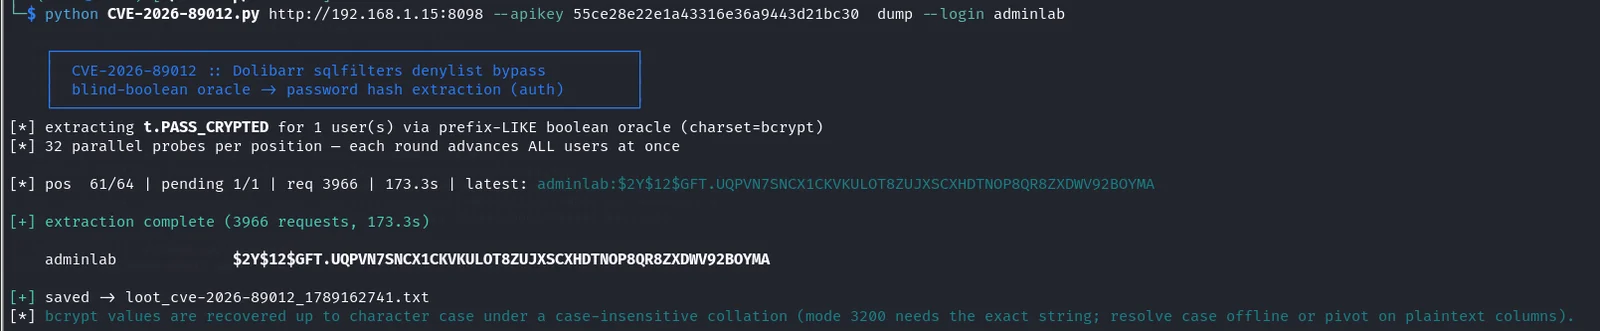
CVE-2026-89012 preview

CVE-2026-89012

GitHubfaceless0x7/cve-2026-89012

Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
api-securitydata-exfiltrationexploitation+6
61 month ago
enforcement-coverage preview

enforcement-coverage

GitHubarian-gogani/enforcement-coverage

Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
api-securitycode-analysisdevsecops+3
11 month ago
mcpjam-to-root preview

mcpjam-to-root

GitHubitsc1sco/mcpjam-to-root

From MCPJam Inspector RCE to root — CVE-2026-23744, JupyterLab token disclosure, kernel execution, and OPSMCP privilege escalation
api-securityeducationexploitation+5
2 months ago
CVE-2026-52616 preview

CVE-2026-52616

GitHubs1ko/cve-2026-52616

Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
api-securityexploitationnetwork-security+1
2 months ago
lm-fingerprint preview

lm-fingerprint

GitLabwattocyber/lm-fingerprint

Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.

ai-securityapi-securityinformation-gathering+3
2 months ago
CVE-2026-64849 preview

CVE-2026-64849

GitHubbiutrap/cve-2026-64849

Proof-of-concept exploit for CVE-2026-64849: triggers SSRF in MLflow webhook API via crafted POST, fetching cloud instance metadata from…
api-securitycloud-securityexploitation+4
2 months ago
CVE-2026-27344 preview

CVE-2026-27344

GitHubac8999/cve-2026-27344

Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…
api-securityauthentication-authorizationmisconfiguration+3
2 months ago
CVE-2026-64640 preview

CVE-2026-64640

GitHuboscerd/cve-2026-64640

Reproducer for CVE-2026-64640 — Apache Polaris Iceberg REST register/register-view vends storage credentials and reads an attacker-chosen metadata…
api-securitycloud-securitydata-exfiltration+5
2 months ago
Azure-APIM-Dev-Portal-Signup-Bypass preview

Azure-APIM-Dev-Portal-Signup-Bypass

GitHubdz-y/azure-apim-dev-portal-signup-bypass

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

api-securityapi-security-testingauthentication-authorization+6
3 months ago
Previous123Next