
CVE-2025-56223
 saykino/cve-2025-56223
Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…
api-securitypenetration-testingvulnerability-analysis+1
saykino/cve-2025-56223Documentation of CVE-2025-56223, a denial-of-service vulnerability in Ascertia SigningHub's Upload Document API, allowing unrestricted file uploads…
 nel-droid/cve-2026-71204-poc
PoC: changedetection.io settings blind-merge mass assignment (CVE-2026-71204, Medium 6.3)
 coffinxp/gemini-api-key-hunter
Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…
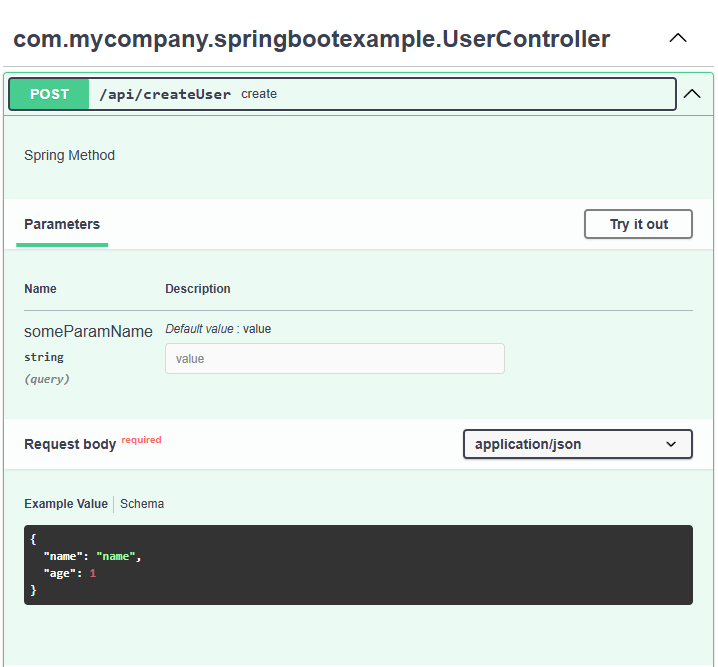 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 afine-com/cve-2018-25031
.json and .yaml files used to exploit CVE-2018-25031
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
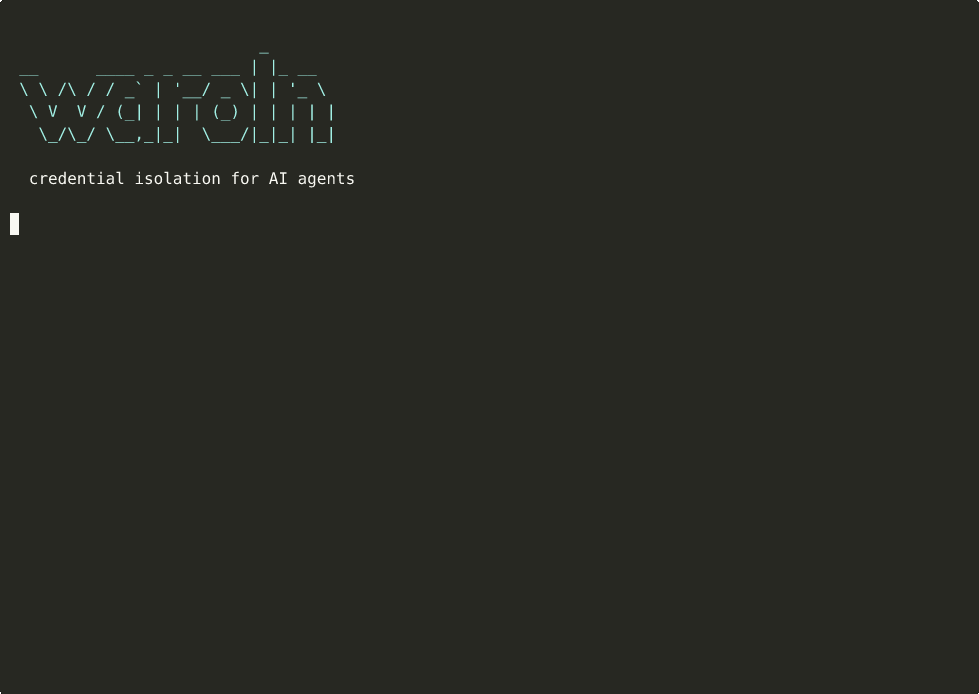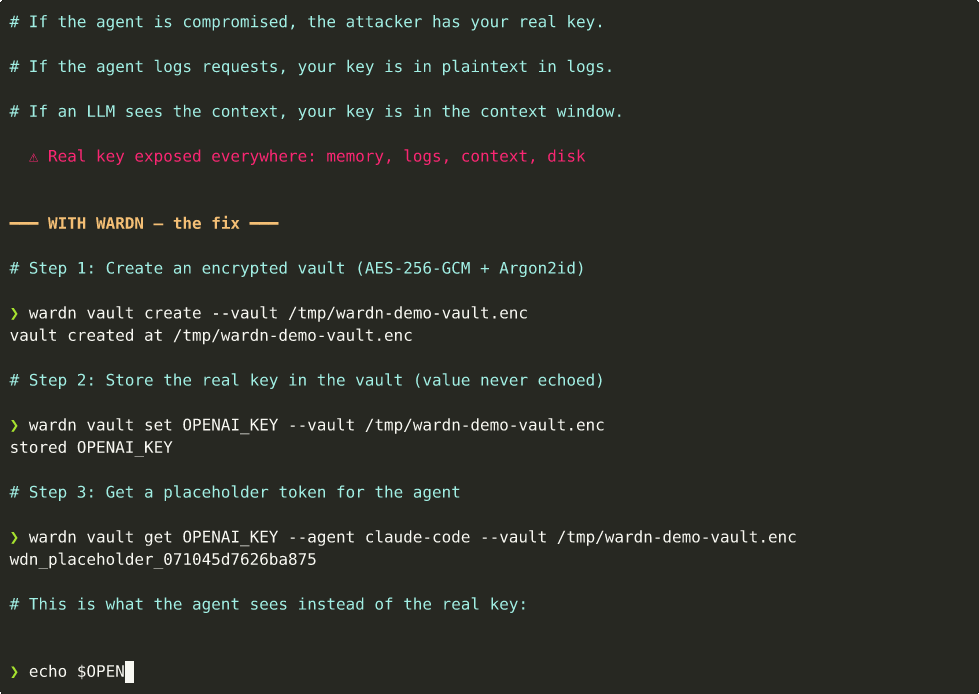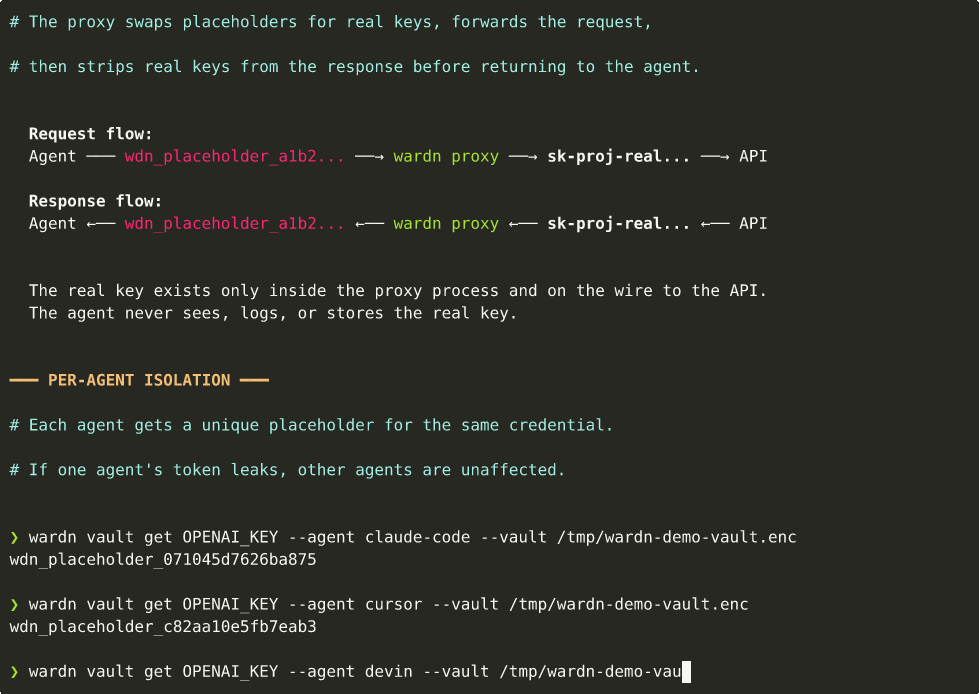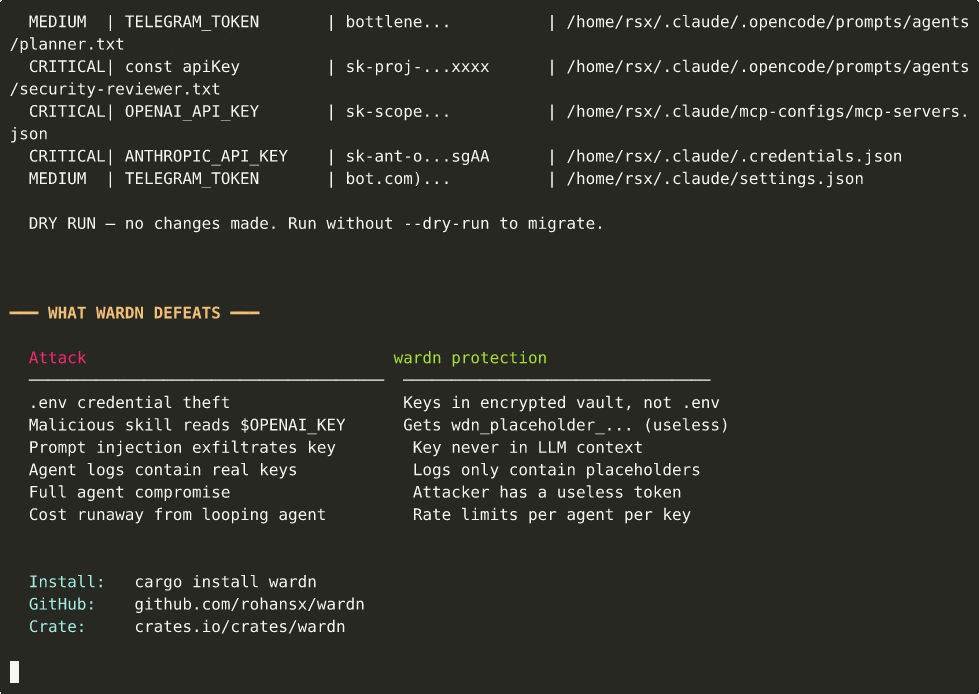 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
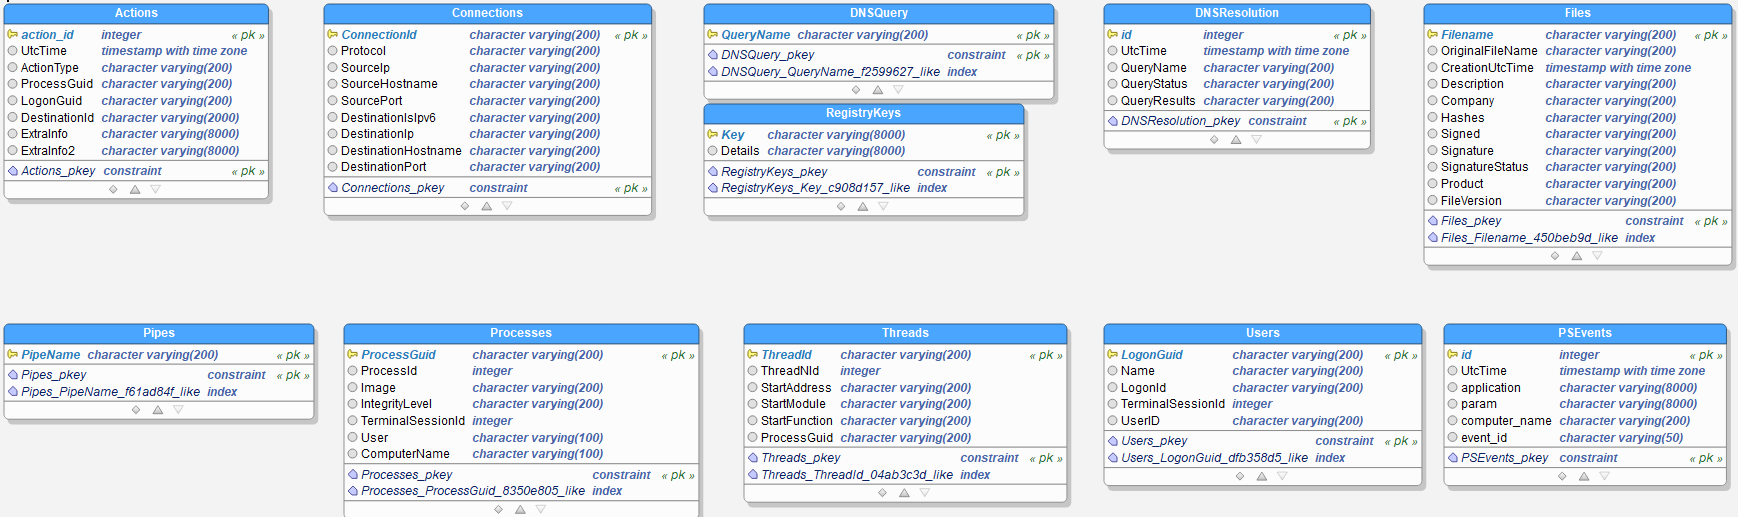 lucky-luk3/grafiki
Threat Hunting tool about Sysmon and graphs
 gdatasoftwareag/vaas
Verdict-as-a-Service SDKs: Analyze files for malicious content
 kaysec/hybrid-submit
A script that automatically submits files to Hybrid Analysis (API)