

APIHarvester
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
api-securityapi-security-testingcrawler+9
32
piratesshield/apiharvesterThe one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 asvorg/cve-2026-105030-poc
A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 bombobombone/cve-2026-103440
Report summary and local proof-of-concept script demonstrating CVE-2026-103440, a PageTriage API disclosure of suppressed reviewer usernames on…
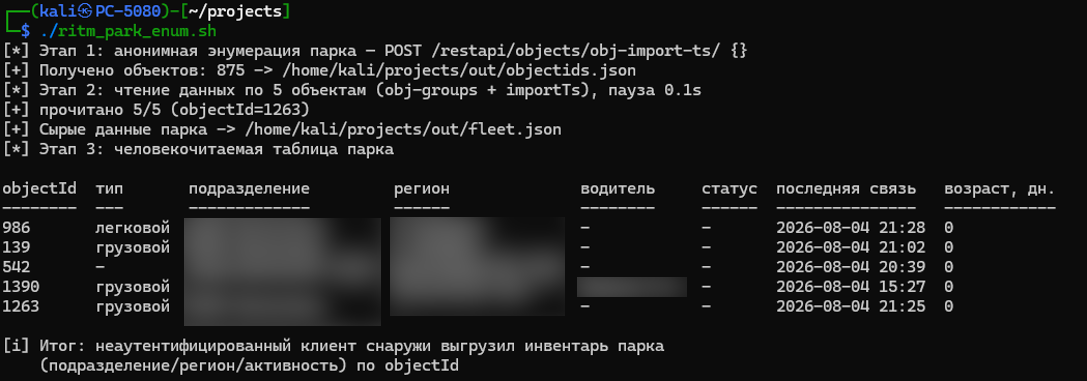 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 ejfkdev/oss
Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…
 mr-redoo7/cve-2026-27739-poc
Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 keraattin/cve-2026-33032
One missing function call on the route registration was enough to turn the MCP interface into an unauthenticated RCE gateway.
 yggcwhat/cve-2021-45232
Batch vulnerability scanner that integrates FOFA to discover and test Apache APISIX Dashboard instances for CVE-2021-45232 unauthorized access.
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 wildandeveloper/cve-2026-58231
Non-destructive detection and precondition-verification tool for CVE-2026-58231, probing SAP Commerce Cloud Data Hub endpoints, default OAuth…
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 wattocyber/lm-fingerprint
Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.