CVE-2026-8206-Kirki-Exploit-Analysis

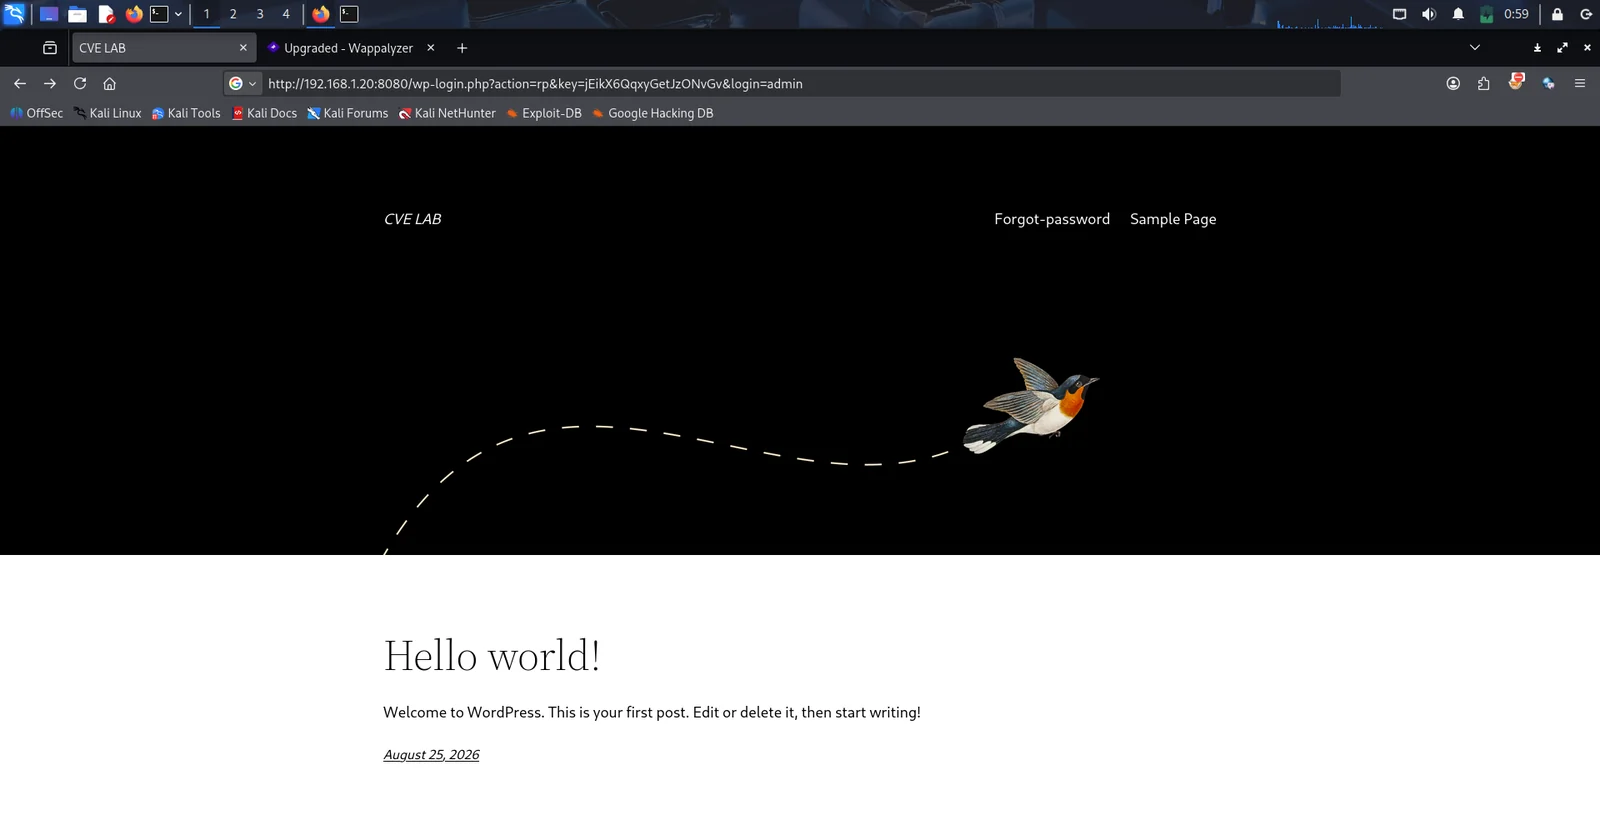
Technical reconstruction and proof-of-concept for CVE-2026-8206, an unauthenticated account takeover in the WordPress Kirki plugin, with detection…

Technical reconstruction and proof-of-concept for CVE-2026-8206, an unauthenticated account takeover in the WordPress Kirki plugin, with detection…

Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…

Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…

From MCPJam Inspector RCE to root — CVE-2026-23744, JupyterLab token disclosure, kernel execution, and OPSMCP privilege escalation

Exploit chain for WordPress Core using REST API route-confusion and SQL injection for unauthenticated RCE, privilege escalation, and full server…

Demonstrates CVE-2026-3030 prototype pollution in a Node.js JSON merge patch REST API, including a vulnerable server and exploit script for privilege…

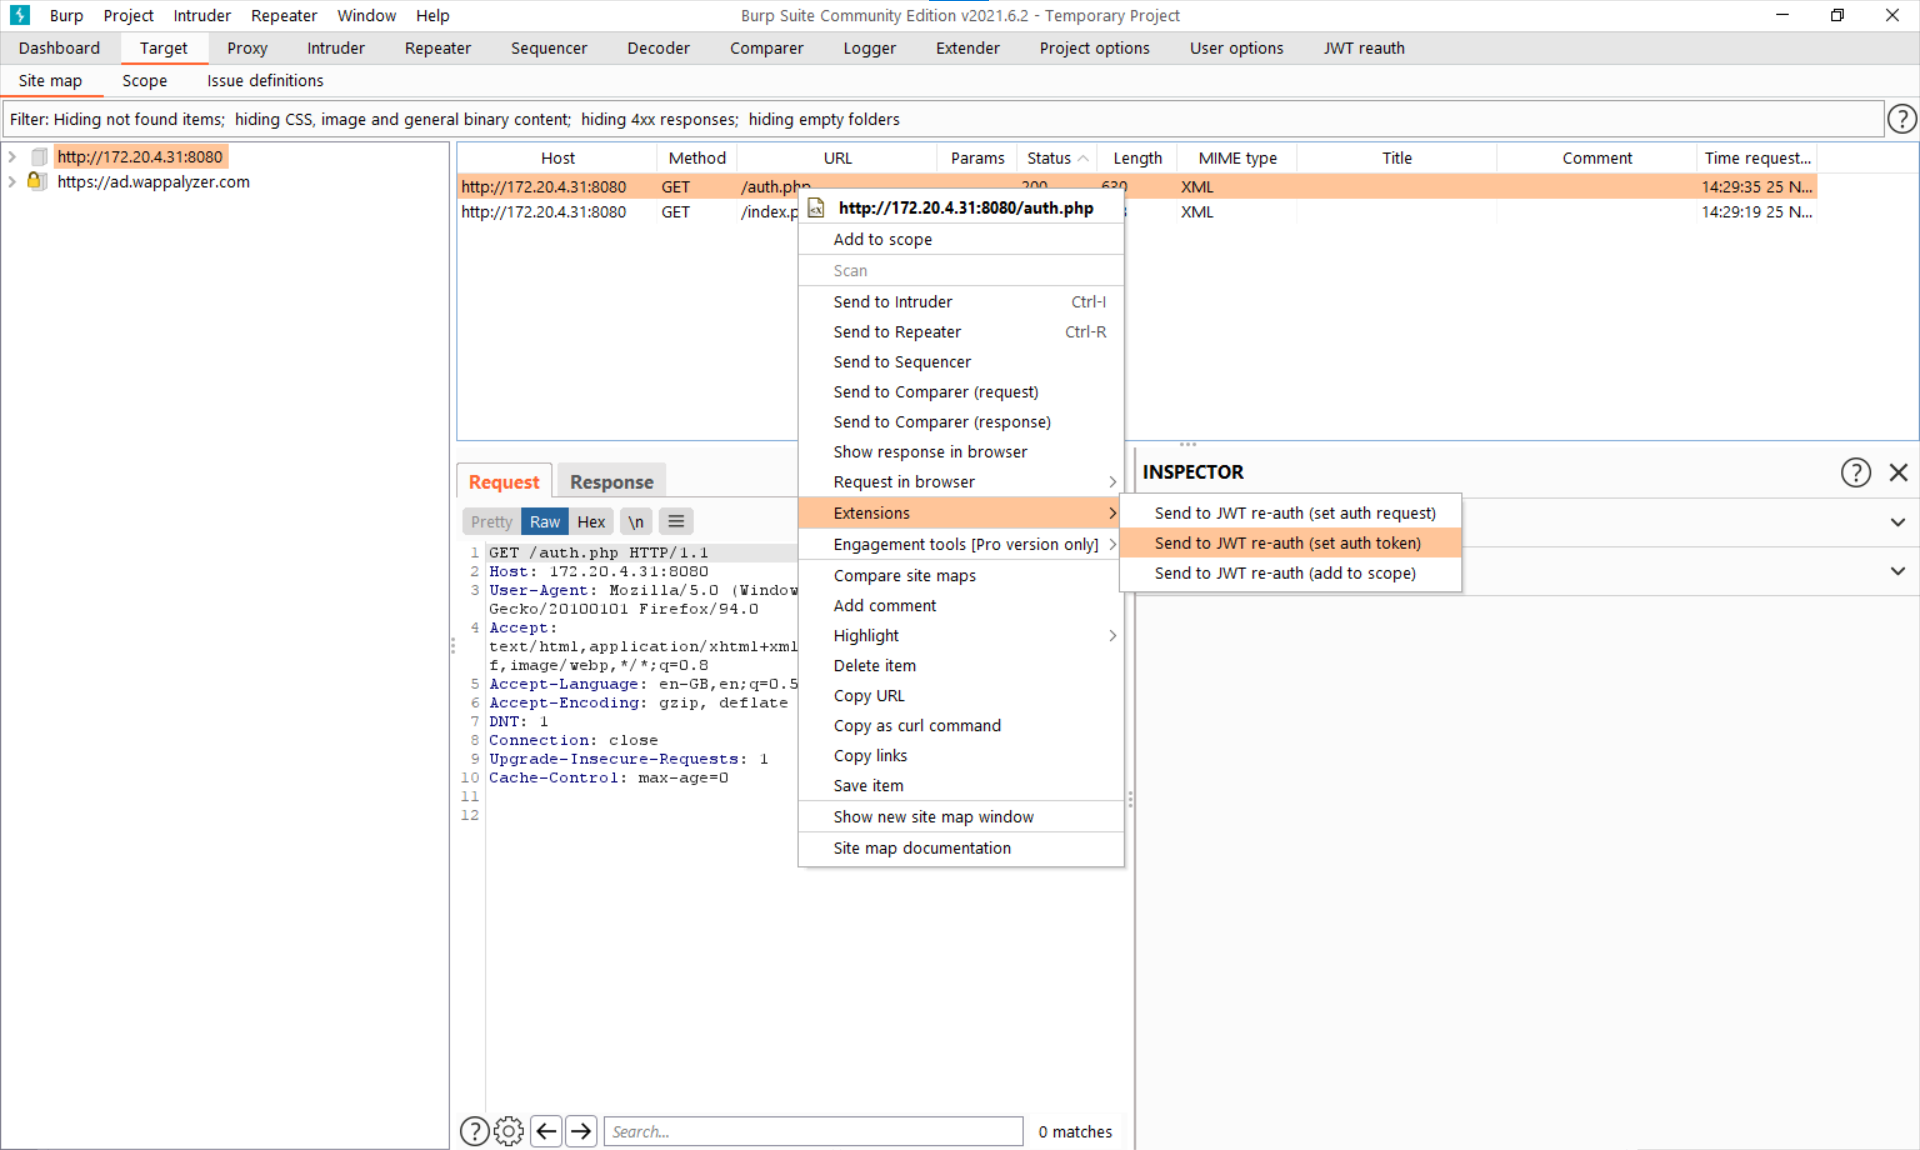
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.

An implementation of a vulnerable MCP server using mcp-go

unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)

A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…

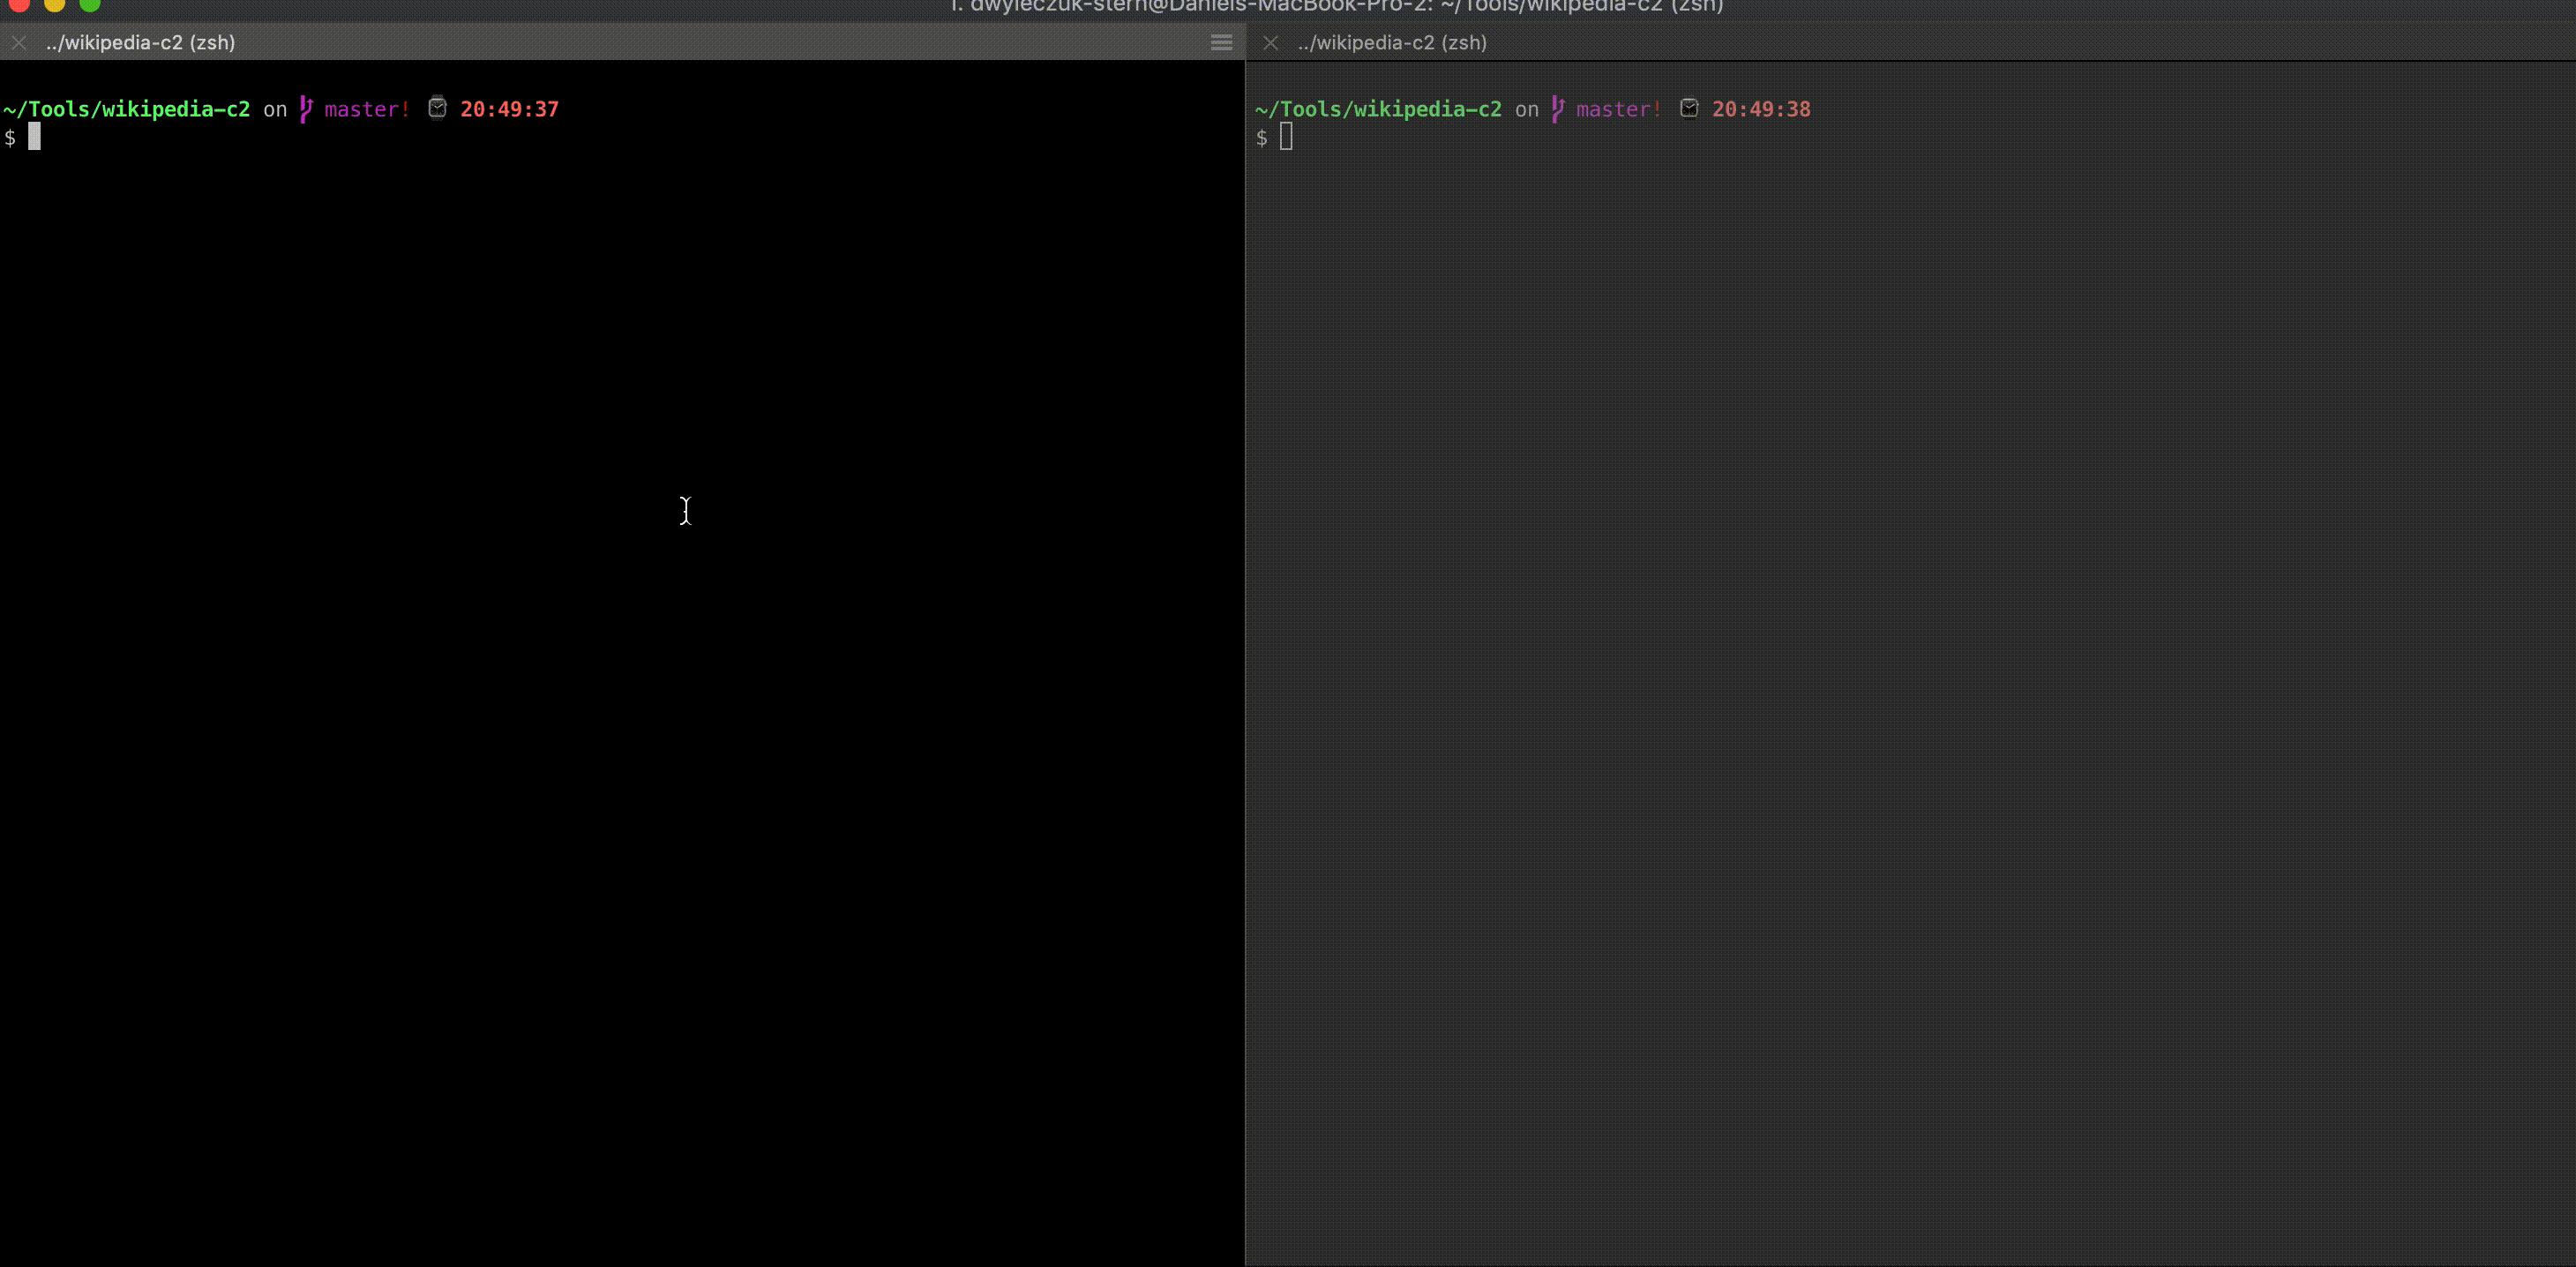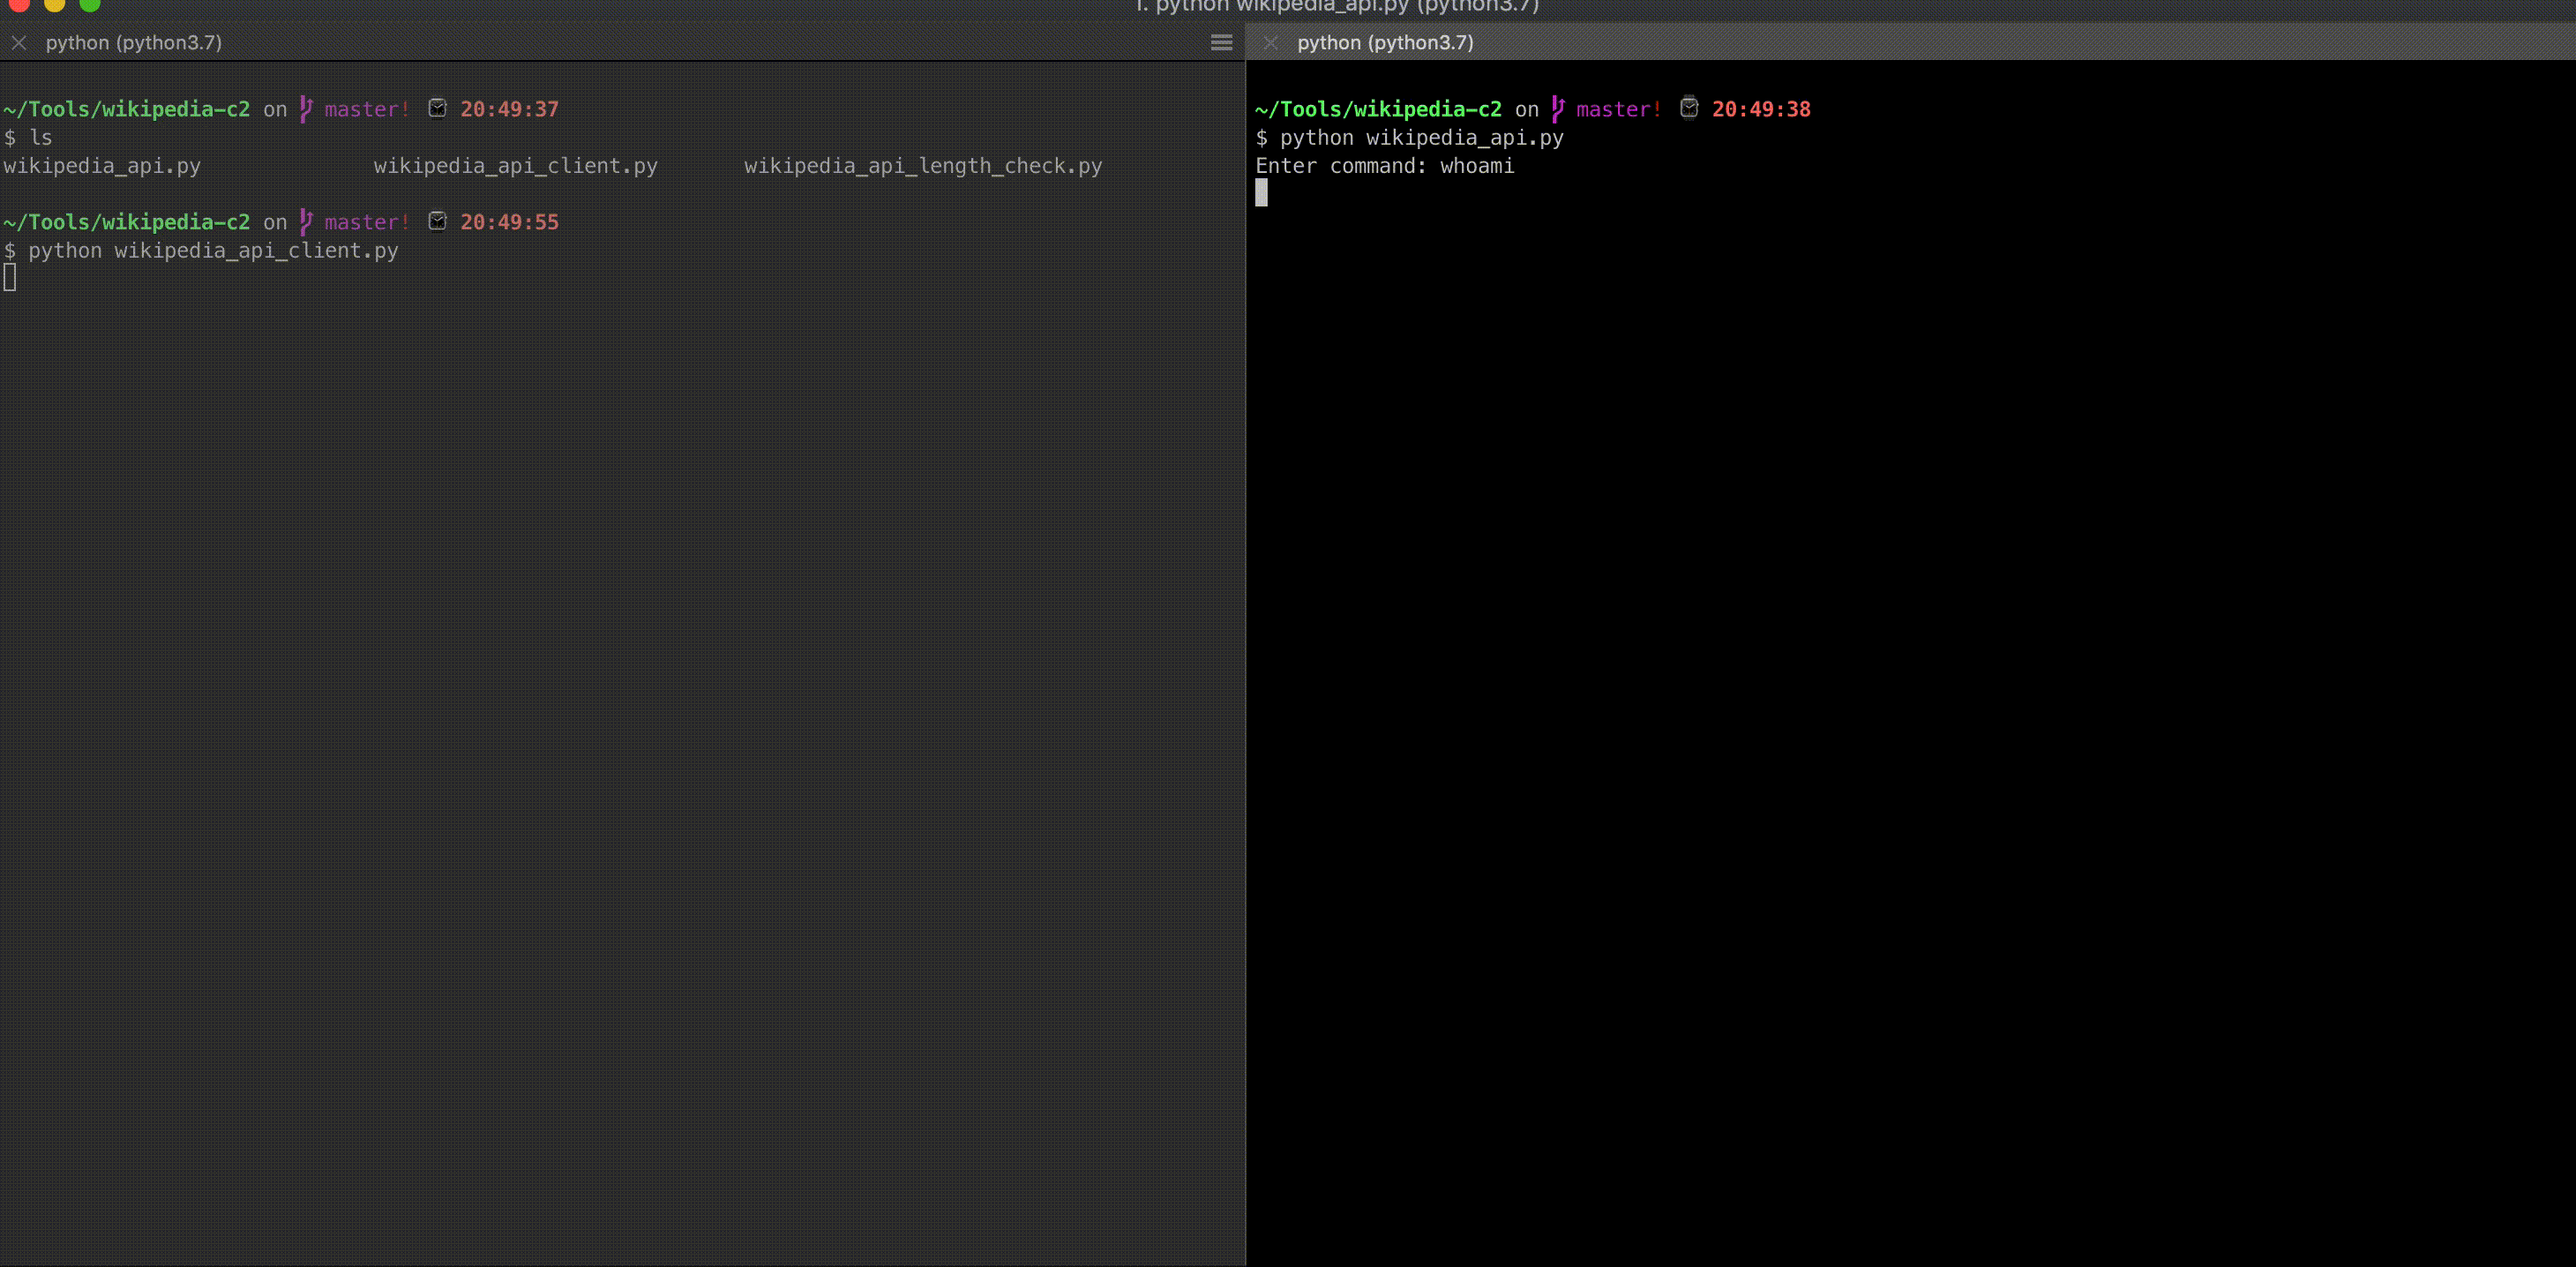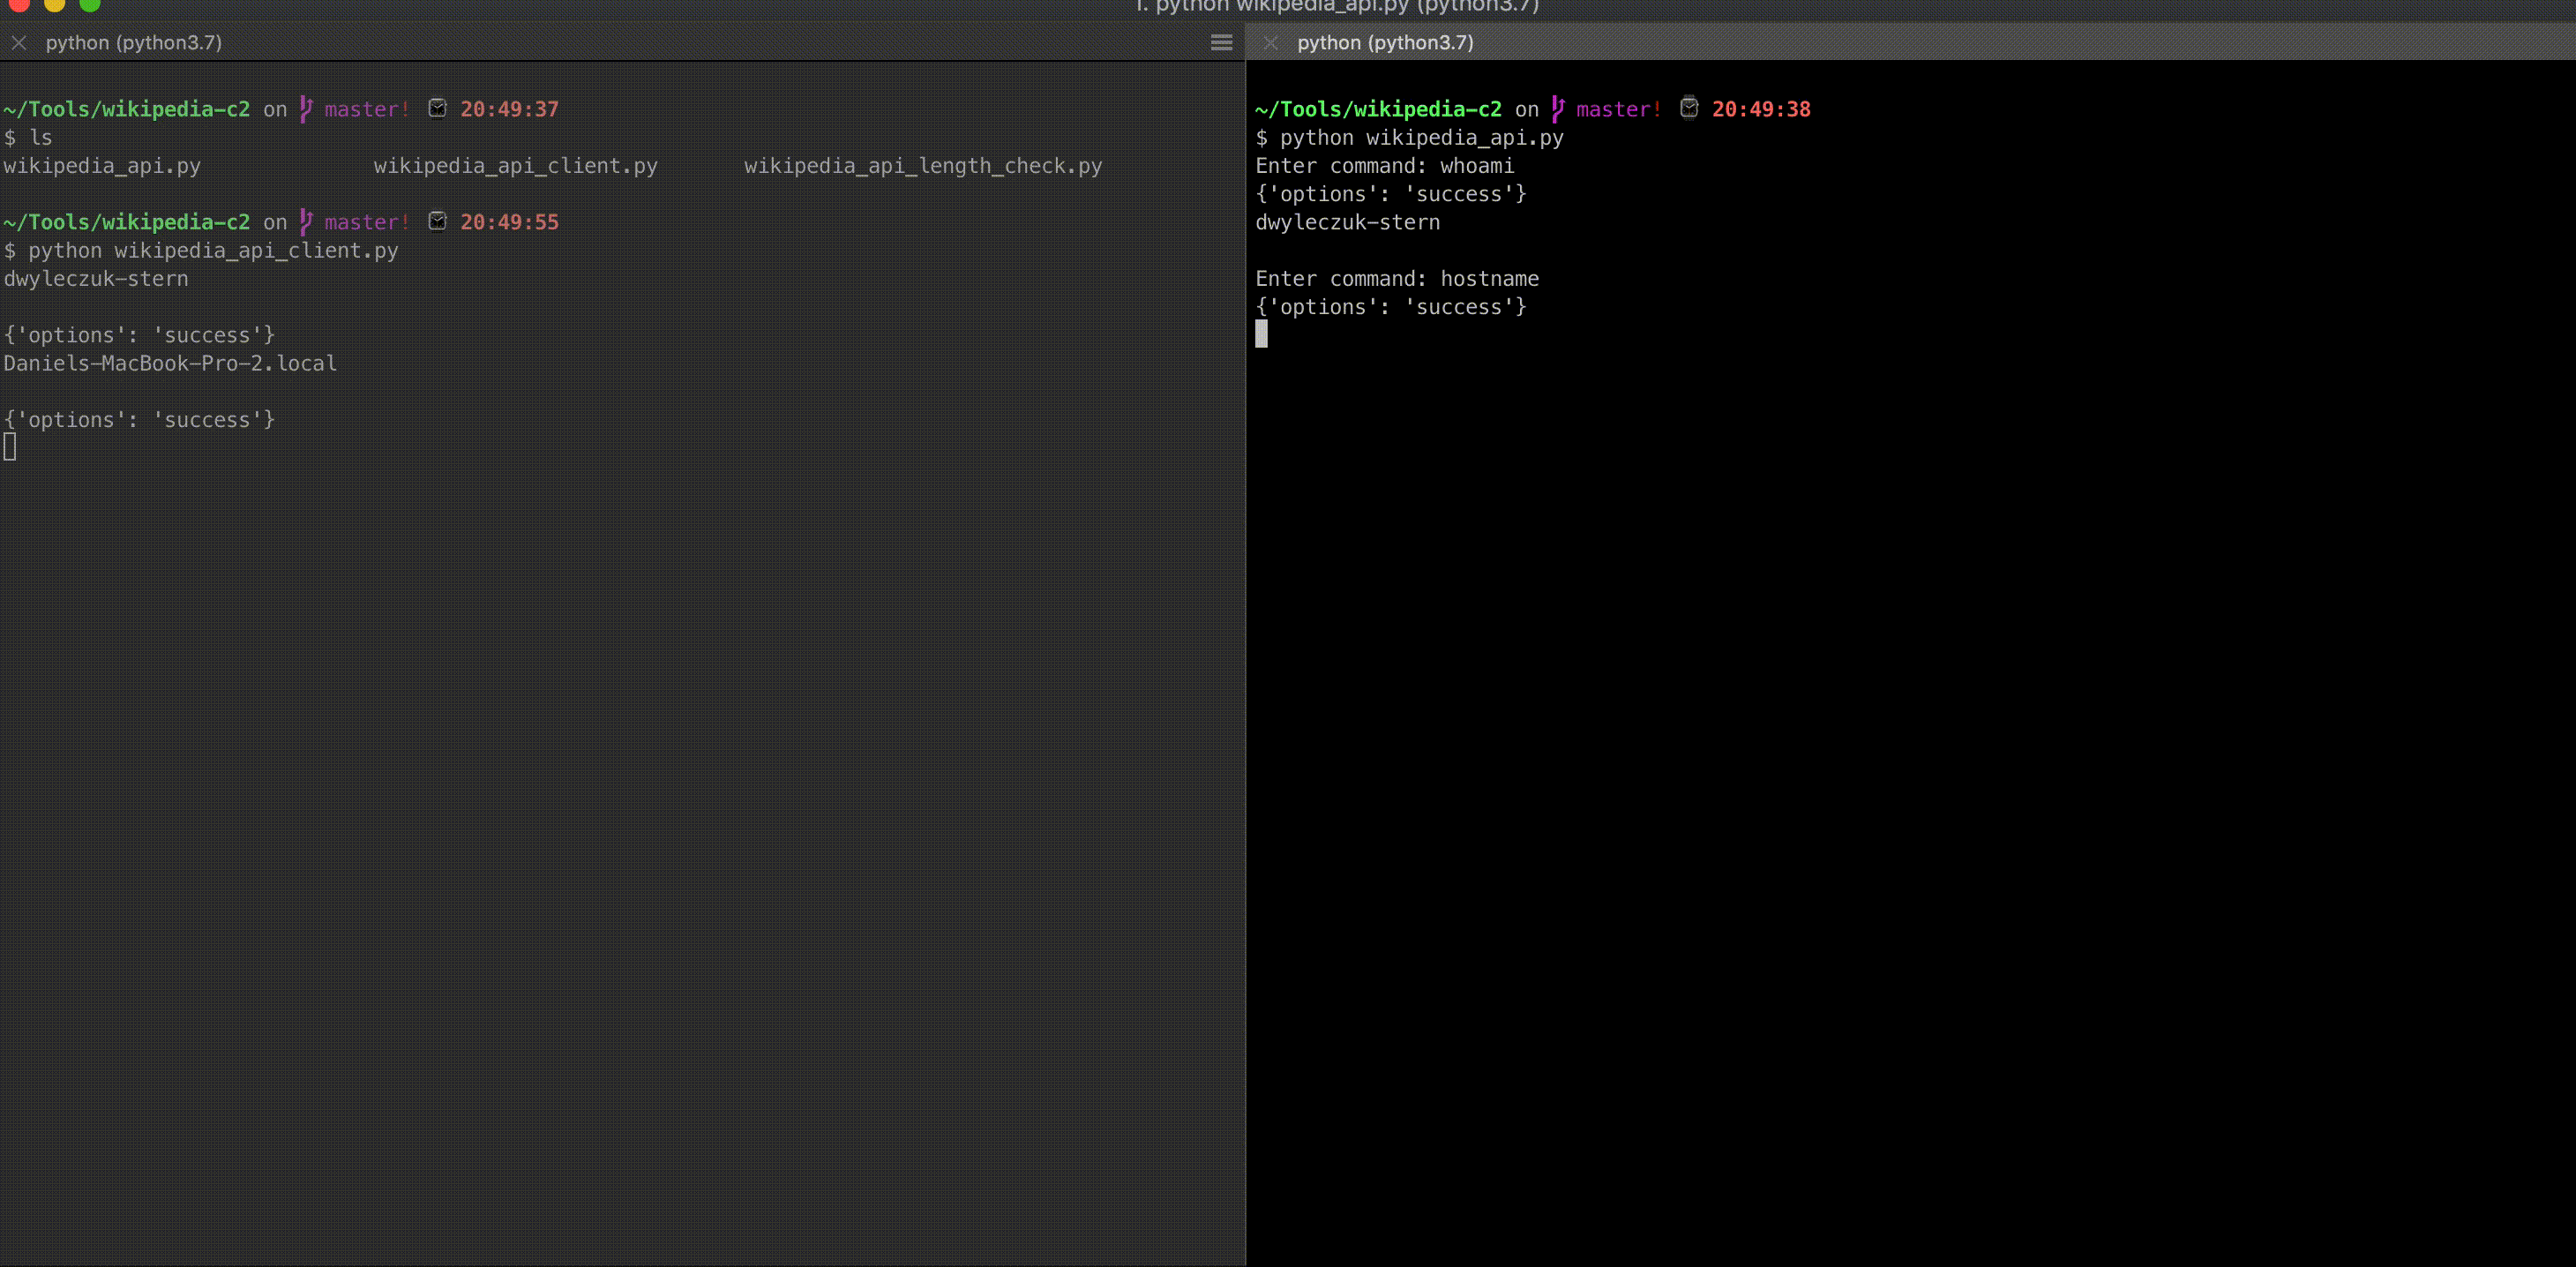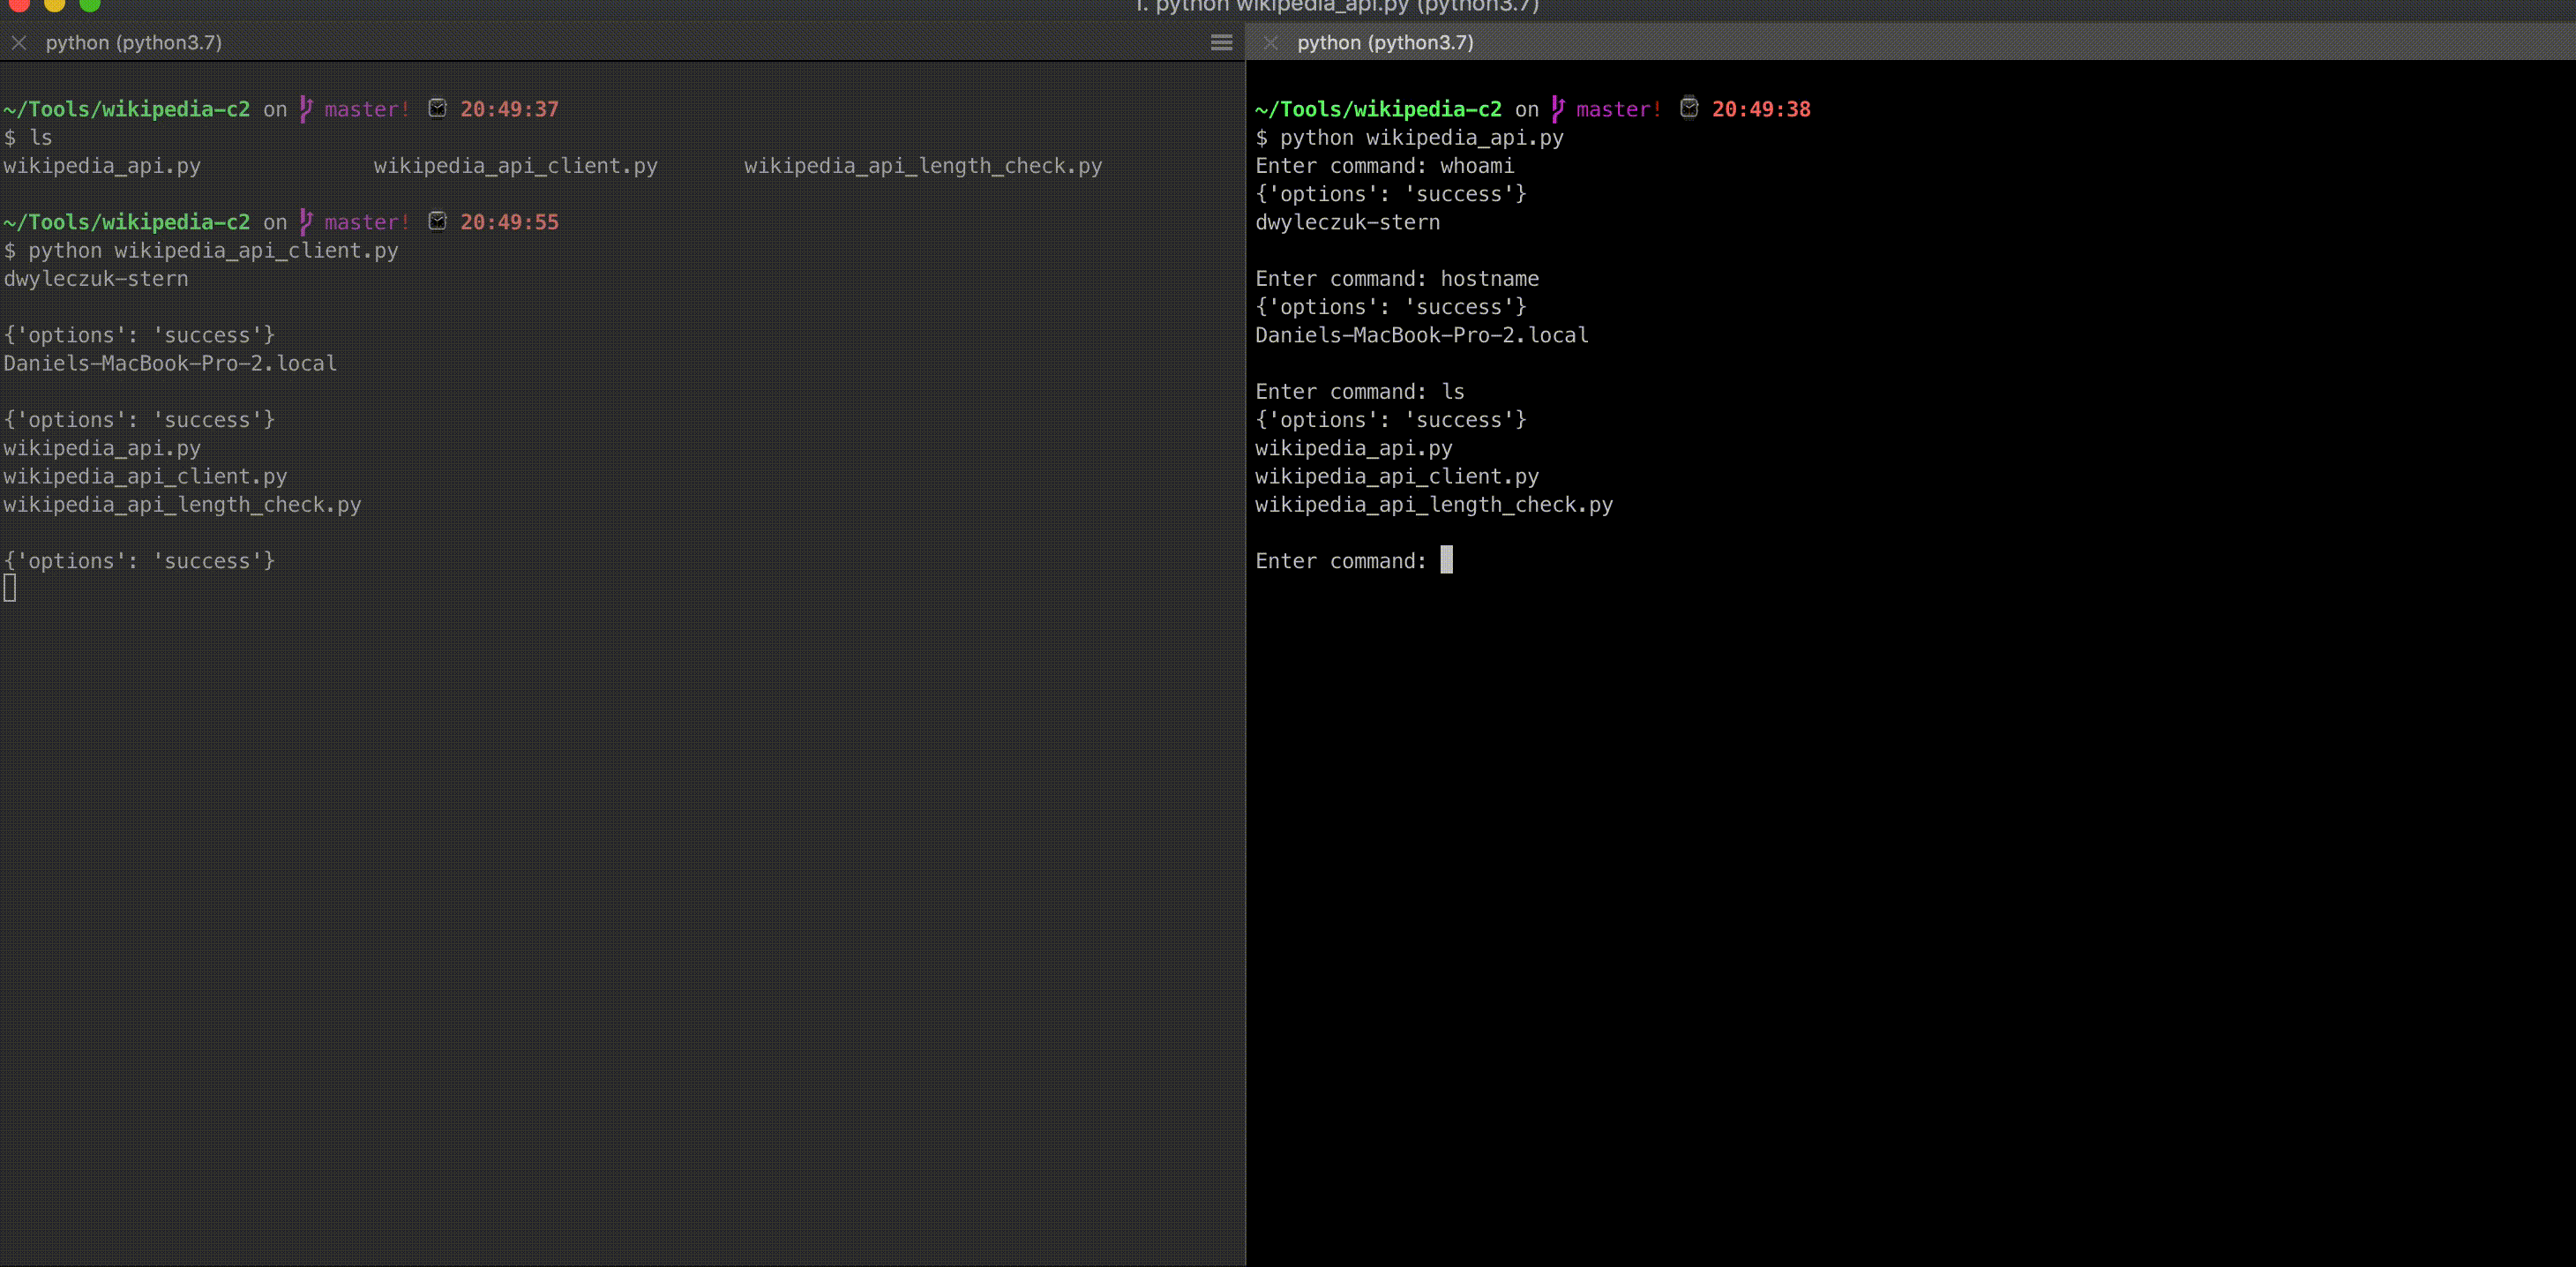
POC for utilizing wikipedia API for Command and Control

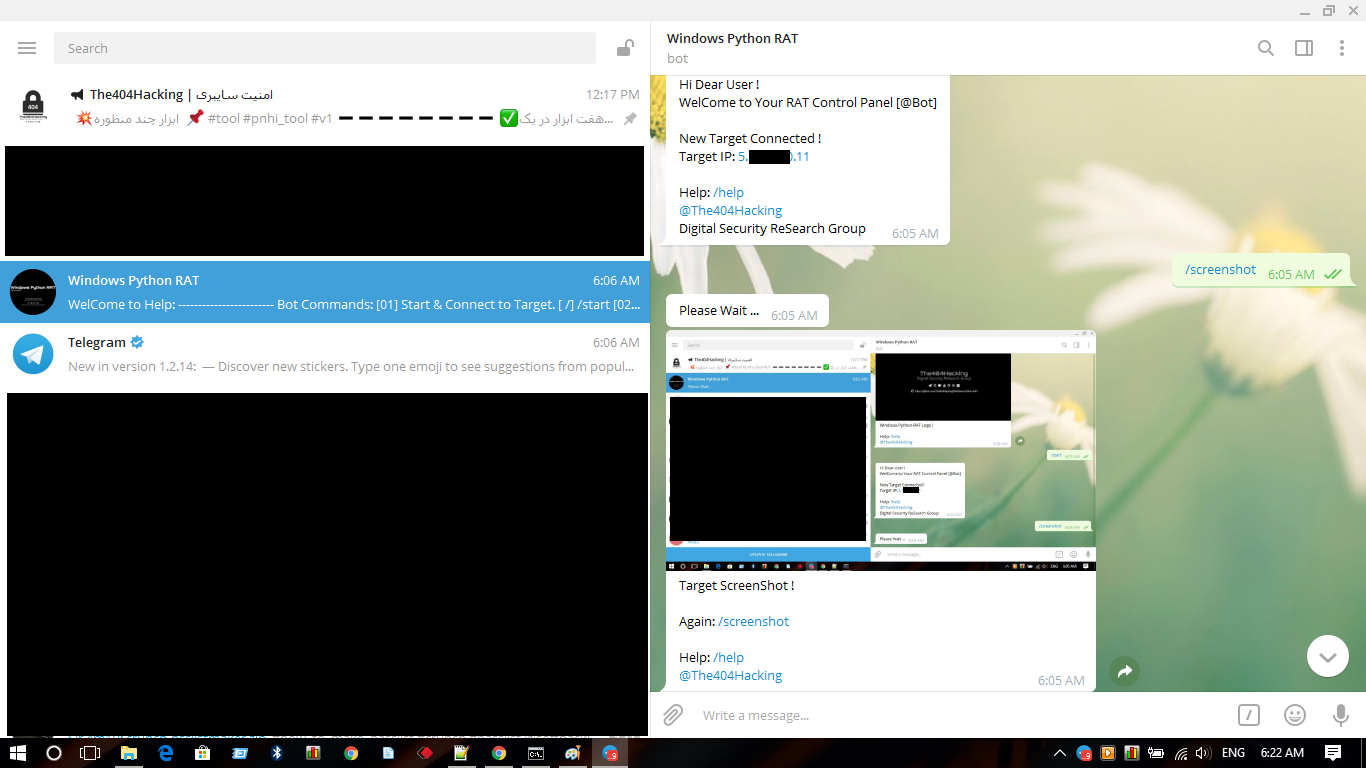
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.

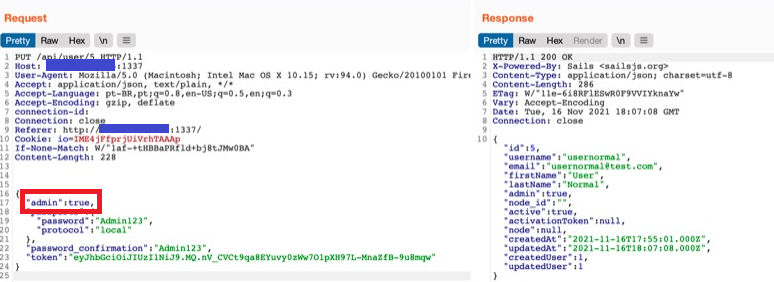
Proof-of-concept exploit for CVE-2021-44103 demonstrating vertical privilege escalation in Konga API Gateway 0.14.9, allowing authenticated users to…

Authenticated API Key Exposure in Nagios Log Server 2024R1.3.1

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…

"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…

PoC for CVE-2026-49230: Apache APISIX jwe-decrypt authentication bypass (missing AES-GCM tag validation, CWE-354, CVSS 9.1)