
gitea-follow-existence
 abraxas/gitea-follow-existence
Demonstrates a Gitea account-enumeration oracle: authenticated PUT /api/v1/user/following/{username} returns 204 for hidden accounts and 404 for…
api-securityexploitationinformation-gathering+5
abraxas/gitea-follow-existenceDemonstrates a Gitea account-enumeration oracle: authenticated PUT /api/v1/user/following/{username} returns 204 for hidden accounts and 404 for…
 abraxas/gitea-public-only-pat-org
Proof-of-concept lab for a Gitea authorization bypass where a public-only PAT with write:organization creates a private organization via POST…
 abraxas/gitea-stargazers-hidden
Proof-of-concept and lab for an unauthenticated Gitea information disclosure: the stargazers and watchers API leaks usernames that profile endpoints…
 abraxas/gitea-user-keys-idor
Proof-of-concept and lab for a Gitea IDOR (CWE-639) in GET /api/v1/user/keys/{id}, letting an authenticated read:user token enumerate other users'…
 abraxas/hyperswitch-payout-confirm-secret
Proof-of-concept and lab for a Hyperswitch payout confirm flaw: a dummy client_secret plus amount in POST /payouts/{id}/confirm raises the stored…
 abraxas/nextcloud-calendar-sharee-publish
Nextcloud 35.0.0 — a calendar edit-sharee can publish the owner's calendar to an unauthenticated URL
 abraxas/forgejo-keys-idor
Forgejo 16.0.5 - High - Remote - IDOR - GET /api/v1/user/keys/{id} returns other users SSH and deploy keys
 abraxas/joomla-levels-api
Joomla 6.1.3 - High - Remote - ACL - GET /api/v1/users/levels leaks view levels
 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)
 asvorg/cve-2026-105030-poc
A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 bombobombone/cve-2026-103440
Report summary and local proof-of-concept script demonstrating CVE-2026-103440, a PageTriage API disclosure of suppressed reviewer usernames on…
 bombobombone/cve-2026-102973
Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…
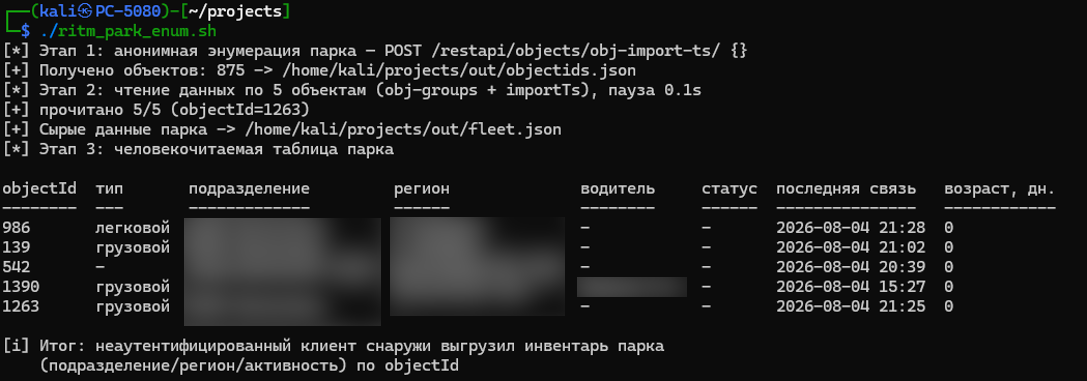 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 hasanuyarrr/cve-2026-18783-trex-mes-uygulamalarinda-yetkisiz-nesne-erisimi
Advisory for CVE-2026-18783: missing server-side authentication on TREX MES /api/GetDataJSON3 allows unauthenticated data queries and arbitrary SQL…
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…