
Wildfire
 defineid/wildfire
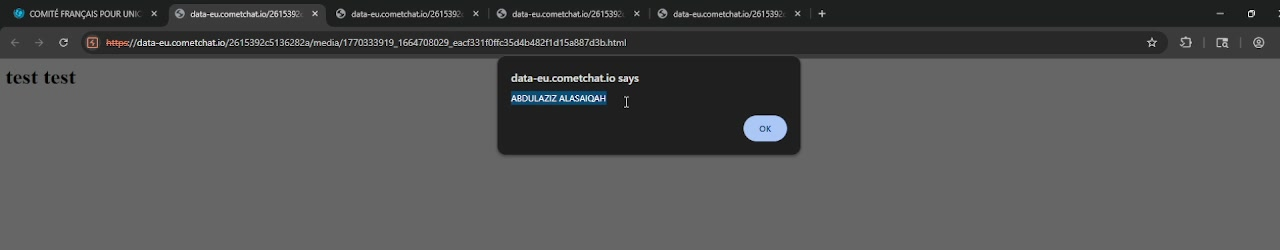
CVE-2026-39154, Stored XSS in CometChat JS SDK
api-securityexploitationpayload-development+4
defineid/wildfireCVE-2026-39154, Stored XSS in CometChat JS SDK
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 furkankayapinar/react-next-scanner
CVE-2025-55182 and CVE-2025-66478
 shoucheng3/nahsra__antisamy_cve-2017-14735_1-5-6
Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…
 shoucheng3/nahsra__antisamy_cve-2016-10006_1-5-3
Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…
 cure53/dompurify
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations
 momenbasel/keyfinder
Passive API key and secret discovery browser extension for Chrome and Firefox. 80+ detection patterns, zero config.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…