
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
13 results
CVE-2026-105030-poc preview

CVE-2026-105030-poc

GitHubasvorg/cve-2026-105030-poc

A python3 PoC for CVE-2026-105030 Kener 4.0.0 before 4.1.6 Hidden Monitor Data Disclosure via Dashboard API

api-securityexploitationinformation-gathering+4
20 days ago
CVE-2026-94609 preview

CVE-2026-94609

GitHubanthonyk2923/cve-2026-94609

Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
api-securityauthentication-authorizationeducation+6
29 days ago
POC-CVE-2026-93680 preview

POC-CVE-2026-93680

GitHubrmhowe425/poc-cve-2026-93680

Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
api-securityauthenticationdata-exfiltration+4
1 month ago
CVE-2025-62727-Demo preview

CVE-2025-62727-Demo

GitHubch4n3-yoon/cve-2025-62727-demo

Proof of concept of CVE-2025-62727 that can cause denial-of-service in FastAPI (based Starlette <= 0.48.0)
api-securityexploitationvulnerability-analysis+1
10 years ago
CVE-2026-53959 preview

CVE-2026-53959

GitHubanirbala98/cve-2026-53959

4gaBoards < 3.3.9 - User Information Disclosure
api-securityeducationexploitation+5
12 months ago
CVE-2026-40179-PoC preview

CVE-2026-40179-PoC

GitHubbsdrip/cve-2026-40179-poc

Minimal Python PoC for CVE-2026-40179: injects a malicious metric name via unauthenticated Prometheus remote_write to trigger stored XSS in the web…
api-securityexploitationvulnerability-analysis+1
1 month ago
EITS-Portal-Exploit-CVE-2026-31367-PoC preview

EITS-Portal-Exploit-CVE-2026-31367-PoC

GitHubhereticl1nk/eits-portal-exploit-cve-2026-31367-poc

PoC exploit for unauthenticated RCE in EITS Admin Dashboard v2.4.0 via command injection in /api/v1/debug, allowing arbitrary OS command execution on…
api-securityexploitationpenetration-testing+2
2 months ago
Azure-APIM-Dev-Portal-Signup-Bypass preview

Azure-APIM-Dev-Portal-Signup-Bypass

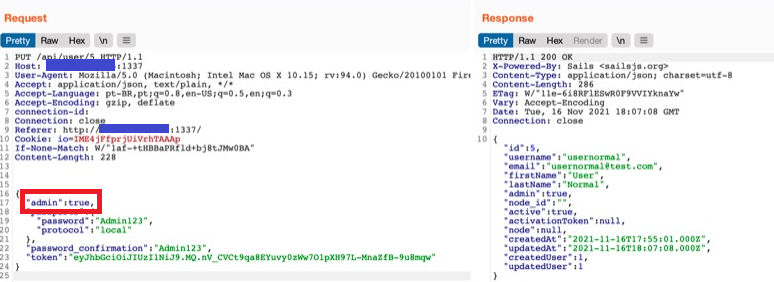
GitHubdz-y/azure-apim-dev-portal-signup-bypass

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
api-securityapi-security-testingauthentication-authorization+6
2 months ago
CVE-2021-44103 preview

CVE-2021-44103

GitHubpaulotrindadec/cve-2021-44103

Proof-of-concept exploit for CVE-2021-44103 demonstrating vertical privilege escalation in Konga API Gateway 0.14.9, allowing authenticated users to…
api-securityexploitationpenetration-testing+3
34 years ago
CVE-2026-46726 preview

CVE-2026-46726

GitHuboscerd/cve-2026-46726

Reproducer for CVE-2026-46726: Apache Camel camel-vertx-websocket unfiltered inbound header injection enabling SSRF and secret disclosure via…
api-securityexploitationpenetration-testing+3
3 months ago
CVE-2026-46456 preview

CVE-2026-46456

GitHuboscerd/cve-2026-46456

Reproducer for CVE-2026-46456 — Apache Camel camel-aws2-sqs inbound message-attribute header injection (Camel control-header injection via…
api-securitycloud-securityexploitation+3
2 months ago
CVE-2025-6514 preview

CVE-2025-6514

GitHubcyberency/cve-2025-6514

mcp-remote exposed to OS command injection
api-securityauthenticationcommand-and-control+3
711 months ago
Apache-APISIX-CVE-2022-24112 preview

Apache-APISIX-CVE-2022-24112

GitHubm4xsec/apache-apisix-cve-2022-24112

Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit

api-securityapi-security-testingexploitation+3
154 years ago