
 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
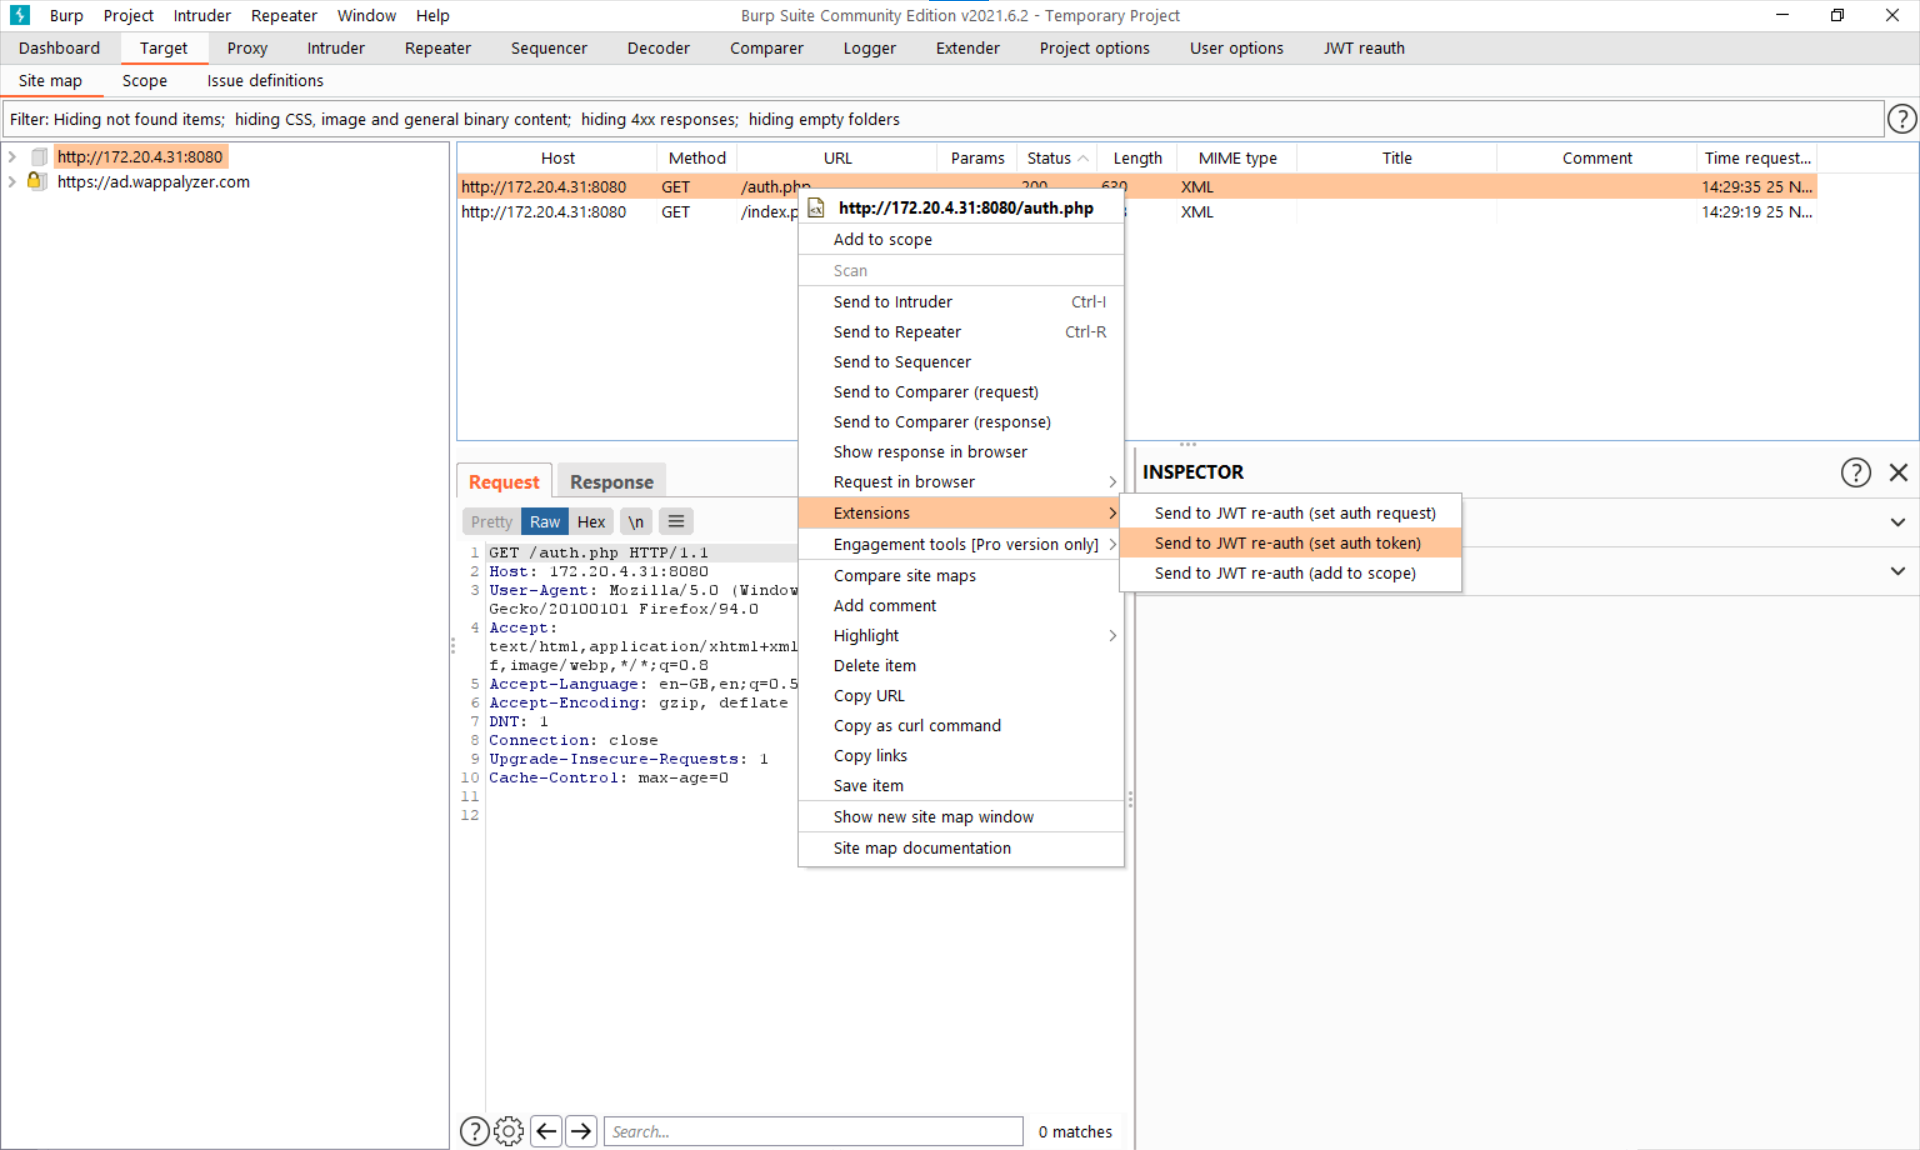 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.

 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
 theopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field
Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)
 remenis/cve-2025-63667
Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…
 0xbs0d27/cve-2025-56643
Public reference for CVE-2025-56643 – Wiki.js 2.5.307 JWT Session Vulnerability
 imthecopilotnow/cve-2025-492030
Proof-of-concept for CVE-2025-492030: account takeover via session token validation bypass in SecureVPN API endpoint /api/v1/authenticate.
 teteco/cve-2026-52217-vtex-checkout-crosstenant-idor
The VTEX Checkout Service exposes OrderForm data through the endpoints `/api/checkout/pub/orderForm/{orderFormId}` and `/attachments/*`. These…
 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)